Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Azure-AccessPermissions — PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access configurations for security auditing. | Kitploit
Tools/GitHubGitHub/csandker/azure-accesspermissions
Authentication & AuthorizationCloud Infrastructure SecurityReconnaissanceInformation GatheringPenetration TestingCloud SecurityIdentity & Access Management (IAM)Archived
Share
GitHub
csandker/azure-accesspermissions

Azure-AccessPermissions

PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access configurations for security auditing.

View Repository
11018513 years agoReviewed by Kitploit

Azure-AccessPermissions

Easy to use PowerShell script to enumerate access permissions in an Azure Active Directory environment.

Background details can be found in the accompanied blog posts:

  • Untangling Azure Active Directory Principals & Access Permissions
  • Untangling Azure Active Directory Permissions II: Privileged Access

Requirements

To run this script you'll need these two PowerShell modules:

  • Microsoft.Graph
  • AADInternals
  • AzureADPreview

All of these can be installed directly within PowerShell:

PS:> Install-Module Microsoft.Graph
PS:> Install-Module AADInternals
PS:> Install-Module AzureADPreview

Usage

First time use

The script uses a browser-based Login UI to connect to Azure. If you run the tool for the first time you might experience the following error

[*] Connecting to Microsoft Graph...
WARNING: WebBrowser control emulation not set for PowerShell or PowerShell ISE!
Would you like set the emulation to IE 11? Otherwise the login form may not work! (Y/N): Y
Emulation set. Restart PowerShell/ISE!

Error on first run

To solve this simply allow PowerShell to emulate the browser and rerun your command.

Example use

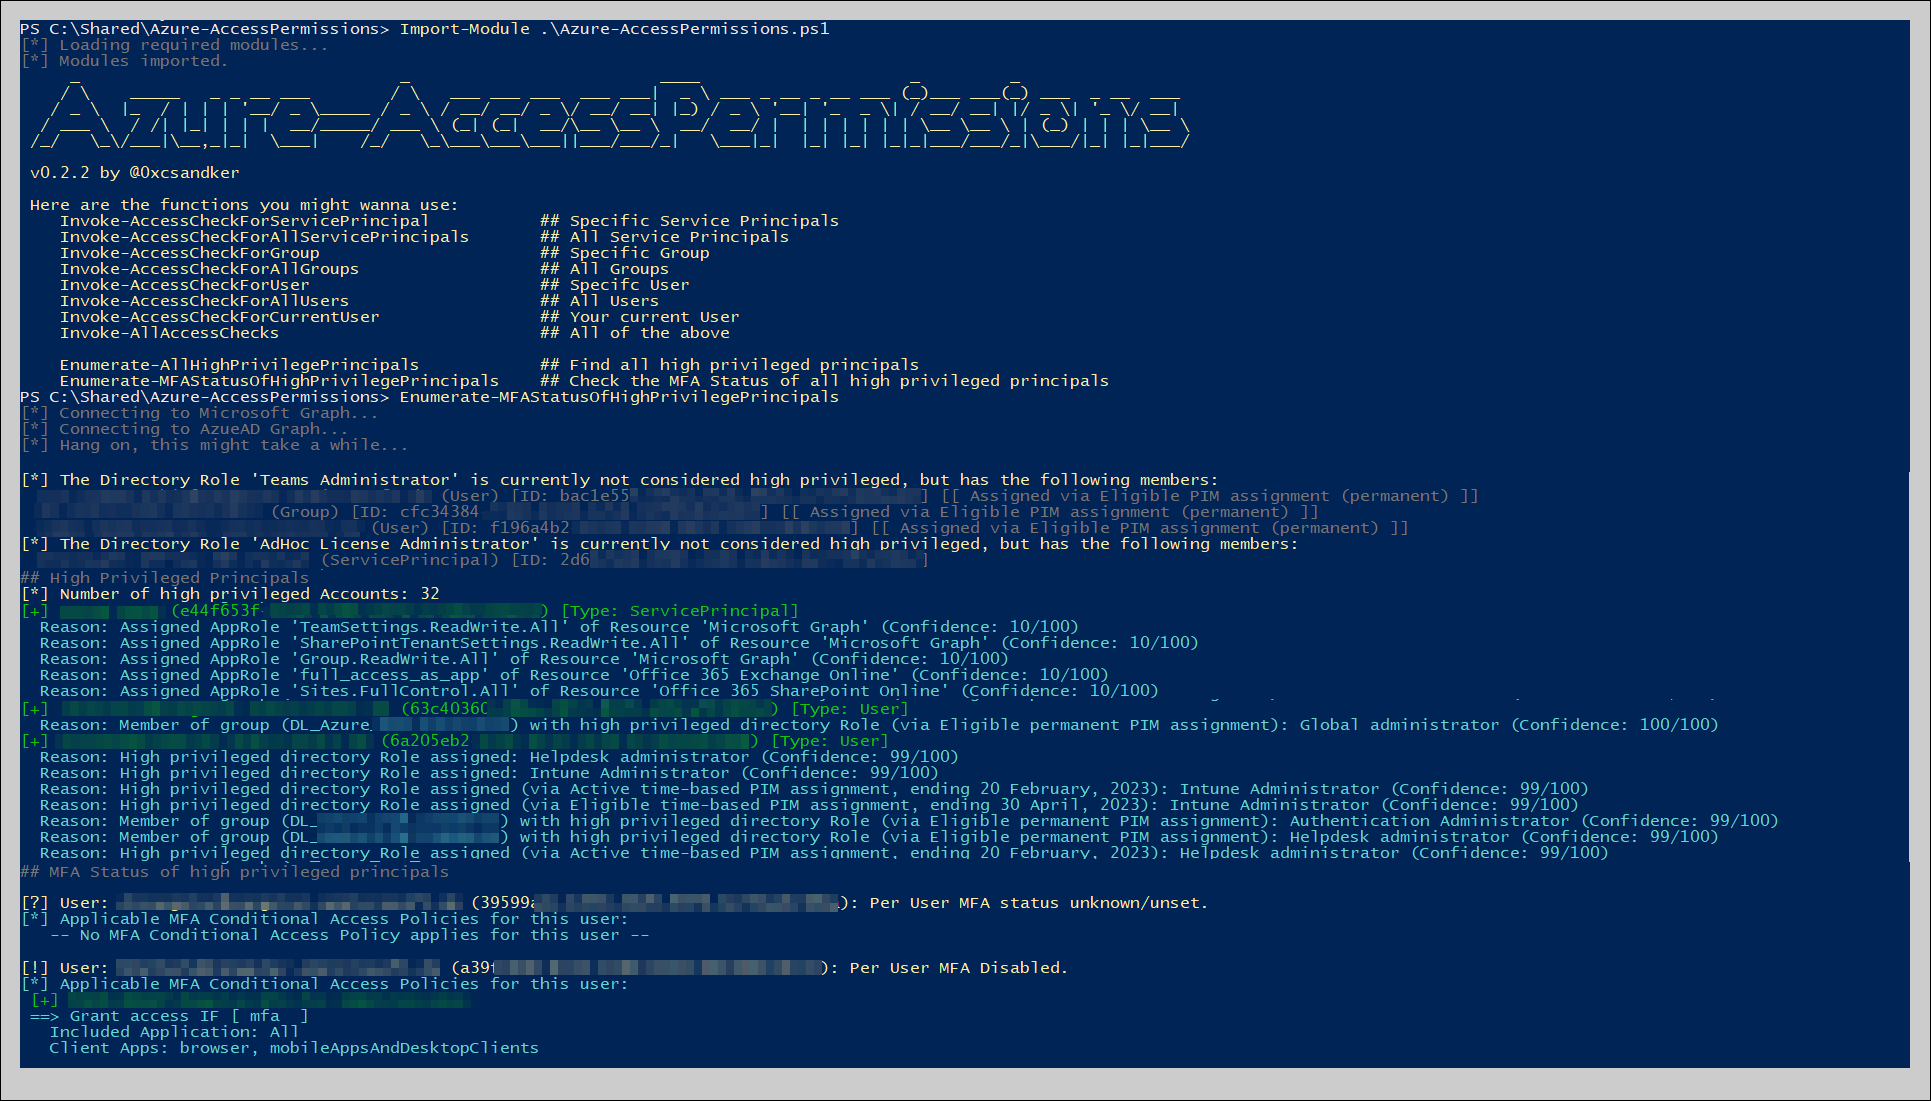
Import and run, no argumentes needed.

Note: On your first run you will likely have to authenticate twice (once Microsoft Graph and once against Azure AD Graph). I might wrap this into a single login in the future...

PS:> Import-Module .\Azure-AccessPermissions.ps1

SampleOutput

SampleOutput

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    717
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    504
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    402
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →