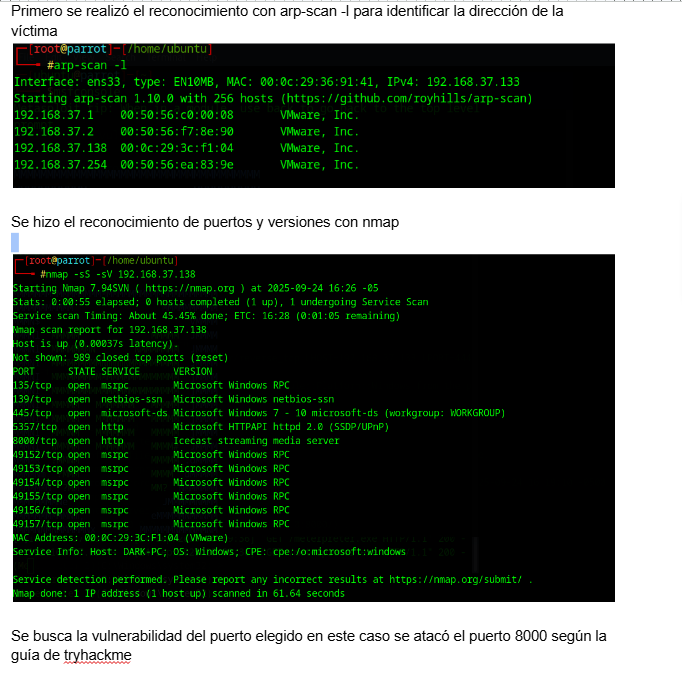
thm-ice-icecast-rce-privesc

Full compromise of TryHackMe's Ice machine — Icecast 2.0.1 RCE (CVE-2004-1561) via buffer overflow, followed by Windows privilege escalation through…

Full compromise of TryHackMe's Ice machine — Icecast 2.0.1 RCE (CVE-2004-1561) via buffer overflow, followed by Windows privilege escalation through…

KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…

Reproduction and analysis toolkit for CVE-2025-55423, providing exploit verification and vulnerability assessment capabilities for security…

Leaking kernel addresses from ETW consumers. Requires Administrator privileges.

CVE-2018-4248: Out-of-bounds read in libxpc during string serialization.

Program for determining types of files for Windows, Linux and MacOS.

Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.

Windows KASLR bypass using prefetch side-channel

exploit for CVE-2026-42945

Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…

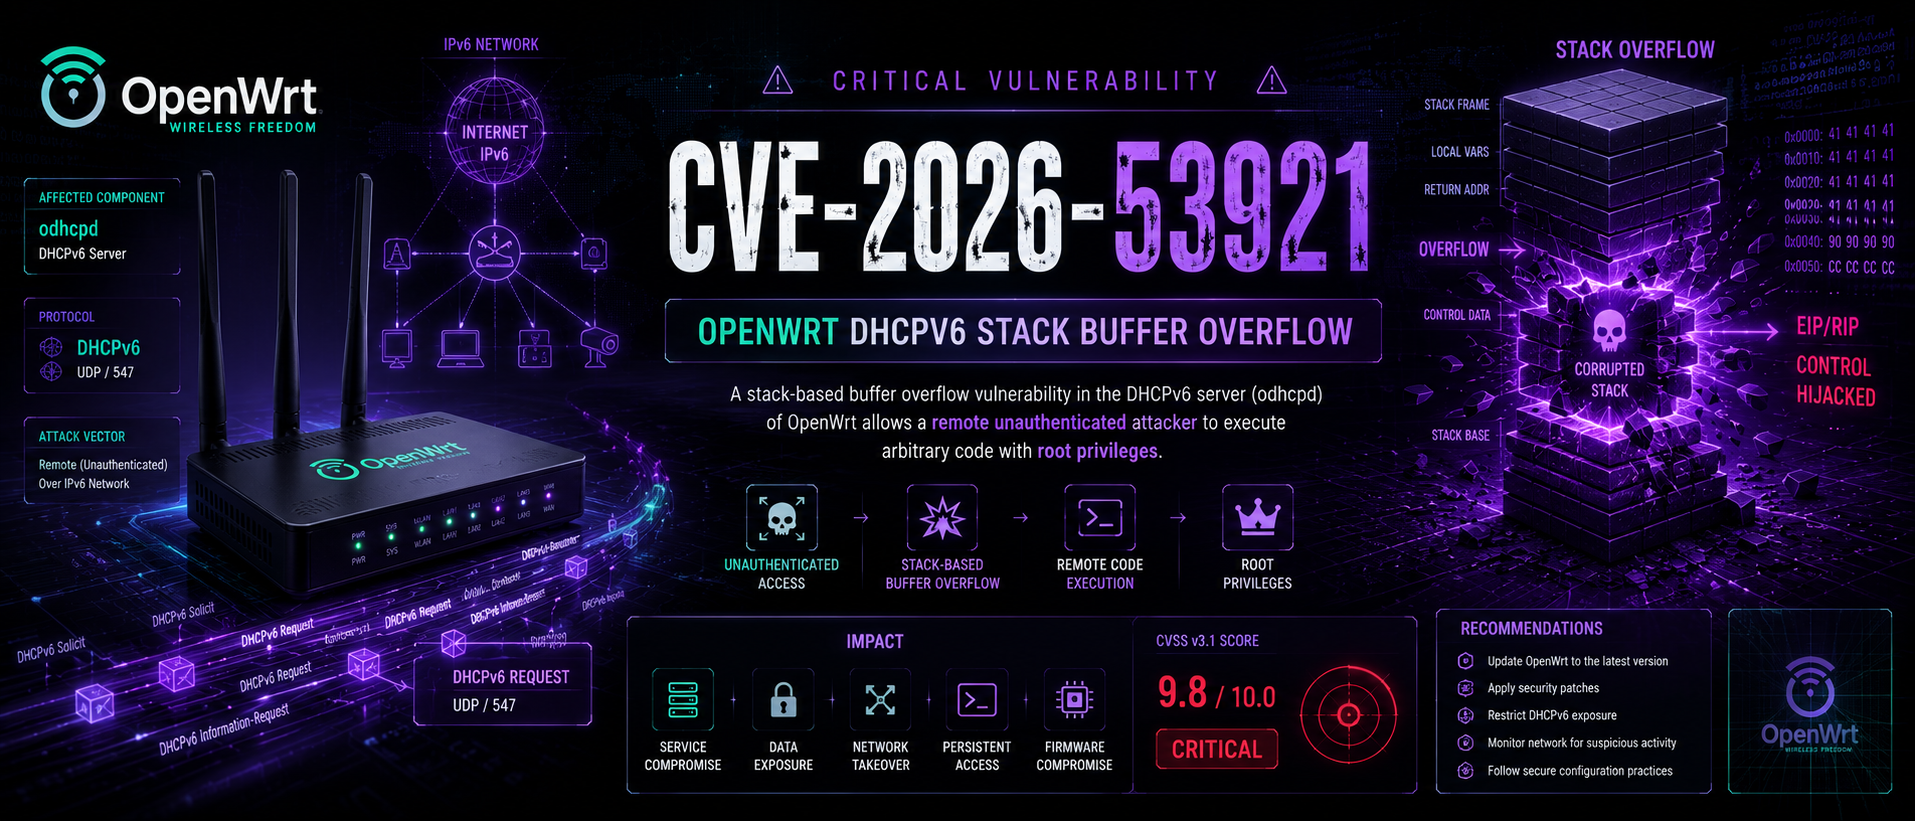
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…

Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…

A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…

Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…

CVE-2026-42945 Nginx Rift

[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…

Reproduction exploit for CVE-2024-21409, demonstrating the vulnerability and providing a proof-of-concept for security testing and validation.

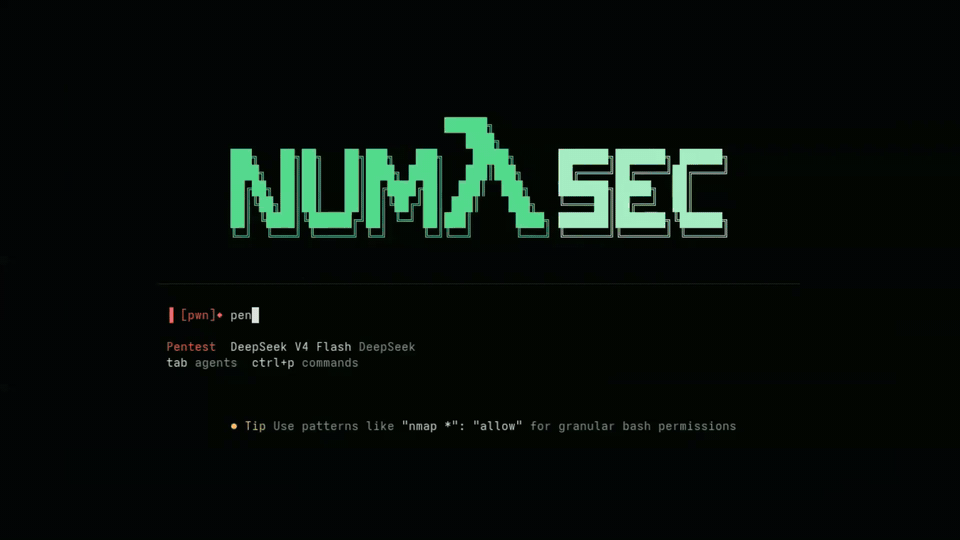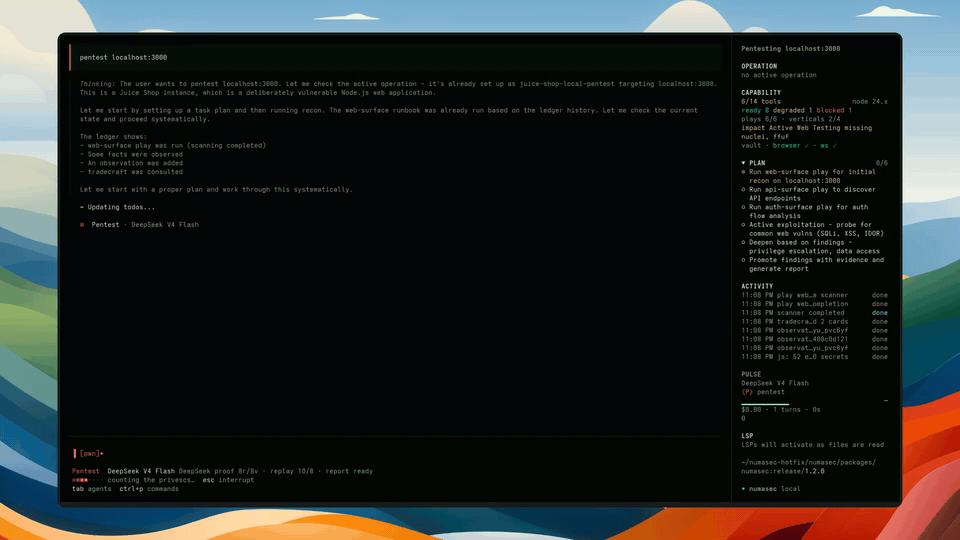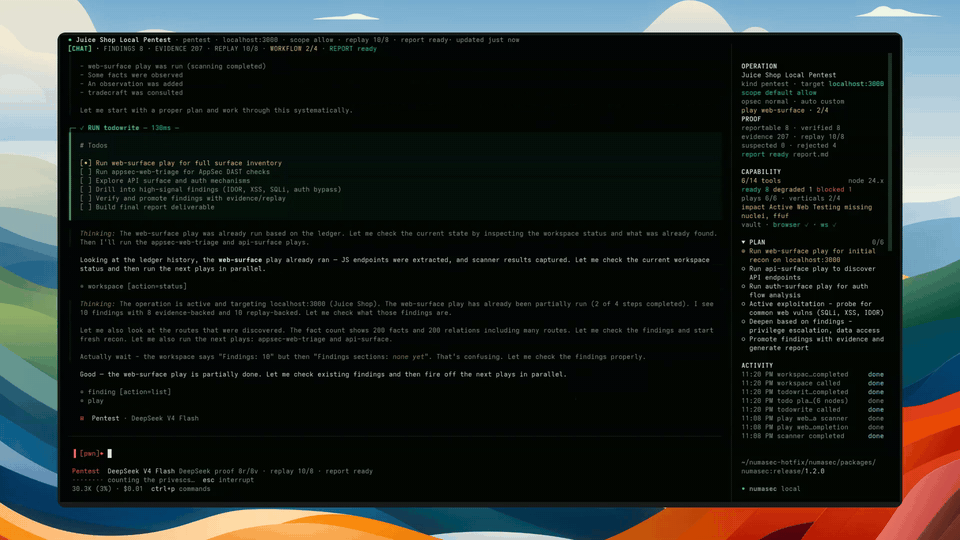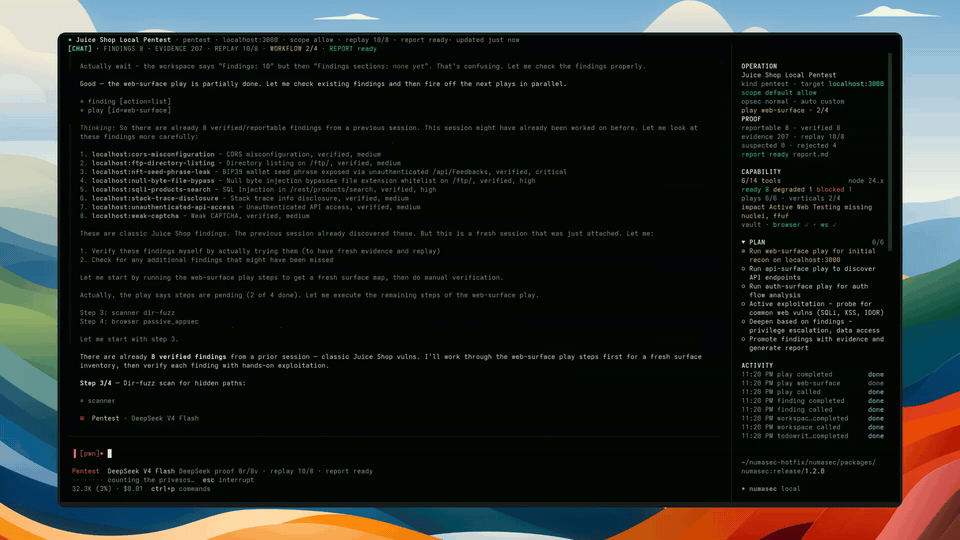
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…