

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 saeeddhqan/maryam
Maryam: Open-source Intelligence(OSINT) Framework
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 owasp/wwwgrep
OWASP Foundation Web Respository
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 owasp/awscanner
Finds internet-exposed resources in an AWS account
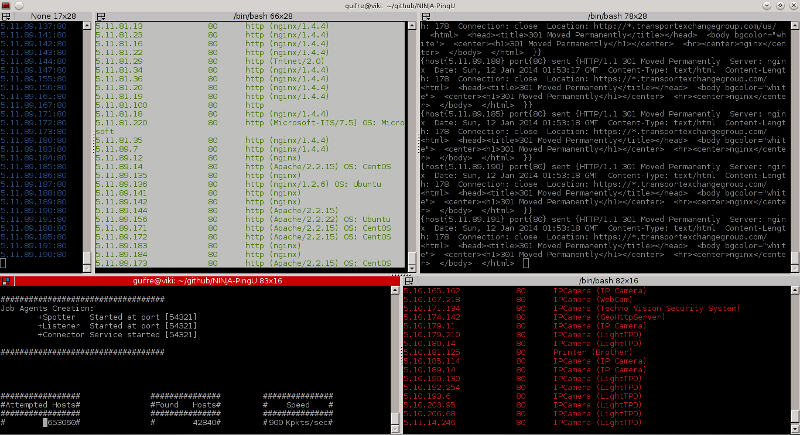 owasp/ninja-pingu
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…
 moeinfatehi/admin-panel_finder
Burp Suite extension that finds exposed admin panels and login pages of web applications and infrastructure. 1,000+ payloads, OWASP WSTG-CONF-05.
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 urbanadventurer/whatweb
Next generation web scanner
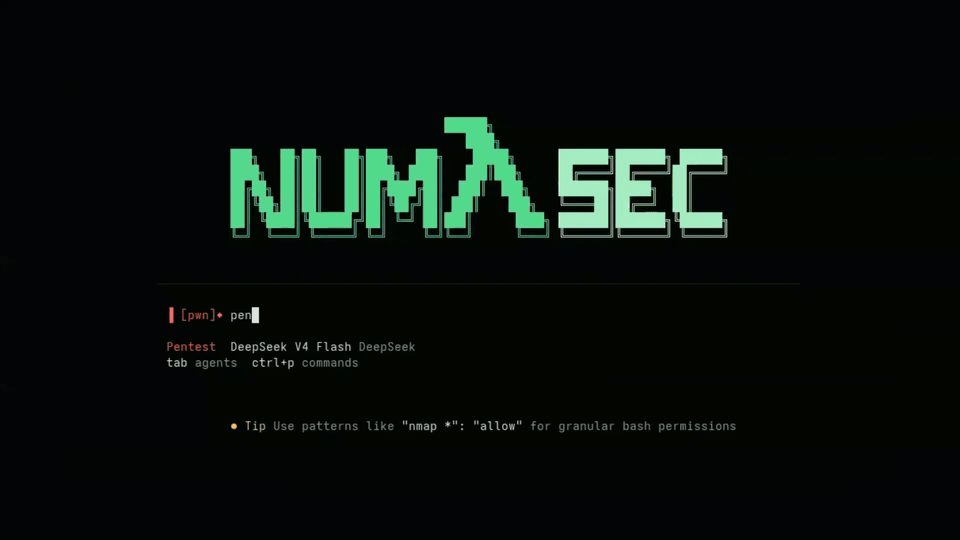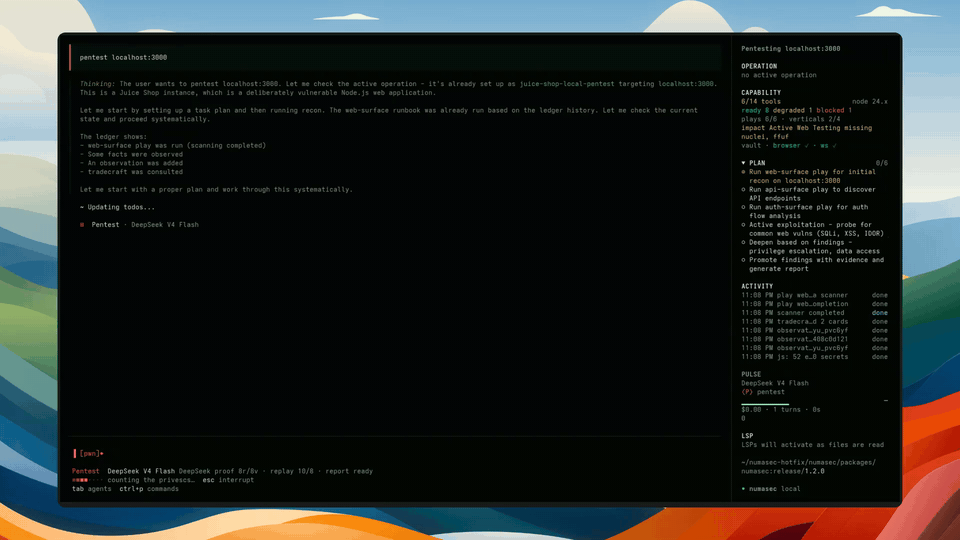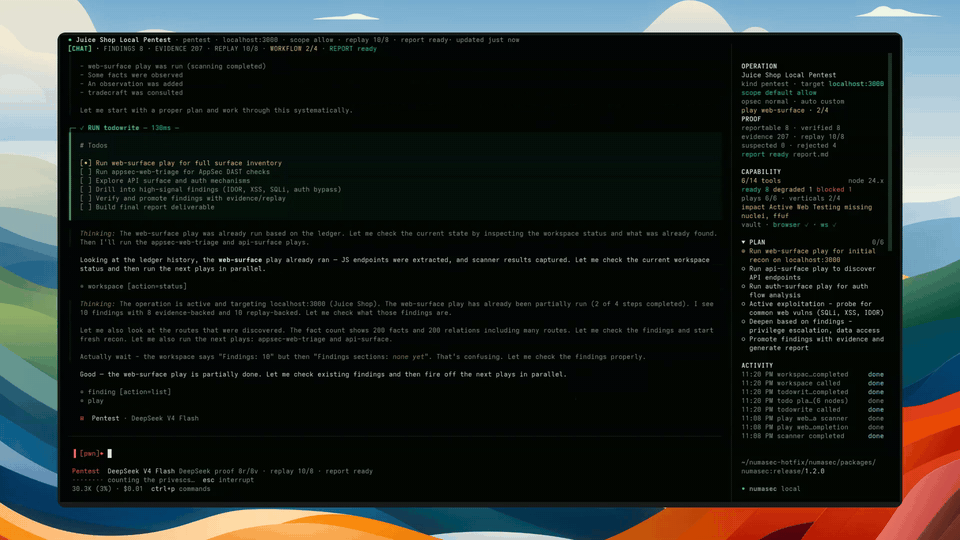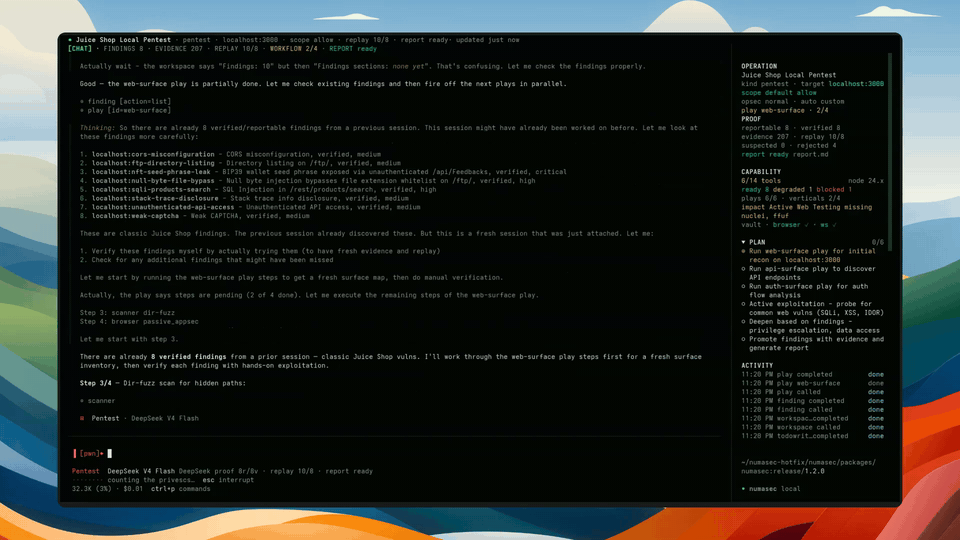 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 stuub/cve-2024-28995
CVE-2024-28955 Exploitation PoC