

Bug-Bounty-Arsenal-v.3
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
api-security-testingcrawlerdevsecops+8
12
foxvr-sudo/bug-bounty-arsenal-v.3Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
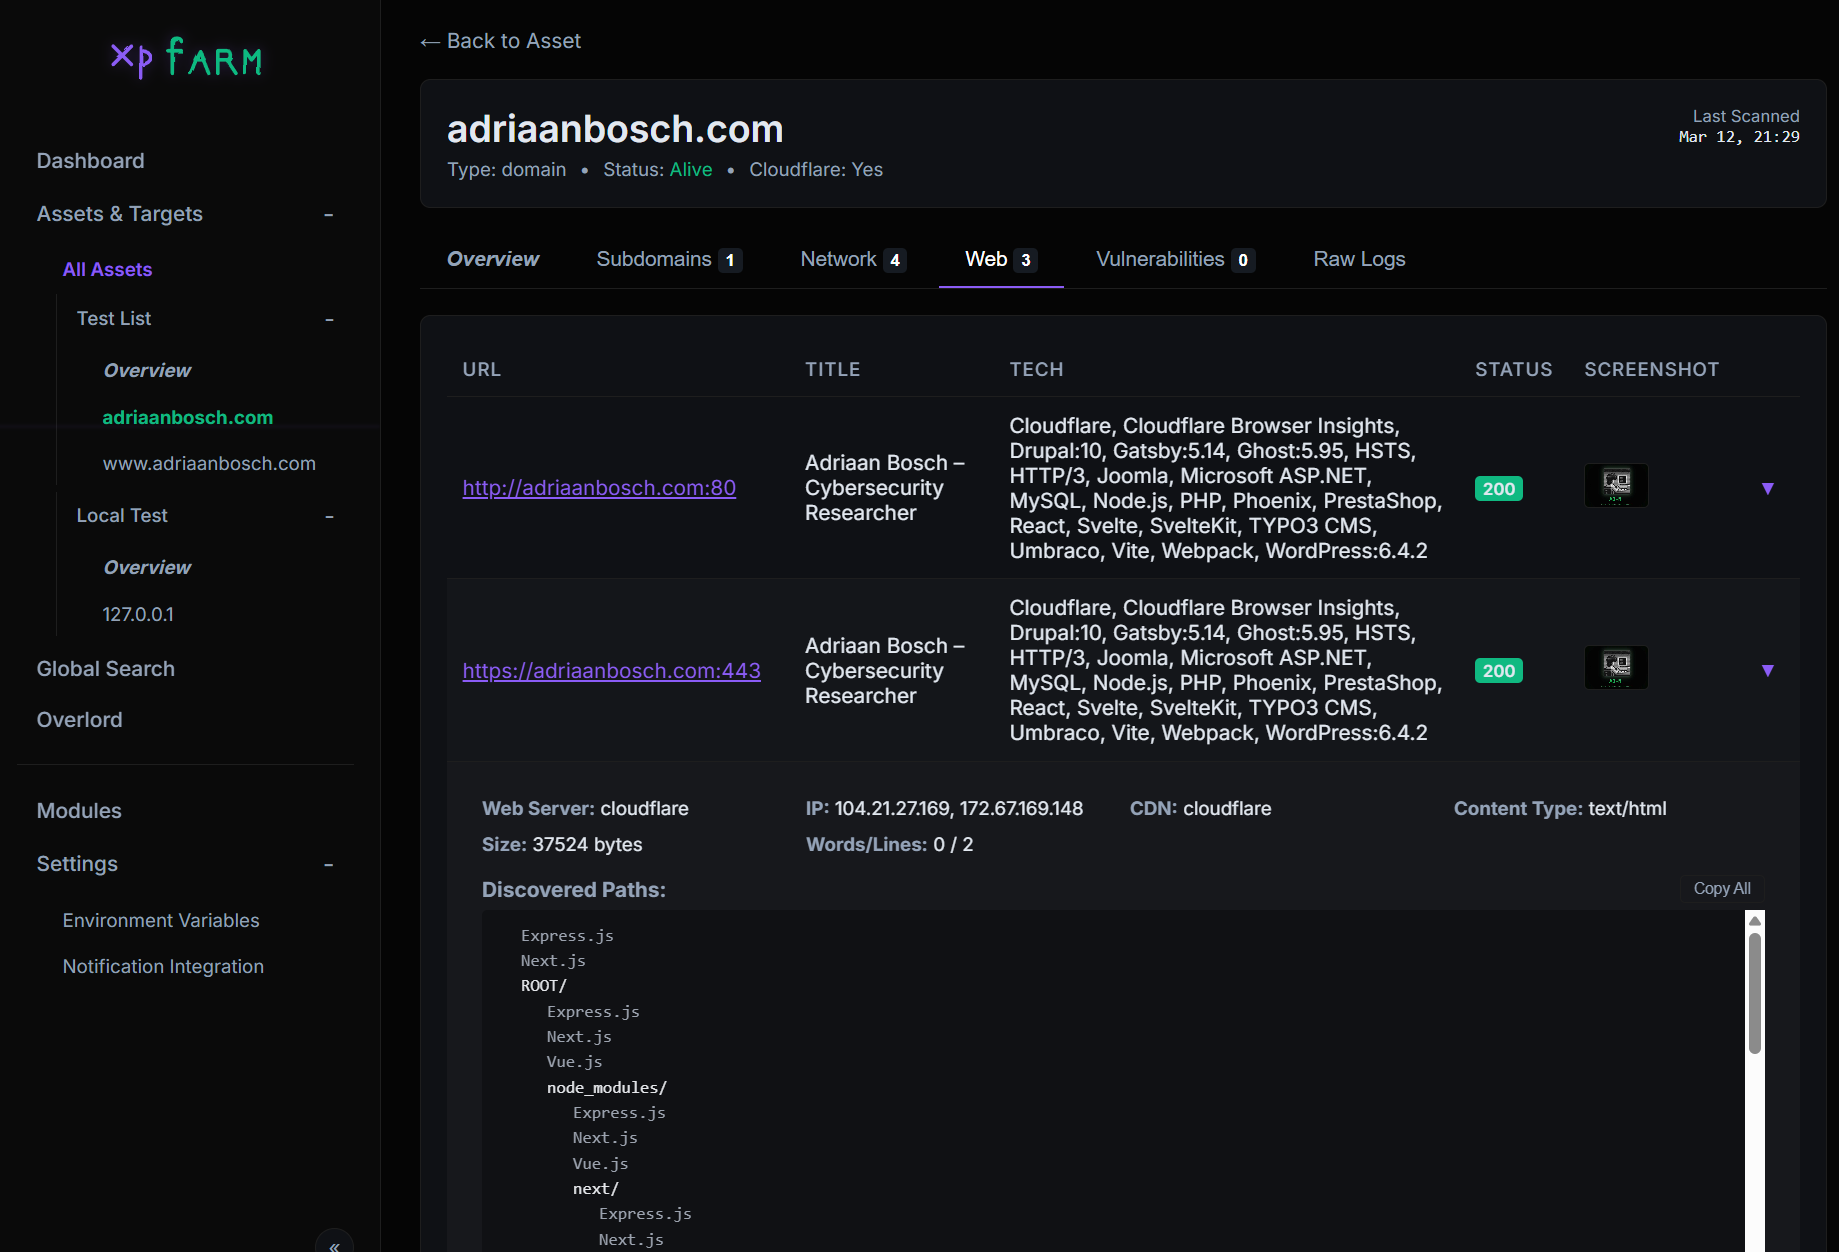 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 maverickaayush/onus
Locally-hosted, air-gapped VAPT platform that runs 8 parallel scanning modules, deterministically scores findings with CVSS v3.1, and generates PDF…
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.
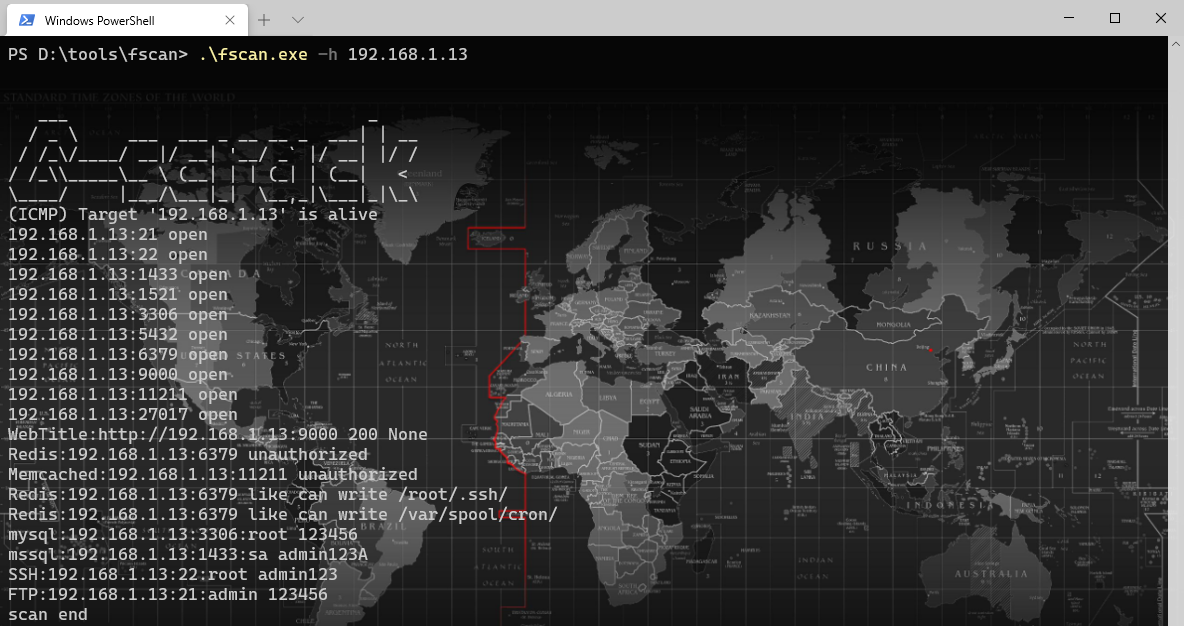 shadow1ng/fscan
一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。(An intranet comprehensive scanning tool, enabling one-click automated, all-round vulnerability scanning)
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 bigb0x/cve-2024-6387
Bulk Scanning Tool for OpenSSH CVE-2024-6387, CVE-2006-5051 , CVE-2008-4109 and others.
 aniqfakhrul/cve-2022-22954
Python exploit for CVE-2022-22954, a VMware Workspace ONE SSTI vulnerability, with batch scanning and Shodan integration for vulnerable host…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 phirojshah/cve-2024-4577
Proof-of-concept exploit for PHP CGI argument injection (CVE-2024-4577) enabling remote code execution on vulnerable Windows servers with scanning…
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning
 jan0x190/cve-2025-55182-simple-scanner-main
Multi-language scanner for CVE-2025-55182 RCE in Next.js React Server Components, with single/mass scanning modes and integrated bug bounty…
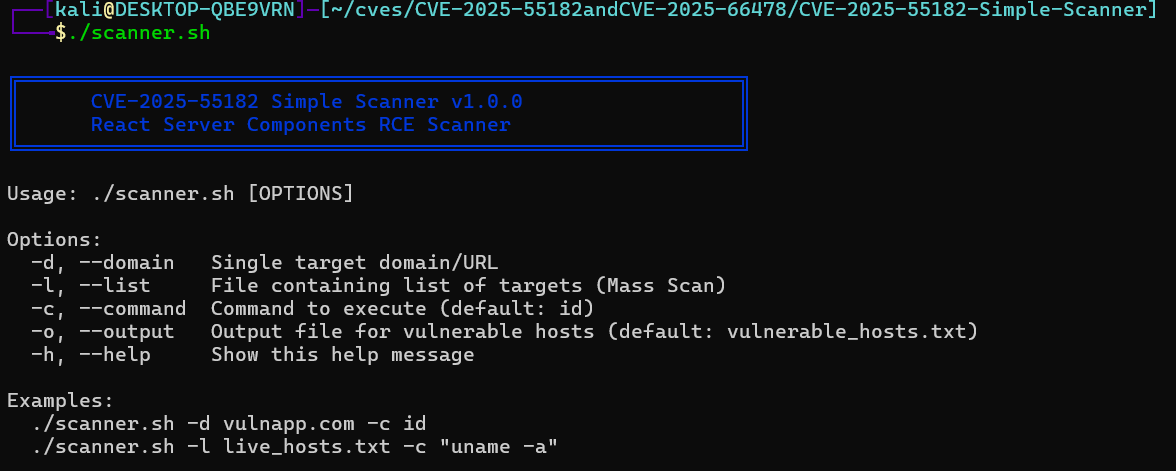 satriarizka/cve-2025-55182-simple-scanner
High-fidelity RCE scanner for CVE-2025-55182 affecting Next.js RSC. Supports mass scanning, command execution, and automated recon pipelines. Built…