

ARTEX
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
ai-securityinformation-gatheringnetwork-mapping+9
855
baarai/artexLLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
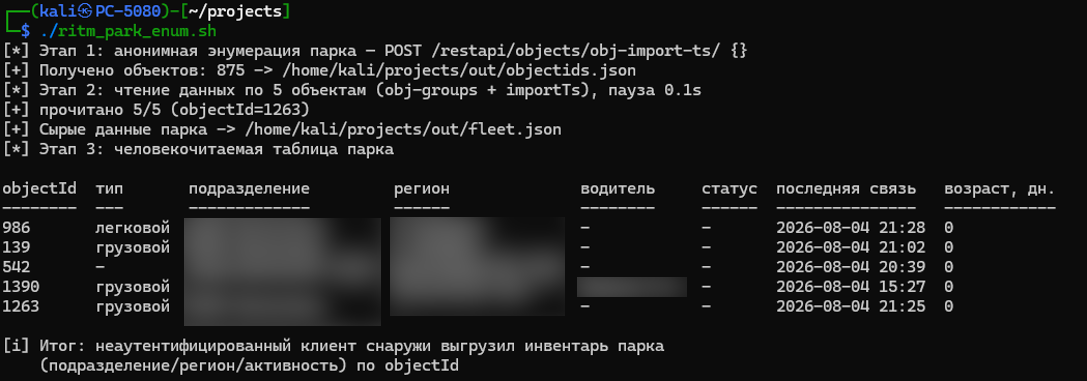 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 nu11secur1ty/cisco
Security auditing toolkit for Cisco network devices, focusing on configuration review, vulnerability detection, and penetration testing of enterprise…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 l1lf1ng3r/heartbleed-vulnerability-exploitation
hands on investigation of the heartbleed vulnerability (CVE-2014-0160).
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 fishjojo1/devin-cve48384-1789318364-1162143-parent
Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.