
RedGhost
 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
command-and-controllateral-movementpayload-generation+5
d4rk007/redghostLinux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 syssec-kaist/ltesniffer
An Open-source LTE Downlink/Uplink Eavesdropper
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 beyarz/portforge
Lightweight utility to fool port scanners
 redsiege/just-metadata
Just-Metadata is a tool that gathers and analyzes metadata about IP addresses. It attempts to find relationships between systems within a large…
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 adminempire/meshdeck
MeshDeck port for Arch Linux ARM - Wilson
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
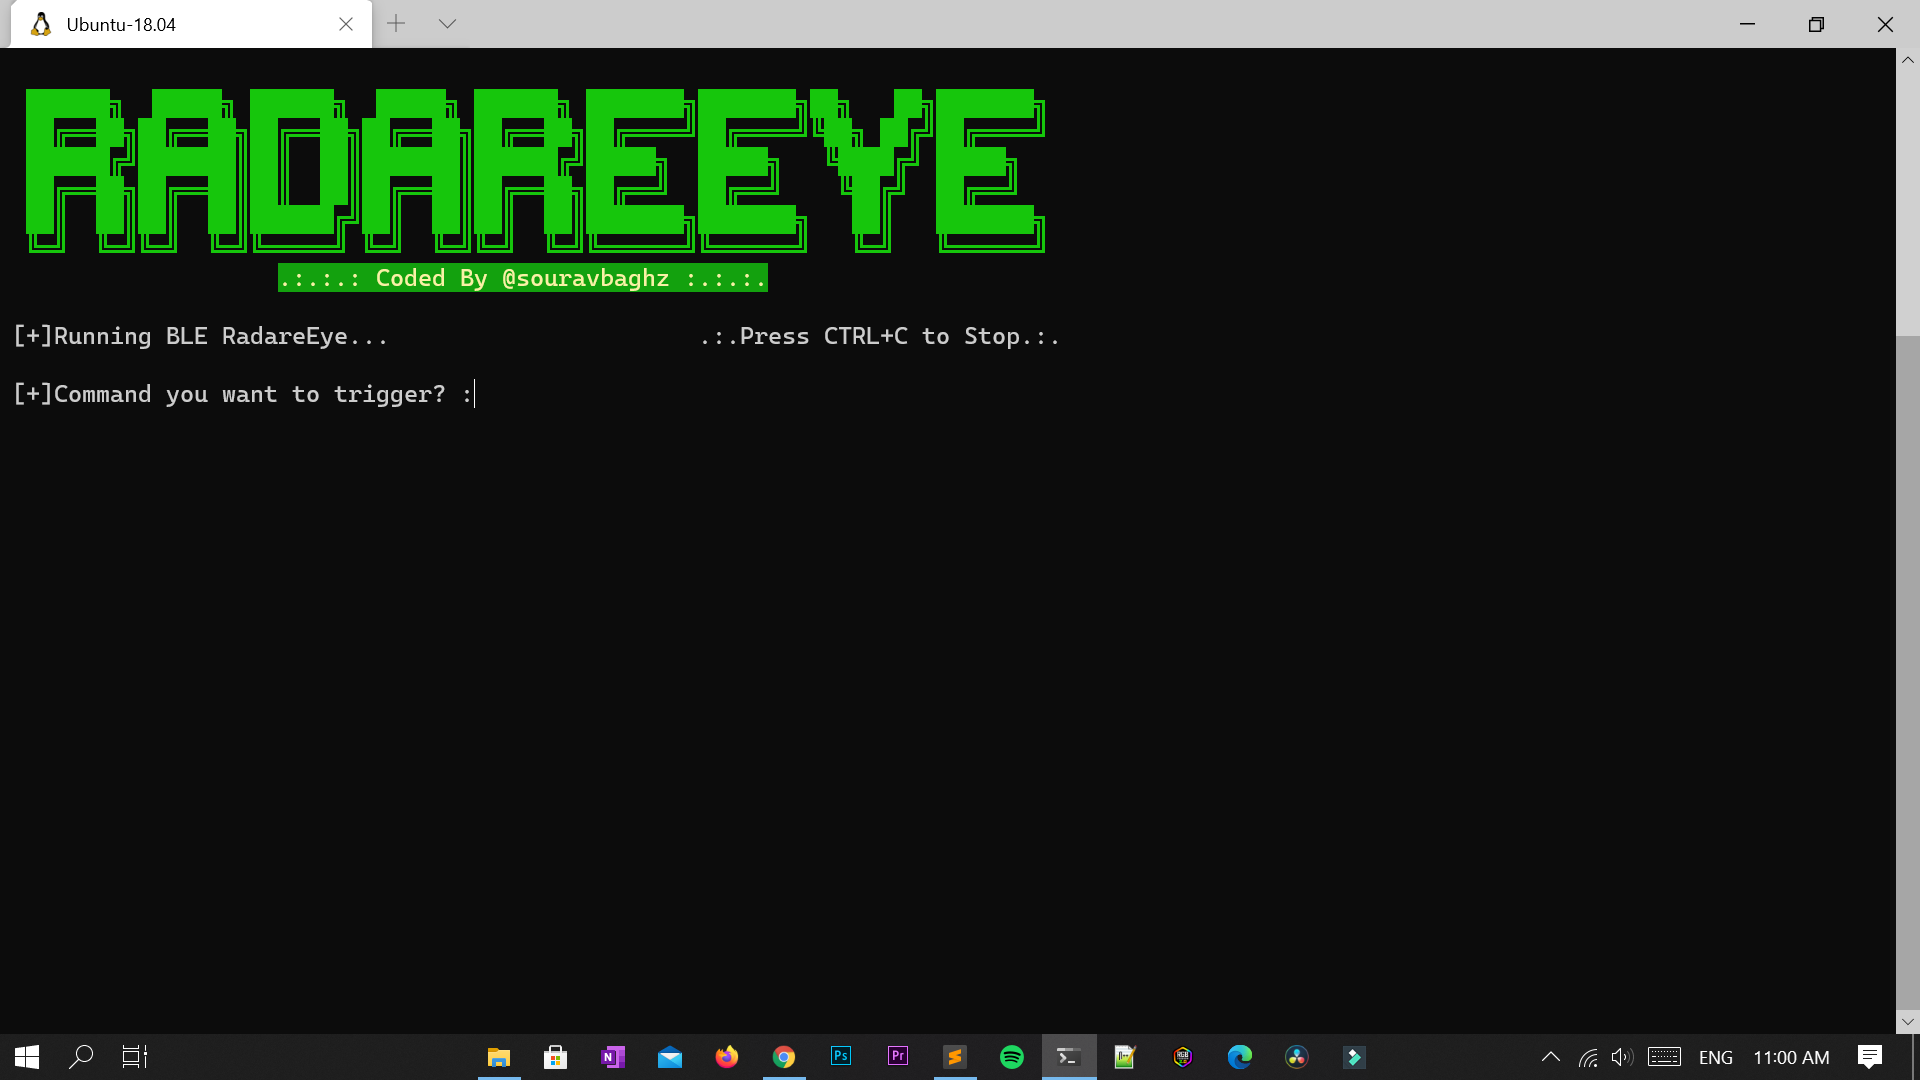 souravbaghz/radareeye
Tool for especially scanning nearby devices and execute a given command on its own system while the target device comes in range.
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
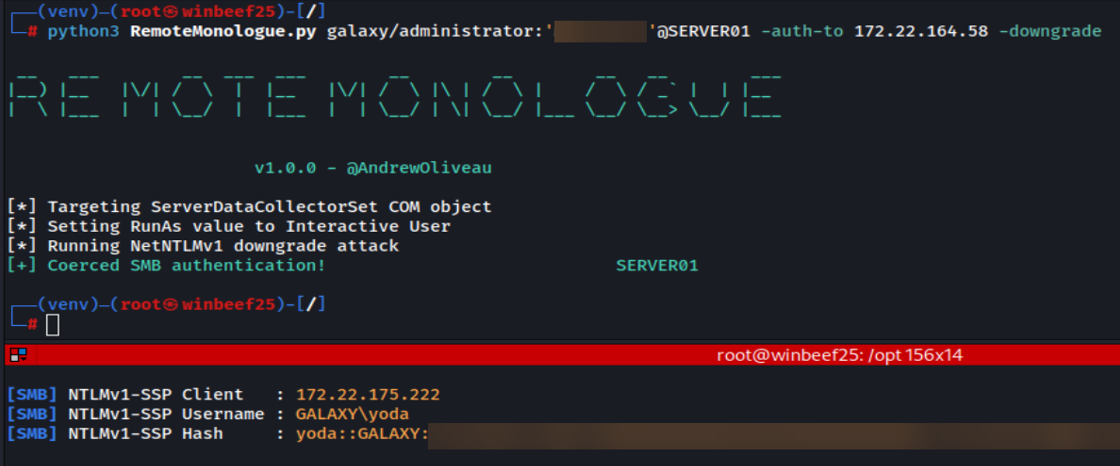 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 eth0izzle/the-endorser
An OSINT tool that allows you to draw out relationships between people on LinkedIn via endorsements/skills.