

TOP
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
curated-resourcesexploitationpenetration-testing+4
ghosttroops/topTOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 mrdebora/cups-2.4.16-lpe
CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)
 khush-613/cve-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
 dennisdgr/cve-2026-34990-poc
LPE PoC for CVE-2026-34990 using a CUPS root file write vulnerability.
 gbuyssens/cve-2026-34990
Local privilege escalation against a root `cupsd`.
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
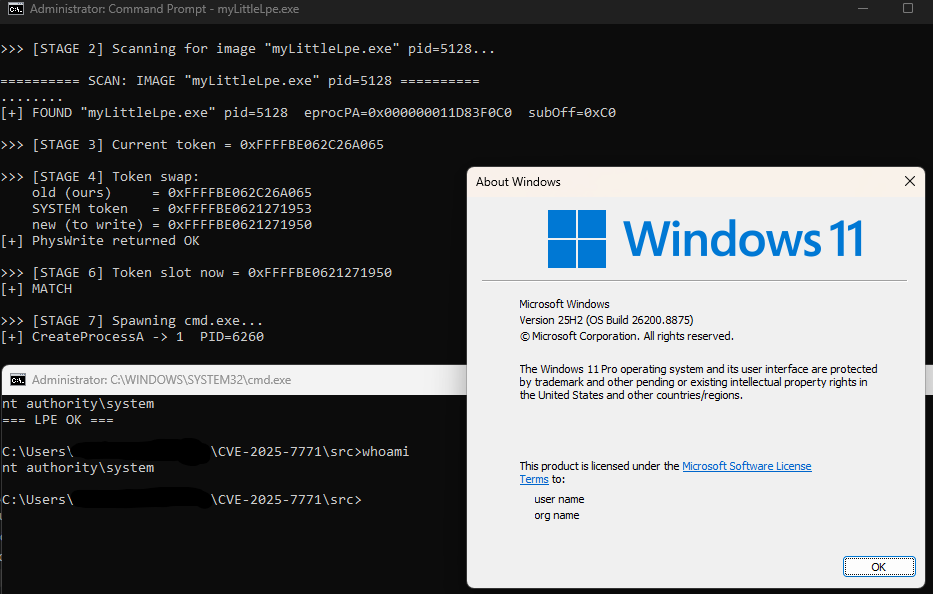 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…