CVE-2026-78006-CVE-2026-78159

Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Verified PoC and analysis for a Linux perf/core permission-check bypass that leaks kernel callchain addresses to unprivileged Android tasks, enabling…

Toolkit for CVE-2026-98432 Linux TCP use-after-free: kernel patch checks, race oracle triggering, pcap UAF analysis, KASLR slide recovery, and…

AI-Powered Active Directory Attack Platform

Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…

一个攻防知识库。A knowledge base for red teaming and offensive security.

A comprehensive collection of penetration testing cheatsheets, guides, and tools.

Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777

Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…

Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…

Captures Windows Hello PINs at entry by injecting a DLL into LogonUI.exe that sets a CPU hardware breakpoint on NgcSerializeConvenienceCredential,…

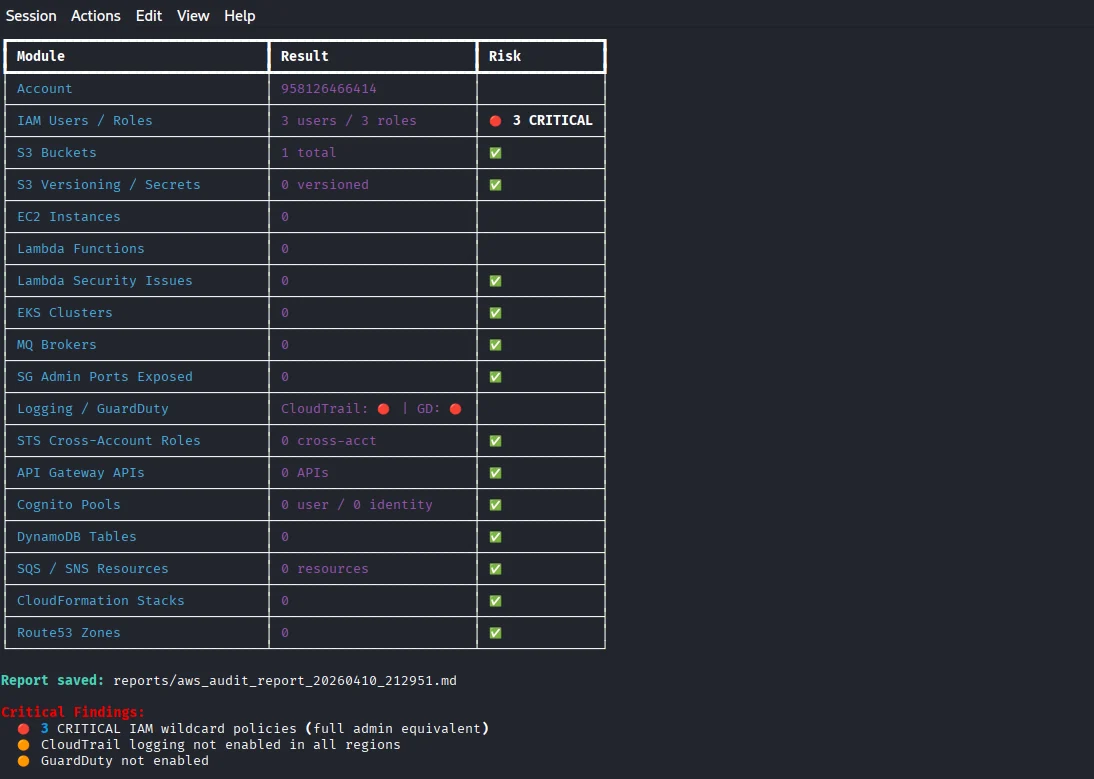
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…

Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…

pfSense Plus MIM API toolkit b4acd7ca - High - Local - Privilege leftover - unix sock enroll no JWT

Active Directory recon and read-only security audit over ADWS (net.tcp/9389), in Go

An interactive command-line shell for BloodHound API.

Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…