
ContextMenuHijack
 ristbs/contextmenuhijack
Execute a payload at each right click on a file/folder in the explorer menu for persistence
payload-developmentpersistence-mechanismspost-exploitation+1
173
ristbs/contextmenuhijackExecute a payload at each right click on a file/folder in the explorer menu for persistence
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 ustayready/wnfexec
WNF Code Execution Library Using C#
 ustayready/casperstager
PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
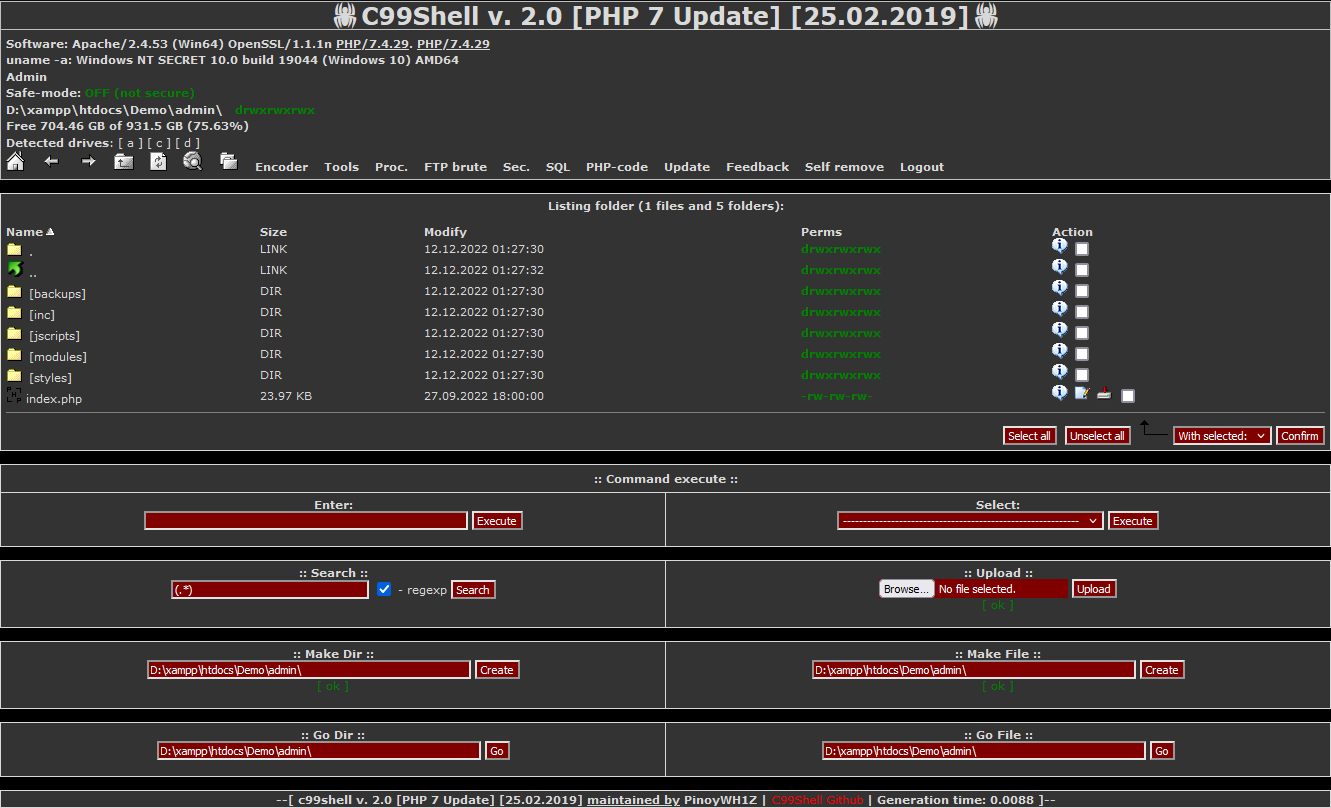 pinoywh1z/c99shell-php7
PHP 7 and safe-build Update of the popular C99 variant of PHP Shell.
 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
 horizon3ai/vrealizeloginsightrce
POC for RCE using vulnerabilities described in VMSA-2023-0001
 octoberfest7/eventvieweruac_bof
Beacon Object File implementation of Event Viewer deserialization UAC bypass
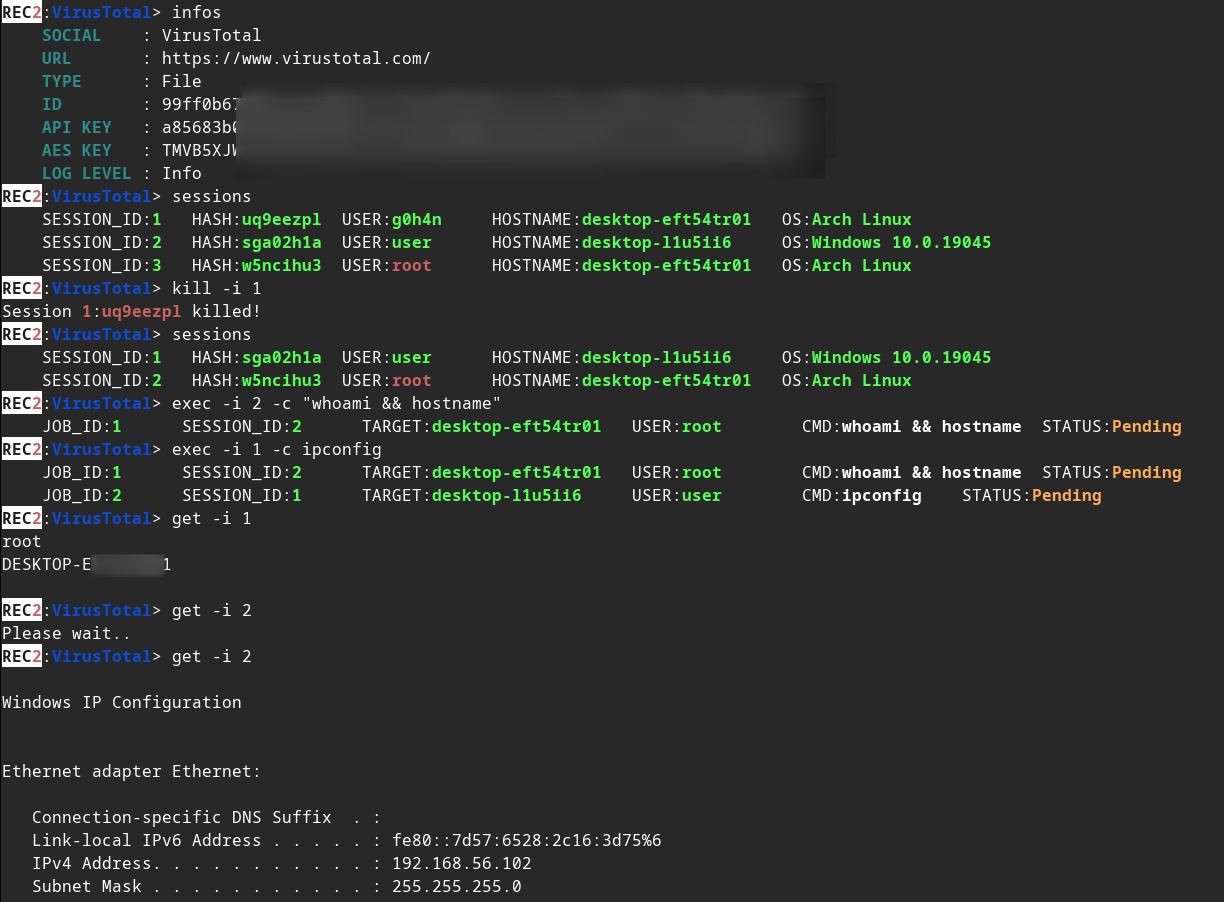 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 je5442804/wptaskscheduler_cve-2024-49039
WPTaskScheduler RPC Persistence & CVE-2024-49039 via Task Scheduler
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell