

redamon
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
ai-securityexploit-frameworkslateral-movement+8
samugit83/redamonAutonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
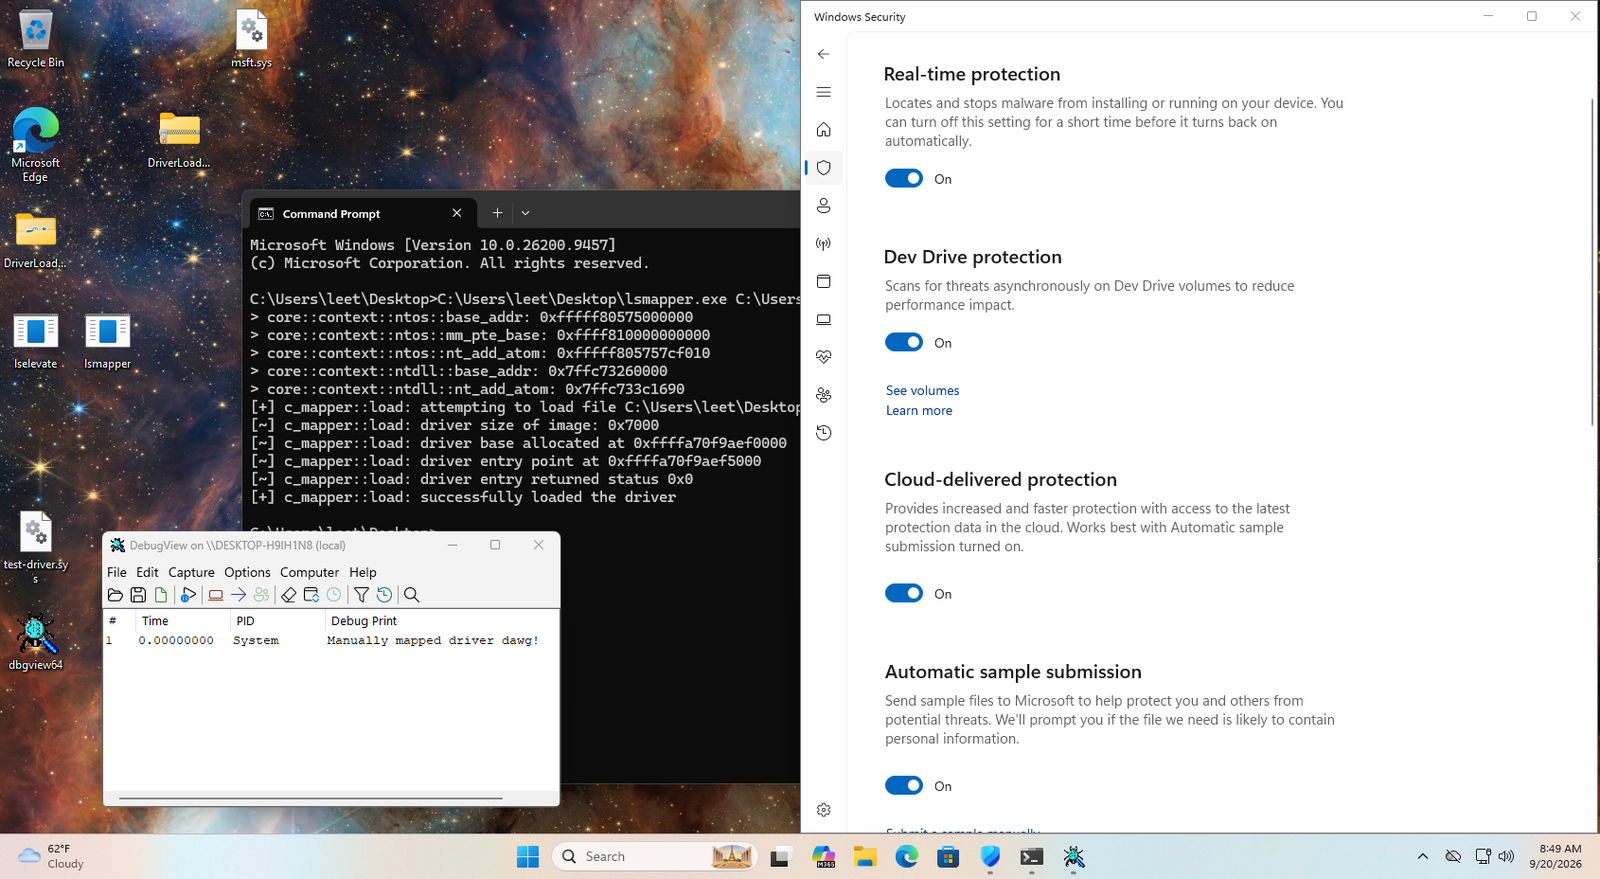 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 zeromemoryex/tokenizer
Simple Kernel Mode Driver for Swapping Process Token
 synacktiv/gpoddity
Automates Active Directory GPO exploitation via NTLM relaying, enabling malicious GPO template generation, location spoofing, and command execution…
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 anirbala98/cve-2026-67206
PoC exploit for Wolf CMS <= 0.8.3.1: authenticates to Admin, writes an arbitrary PHP file to /public via FileManagerController, and executes commands…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
 khalilu020/offensive-security-adversary-emulation
Simulated a real-world attack (CVE-2011-2523) against a vulnerable host, then cross-checked detection coverage against an existing…
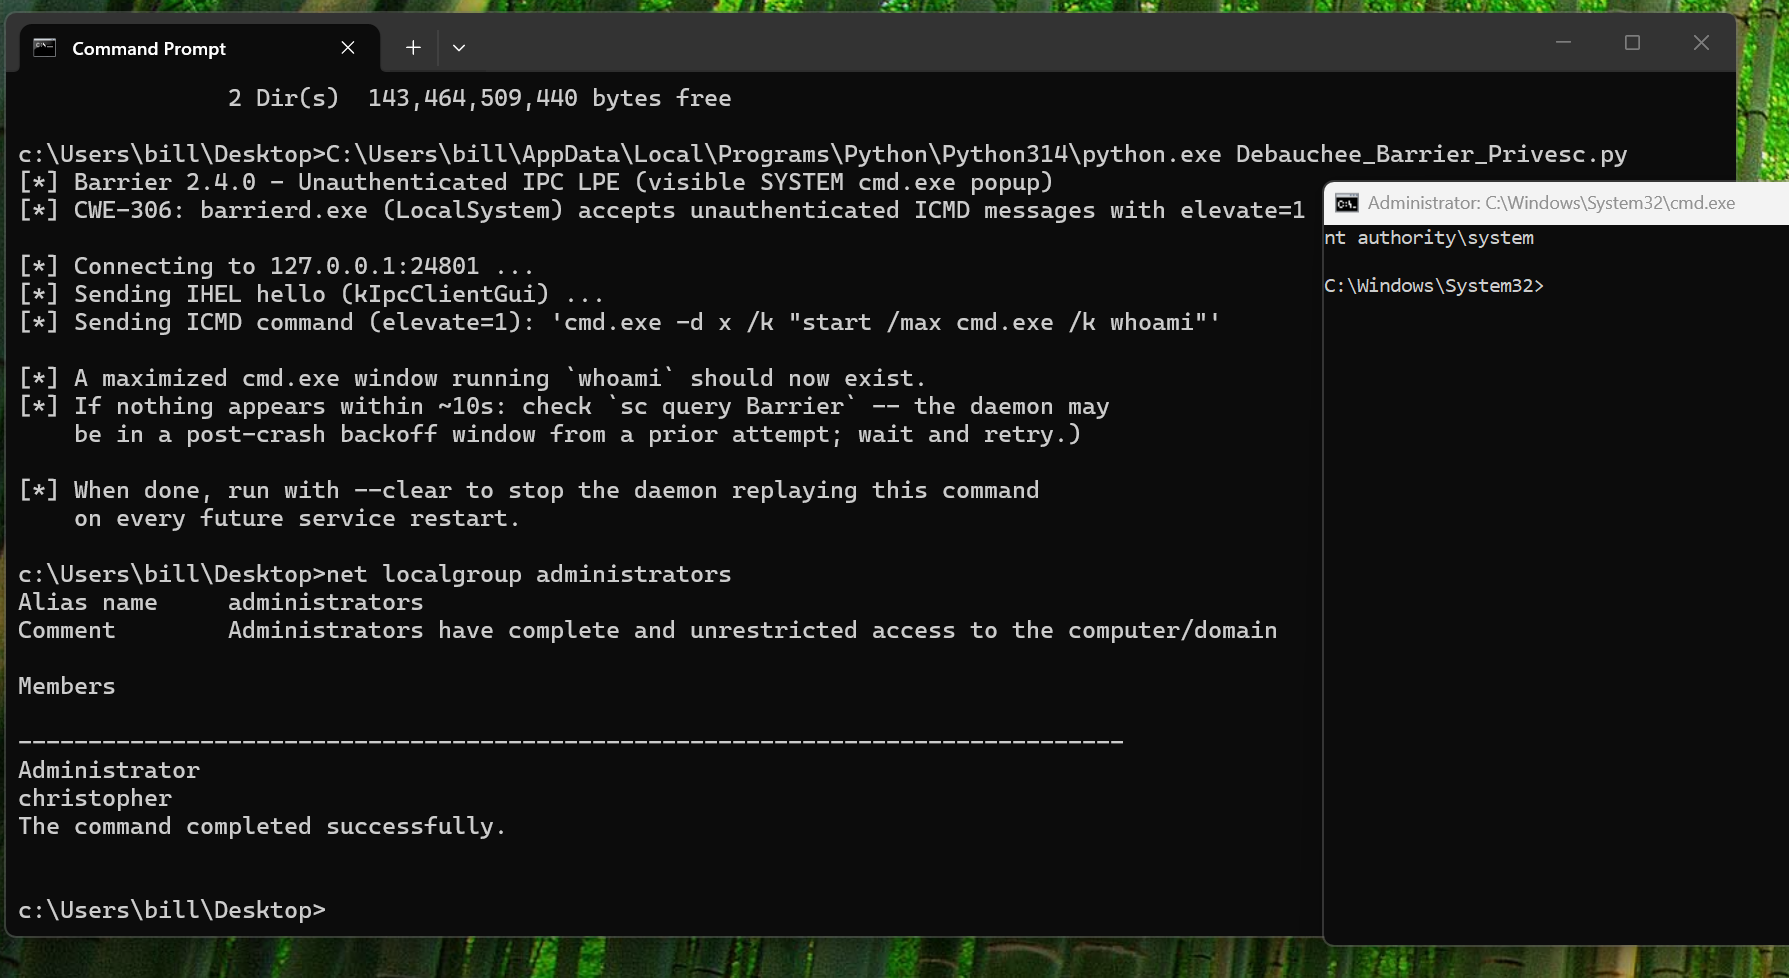 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
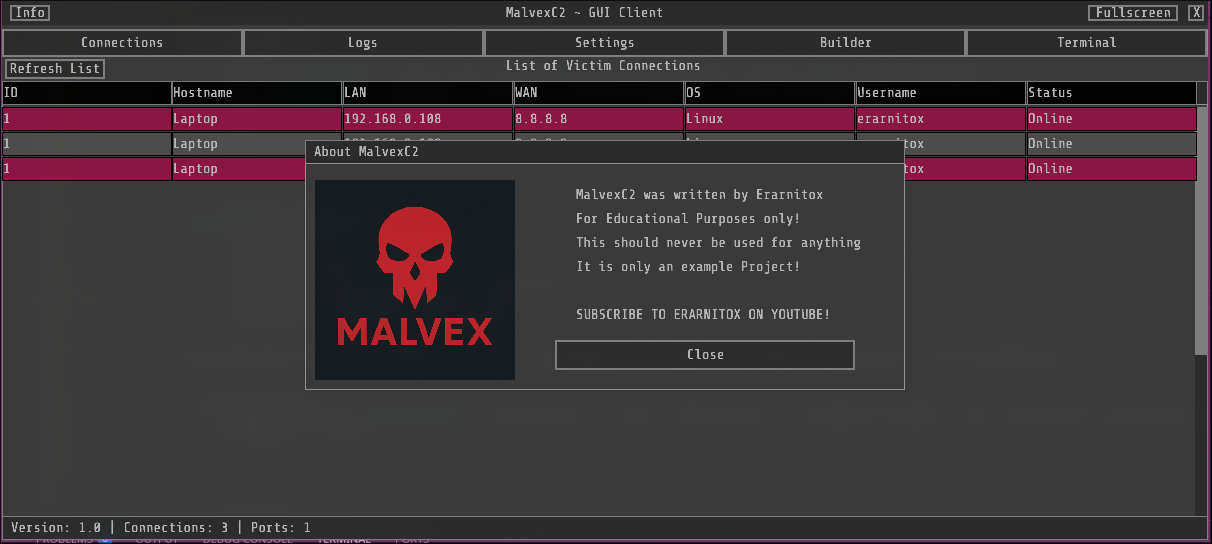 erarnitox/malvexc2
A simple C2 Framework written in modern C++
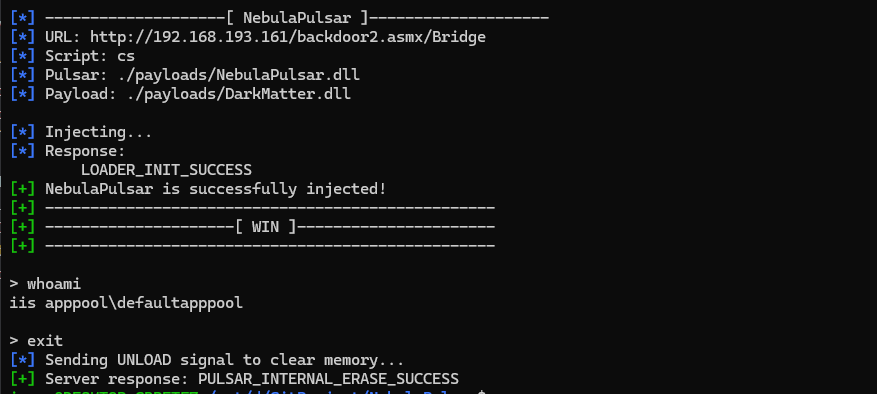 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
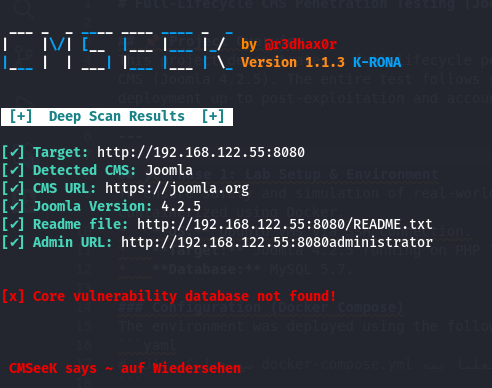 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment