
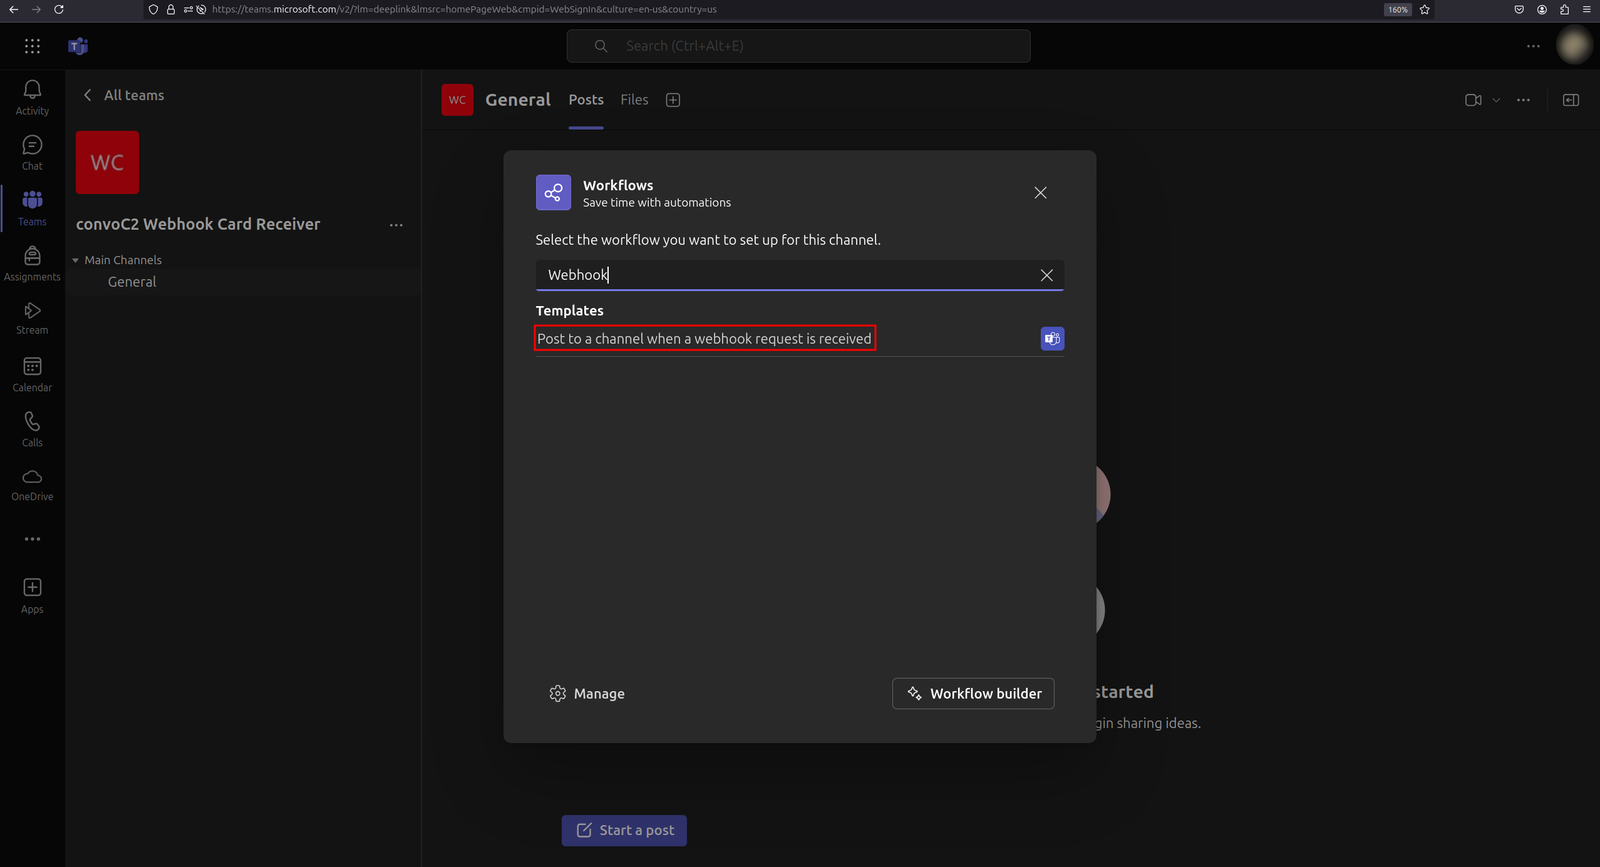
convoC2
 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
command-and-controldata-exfiltrationids-ips-evasion+6
cxnturi0n/convoc2C2 infrastructure over Microsoft Teams.
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
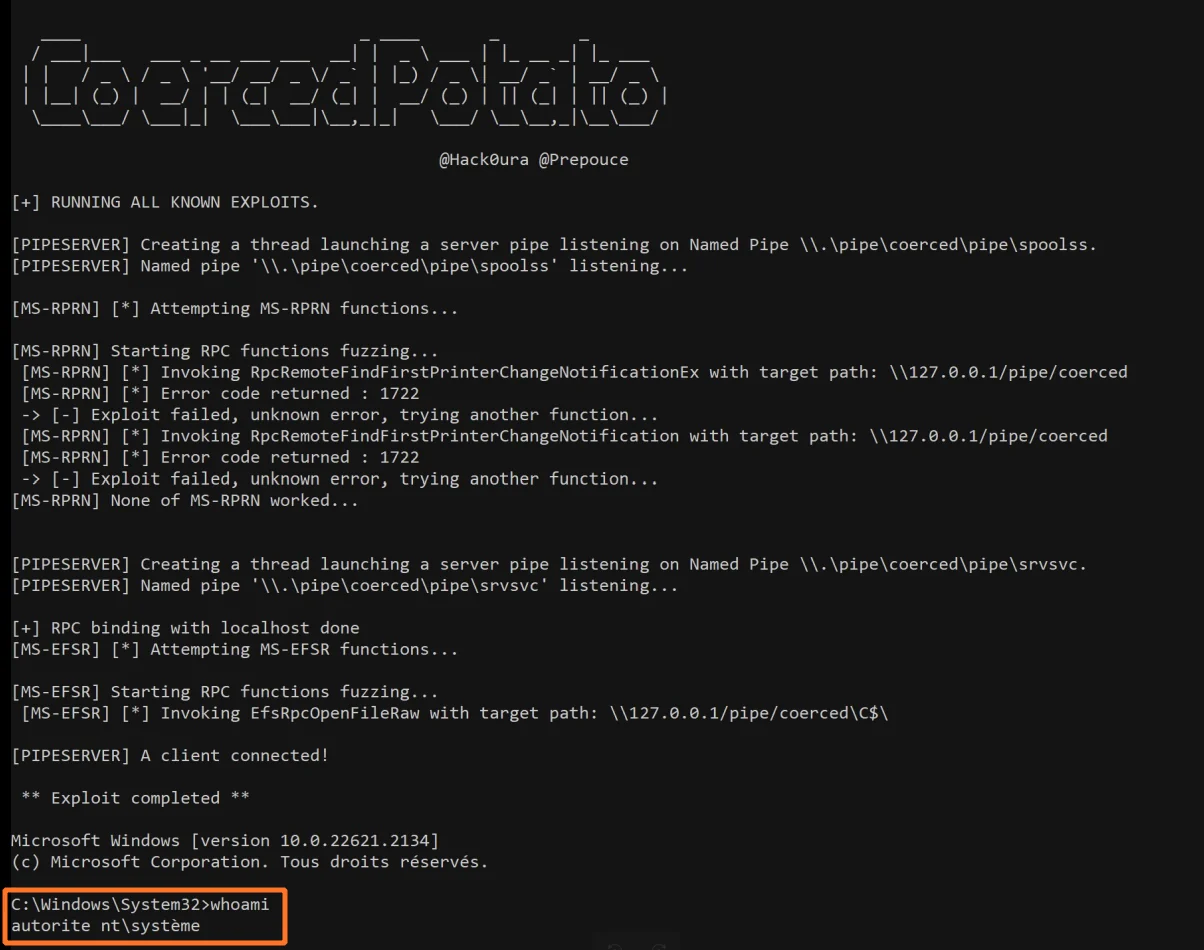 prepouce/coercedpotato
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
 trhhubsd/artex
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 blendin/3snake
Tool for extracting information from newly spawned processes
 ripits-sec/couchpotato
Windows privilege escalation tool that patches ETW and AMSI and uses indirect syscalls to abuse SeImpersonatePrivilege, escalating service accounts…
 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 gmh5225/kernelmode-driver
Kernel Driver for x64 Window System which allows you to read/write Virtual/Physical Memory hooking Win32k
 gmh5225/injection-2
Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 0xsemizzz/cve-2026-92162
Educational write-up and test-mode PoC for CVE-2026-92162, a path traversal in Flatpak's DeployAppstream arch parameter enabling root directory…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 zerodayvpn/cve-2026-24291
About 2026 Guide: Bypass User Account Control Prompts on Windows 11
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…