
CVE-2026-87902-Toolkit
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
defensive-toolseducationexploitation+8
10
tc4dy/cve-2026-87902-toolkitWordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 shlln/cve-2026-90847
Proof-of-concept for CVE-2026-90847, an authenticated RCE in iux_set.cgi via malicious .cfg tar upload that writes commands into crontab for…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
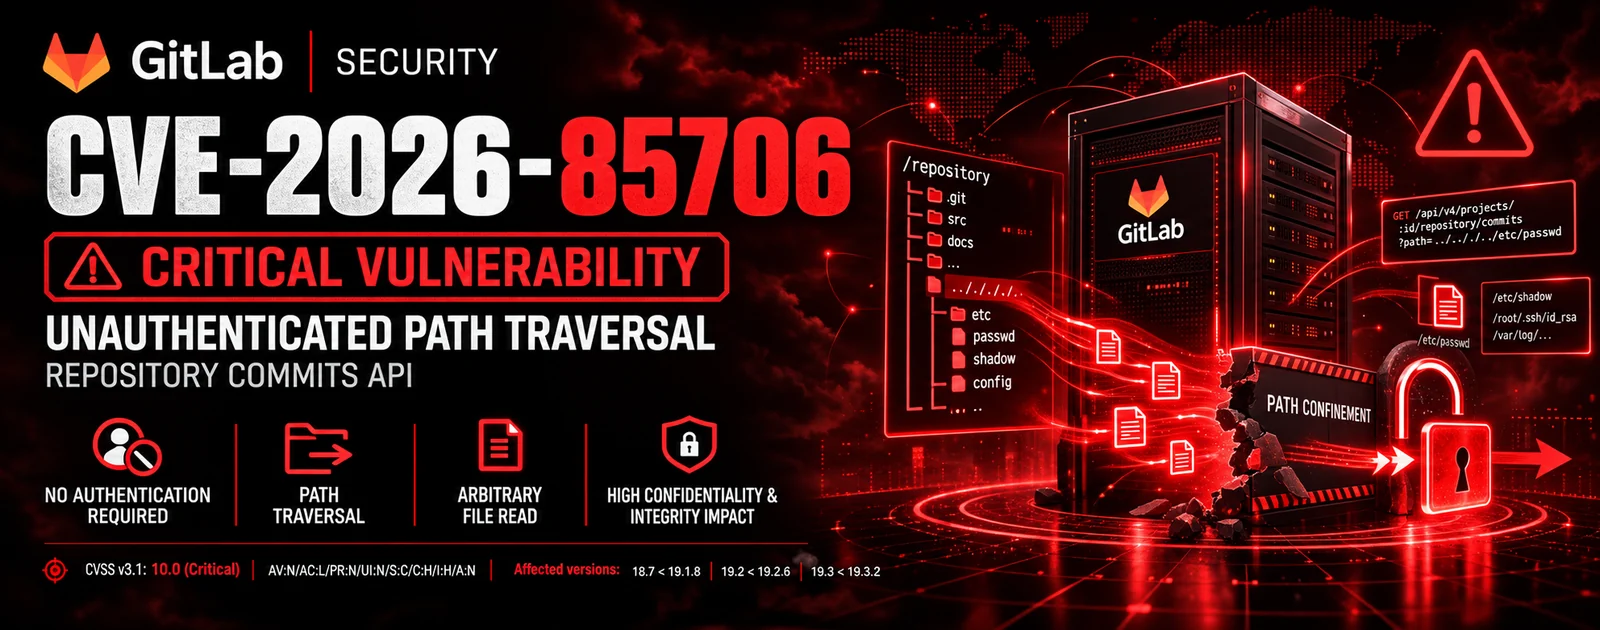 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
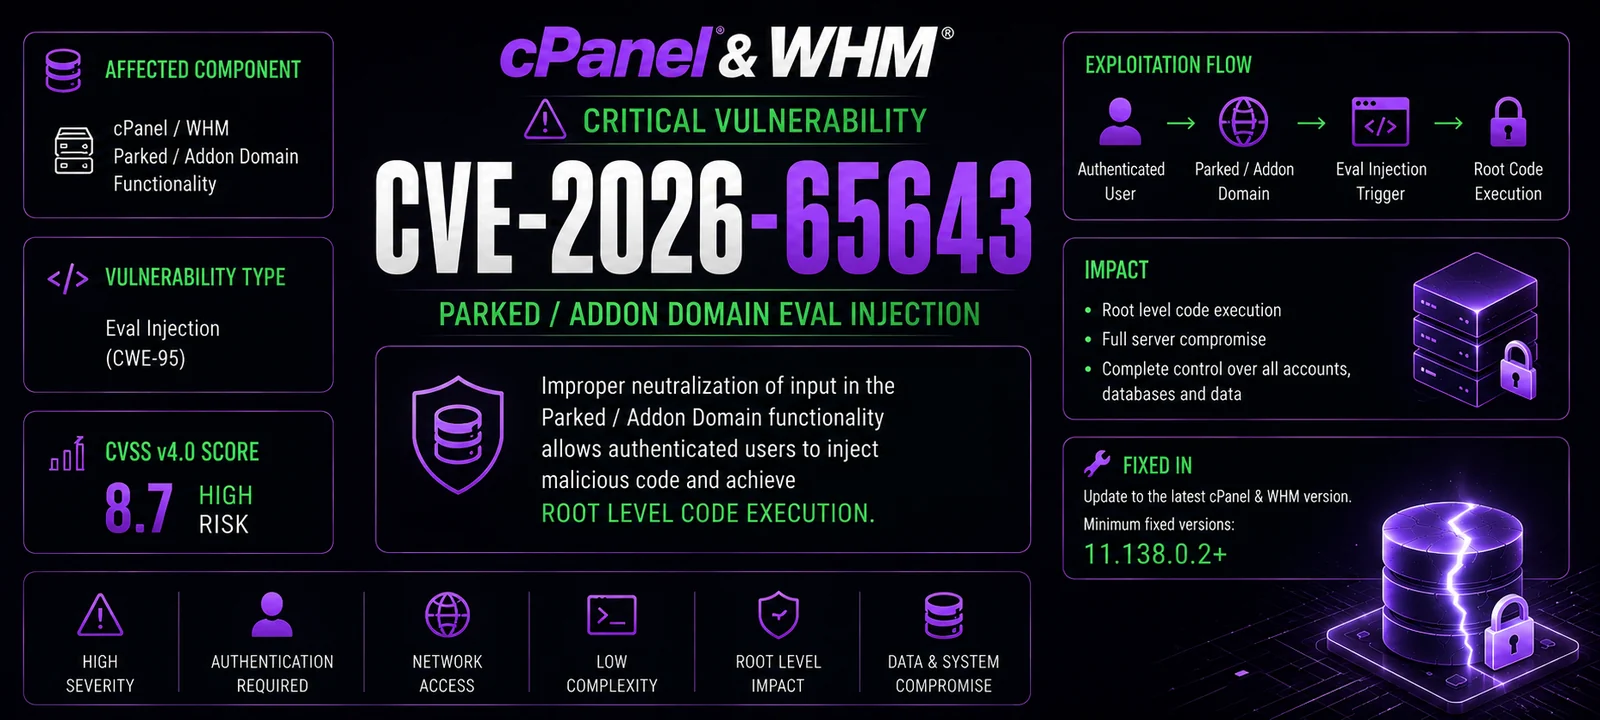 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 mariohy/cve_2026_31431_audit
A security auditing toolkit for CVE-2026-31431 vulnerability research
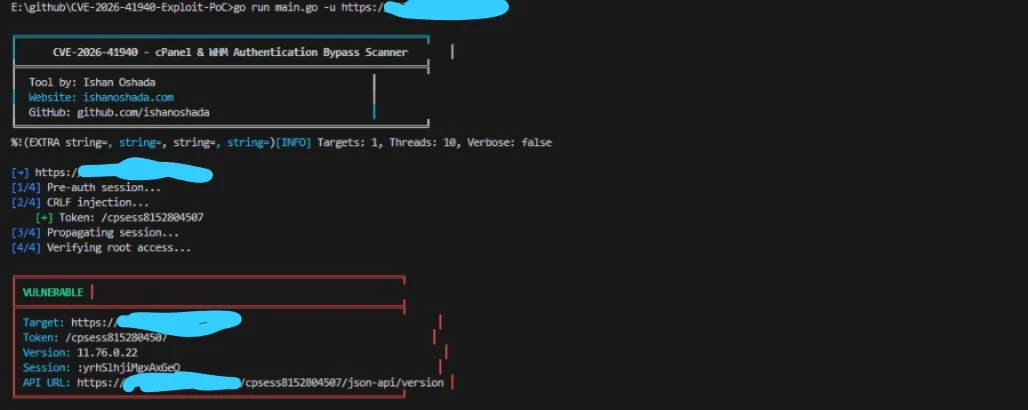 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
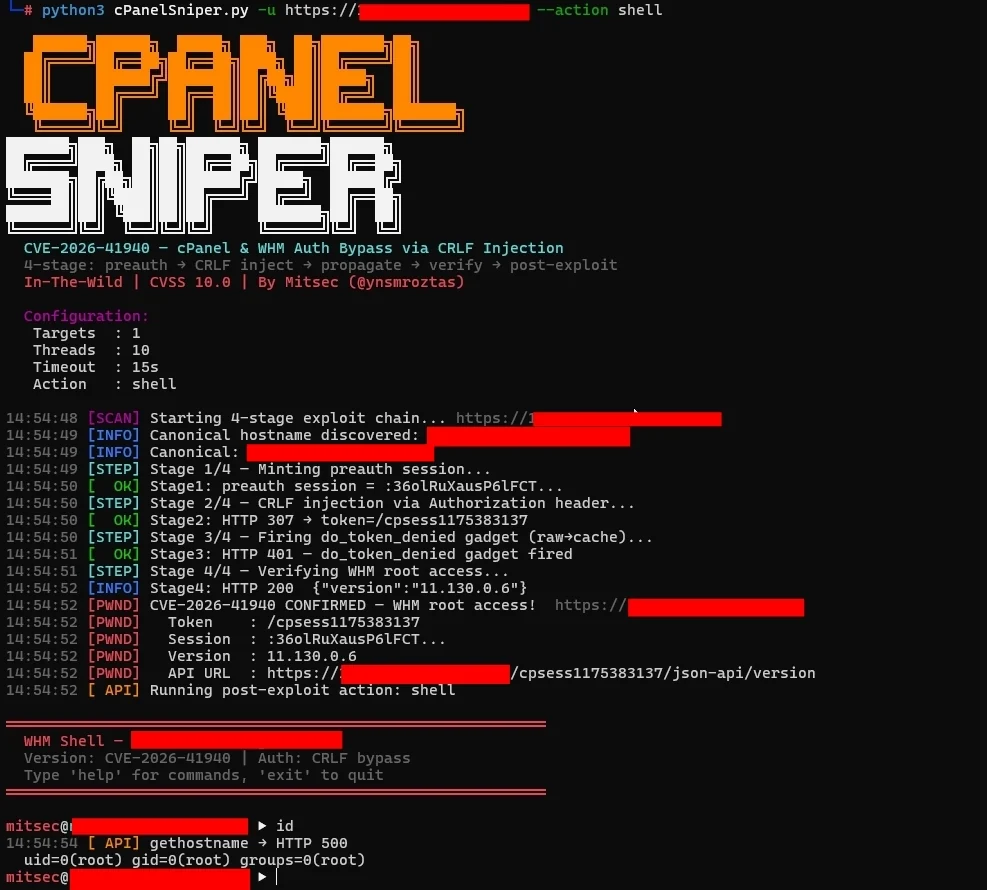 44pie/cpsniper
cPanelSniper STABLE - CVE-2026-41940 optimized for 10M+ targets
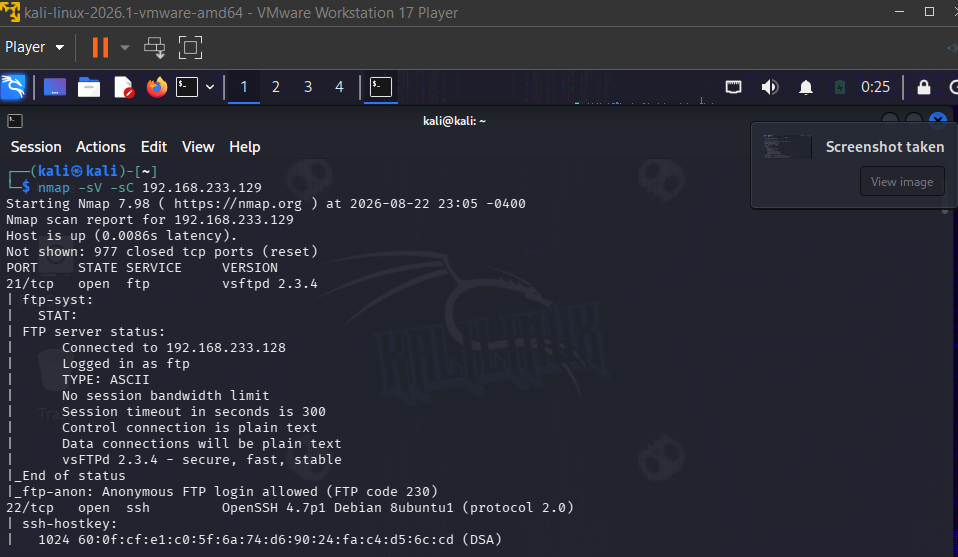 rsakthikumar-cmd/metasploitable2-vsftpd-writeup
Exploiting the vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 — a hands-on pentesting lab writeup covering recon, exploitation, and…
 0xyur1/cve-2026-41940
cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator
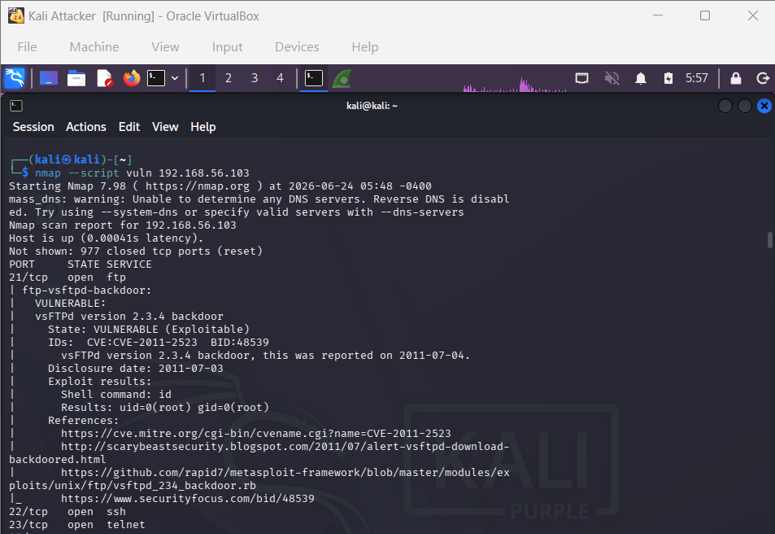 sonalisarkar-2003/ftp-vsftpd-cve-2011-2523-vapt-report
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
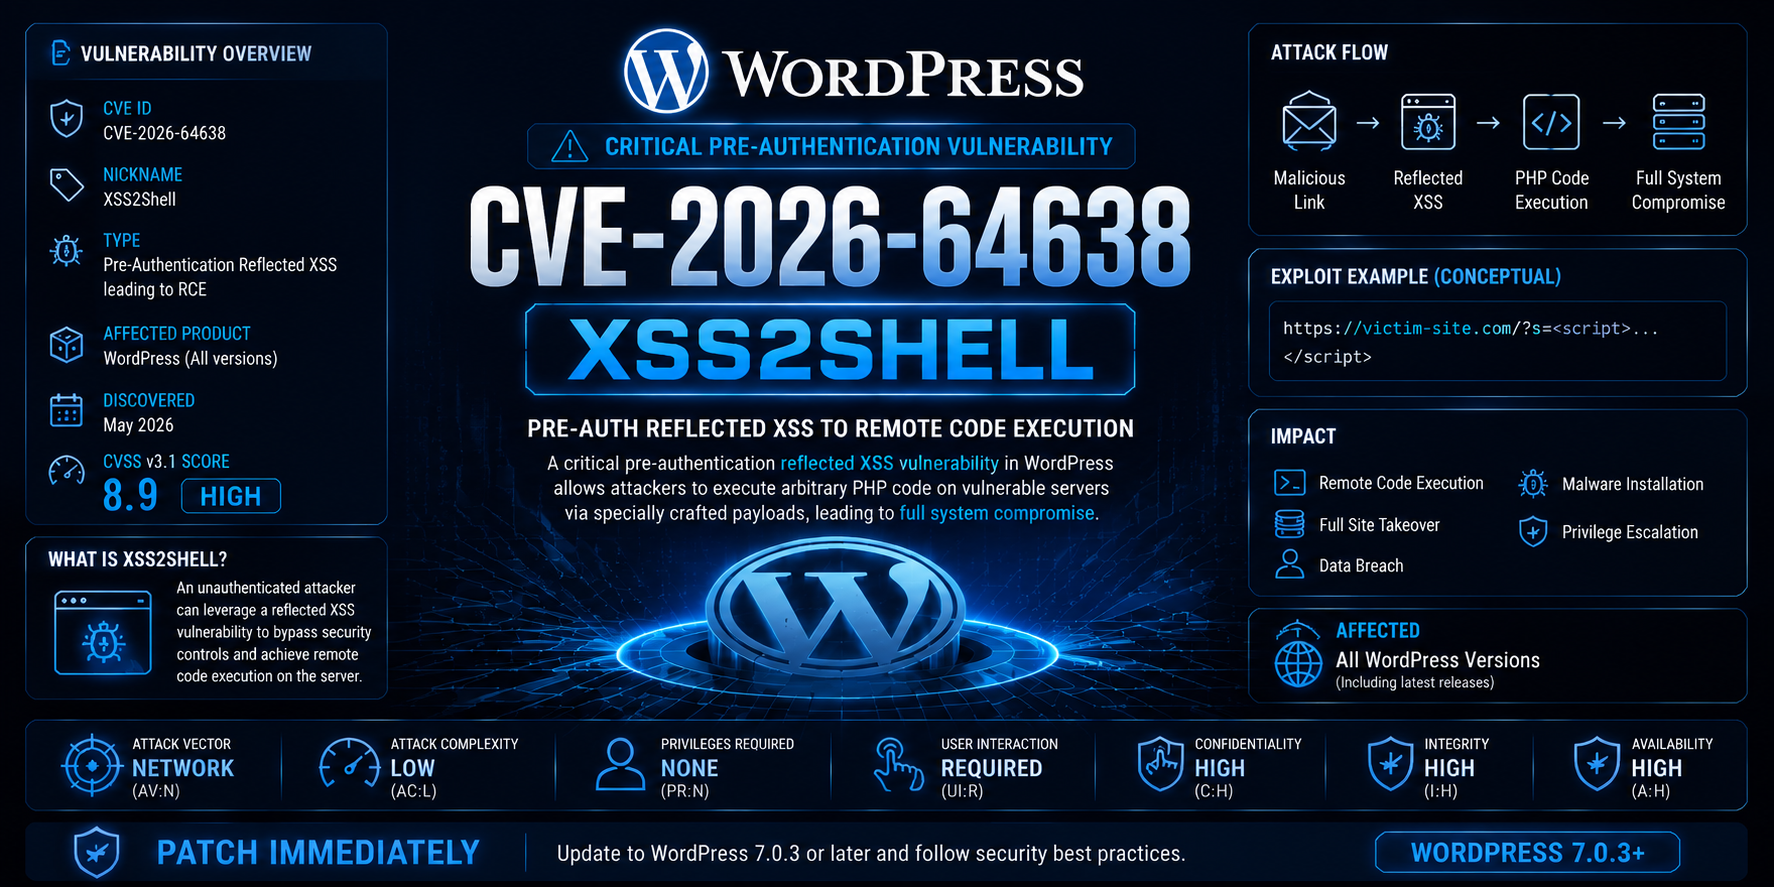 tc4dy/cve-2026-64638-poc-exploit
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…