

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.8k16h 59m ago
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
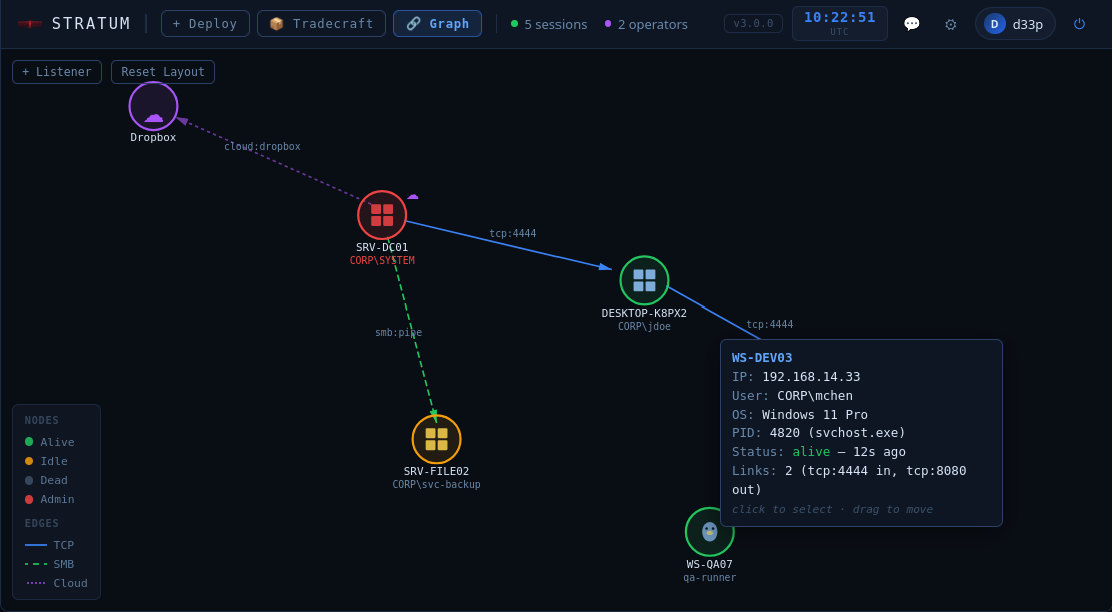 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
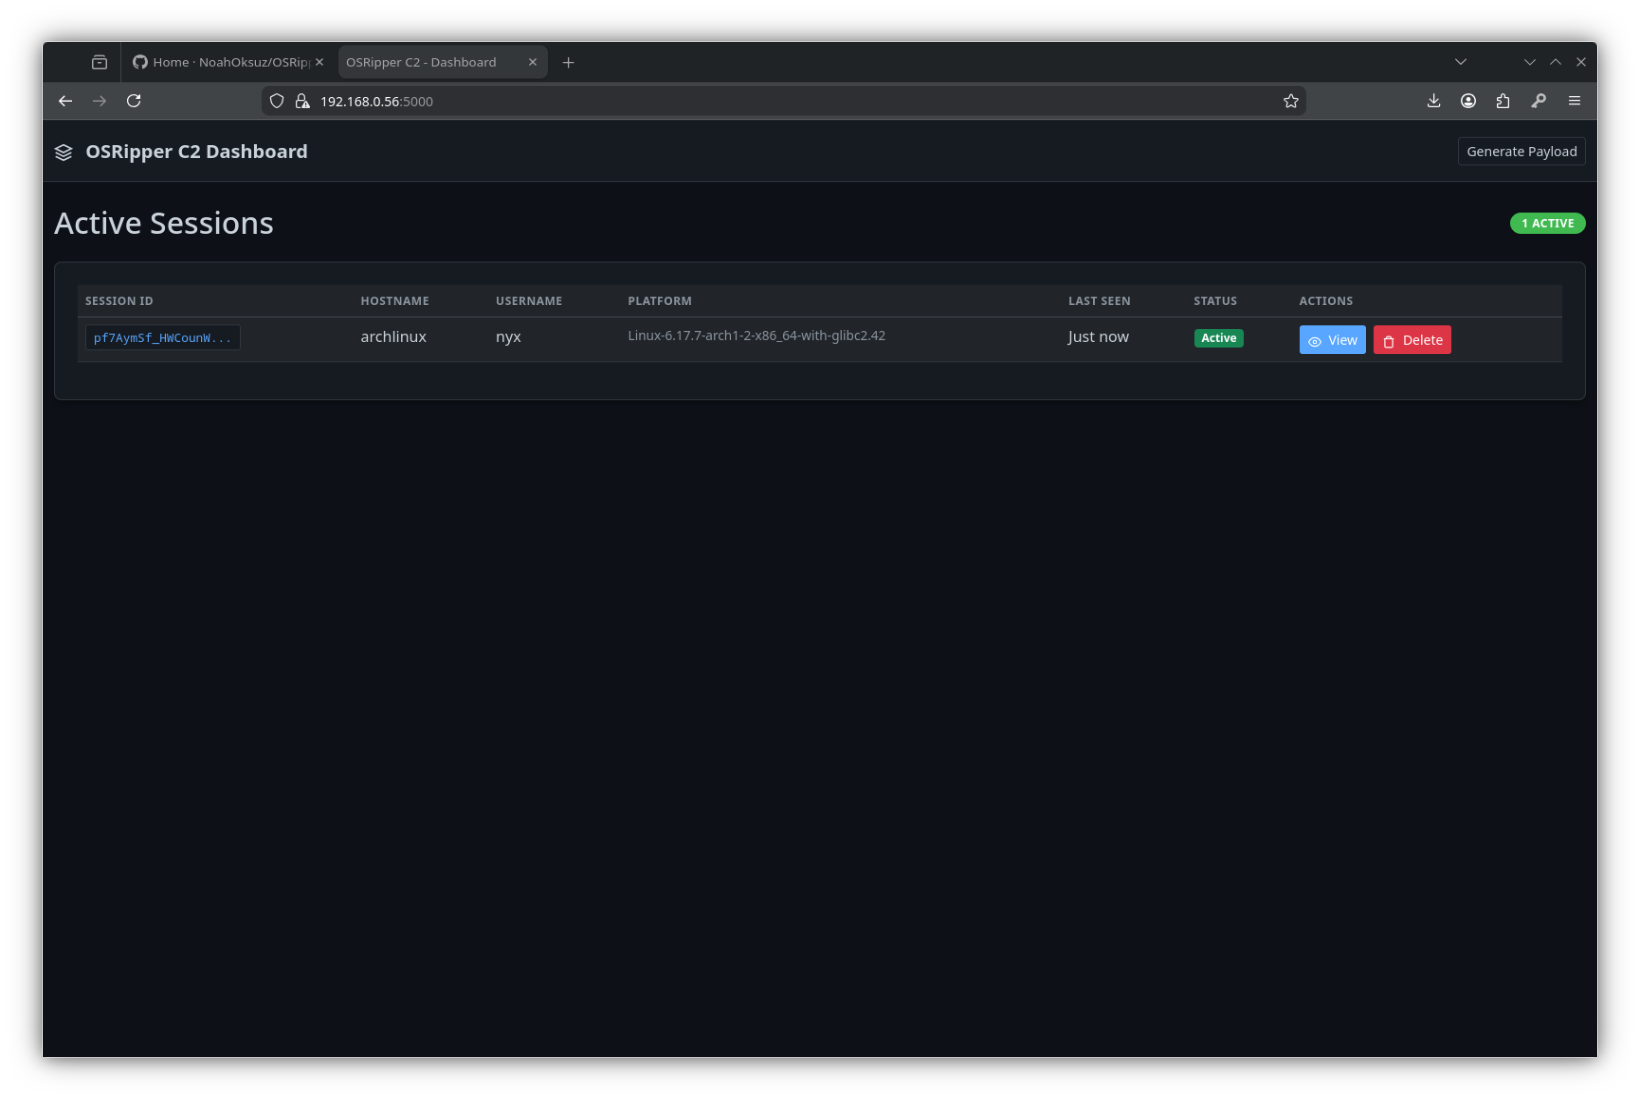 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
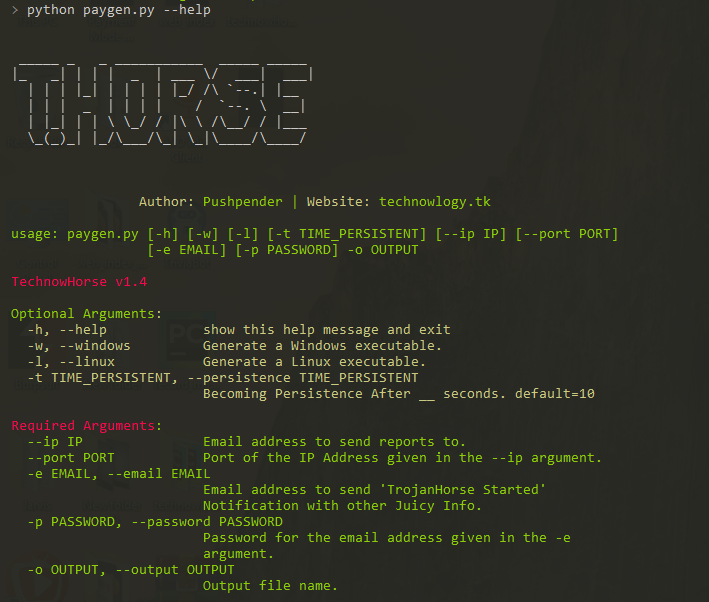 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
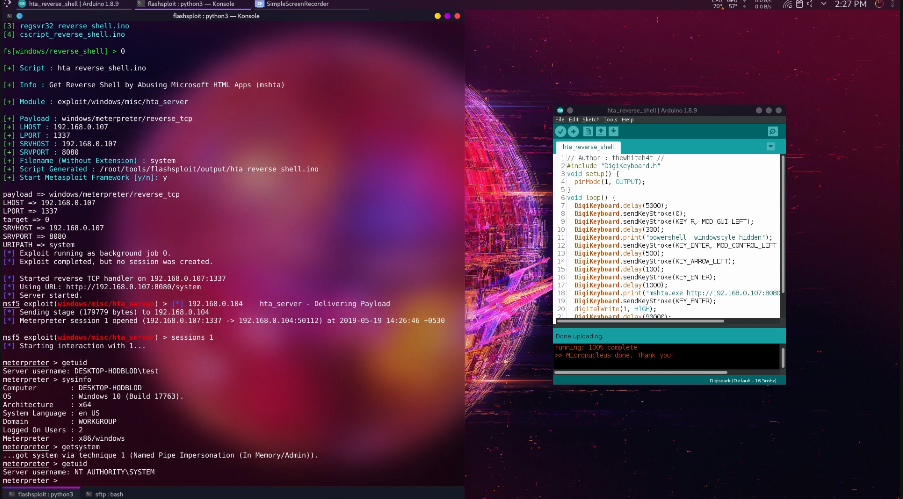 thewhiteh4t/flashsploit
Exploitation Framework for ATtiny85 Based HID Attacks
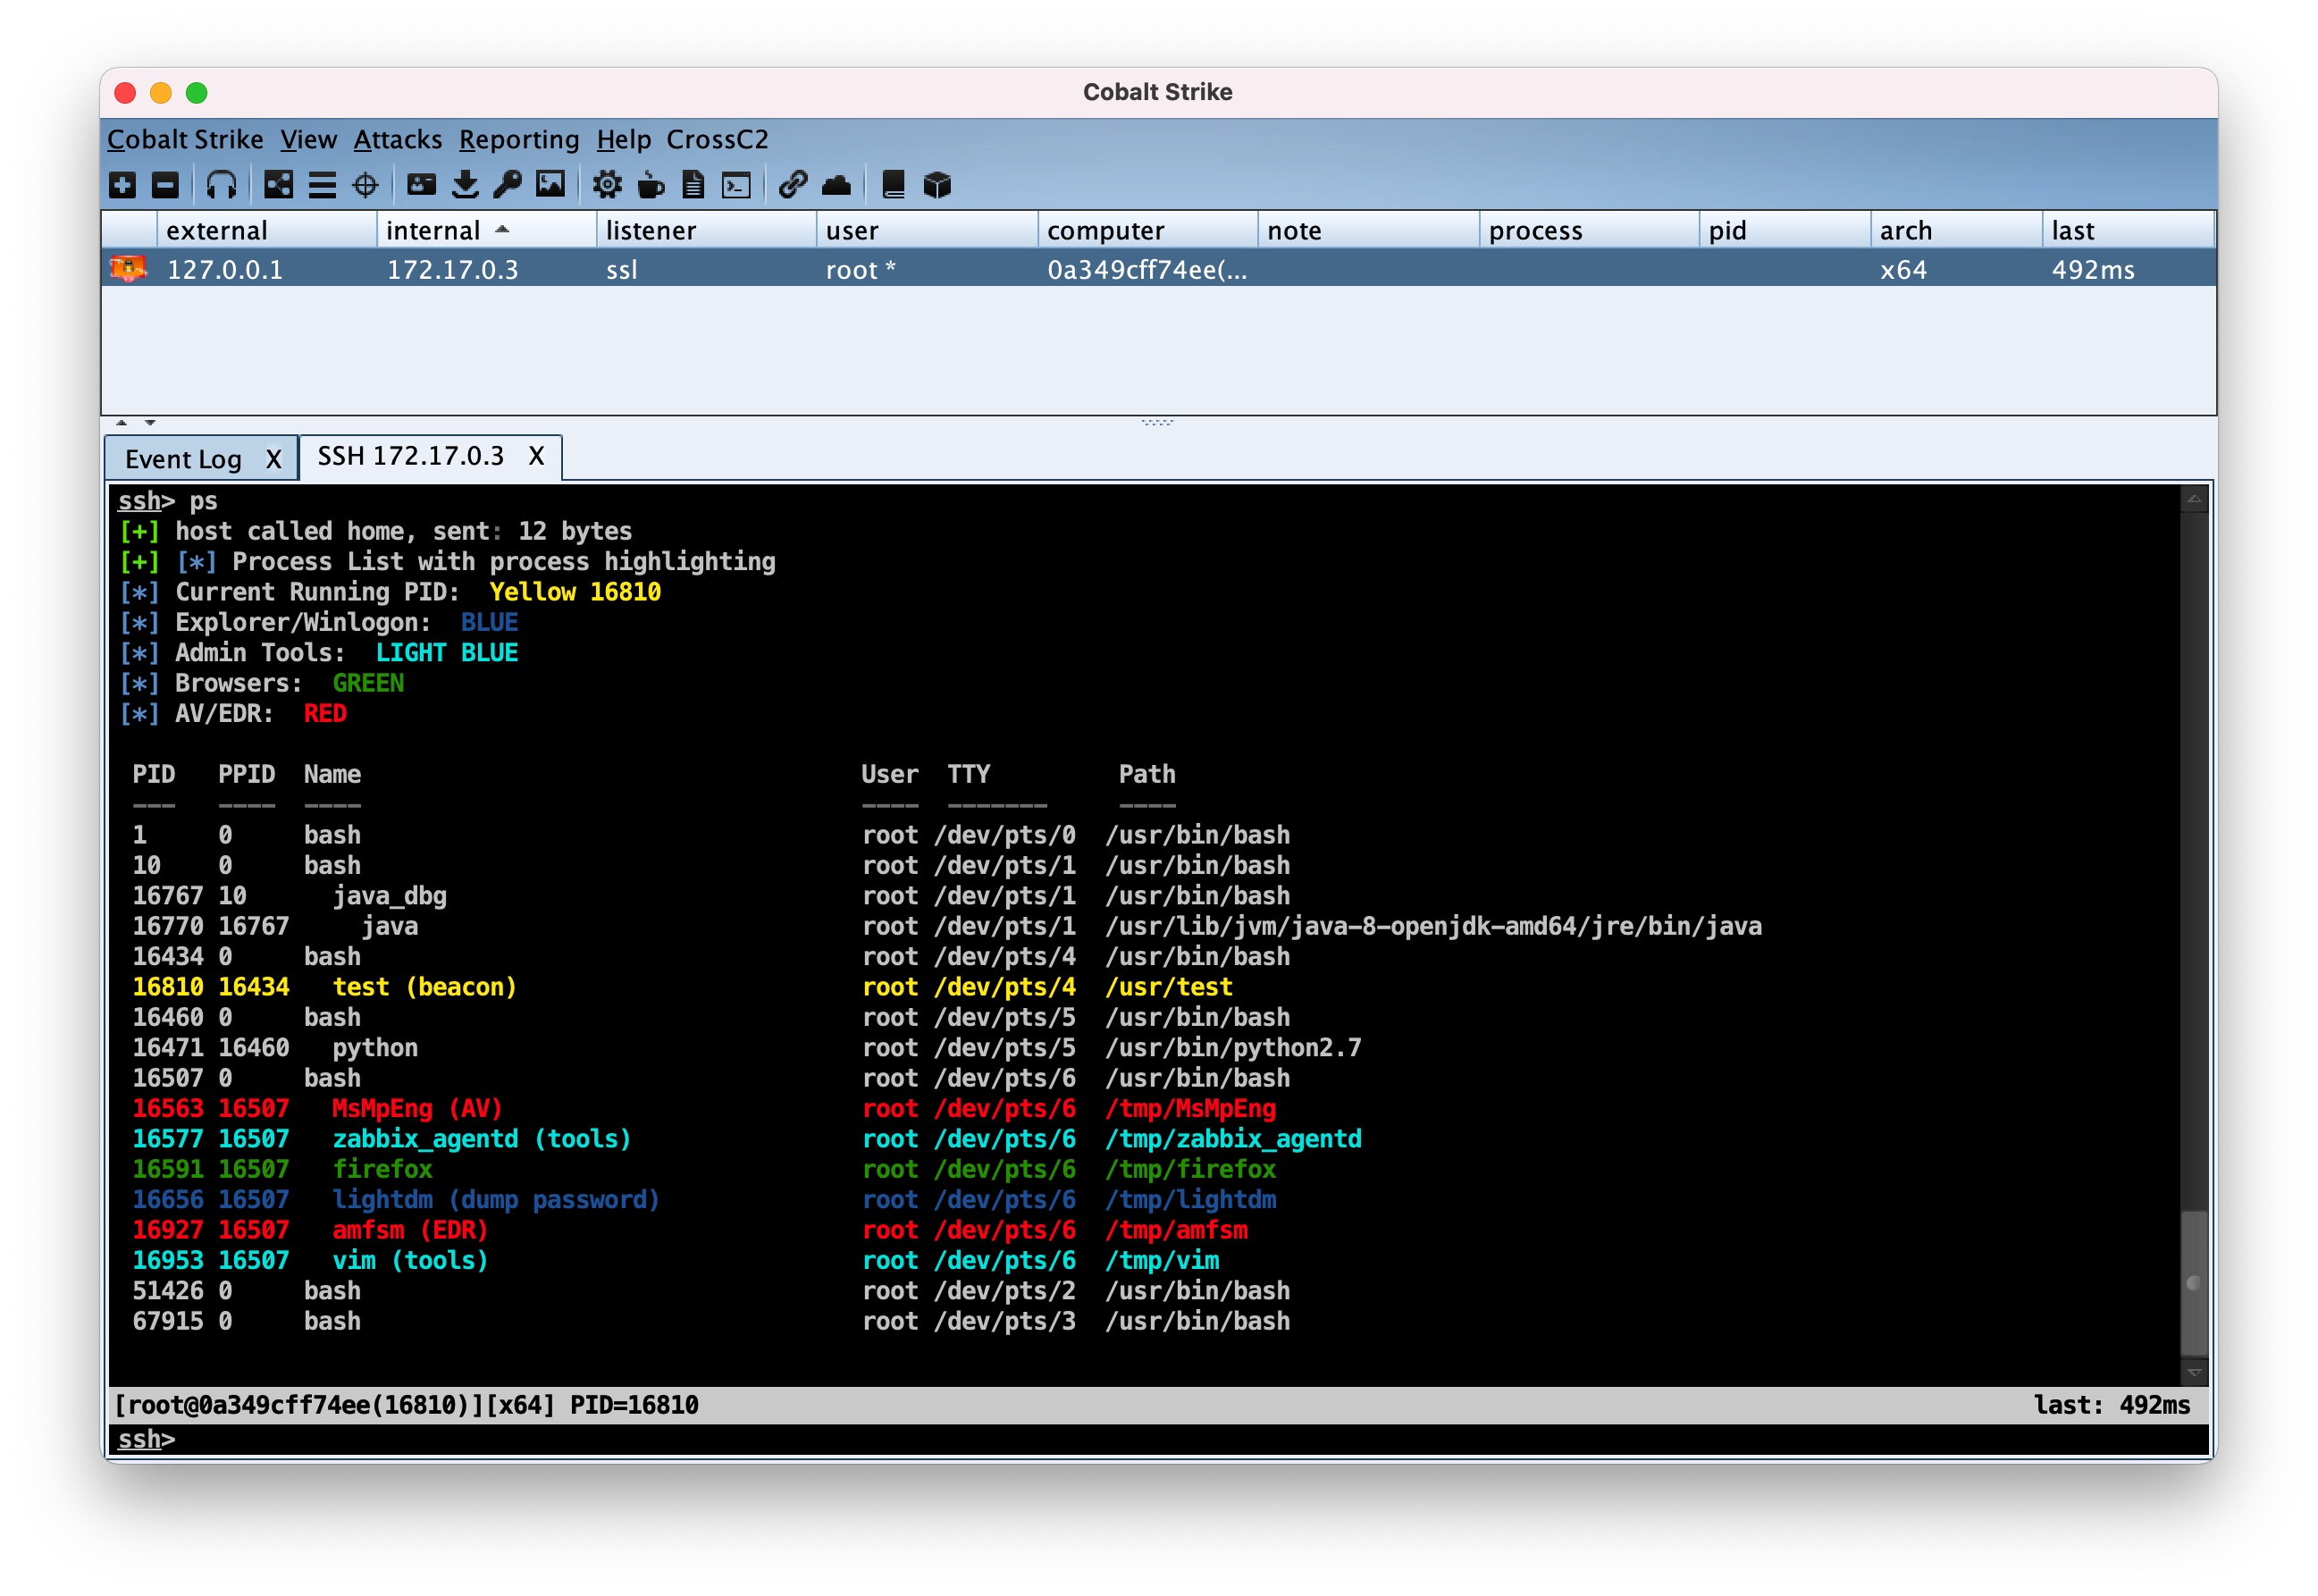 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
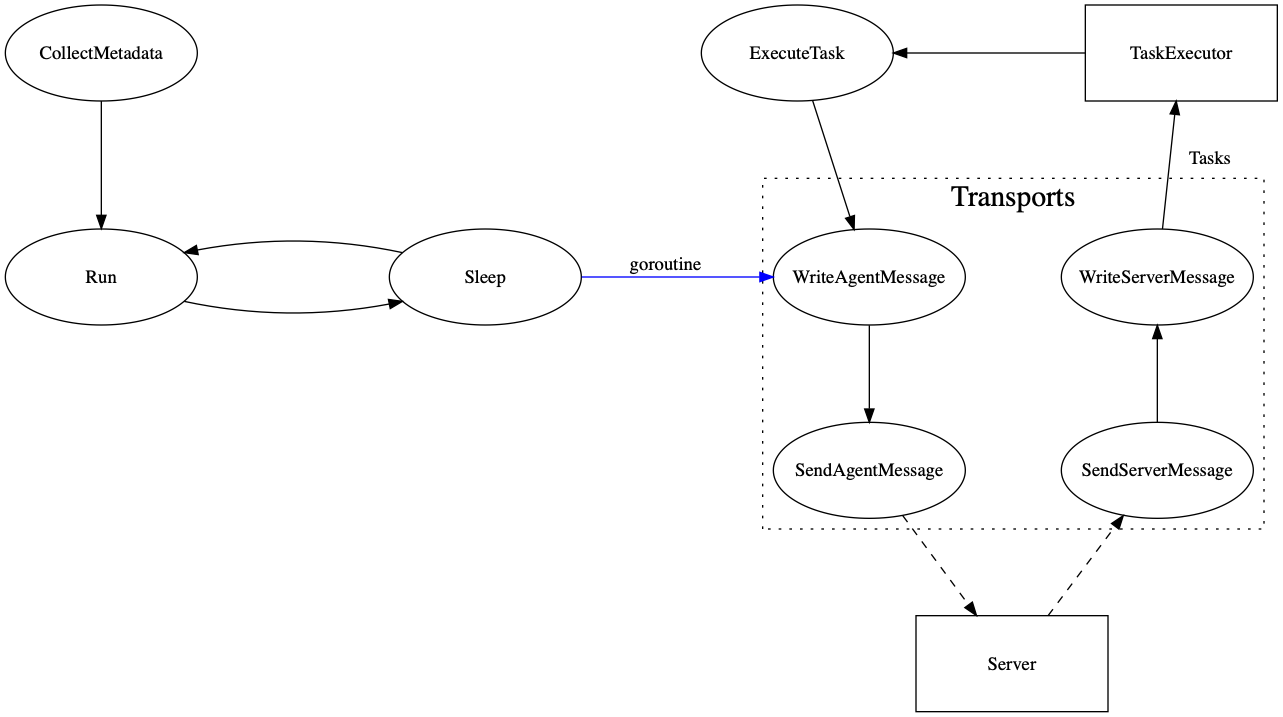 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 enkomio/alanframework
A C2 post-exploitation framework