

Decepticon
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
ai-securitycommand-and-controlexploitation+9
6.5k
bittersecurity/decepticonAutonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 cisc0-gif/kitt
Python-Based Pentesting Framework
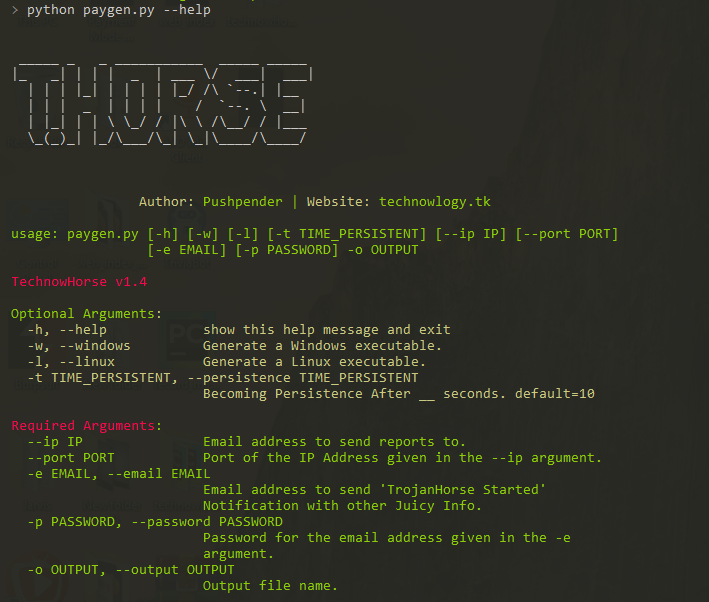 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
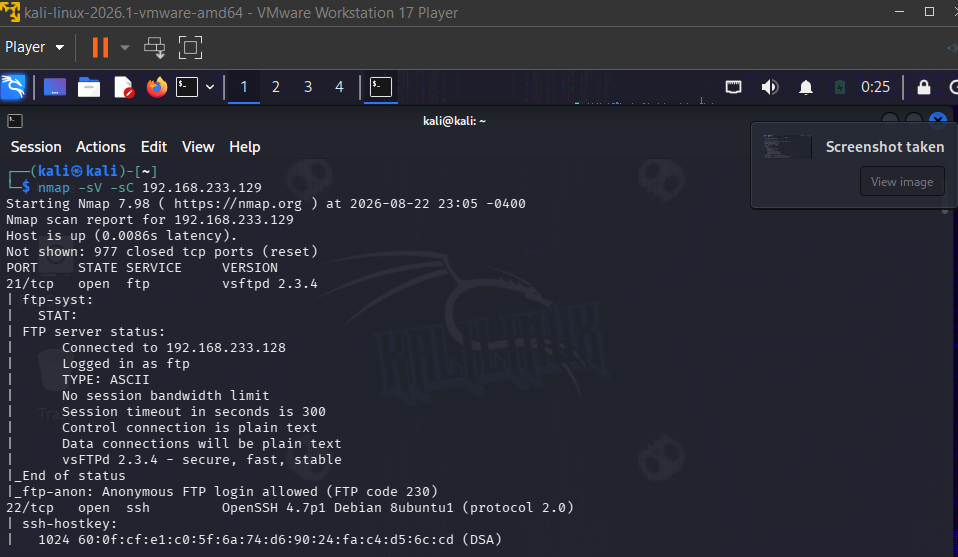 rsakthikumar-cmd/metasploitable2-vsftpd-writeup
Exploiting the vsftpd 2.3.4 backdoor (CVE-2011-2523) on Metasploitable2 — a hands-on pentesting lab writeup covering recon, exploitation, and…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
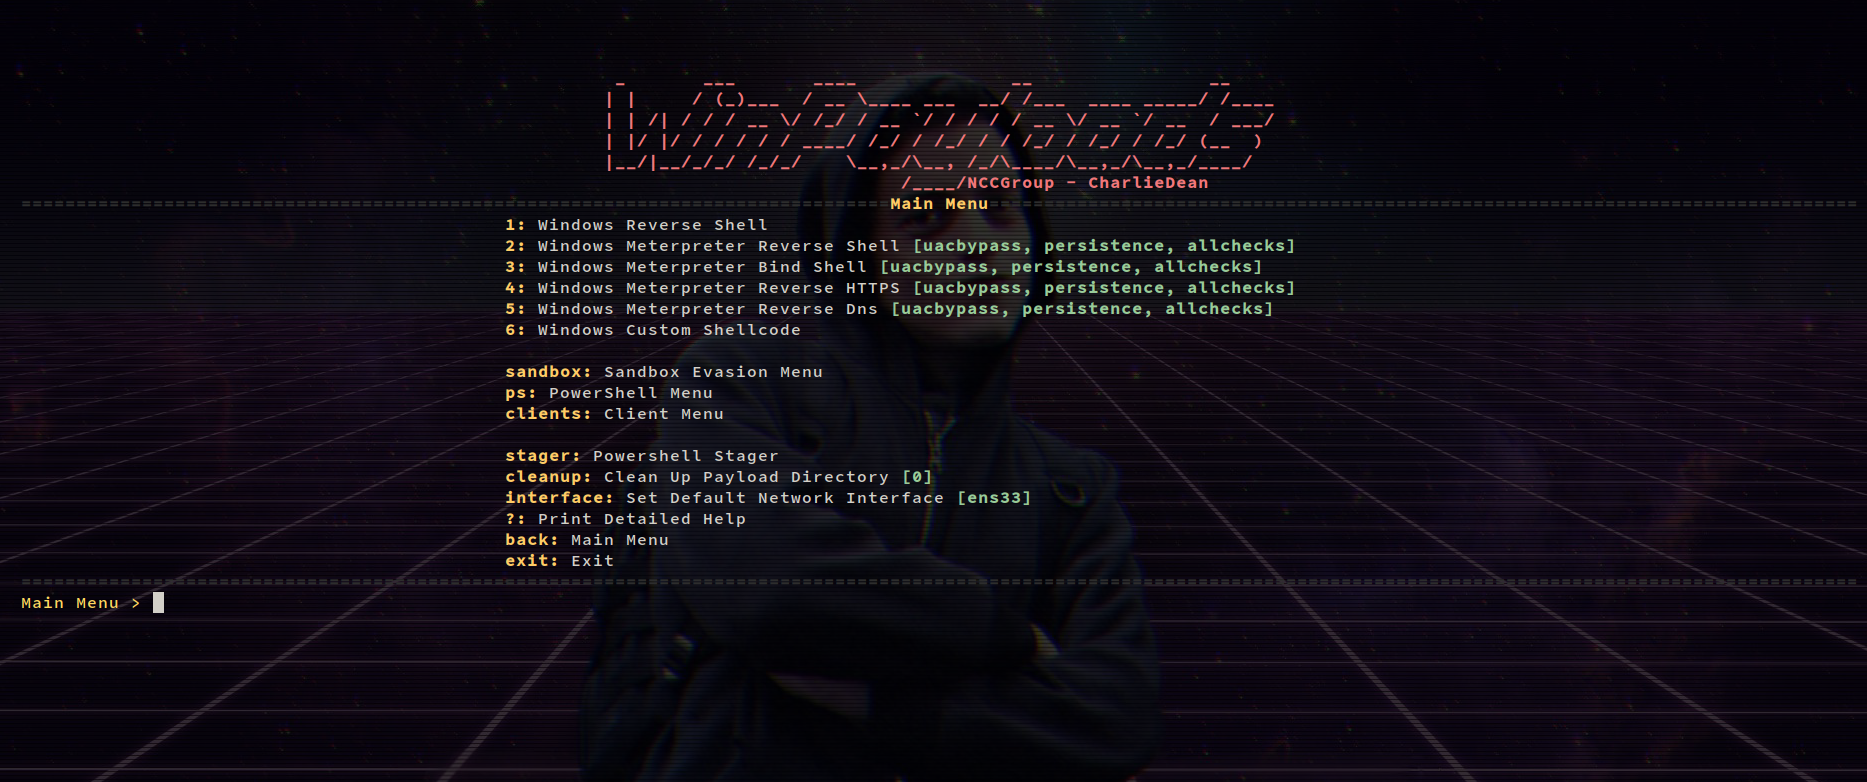 nccgroup/winpayloads
Undetectable Windows Payload Generation
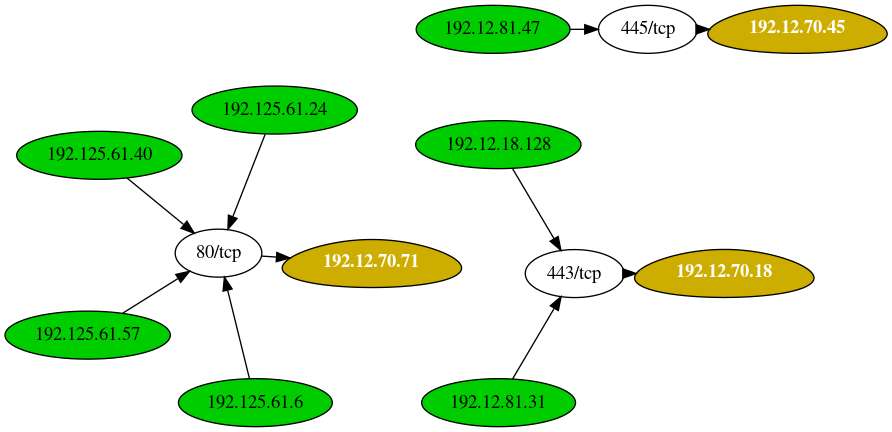 vonahisec/leprechaun
This tool is used to map out the network data flow to help penetration testers identify potentially valuable targets.
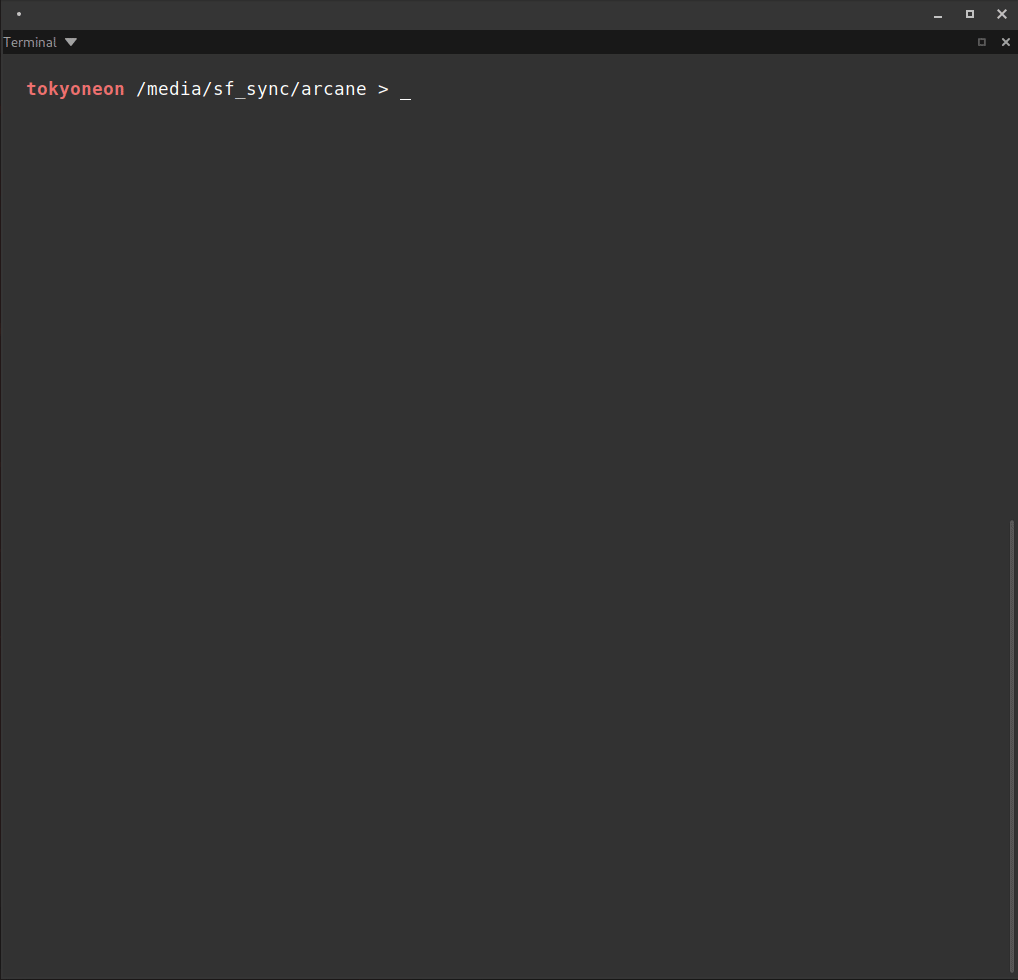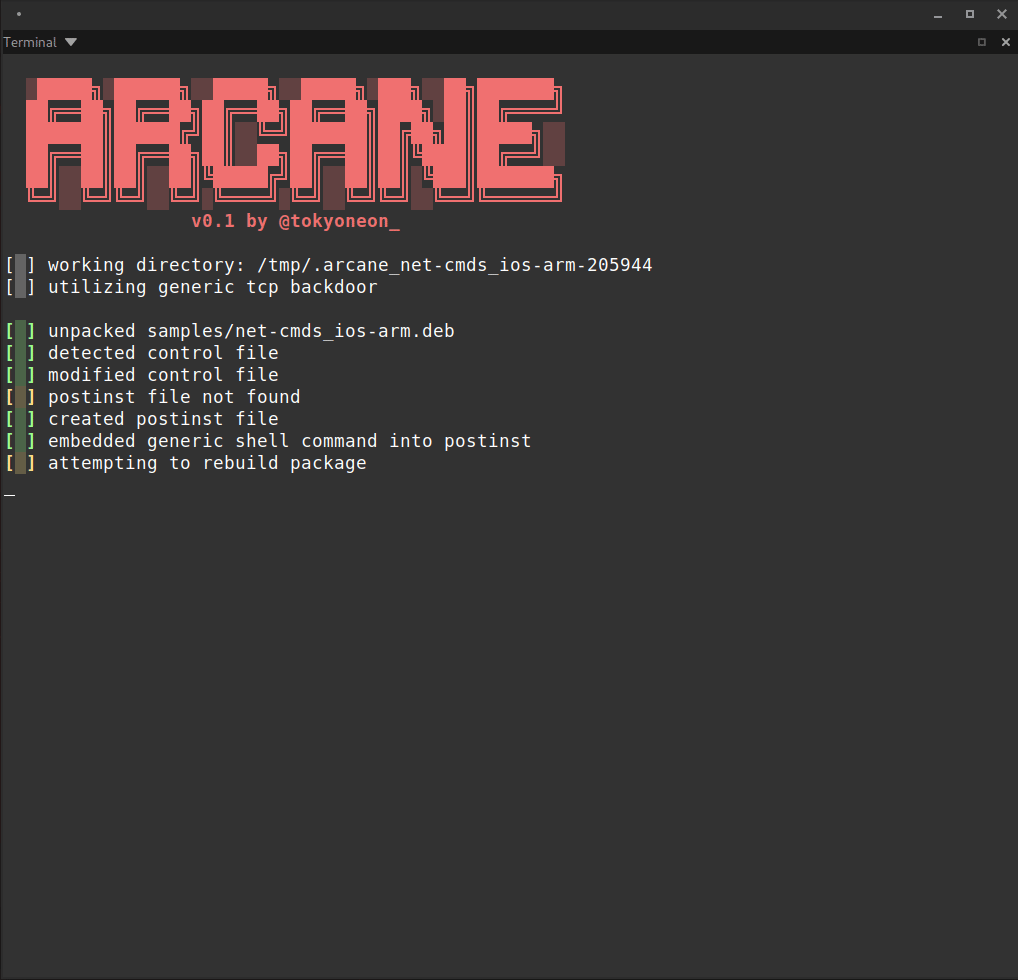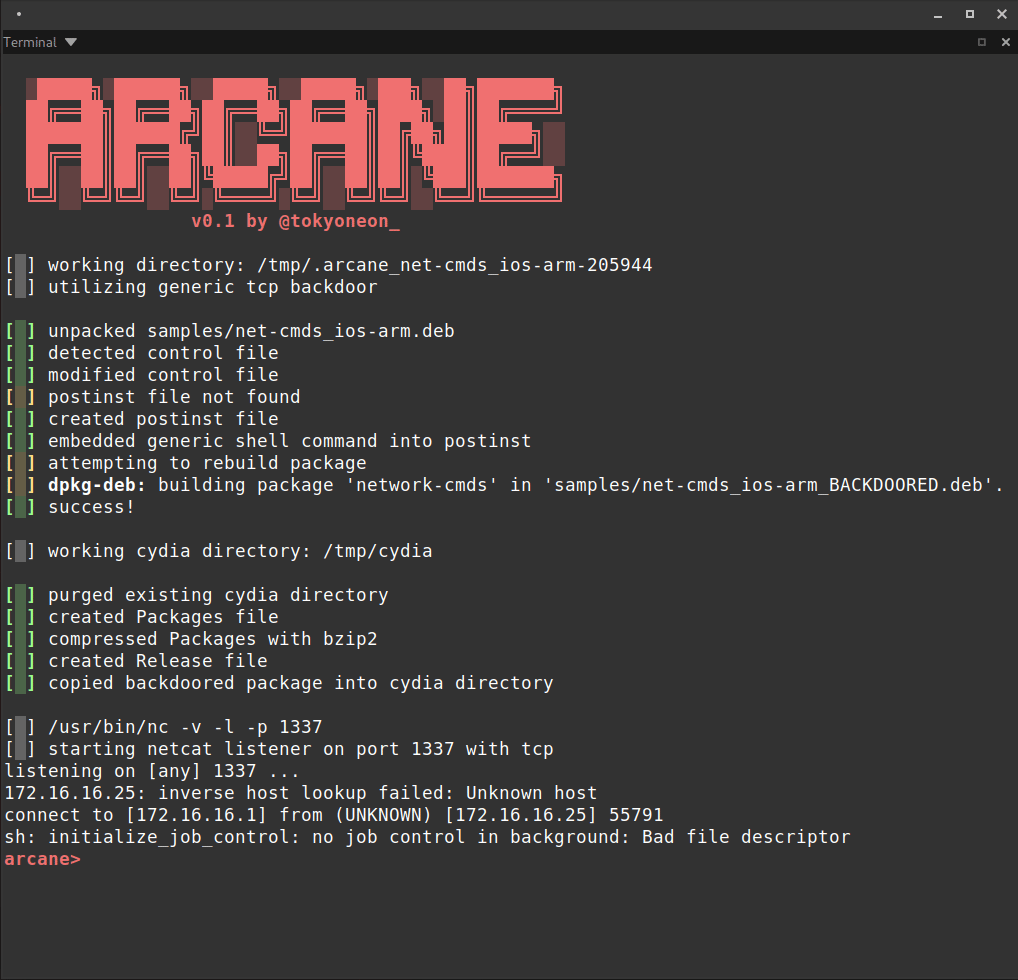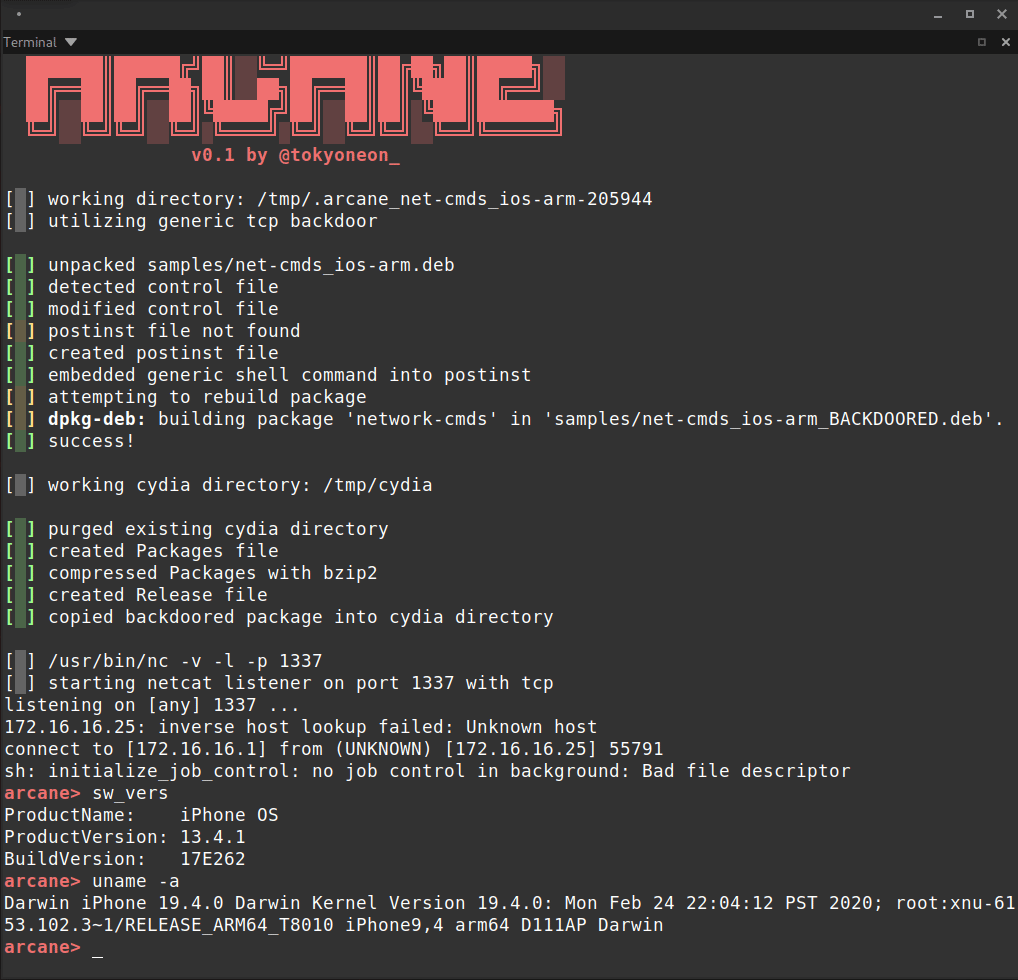 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
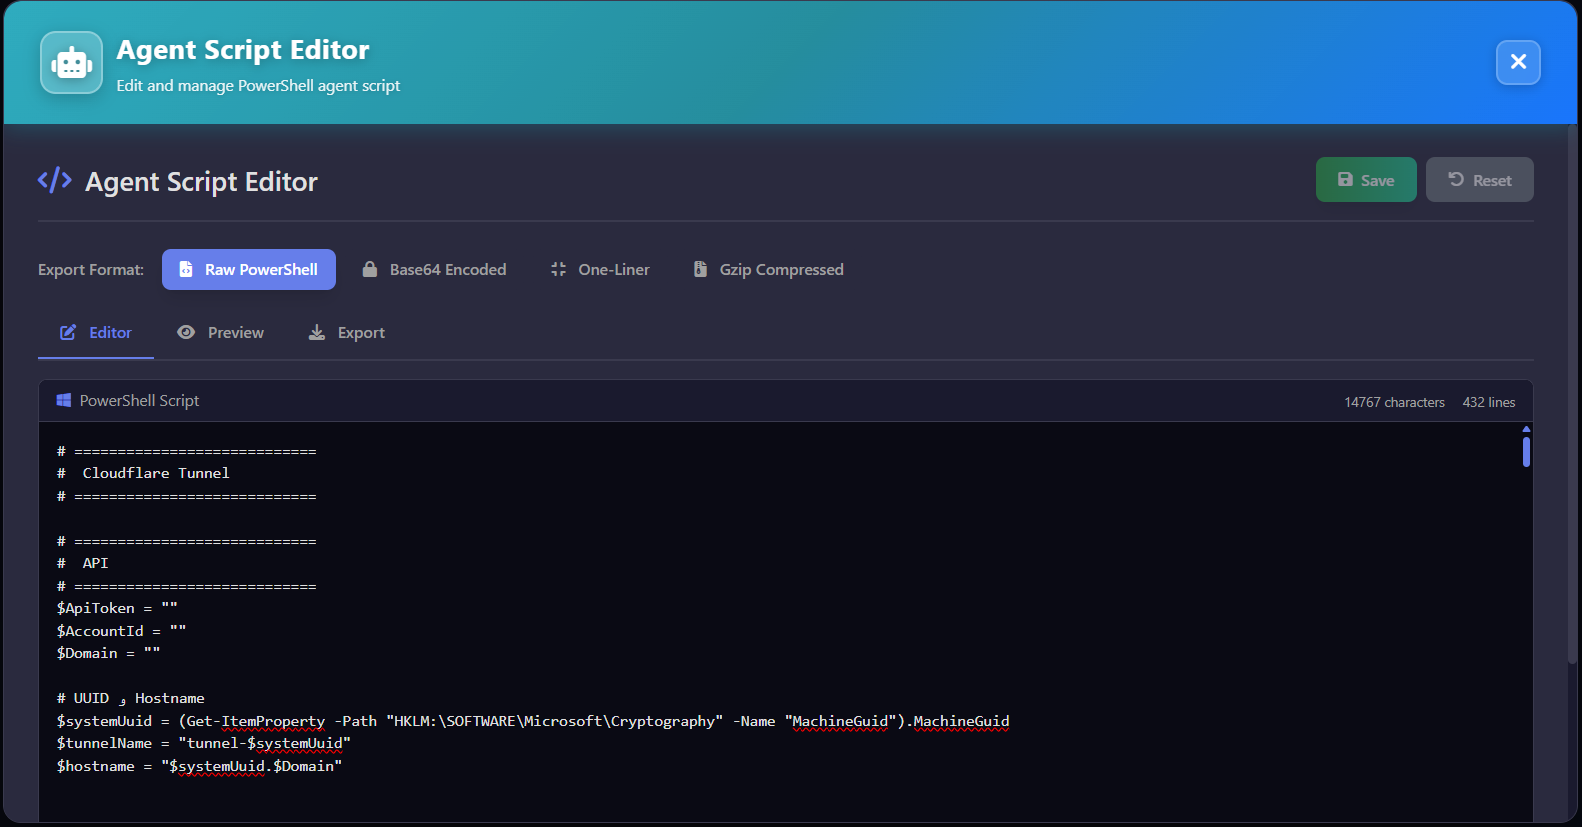 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 seifeldienahmad/penetration-testing-on-metasploitable2
Hands-on pentest project using Kali Linux vs Metasploitable2. Includes full workflow: Nmap scanning, enumeration, Metasploit exploitation (Samba…
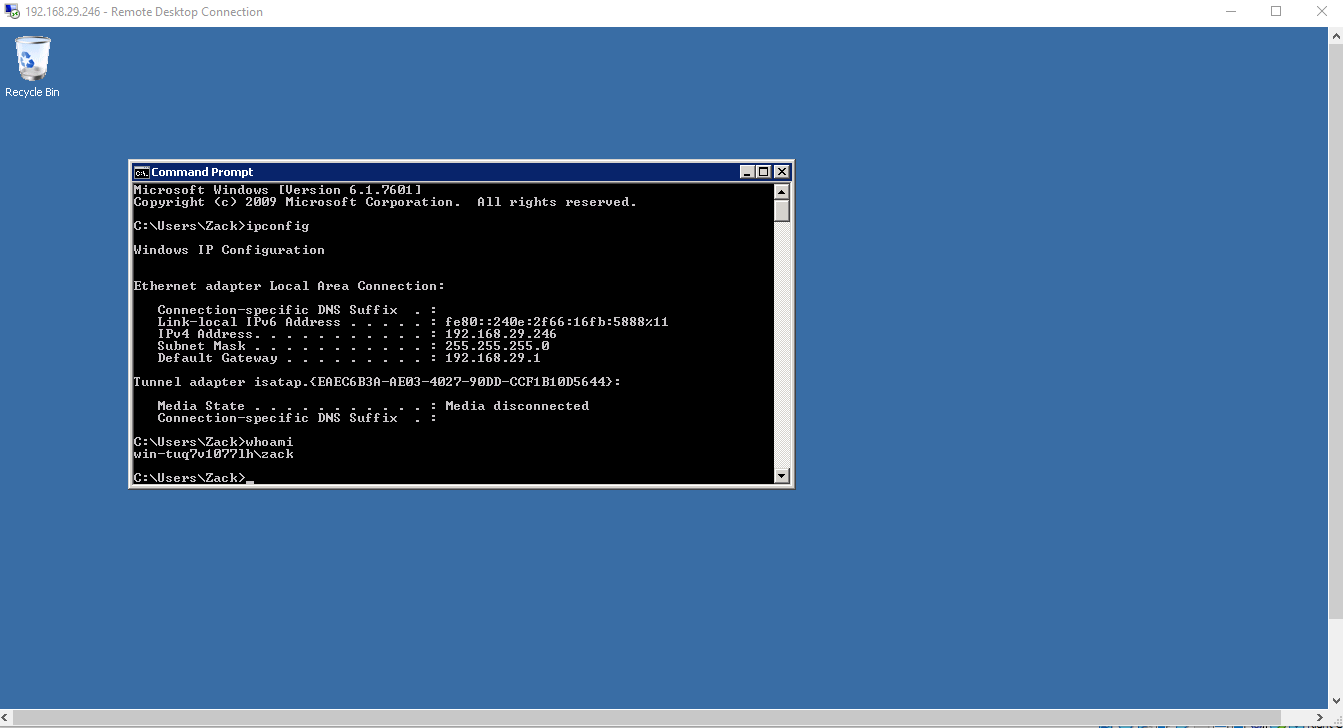 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…