
Evilginx-Phishing-Infra-Setup
 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
command-and-controlcurated-resourceseducation+6
598
an0nud4y/evilginx-phishing-infra-setupEvilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 jenyraval/phishing-simulation
Phishing Simulation mainly aims to increase phishing awareness by providing an intuitive tutorial and customized assessment
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
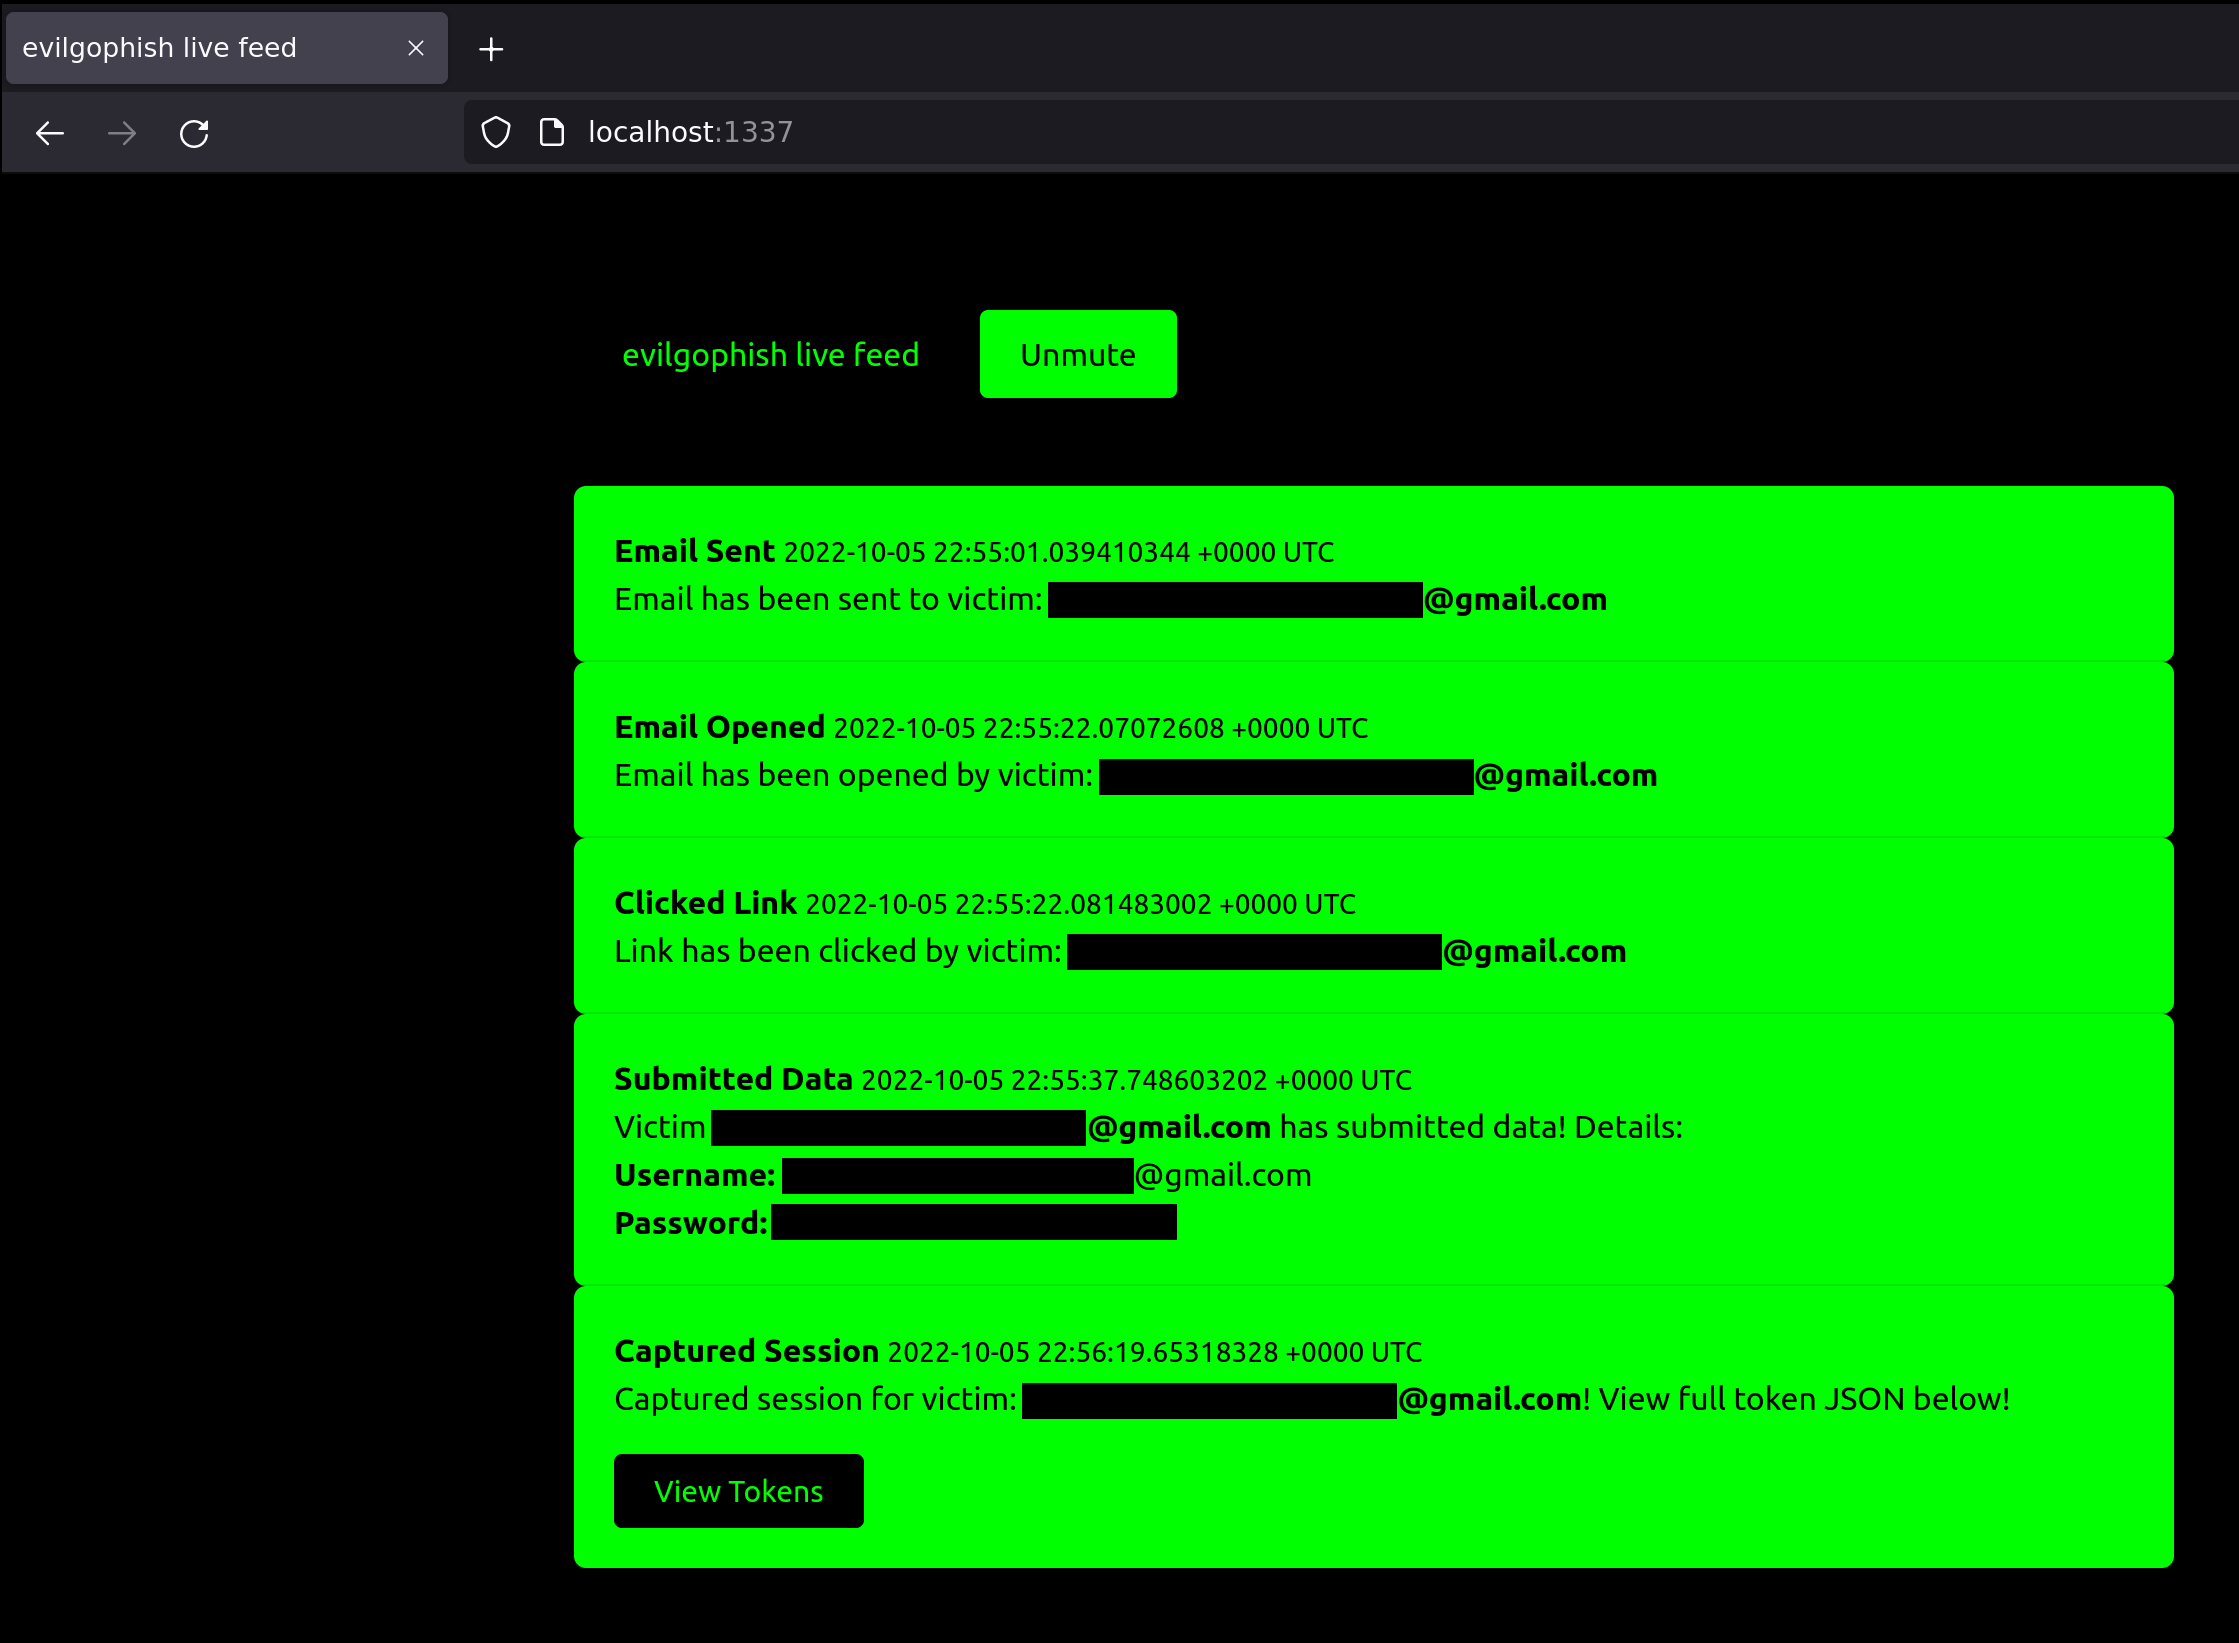 fin3ss3g0d/evilgophish
evilginx3 + gophish
 0xaj2k/cve-2020-11022-cve-2020-11023
Little thing put together quickly to demonstrate this CVE
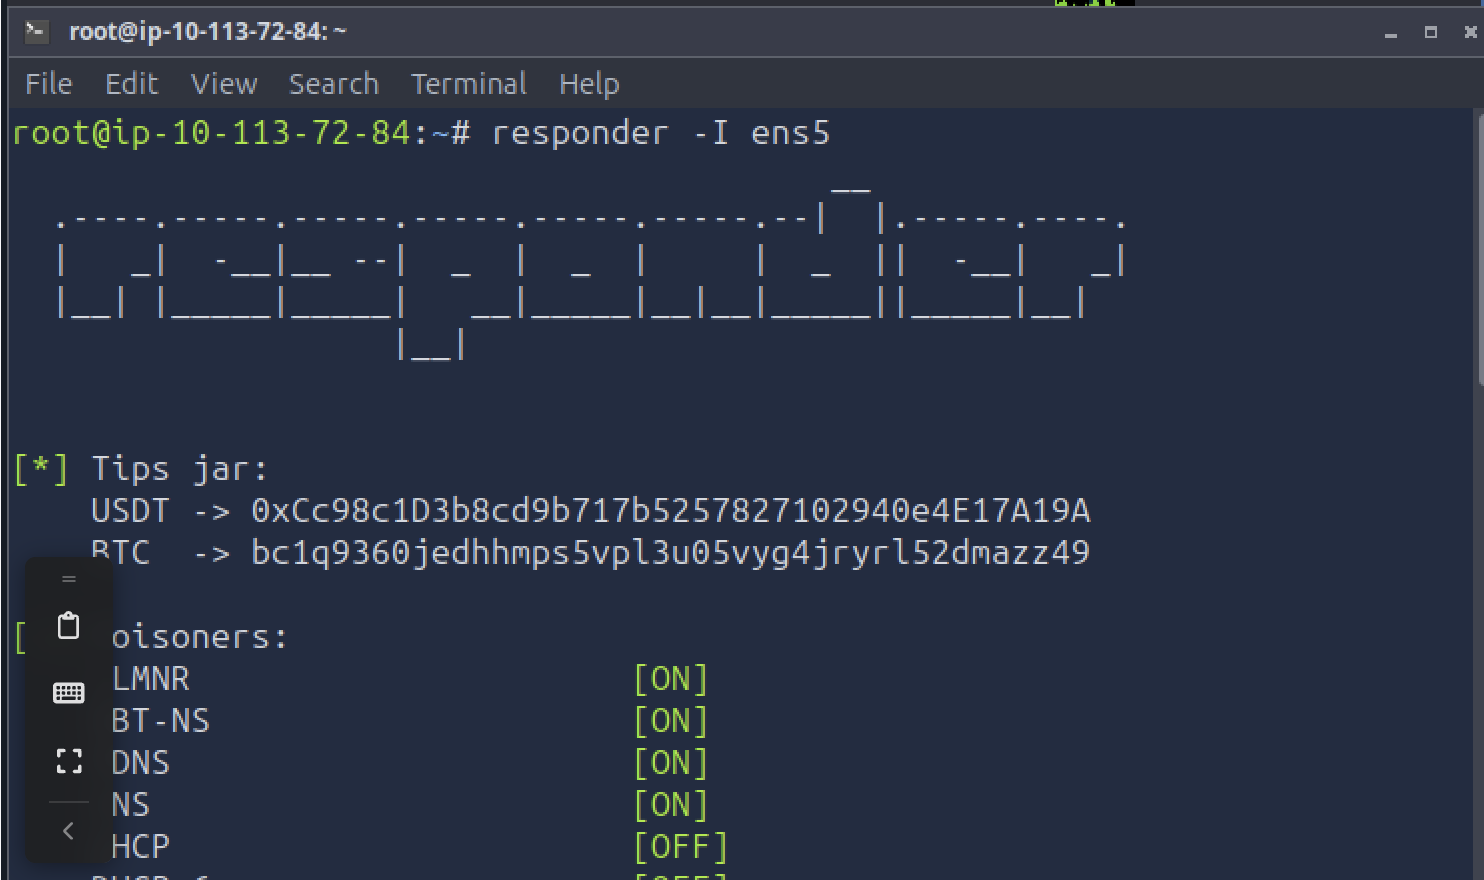 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
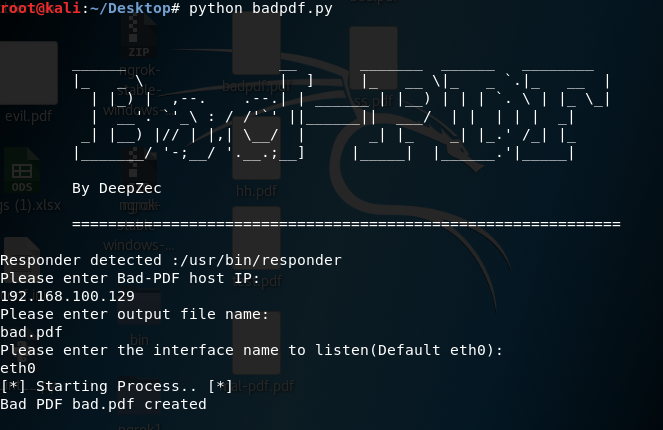
 duy-31/cve-2024-21413
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 omarothmann/embedded-backdoor-connection
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…