
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
2.7k
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
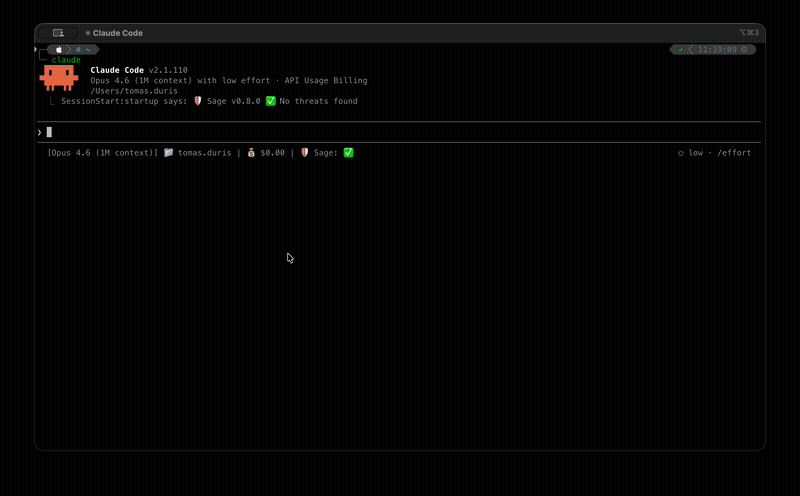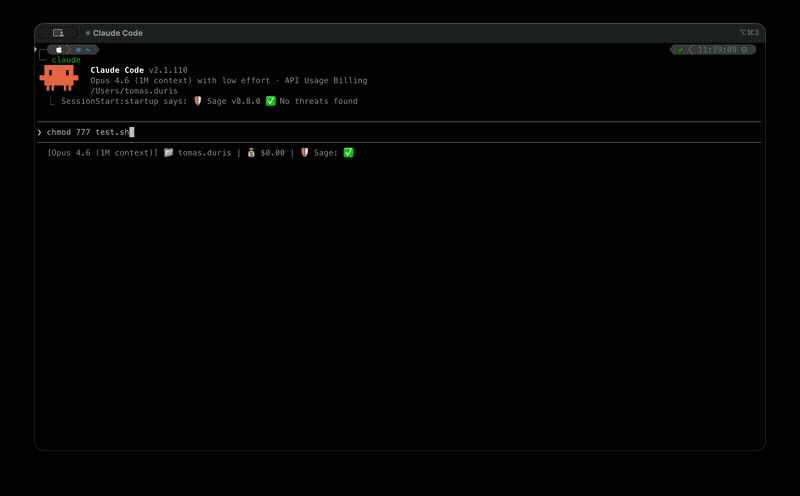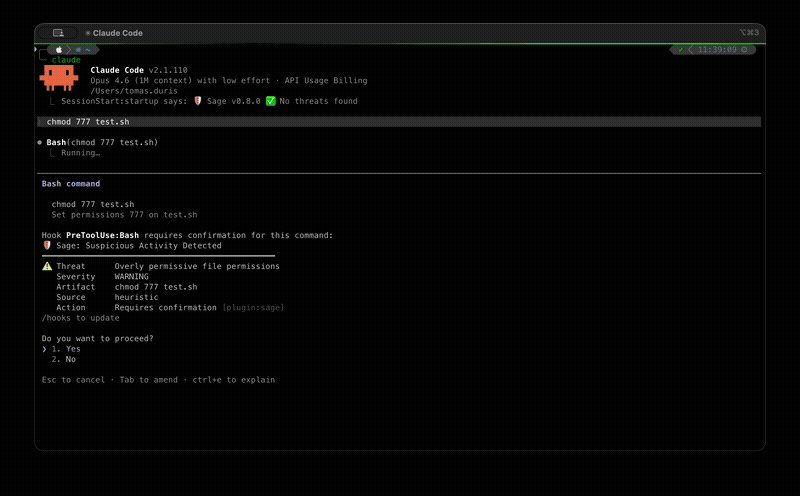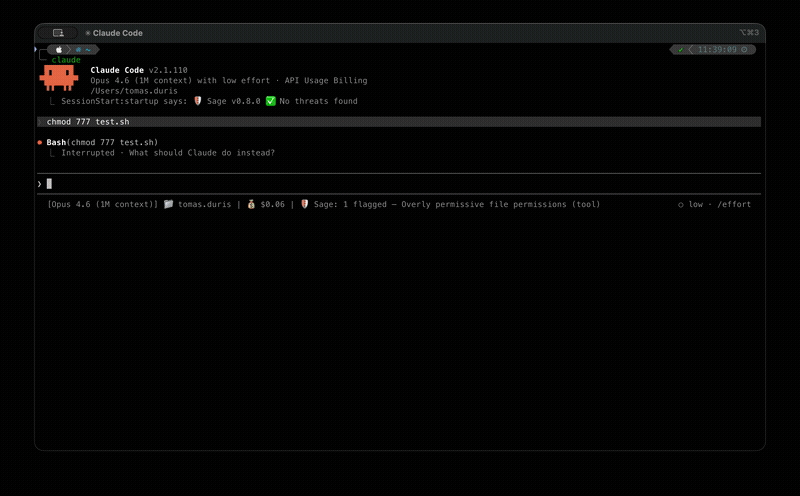 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
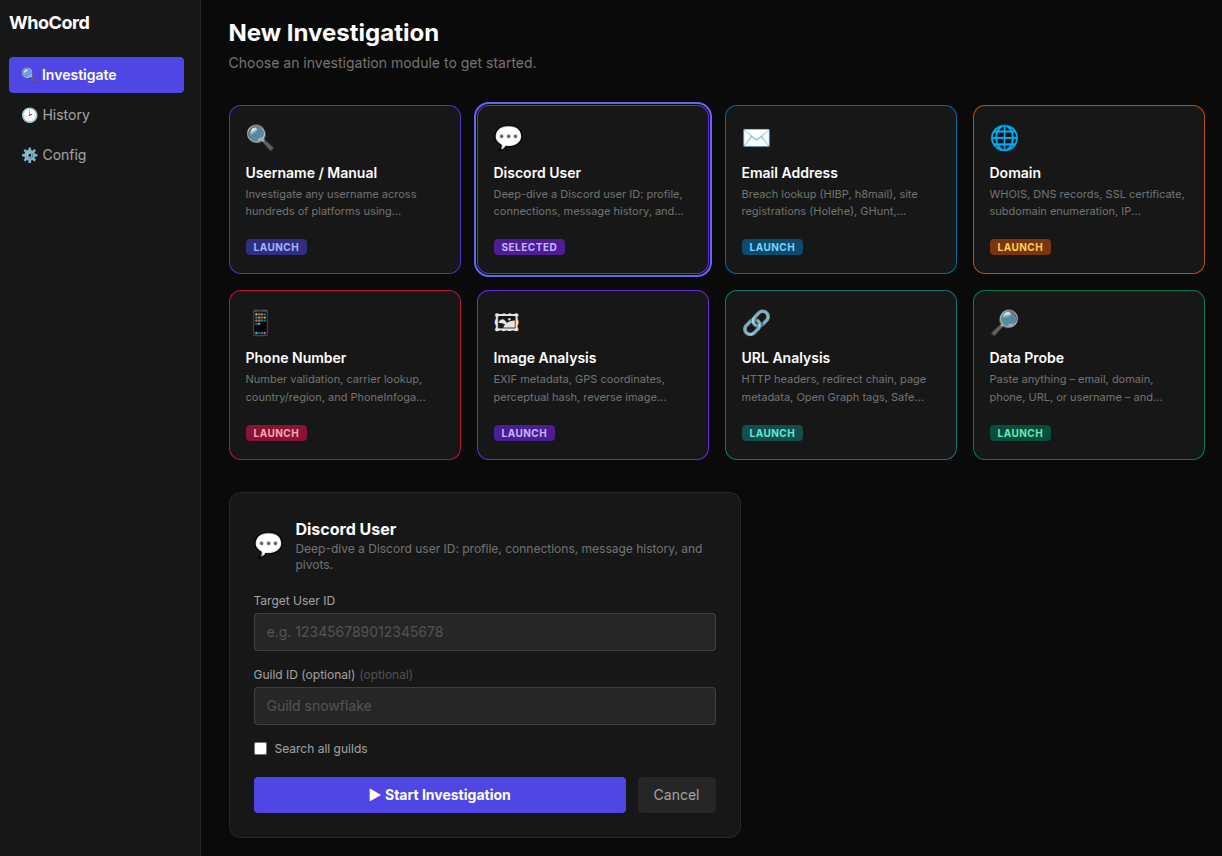 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
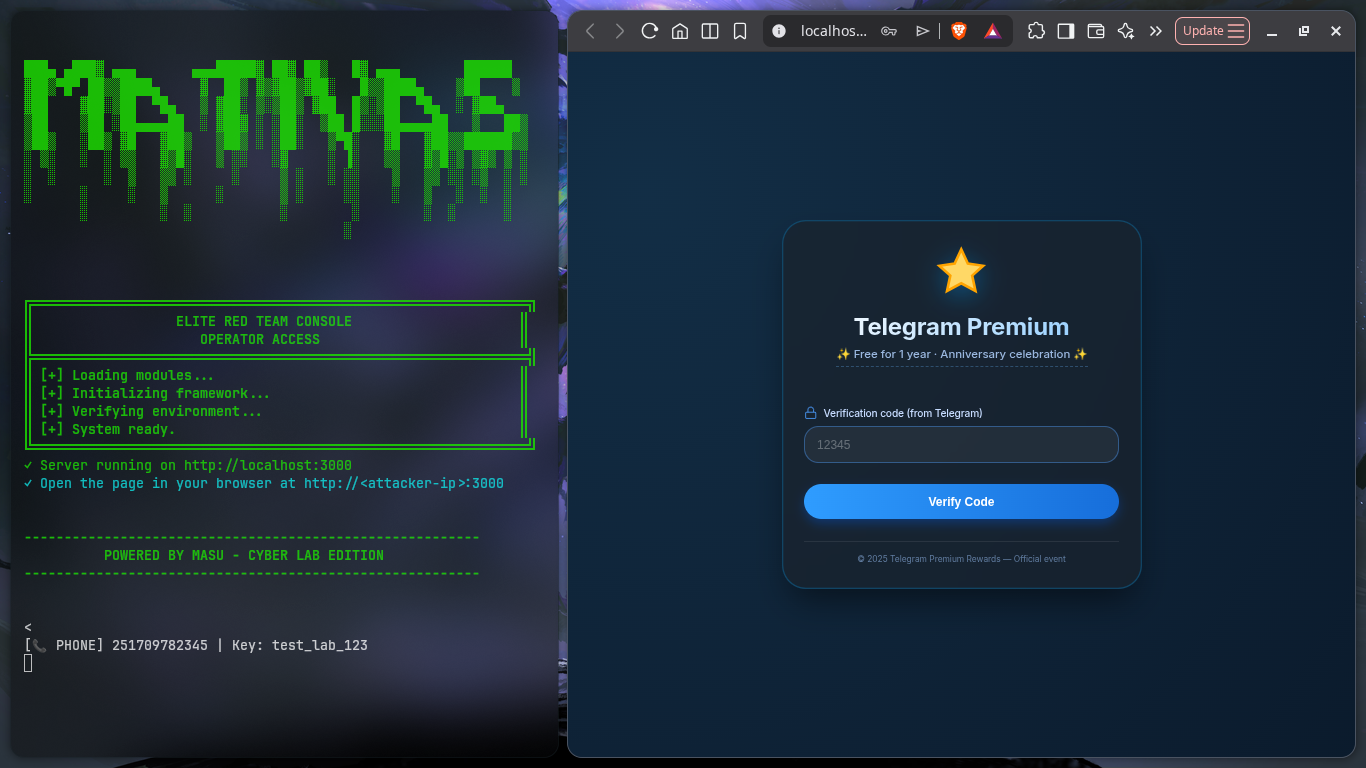 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…
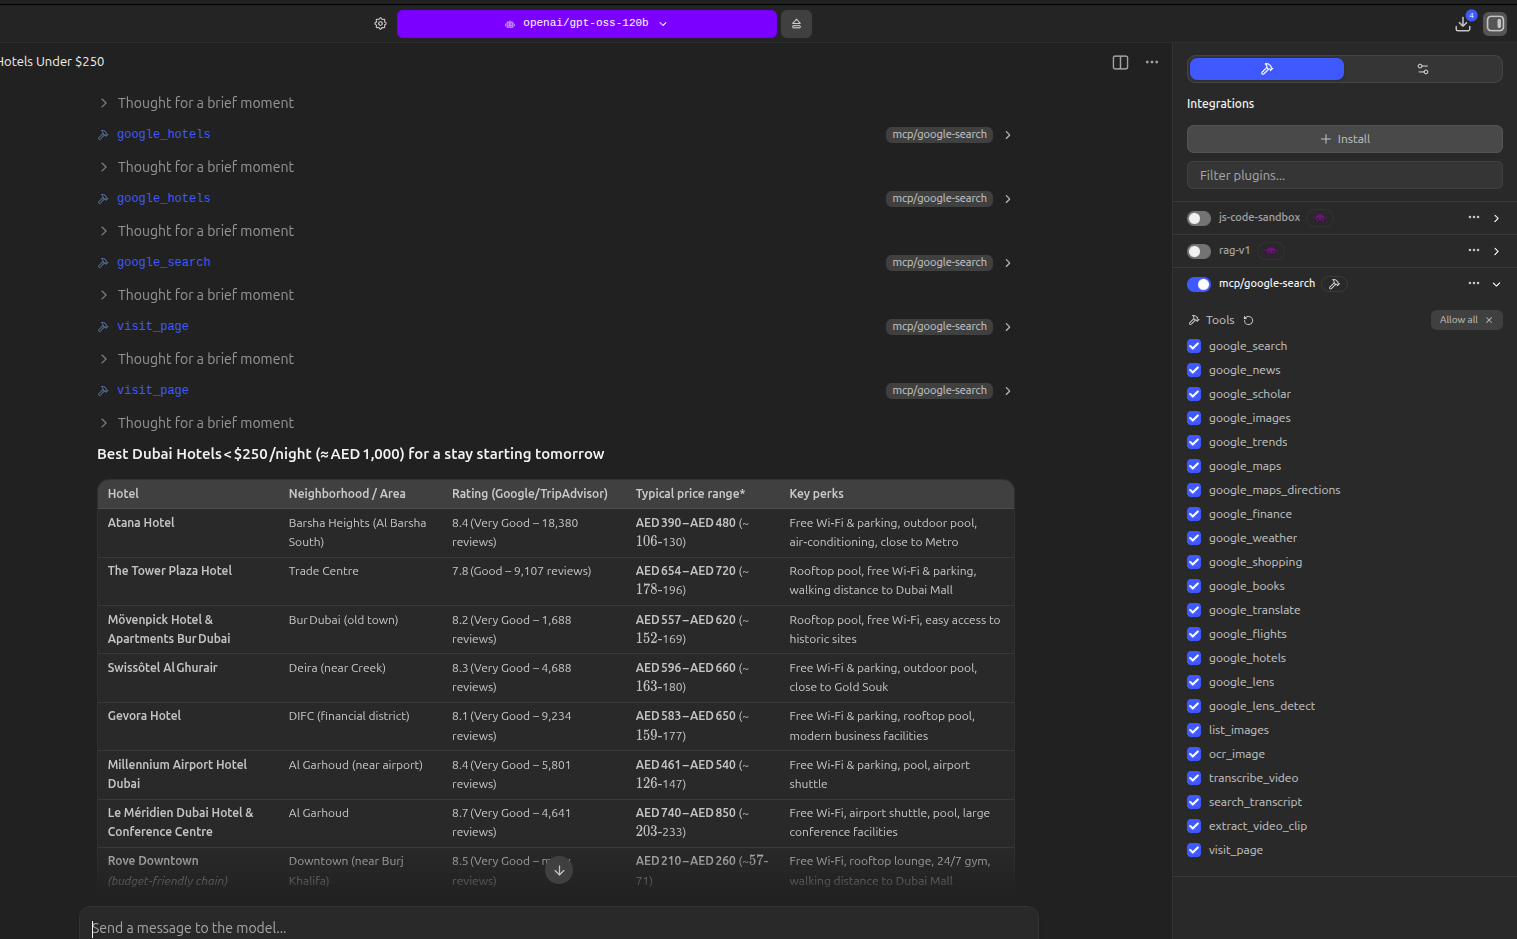 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 hunt-benito/cve-2026-41200-stig-manager-oidc-reflected-xss
Proof-of-concept exploit generator for reflected XSS in STIG Manager OIDC authentication, enabling session token theft via crafted callback URLs and…
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations