WebView2-Cookie-Stealer

Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…

Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…

CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.

Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…

Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…

Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

A Phishing Dropper designed to Pentest.

Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…

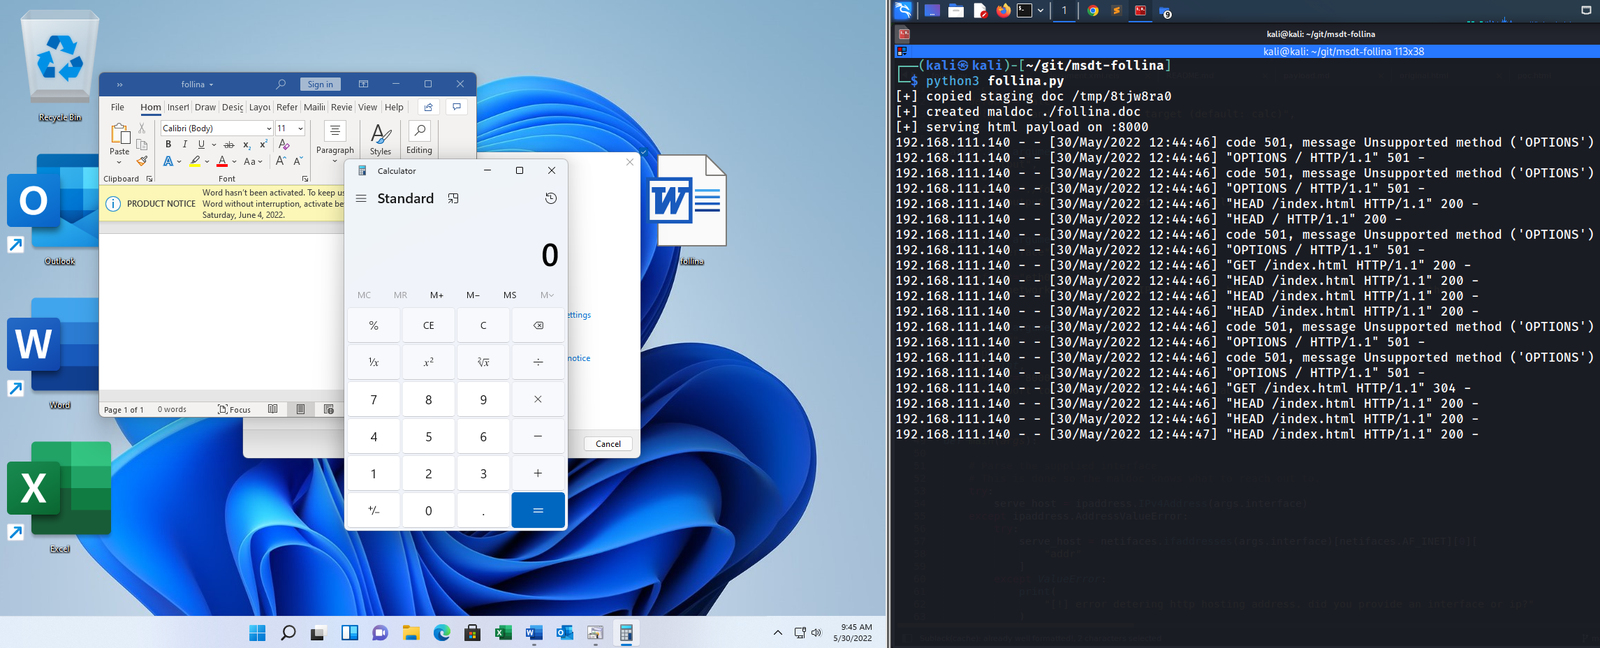
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

A tool to transform Chromium browsers into a C2 Implant

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.

Rogue access point toolkit for WiFi penetration testing, deploying evil portal phishing payloads to capture credentials and perform social…

It is a simple Python Script to hide phishing URL under a normal looking URL (google.com or facebook.com). It can be integrated into Phishing tools…

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…

PoC for the "Windows Notepad RCE"