

 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 atenreiro/opensquat
OSINT tool that detects domain squatting, typosquatting, and phishing look-alikes by monitoring newly registered domains against brand keywords with…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
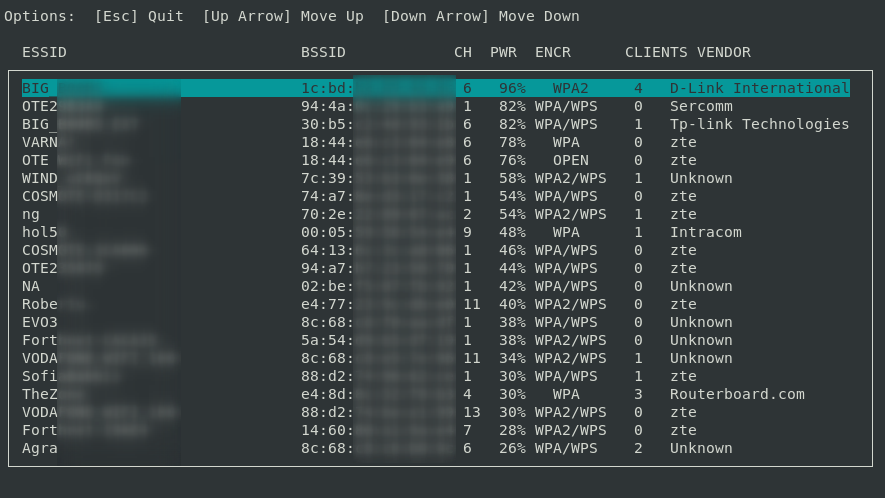 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 theresafewconors/sooty
The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
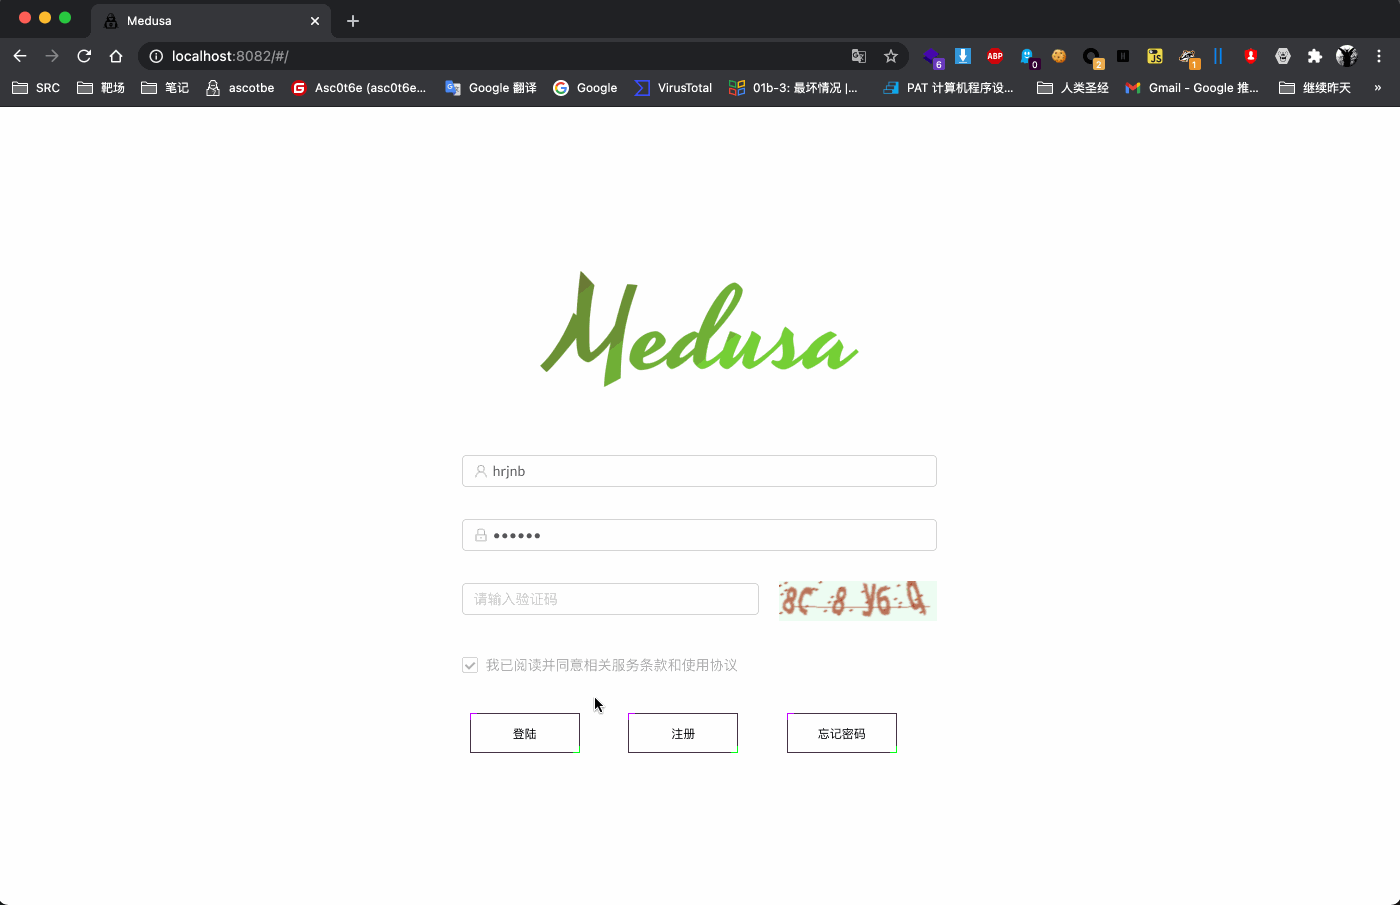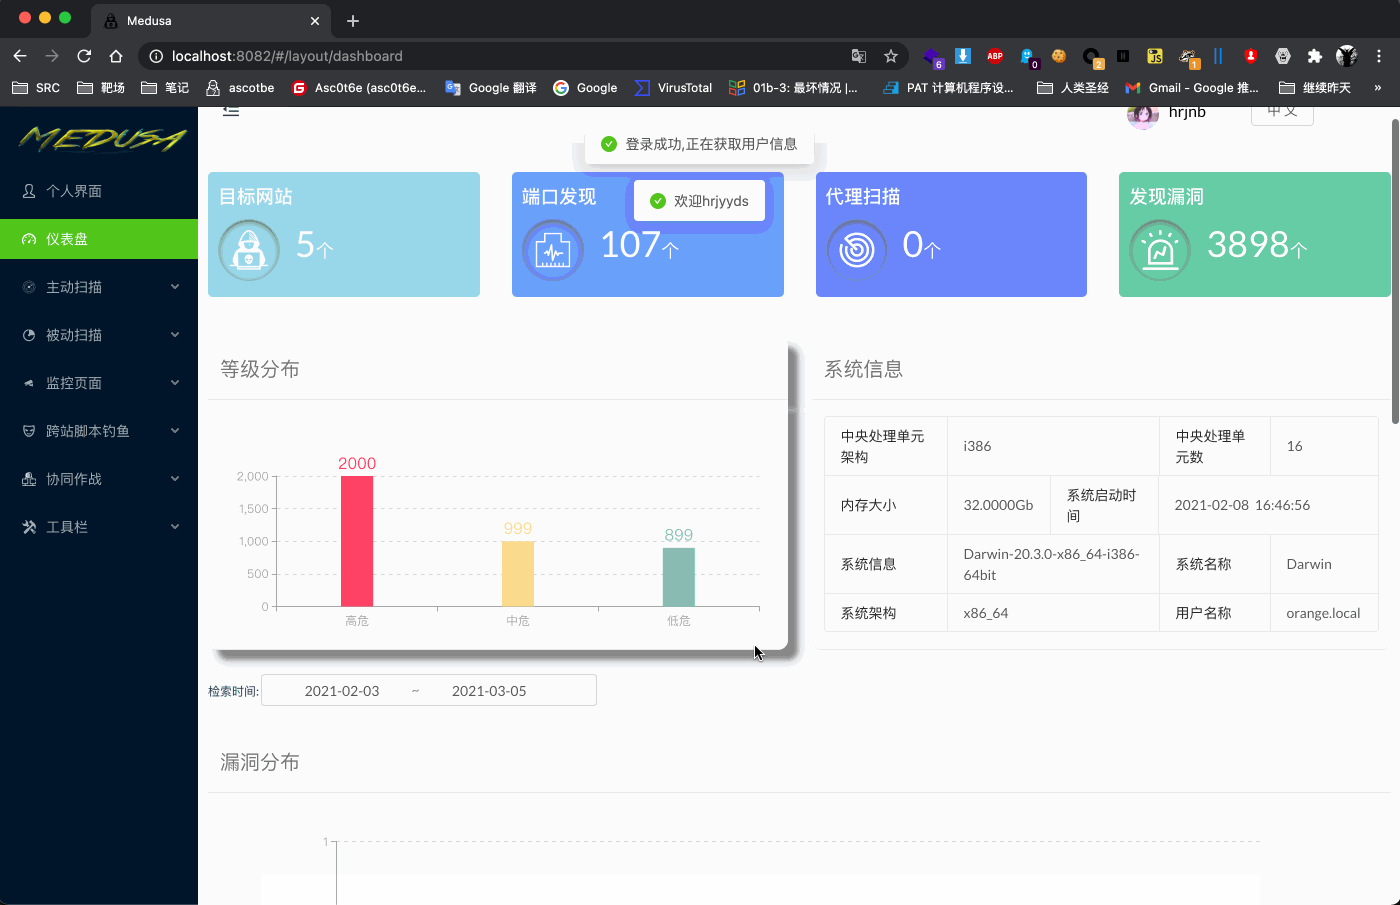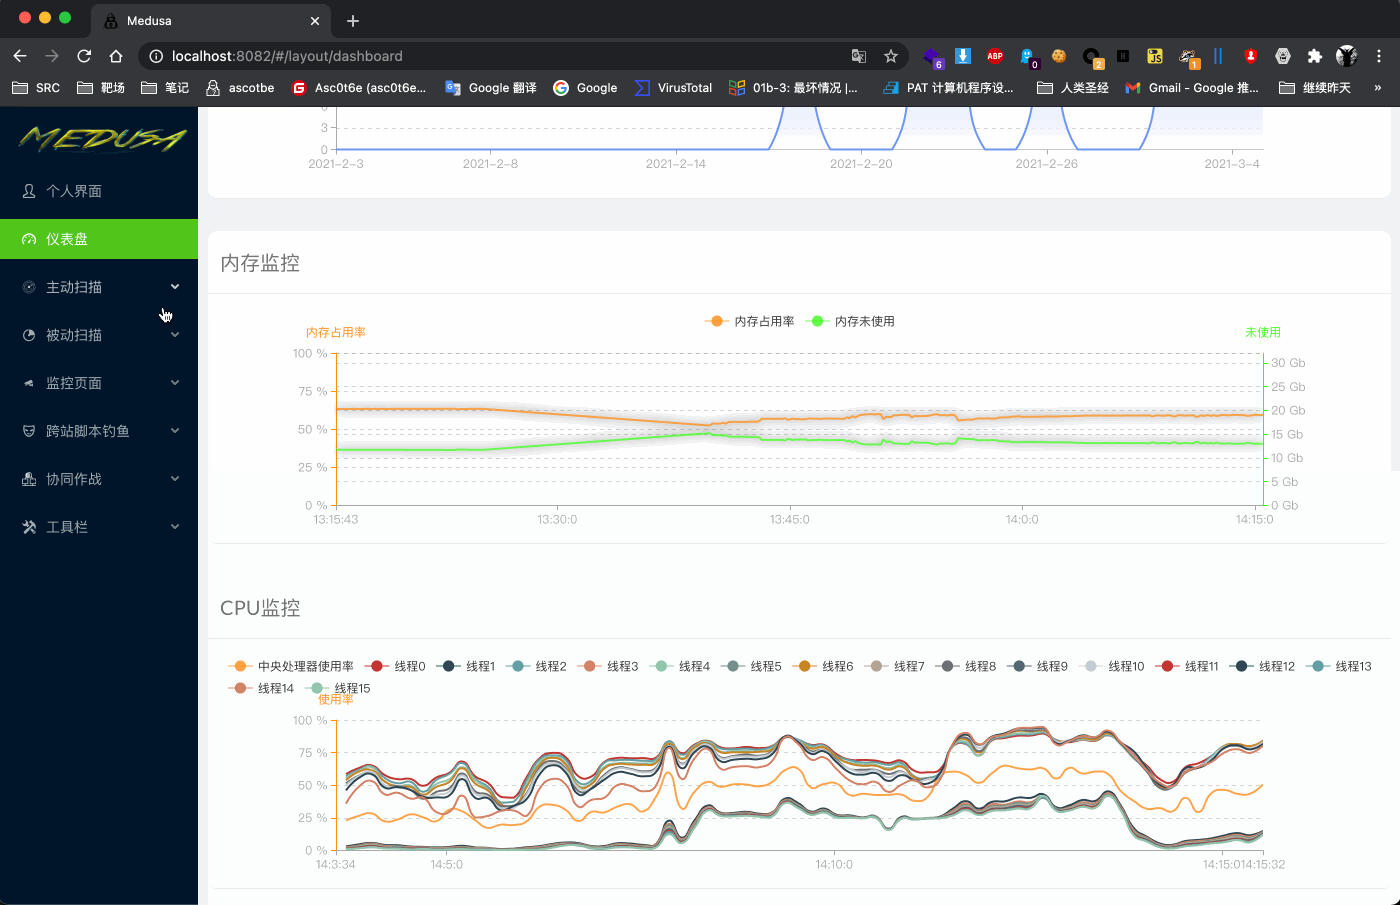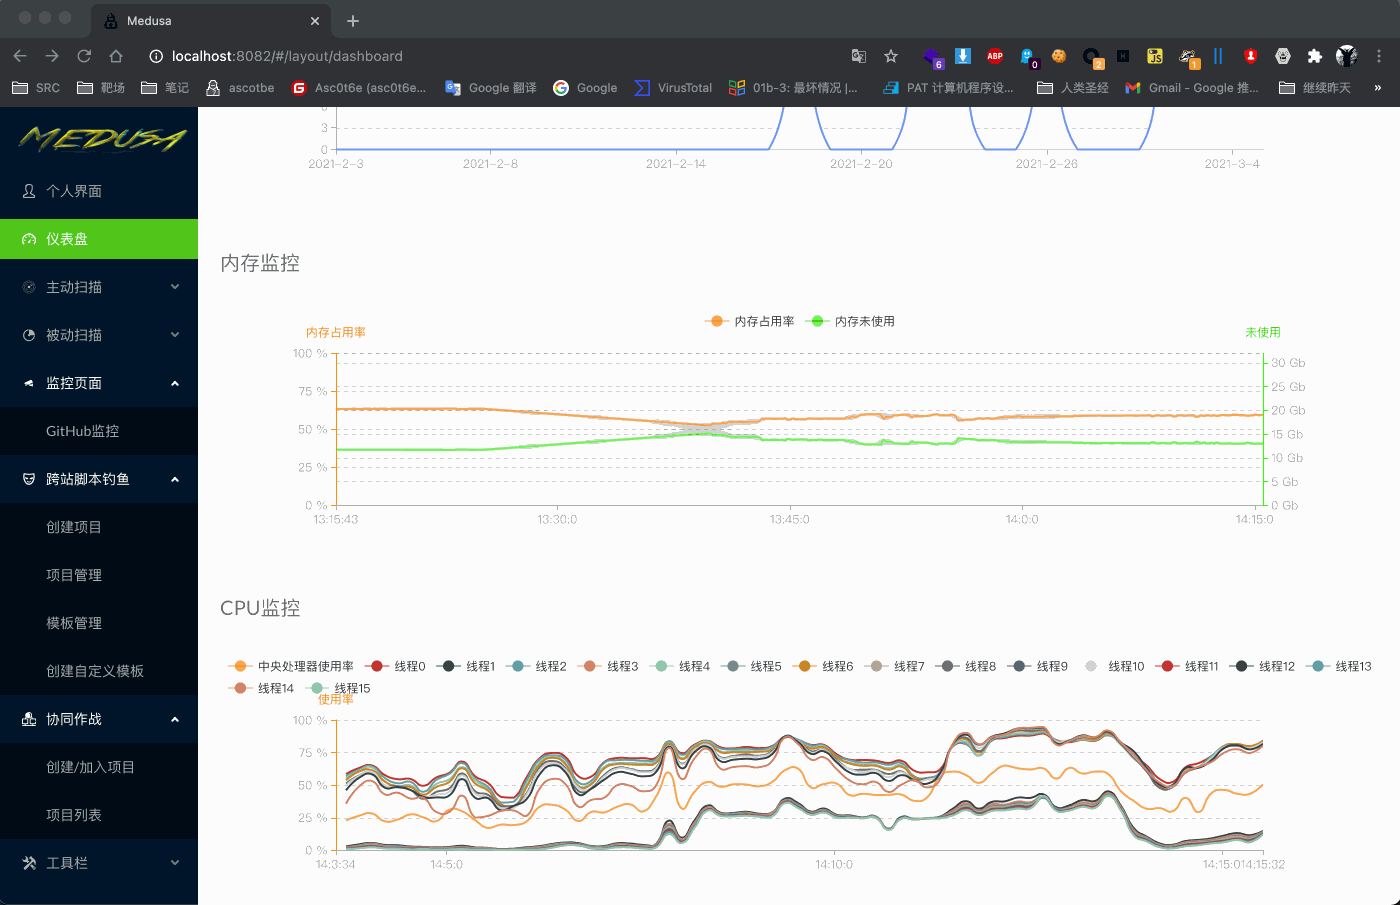 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 letsdefend/awesome-soc-analyst
Useful resources for SOC Analyst and SOC Analyst candidates.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 mattkeeley/spoofy
Bulk domain spoofability checker using authoritative SPF and DMARC record analysis with custom, real-world tested spoof logic and optional DKIM…
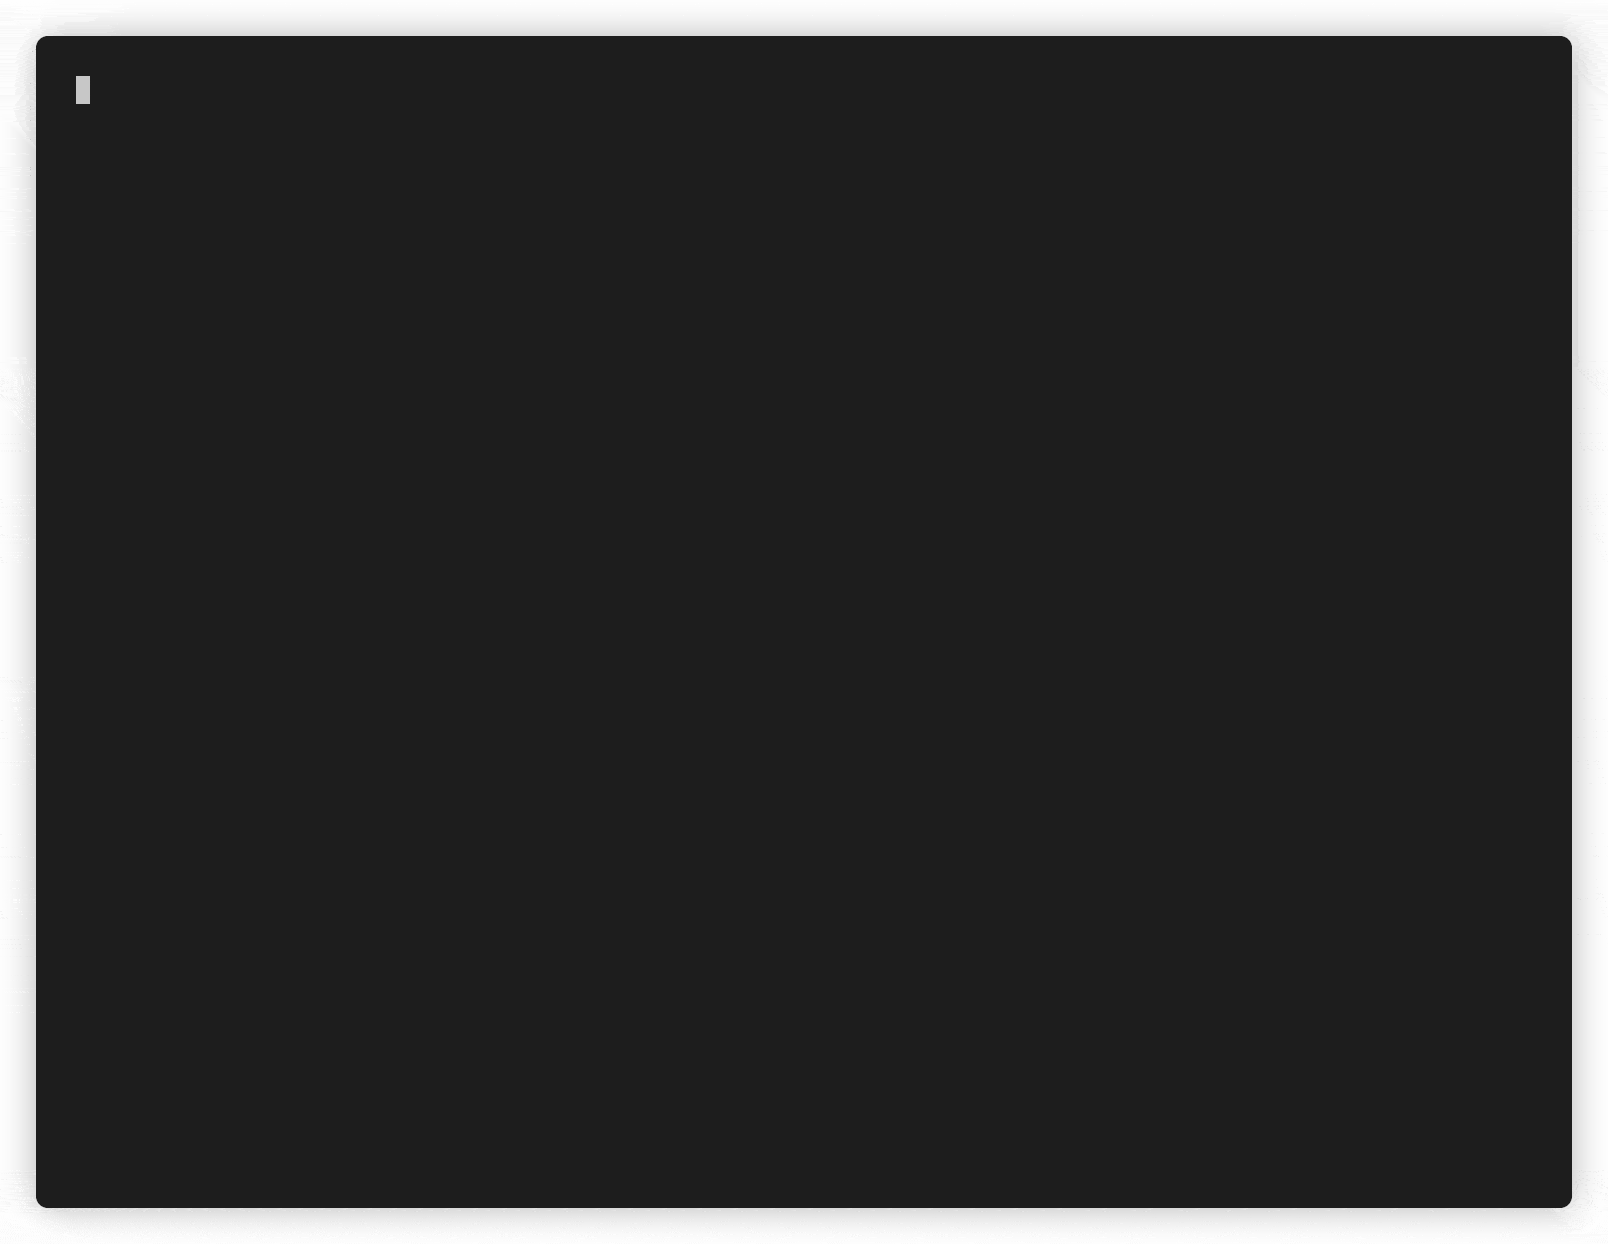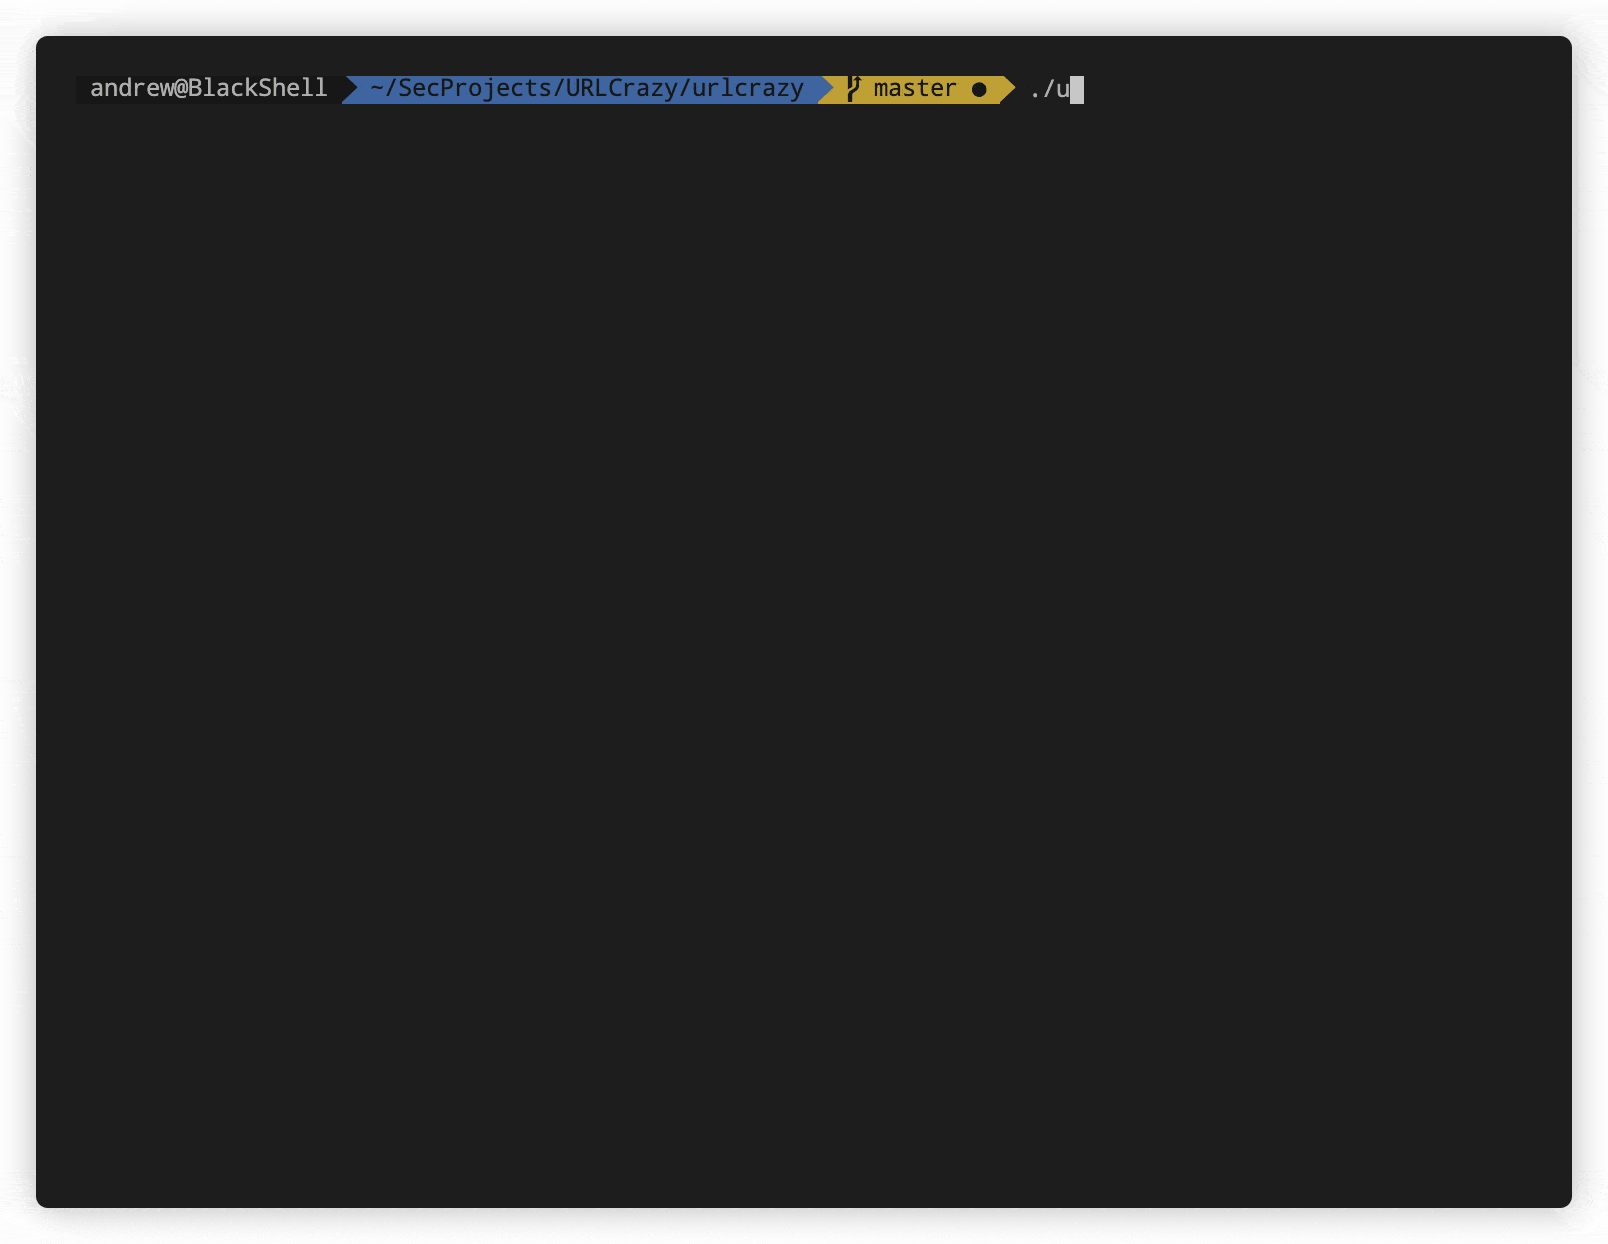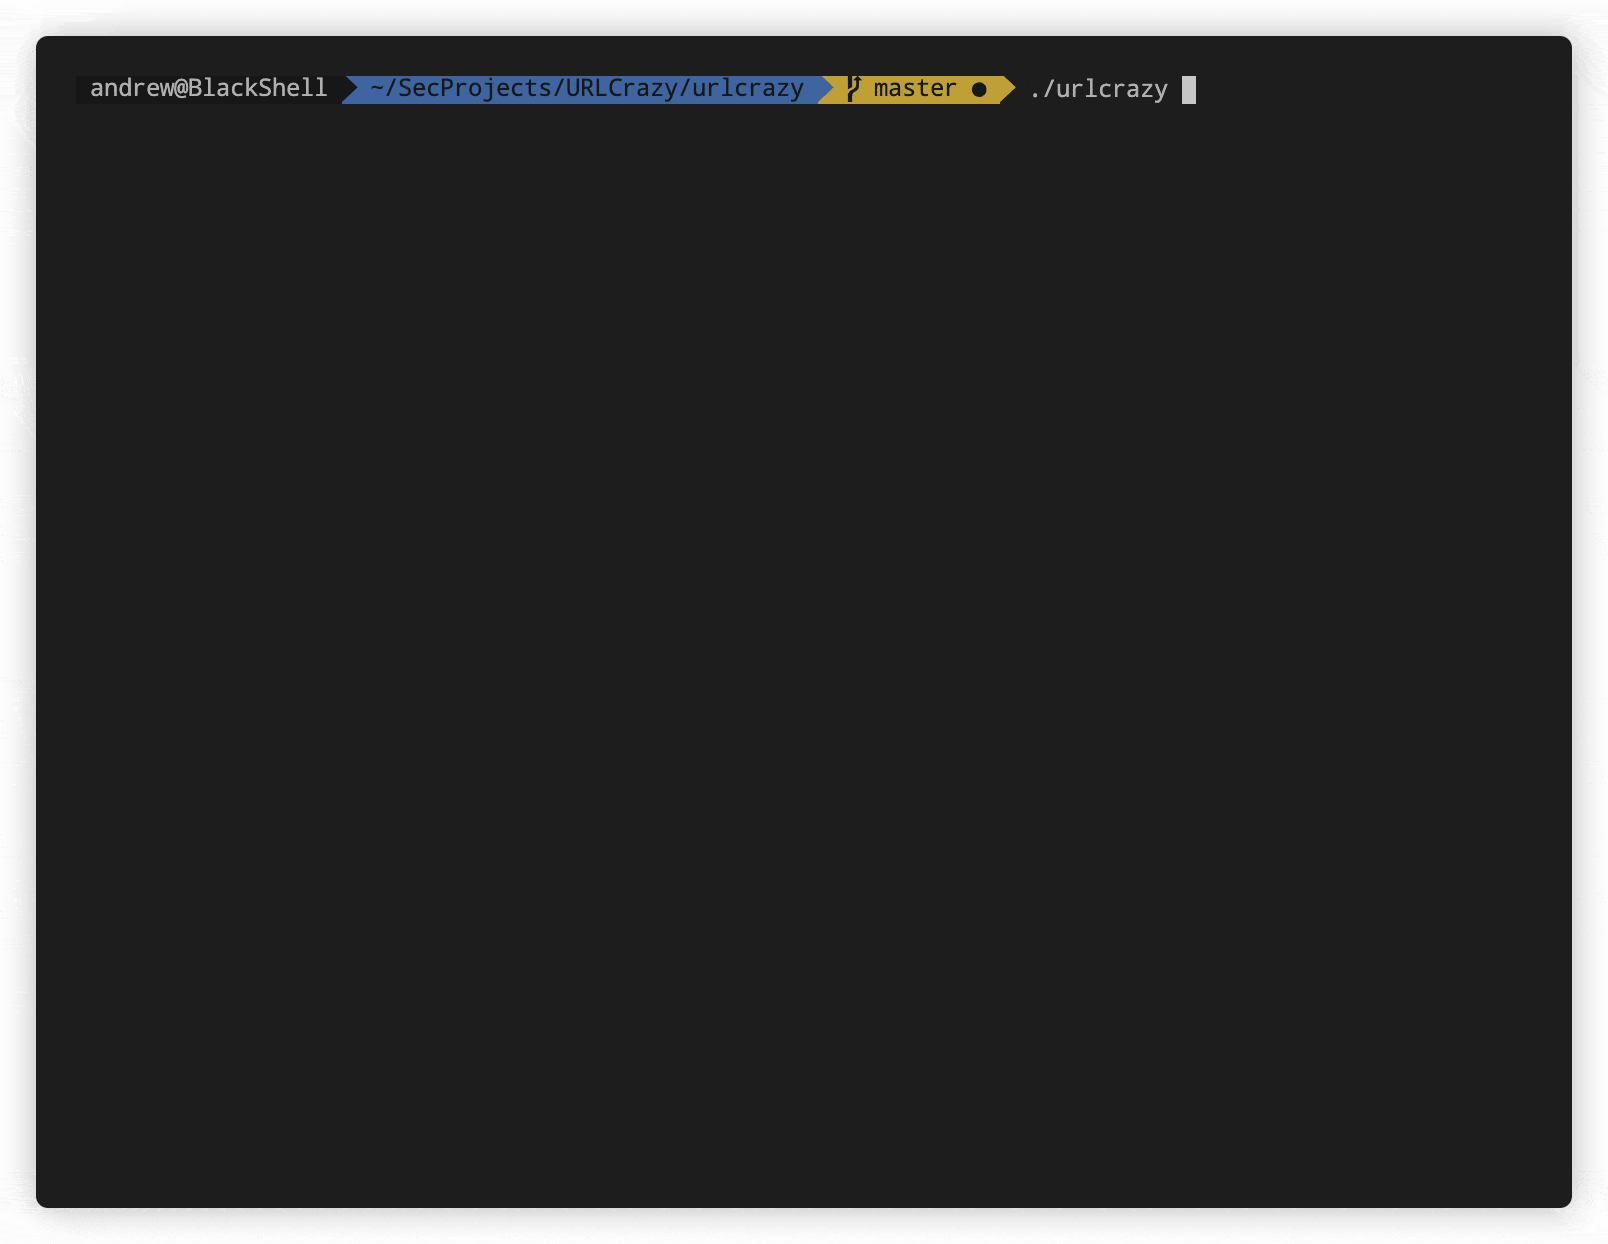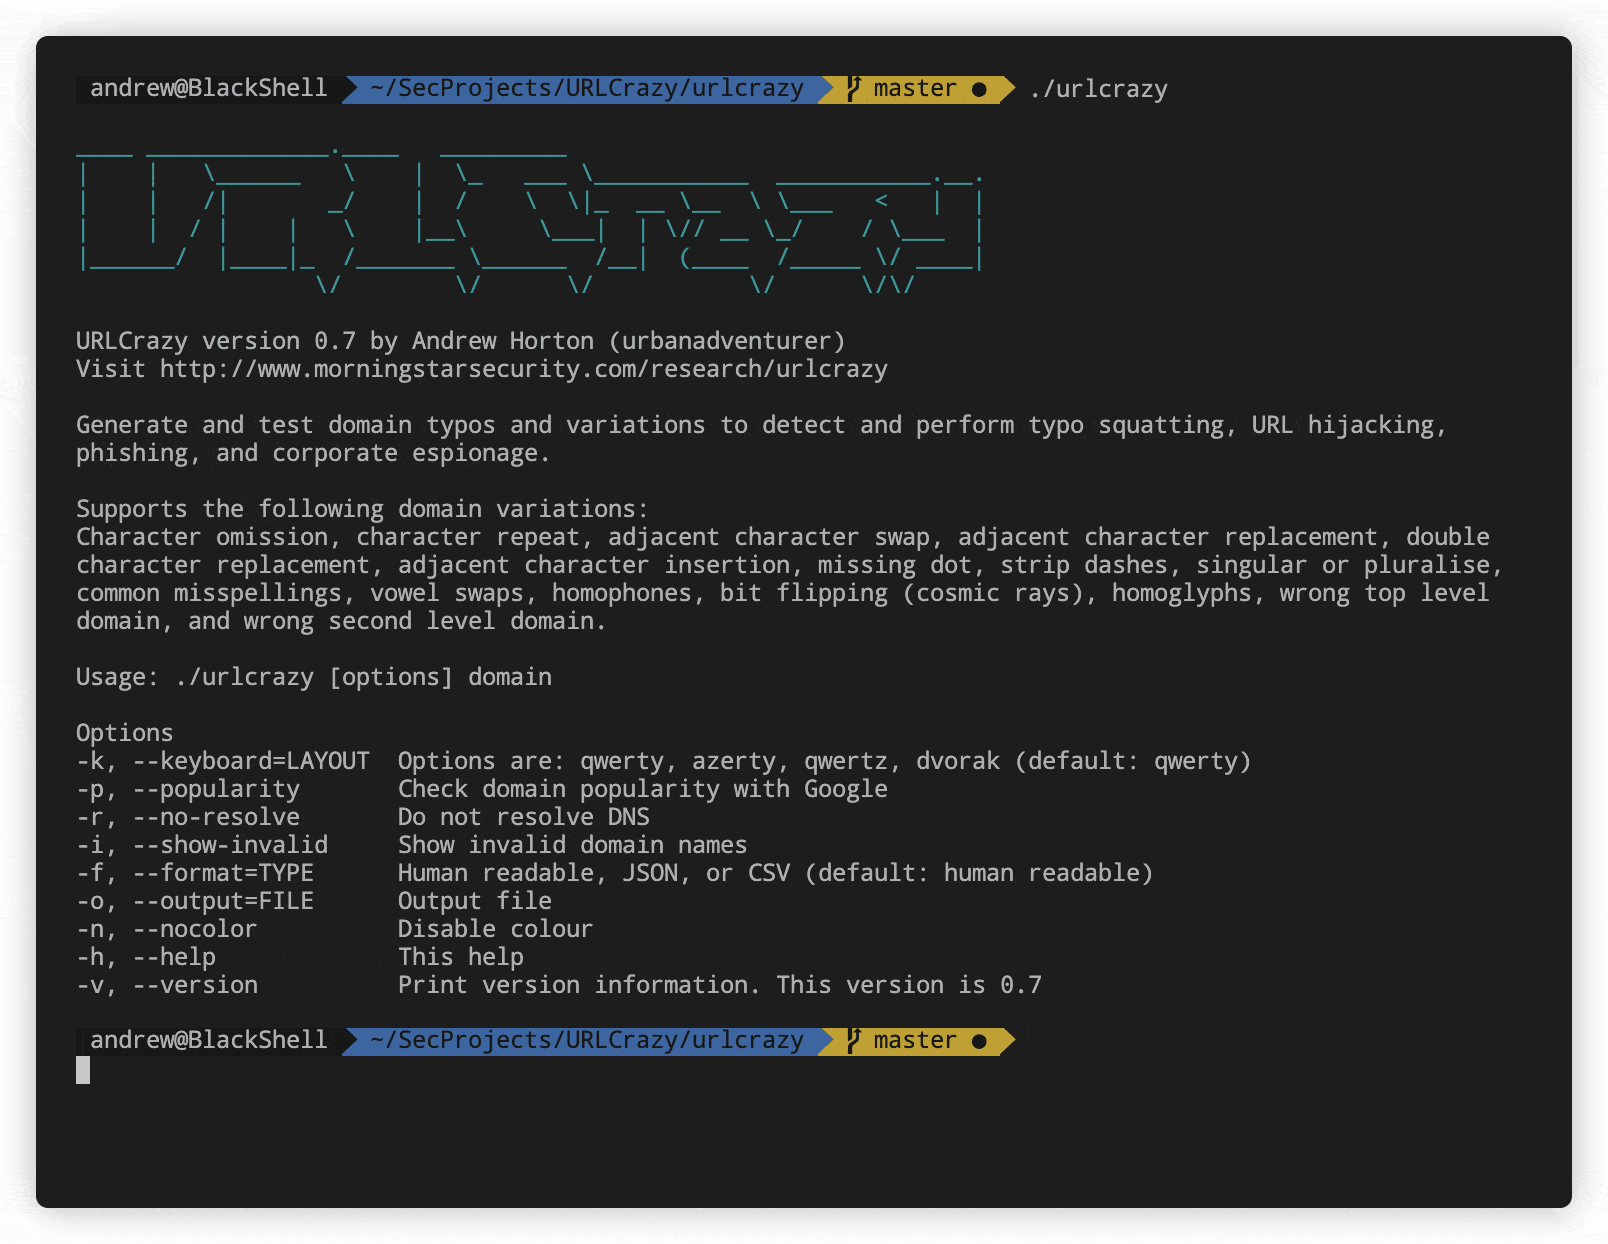 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.