 atenreiro/opensquat
OSINT tool that detects domain squatting, typosquatting, and phishing look-alikes by monitoring newly registered domains against brand keywords with DNS and VT validation.



openSquat is an Open Source Intelligence (OSINT) security tool that identifies cyber squatting threats targeting your brand or domains:
| Threat Type | Description |
|---|---|
| 🎣 Phishing | Fraudulent domains mimicking your brand |
| 🔤 Typosquatting | Domains with common typos (e.g., gooogle.com) |
| 🌐 IDN Homograph | Look-alike characters from other alphabets |
| 👥 Doppelgänger | Domains containing your brand name |
| 🔀 Bitsquatting | Single-bit errors in domain names |
"A powerful swiss army knife for brand protection" — WhoisXML API Blog, August 2022
"A handy tool for collecting information on newly registered domains." — ranked Top 5 phishing detection tool — SOCRadar Blog, July 2022
"openSquat provides essential protection against domain squatting and phishing attacks through automated monitoring and detection." — Prince Yadav, TutorialsPoint, March 2026
"OpenSquat identified 103 squatting domains, 960 active phishing websites, and 53 domains with suspicious certificates." — Sharma et al., Journal of Information Security and Cybercrimes Research (JISCR), Vol. 7, Issue 1, June 2024
openSquat follows an open-core model:
This model enables transparency and community collaboration while supporting the scale, reliability, and operational requirements of enterprise use.
pip install opensquat
opensquat -k keywords.txt
git clone https://github.com/atenreiro/opensquat
cd opensquat
pip install -r requirements.txt
python3 opensquat.py -k keywords.txt
Repo users: in all the examples below, replace
opensquatwithpython3 opensquat.pyto run from a cloned checkout.
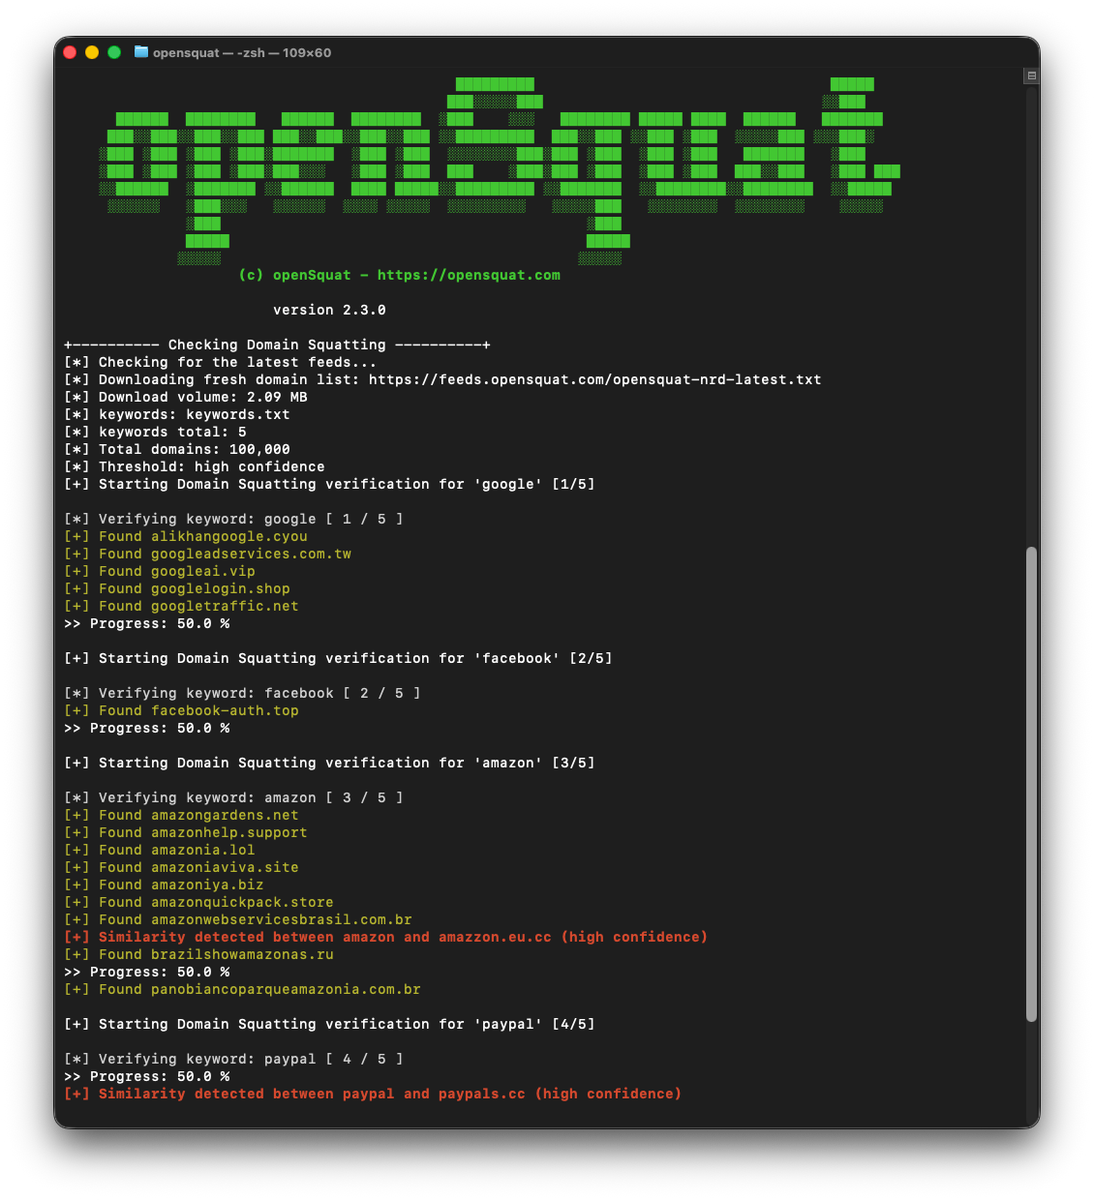
confusable_homoglyphs, homoglyphs, colorama, requests, dnspython, beautifulsoup4# Default run
opensquat
# Show all options
opensquat -h
# Use custom keywords file
opensquat -k my_keywords.txt
# DNS validation via Quad9
opensquat --dns

# Check Certificate Transparency logs
opensquat --ct

# Scan for open ports (80/443)
opensquat --portcheck

# Cross-reference phishing databases
opensquat --phishing results.txt
# Save as JSON
opensquat -o results.json -t json

# Save as CSV
opensquat -o results.csv -t csv
| Level | Flag | Description |
|---|---|---|
| 0 | -c 0 | Very high (fewer results, high accuracy) |
| 1 | -c 1 | High (default) |
| 2 | -c 2 | Medium |
| 3 | -c 3 | Low |
| 4 | -c 4 | Very low (more results, more false positives) |
Note: On the API side (
--api), the five confidence levels map to four fuzziness values (exact,low,auto,high) —-c 3and-c 4both map tohigh. See Premium and API Modes for the full mapping and how to override with--api-fuzziness.
openSquat supports three modes. The default (Community) is unchanged — existing users need no flags. The two Premium modes share a single openSquat API key; pick Premium Feed if you want the same local detection pipeline with a larger feed, or Premium API if you want server-side detection with no local feed download.
| Mode | Flag | What it does |
|---|---|---|
| Community (default) | (none) | Downloads the free NRD feed (~100k domains/day) and runs local Levenshtein detection. |
| Premium Feed | --premium | Downloads the paid NRD feed (nrd-lite, much larger) using your openSquat API key, then runs the same local Levenshtein detection. |
| Premium API | --api | Skips local feed download. Queries the openSquat lookalike REST API per keyword and returns server-side matches. |
Sign up at opensquat.com to get a key. The same key works for both Premium Feed (--premium) and Premium API (--api).
--api-key YOUR_KEY on the command lineOPENSQUAT_API_KEY environment variableapi_key.txt in the current directory (one key per file, # comments allowed)The CLI flag is visible in
psoutput. Prefer the env var or key file in shared environments.
# Premium Feed mode — same local pipeline, larger feed
export OPENSQUAT_API_KEY=os_xxxxxxxxxxxx
opensquat -k keywords.txt --premium

# Premium API mode — server-side detection per keyword
opensquat -k keywords.txt --api

# Premium API + DNS reputation check on each returned domain
opensquat -k keywords.txt --api --dns






