
fluxion
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
penetration-testingphishingred-teaming+3
6.0k
fluxionnetwork/fluxionAutomated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
 atenreiro/opensquat
OSINT tool that detects domain squatting, typosquatting, and phishing look-alikes by monitoring newly registered domains against brand keywords with…
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 dionach/phemail
PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
 antisnatchor/phishlulz
Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…
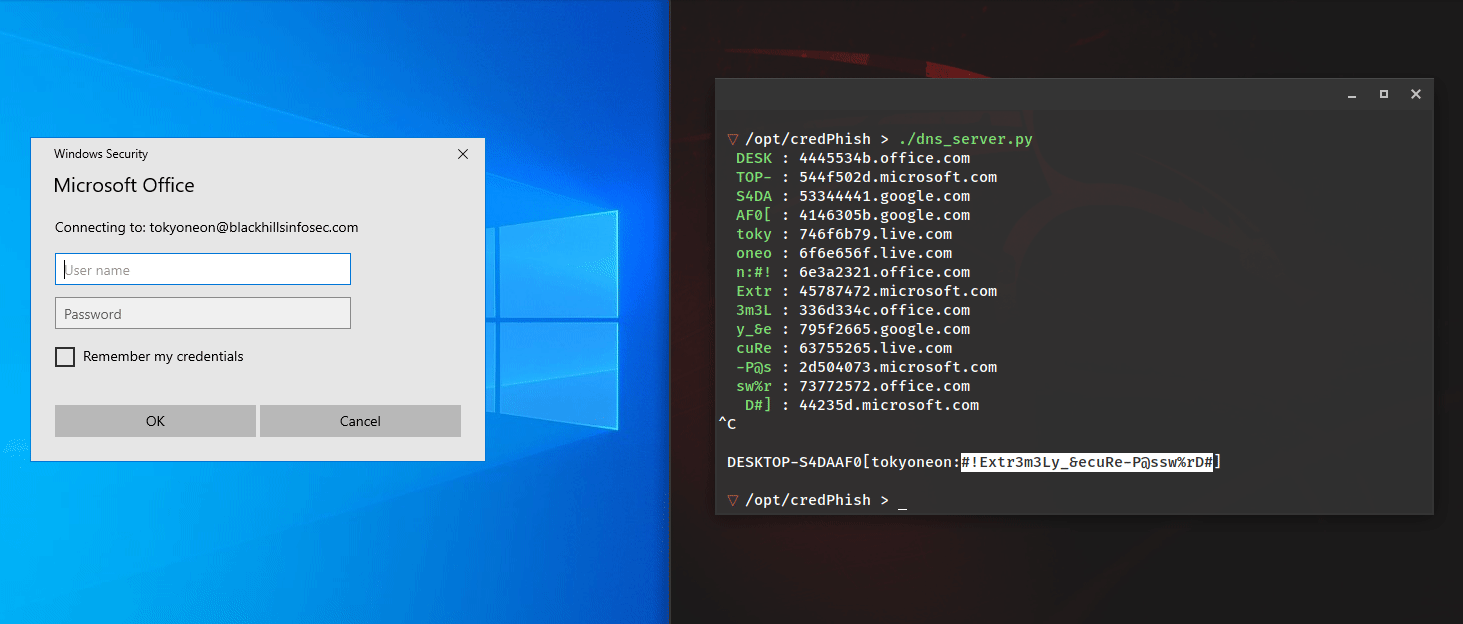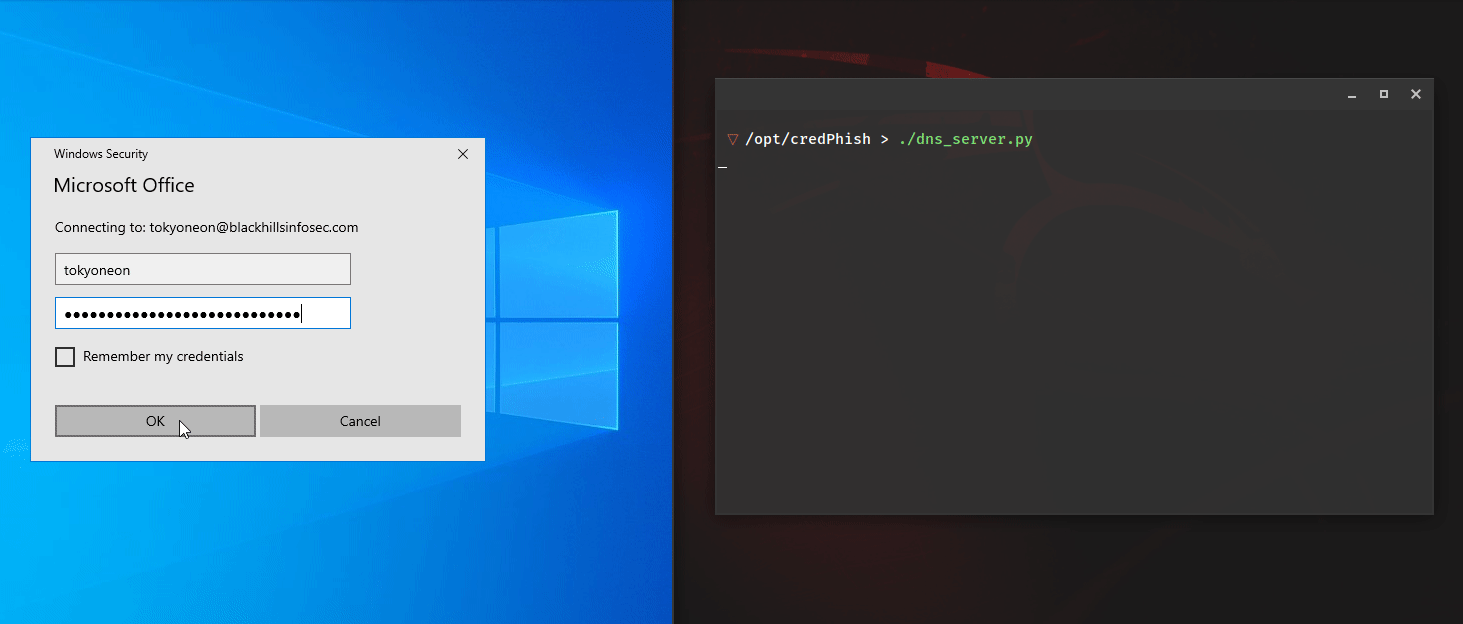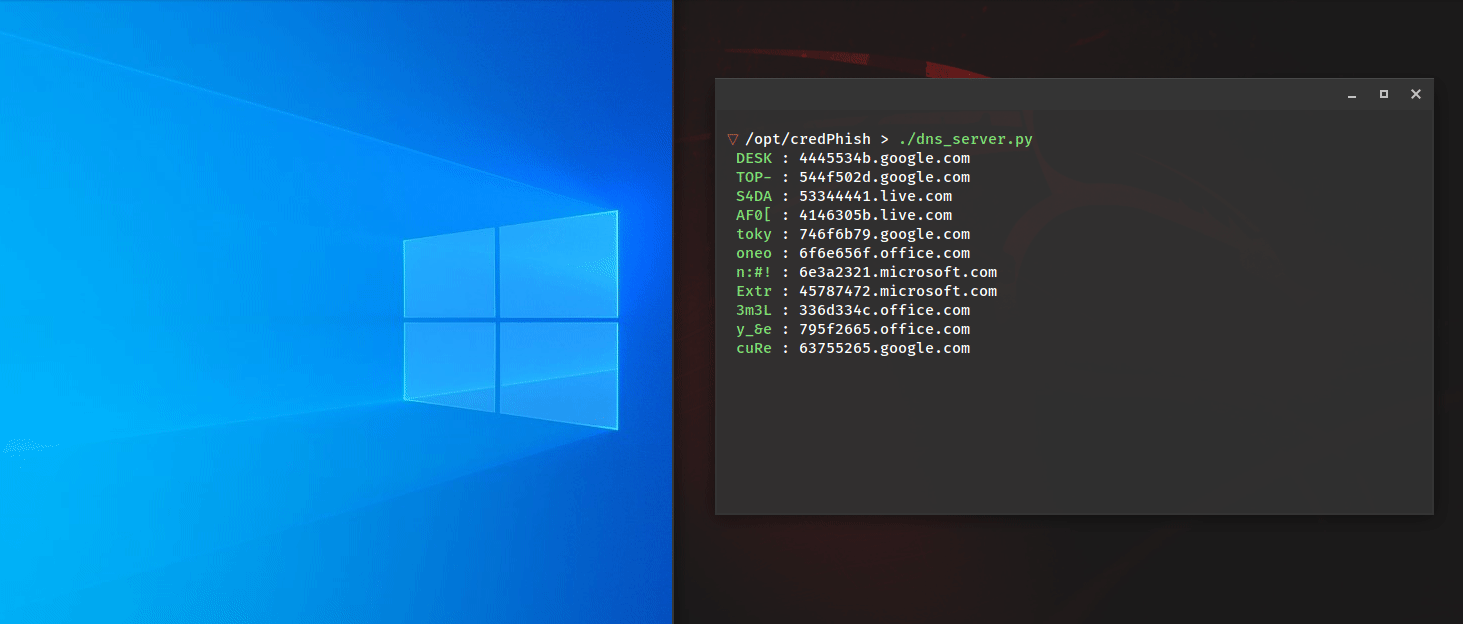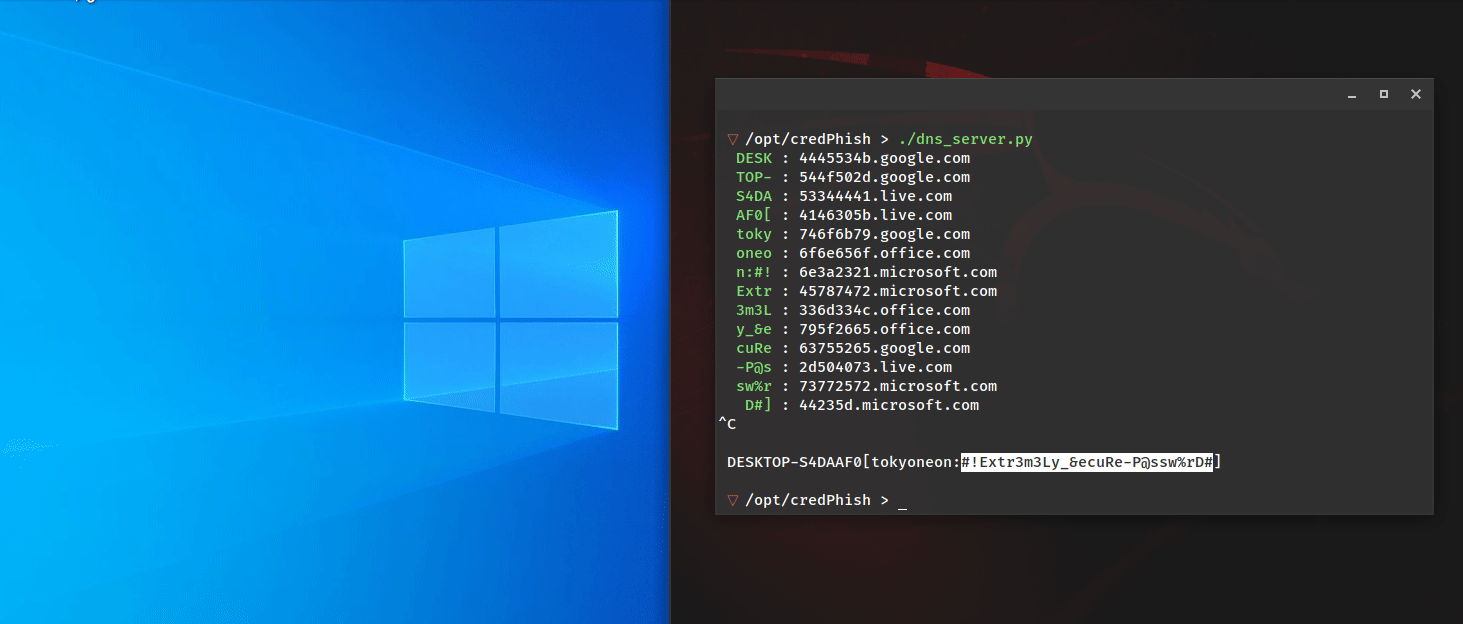 tokyoneon/credphish
PowerShell script that invokes legitimate credential prompts and exfiltrates captured passwords over DNS using CredentialPicker and Resolve-DnsName.
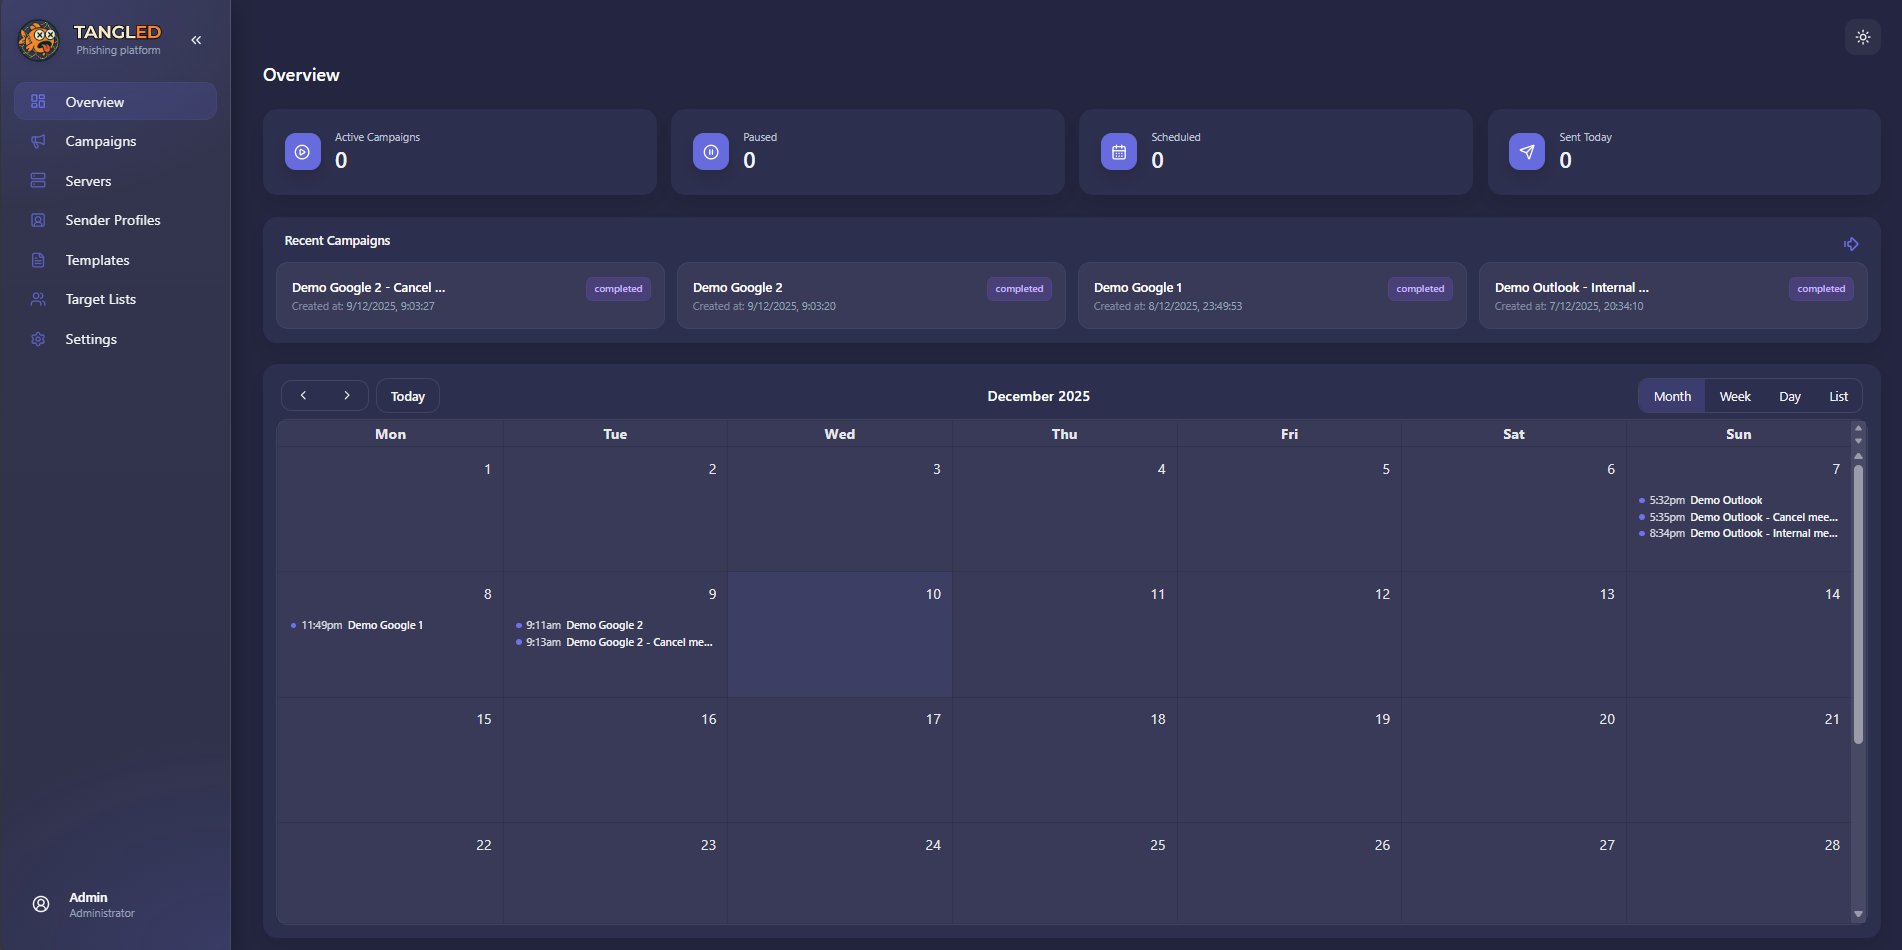 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
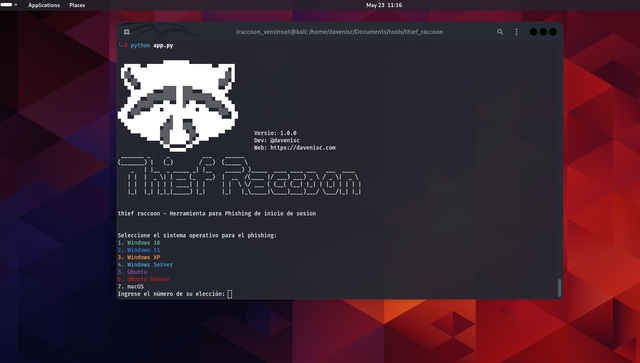 davenisc/thief_raccoon
Educational phishing simulation tool that mimics OS login screens to capture credentials for cybersecurity awareness training. Supports Windows,…
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 ilianazz/young-domain-guard
Browser extension that warns users about recently registered domains to prevent phishing attacks. Queries RDAP to check domain age and displays…
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 rat5ak/cve-2025-59382-qnap-password-reset-account-takeover
Proof-of-concept and technical writeup for CVE-2025-59382, an unauthenticated password reset URL injection in QNAP NAS that enables a…
 roxanne_ardary/emailxpose
EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…