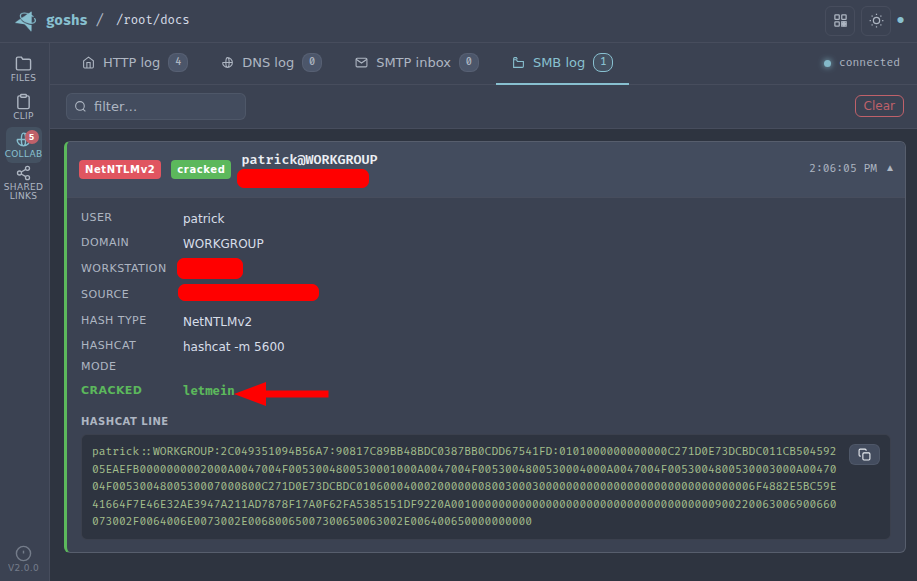
Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

Tools and Techniques for Red Team / Penetration Testing

Modlishka. Reverse Proxy.

HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…

PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2

Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…

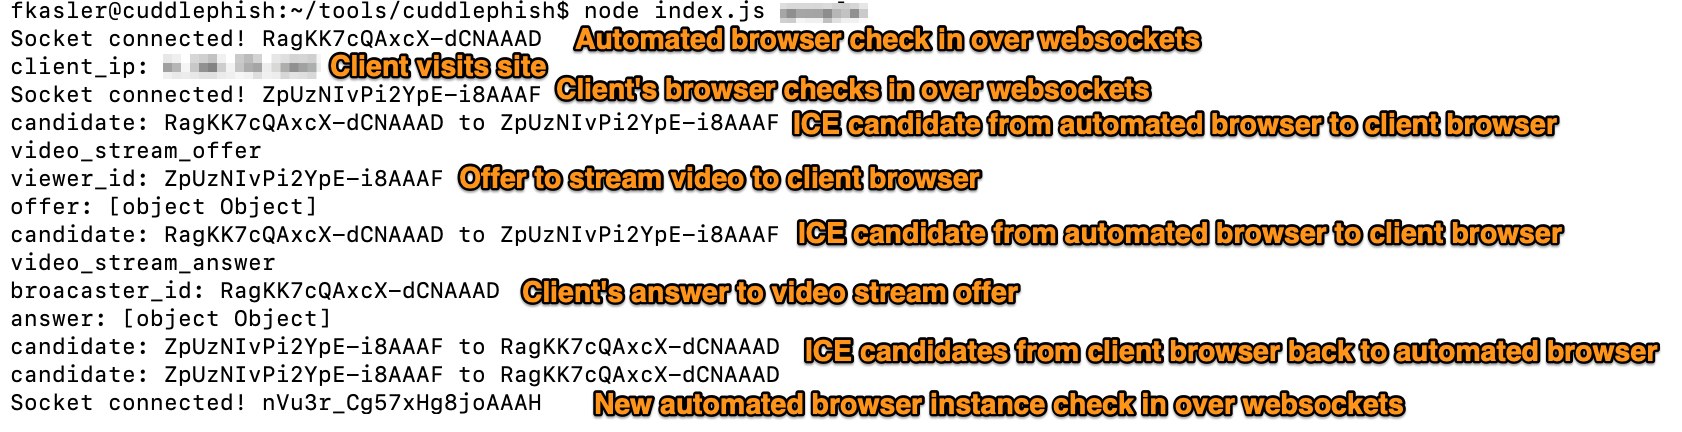
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers

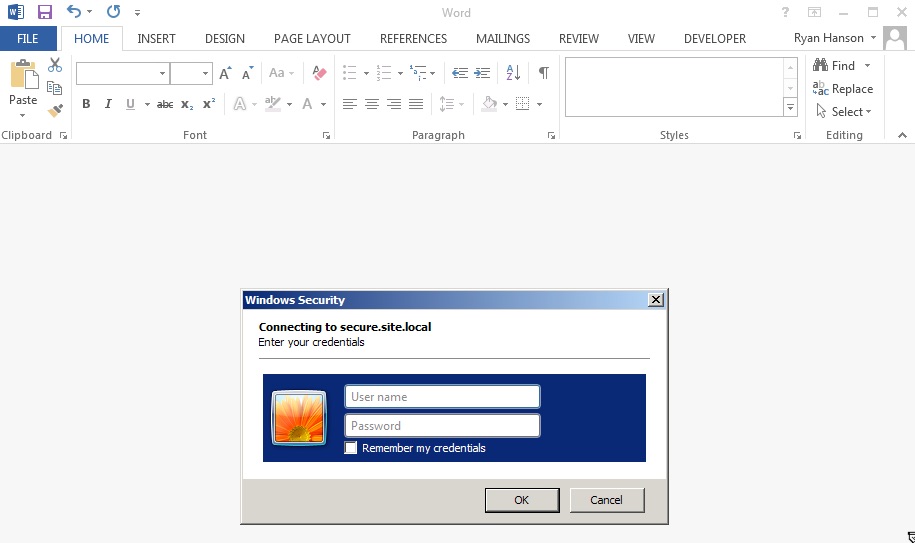
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector

Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.

Social Engineering Tool

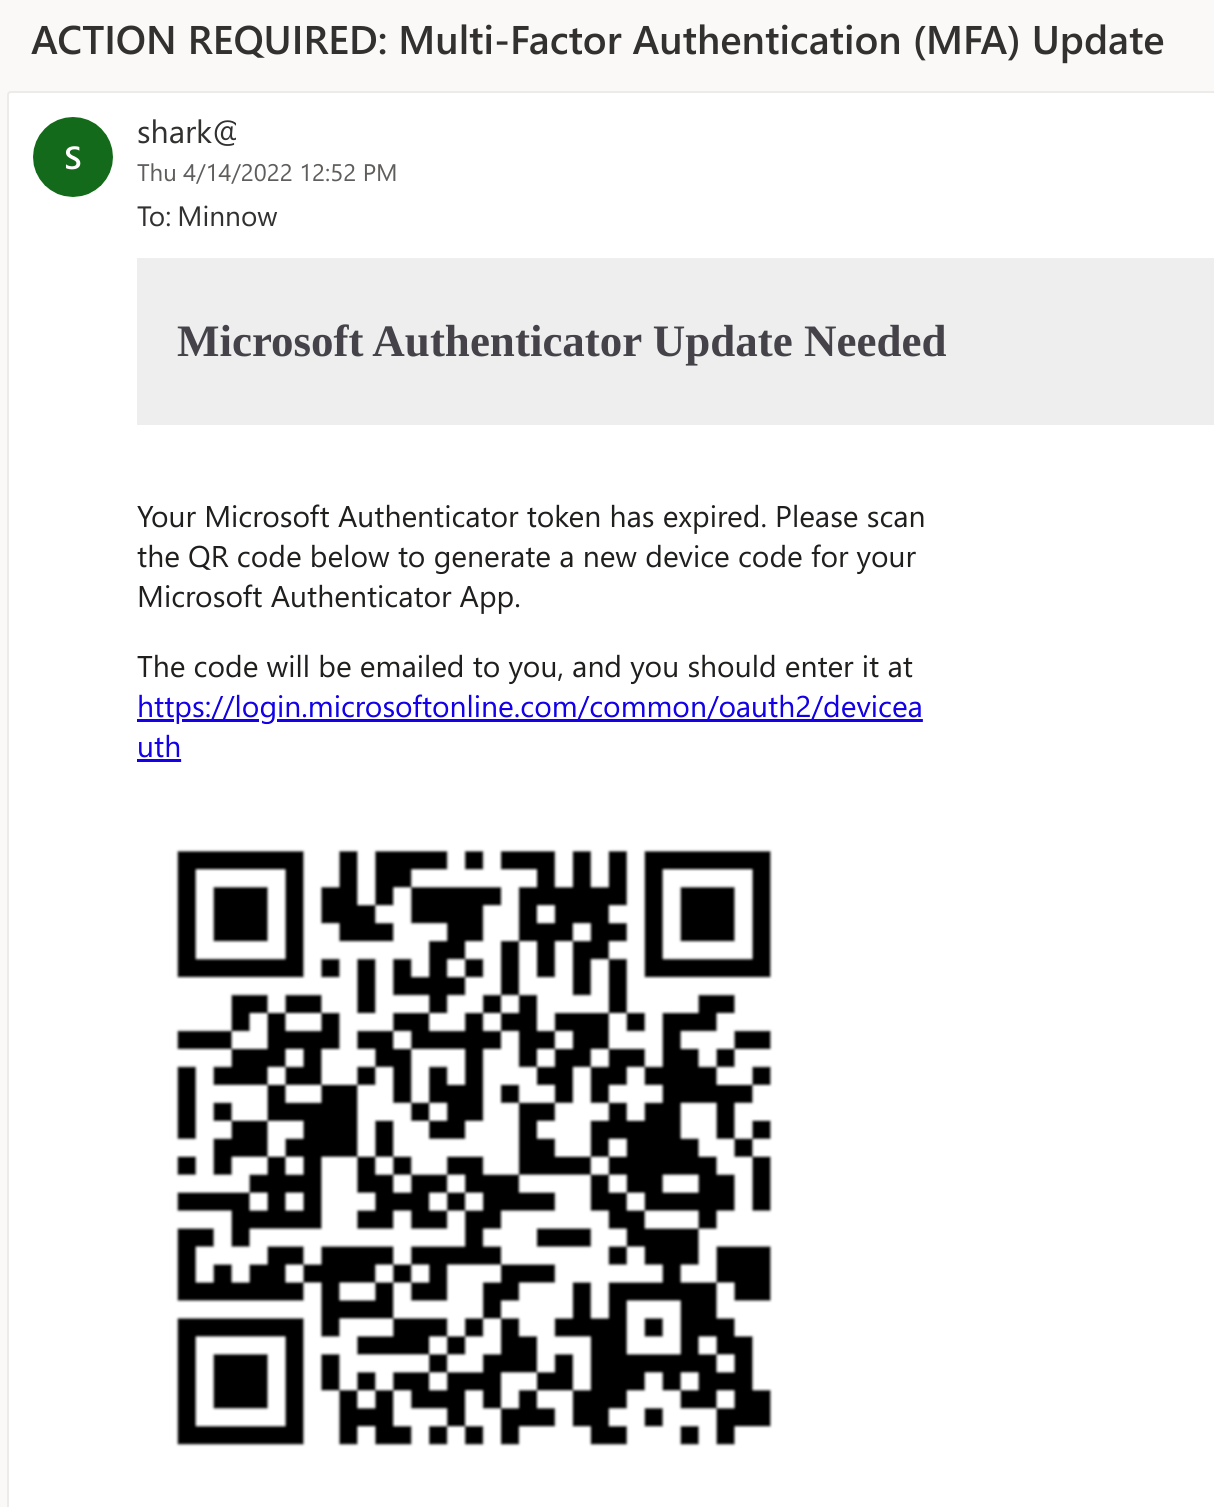
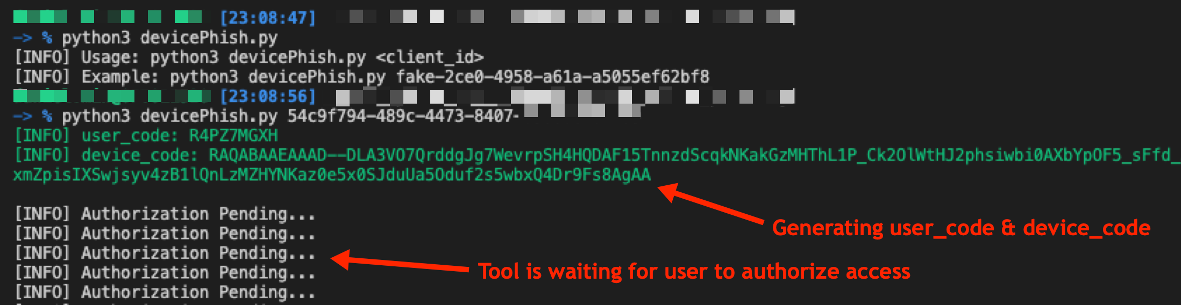
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…

OTP BOT Bypass SMS verifications from Paypal, Instagram, Snapchat, Google, 3D Secure, and many others...

Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.

A proof-of-concept script to conduct a phishing attack abusing Microsoft 365 OAuth Authorization Flow

Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…

Artifacts for the USENIX publication.

A home for detection content developed by the delivr.to team