

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
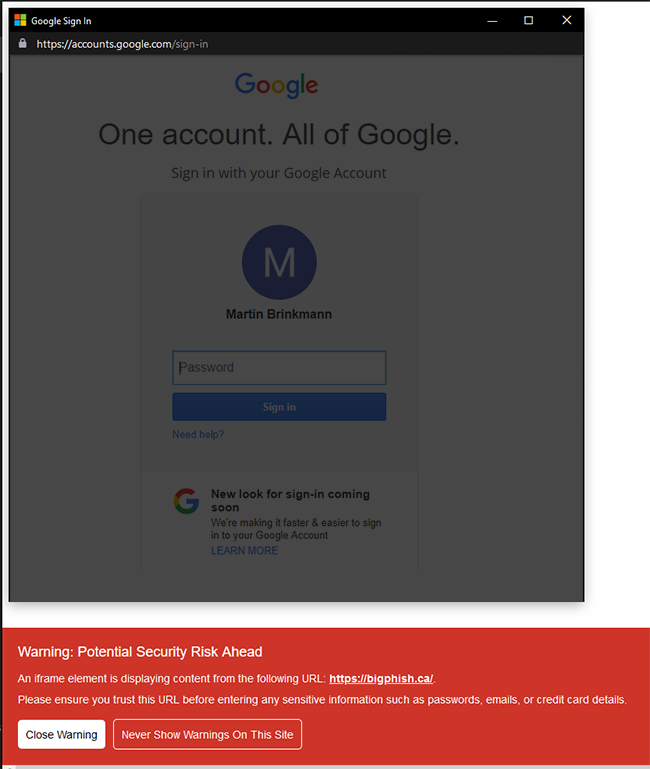 malwarecube/enhanced-iframe-protection
A lightweight extension to automatically detect and provide verbose warnings for embedded iframe elements in order to protect against…
 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
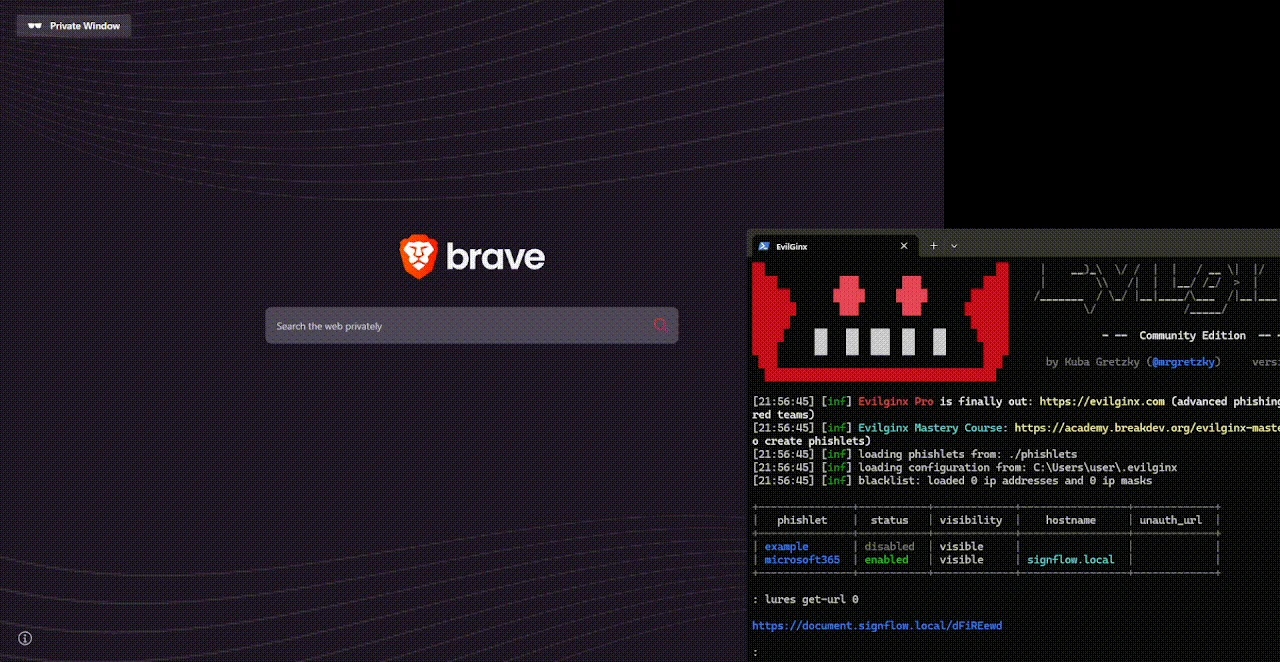 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
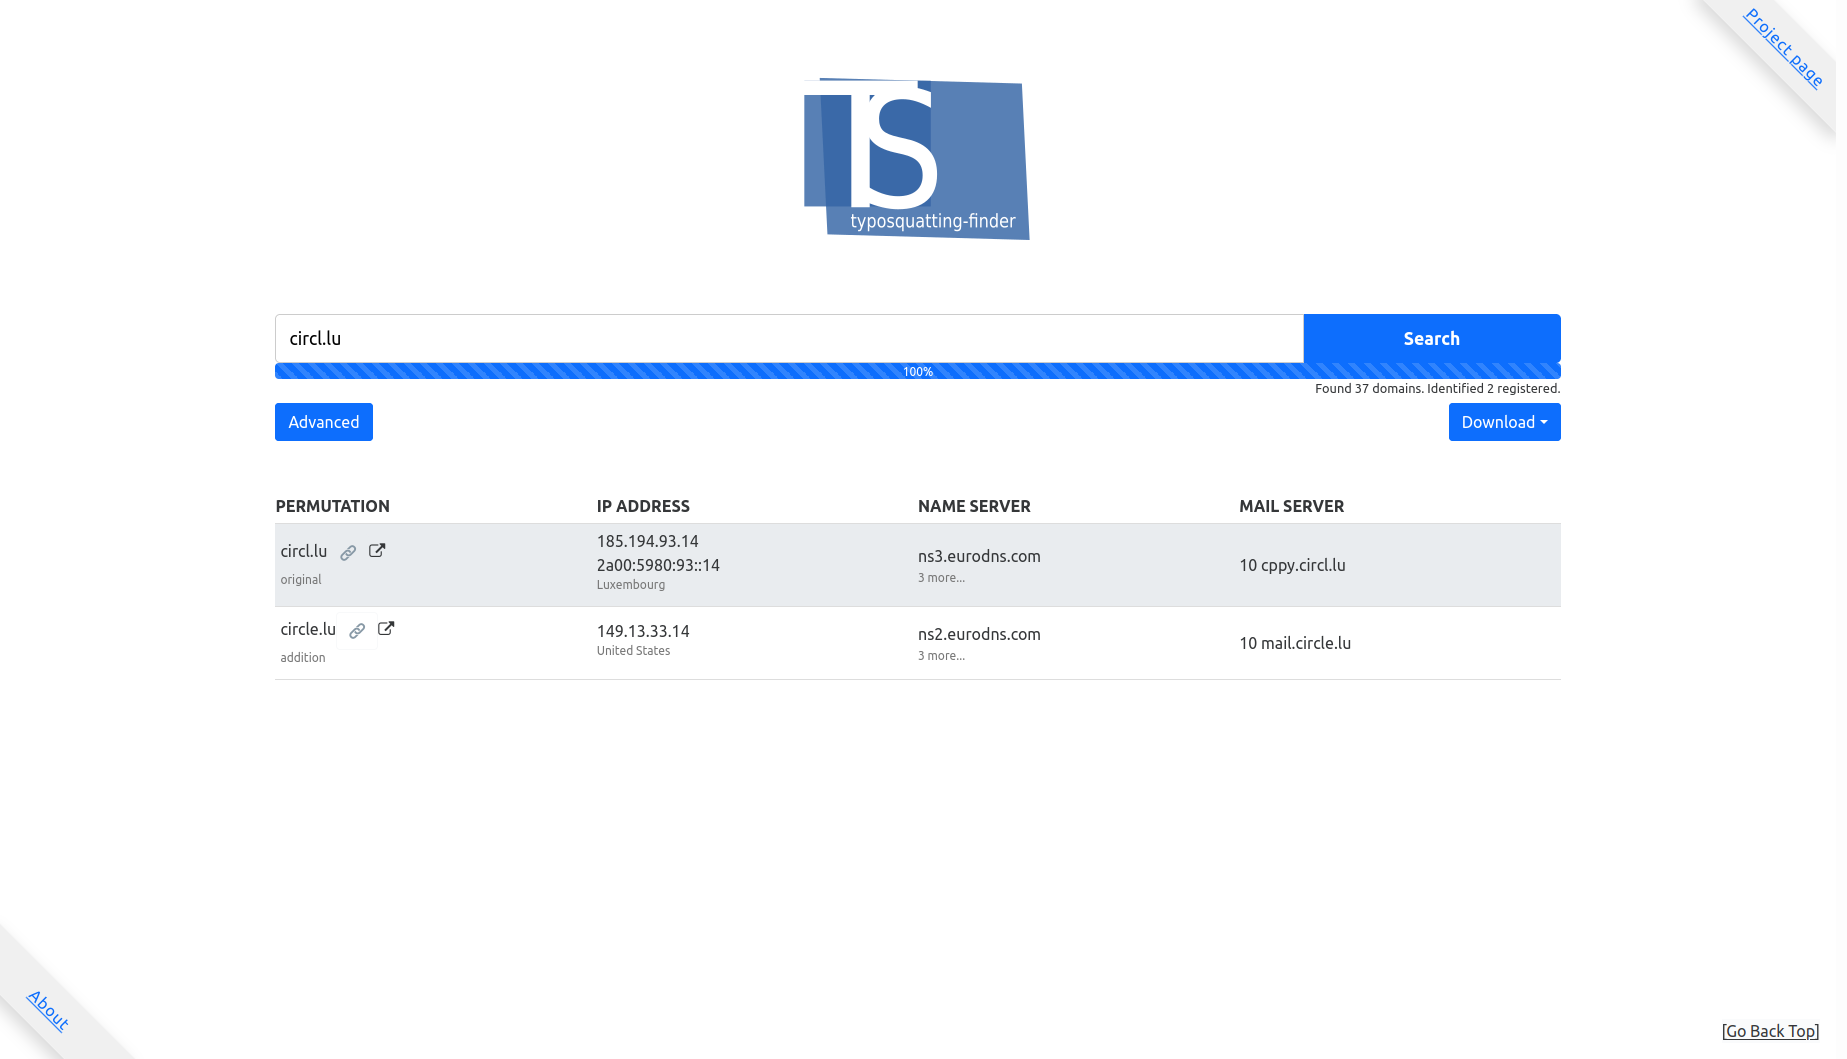 typosquatter/ail-typo-website
Website for ail-typo-squatting library
 alessandrobertoldi/research
Published security research repository featuring academic papers on domain hijacking, 2FA bypass, and large-scale spoofing techniques, authored by…
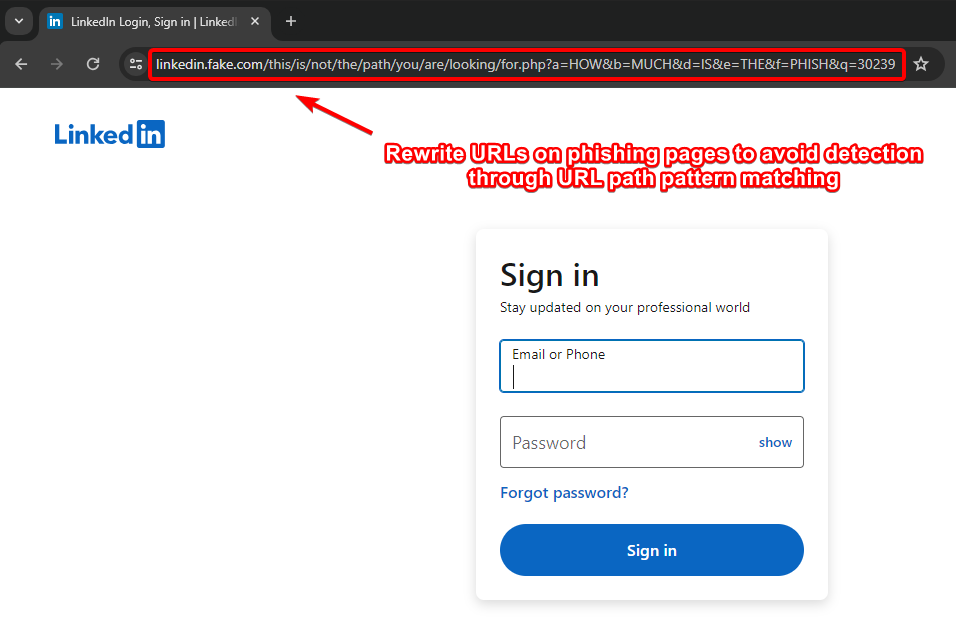 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs
 imthecopilotnow/cve-2025-4102025
Security advisory detailing a critical CVE in Copilot AI where RAG-based citation links are forged to a third-party domain, enabling source…
 sudosammy/cve-2017-15394
Demonstrates an IDN homograph attack in Chromium extensions to spoof URLs, aiding in deception attacks by coercing victims into granting permissions…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 gregory-chatelier/huntglyph
Detect visually similar characters (homoglyphs) and hidden data in text to protect against deceptive attacks