Windows-Defender-Security-Auditor-CVE-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

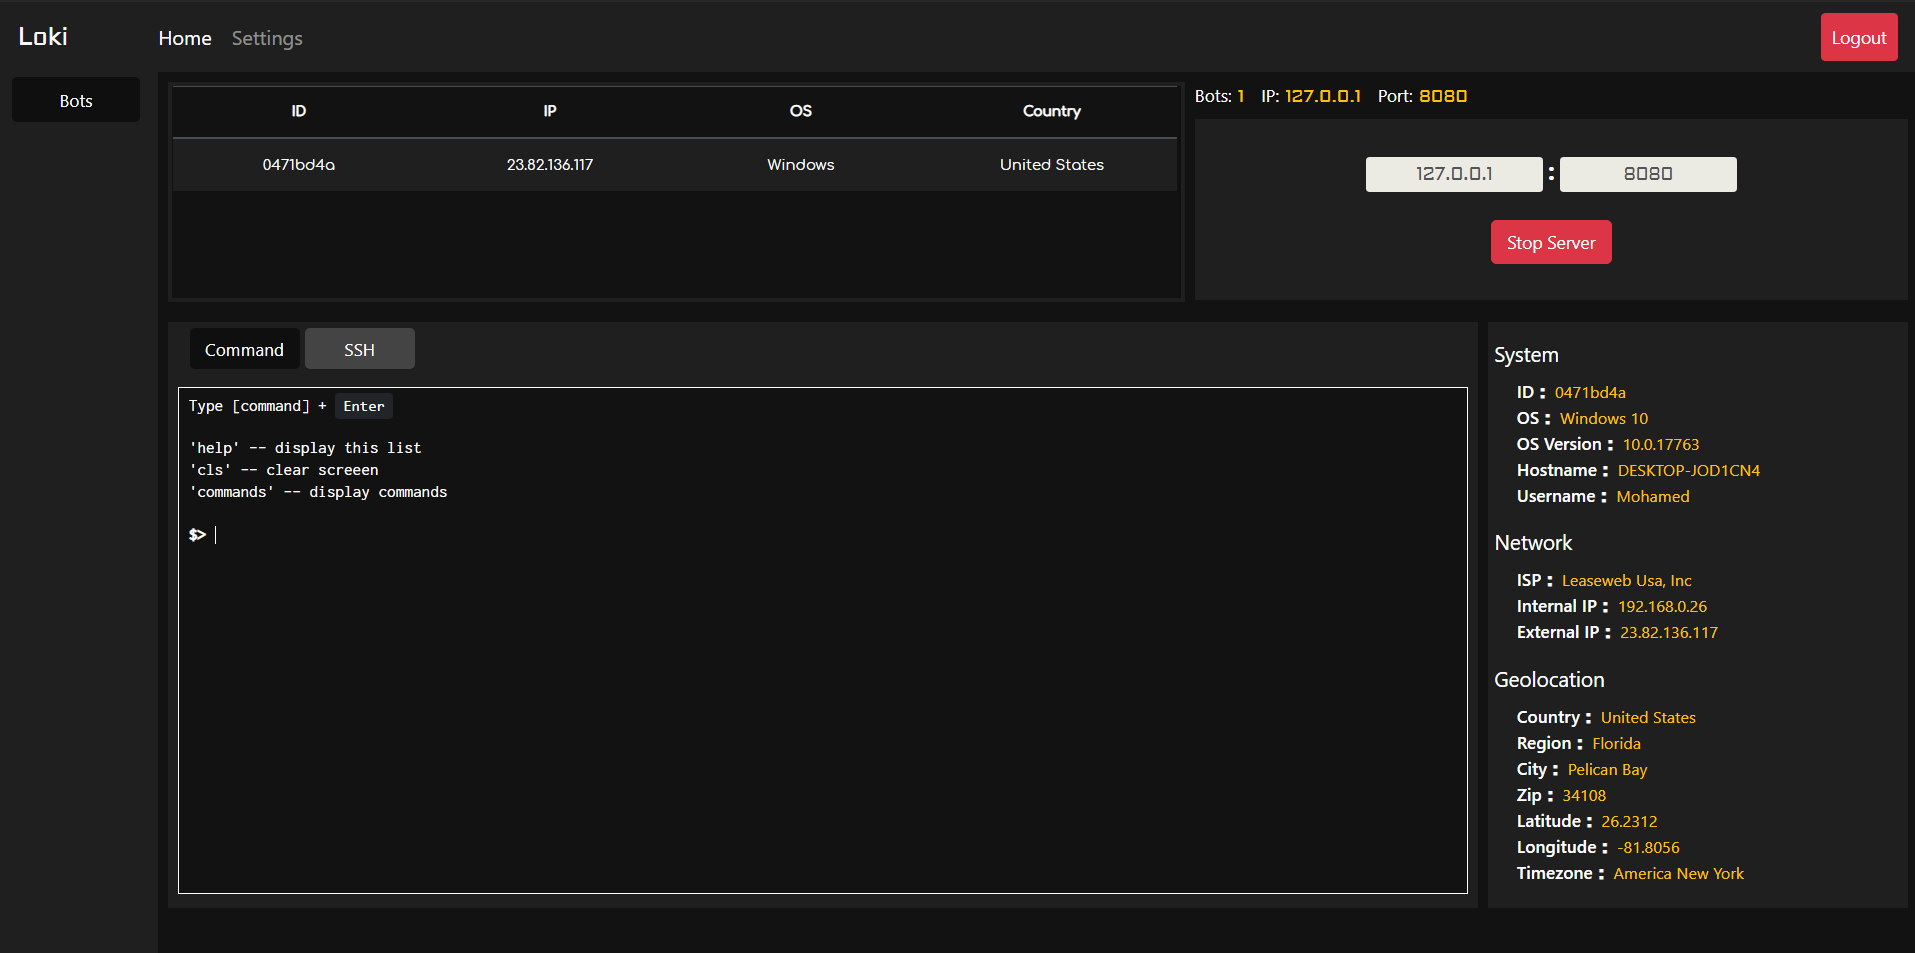
A Simple android remote administration tool using sockets. It uses java on the client side and python on the server side

PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…

SkyRAT - Powershell Remote Administration Tool

Remote administration service which uses twitter as a command and control server

THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.

A little tool to play with Windows security

iOS/macOS/Linux Remote Administration Tool

A tool to abuse Exchange services

An information security preparedness tool to do adversarial simulation.

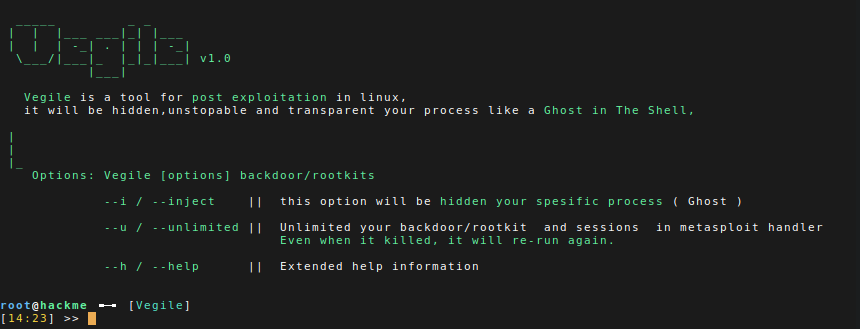
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

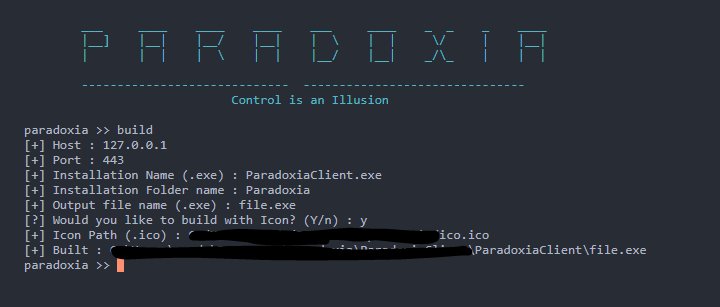
ParadoxiaRat : Native Windows Remote access Tool.

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

A tool to transform Chromium browsers into a C2 Implant

Tool to create hidden registry keys.

Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence

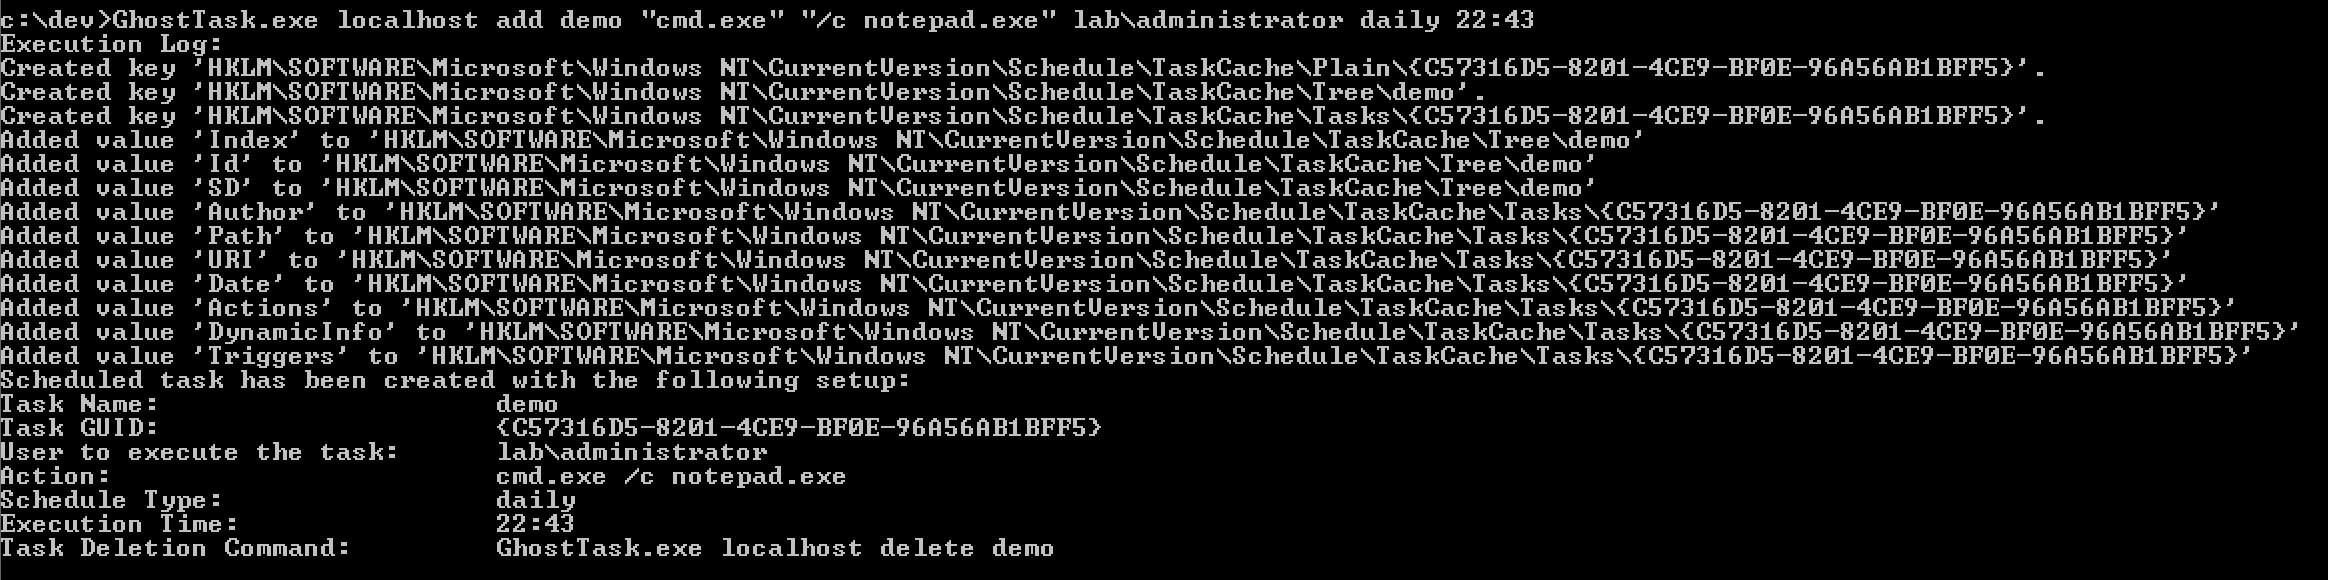
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.