samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…

Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…

Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…

Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…

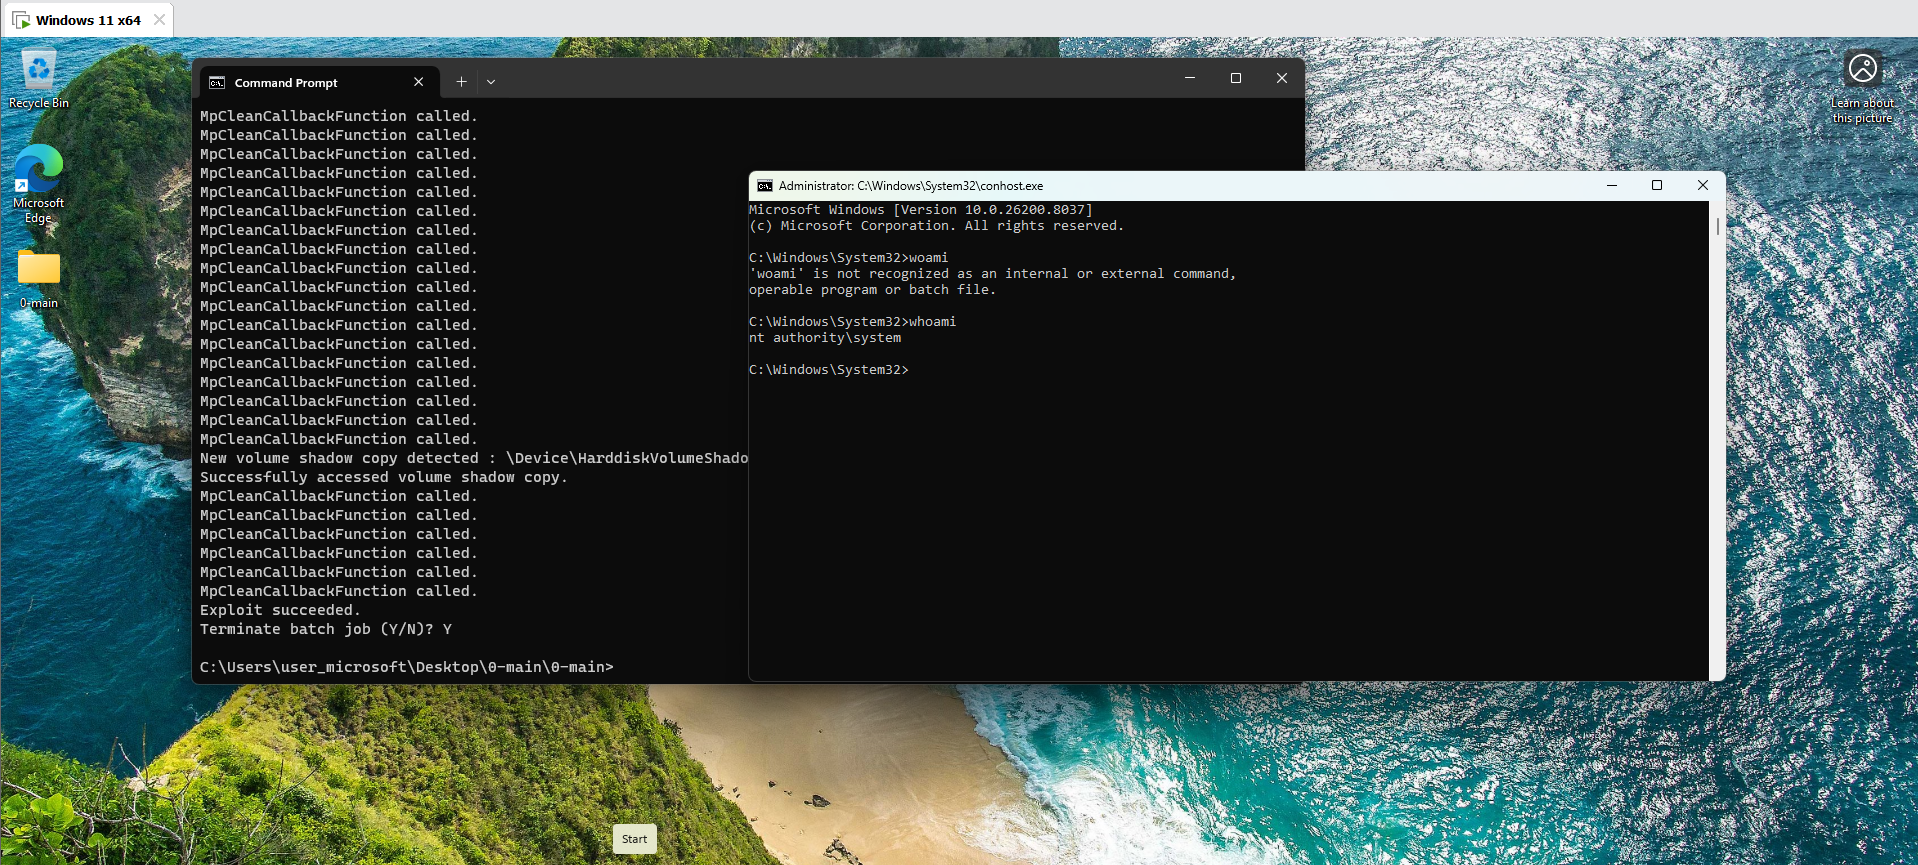
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…

Exploit for Apache Kyuubi path traversal (CVE-2026-52680) achieving unauthenticated arbitrary file write and code execution via profile.d shell…

Post-exploit a compromised etcd, gain persistence and remote shell to nodes.

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.

Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…

Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.

A Windows Remote Administration Tool in Visual Basic with UNC paths