

SandboxBootkit
 thesecretclub/sandboxbootkit
Bootkit for Windows Sandbox to disable DSE/PatchGuard.
binary-exploitationdefensive-toolsexploitation+5
349
thesecretclub/sandboxbootkitBootkit for Windows Sandbox to disable DSE/PatchGuard.
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
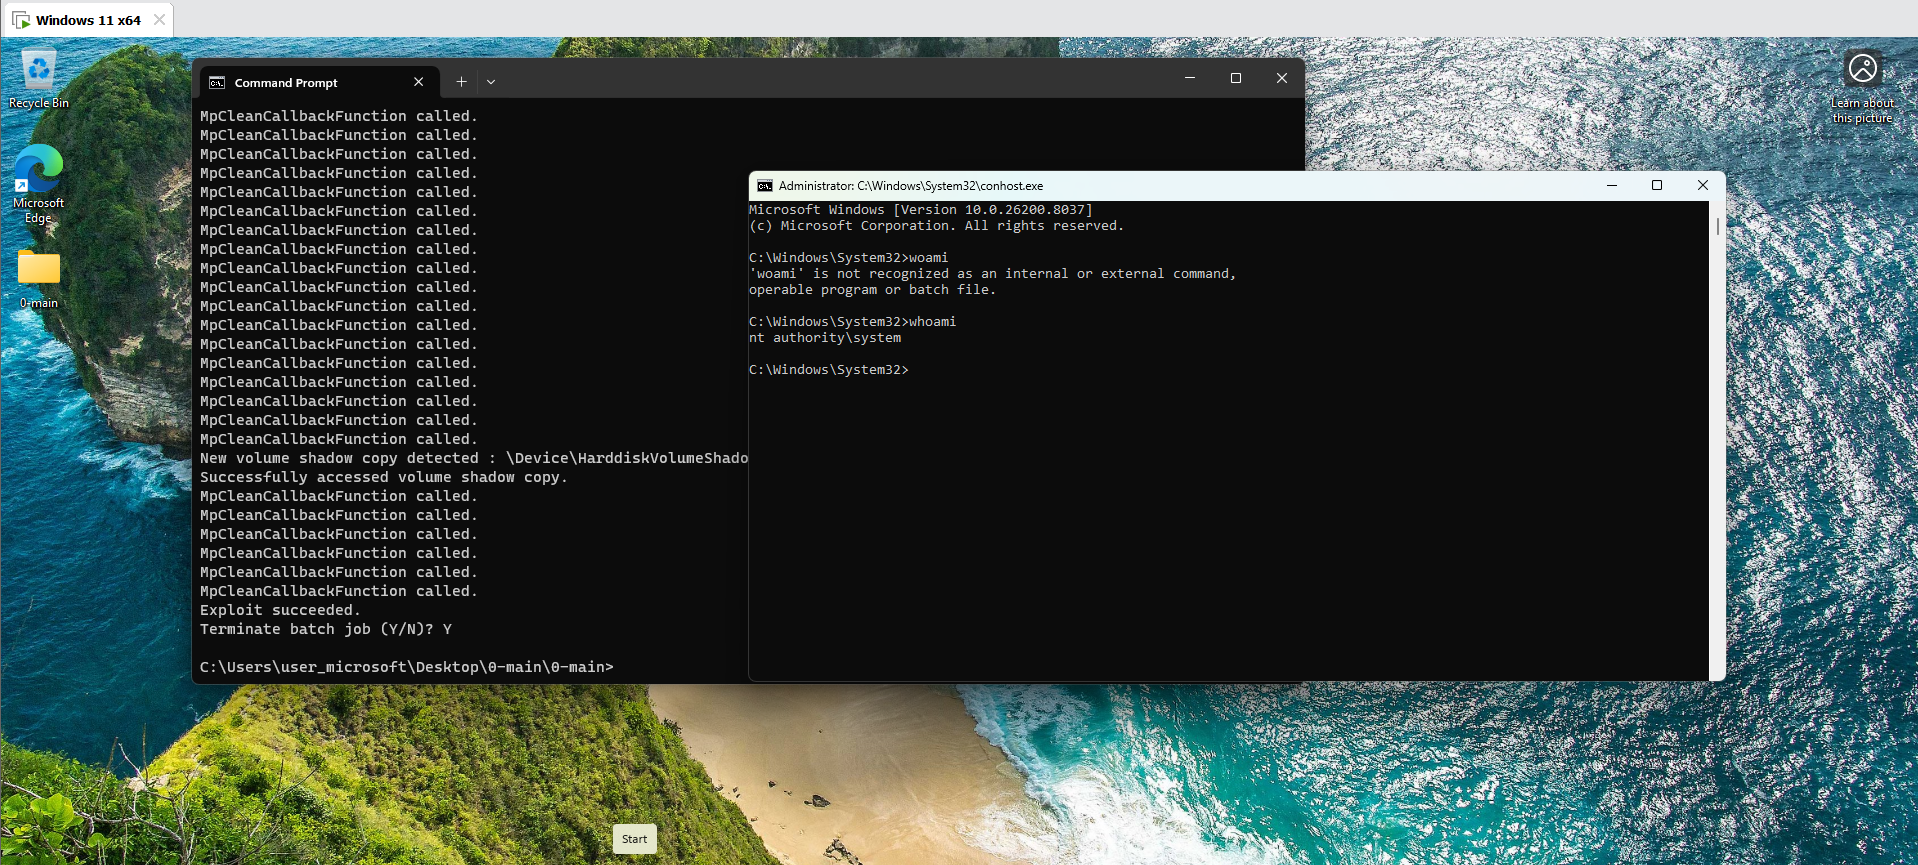
 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
 nuky-alt/cve-2025-8088
Proof-of-concept exploit and technical analysis for a WinRAR path traversal vulnerability enabling code execution via crafted archives with binary…
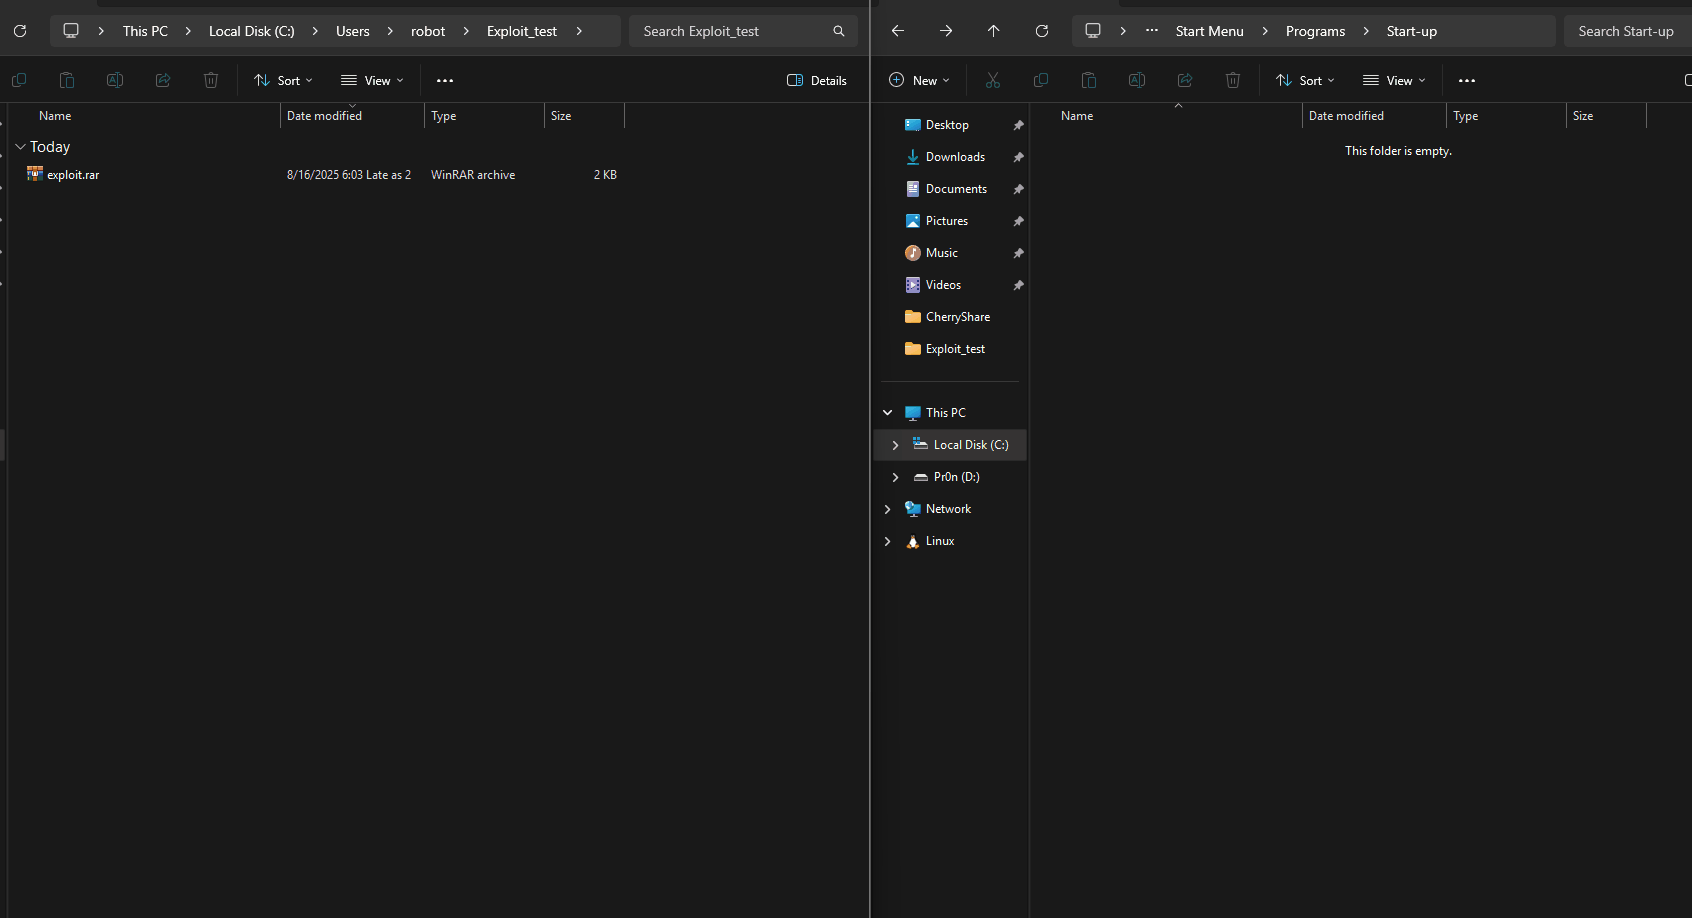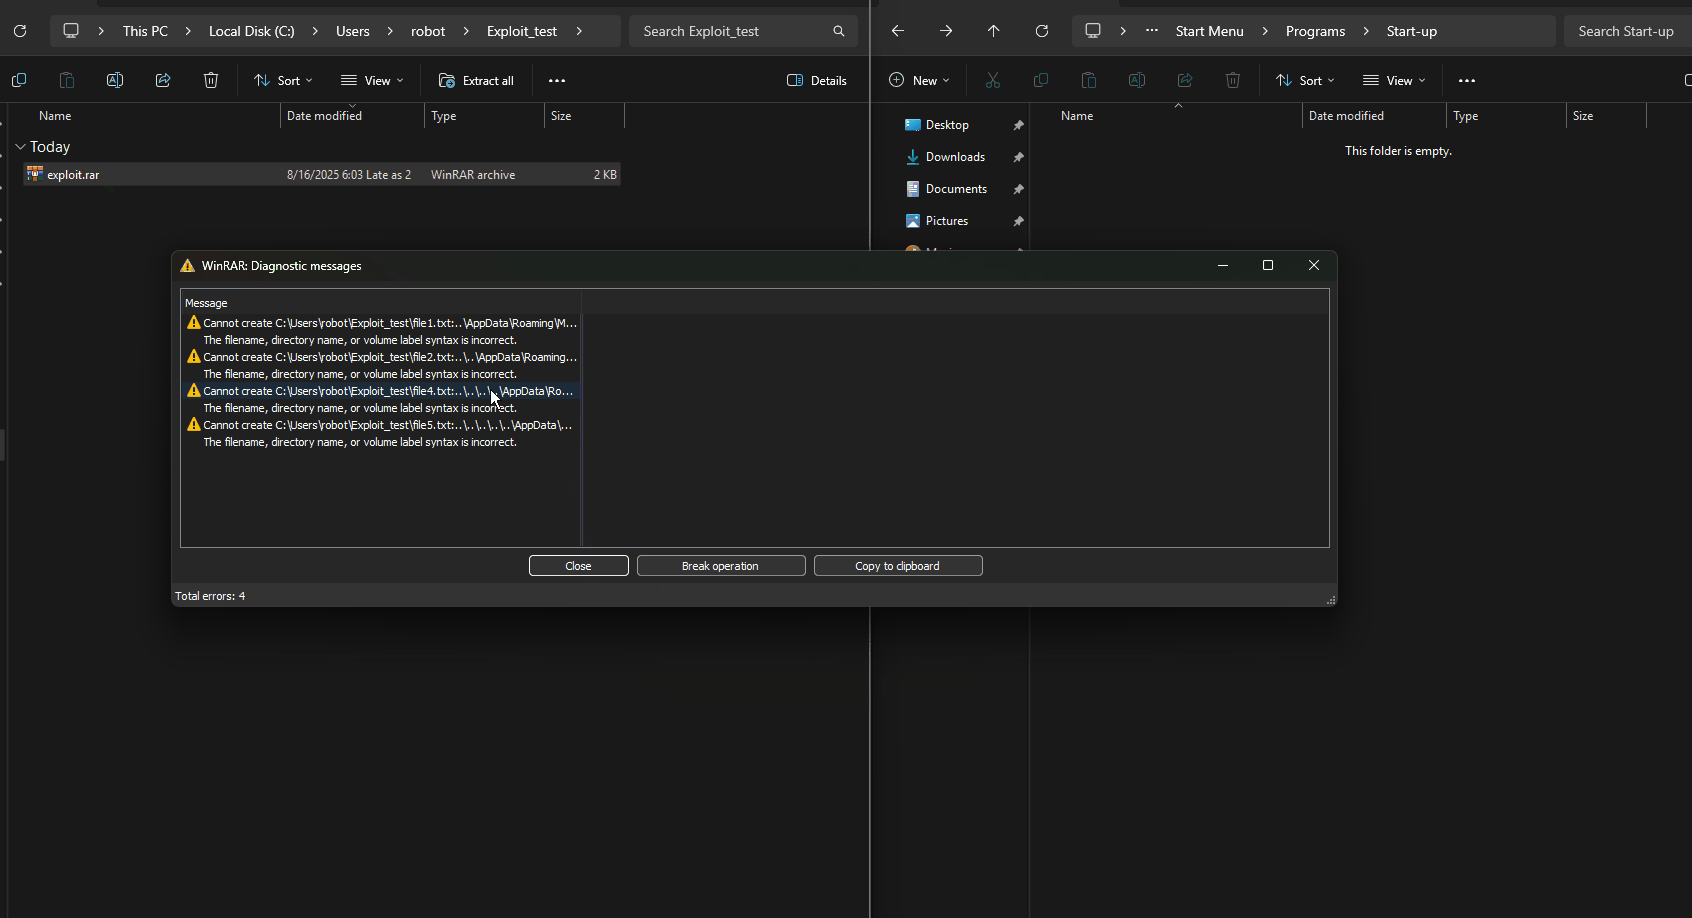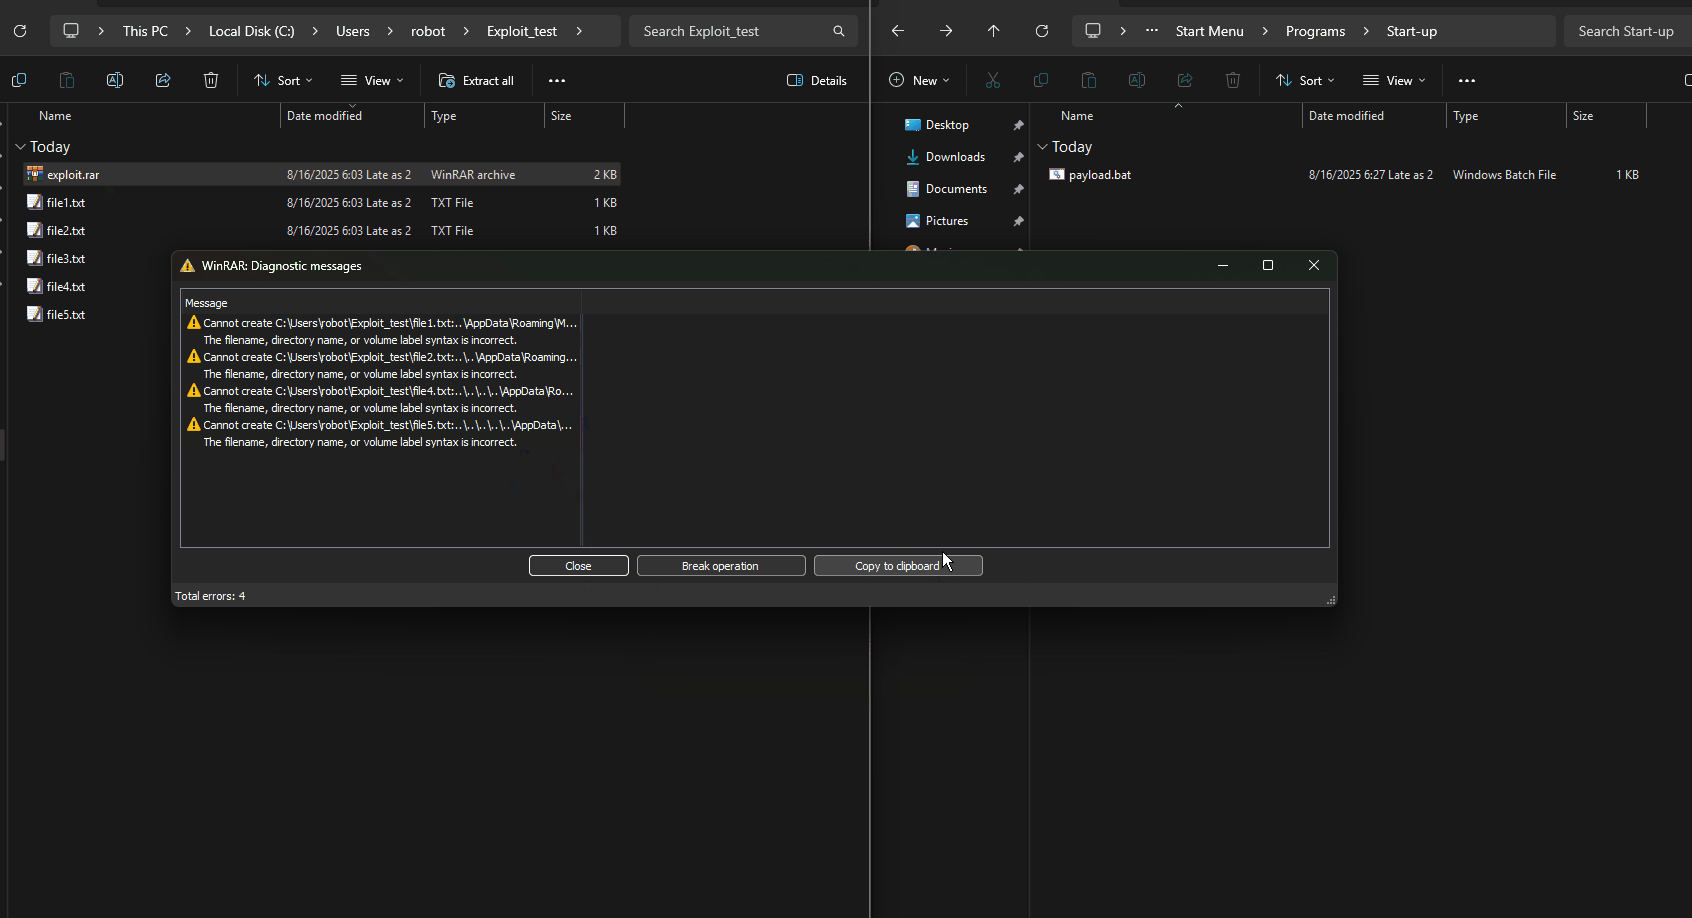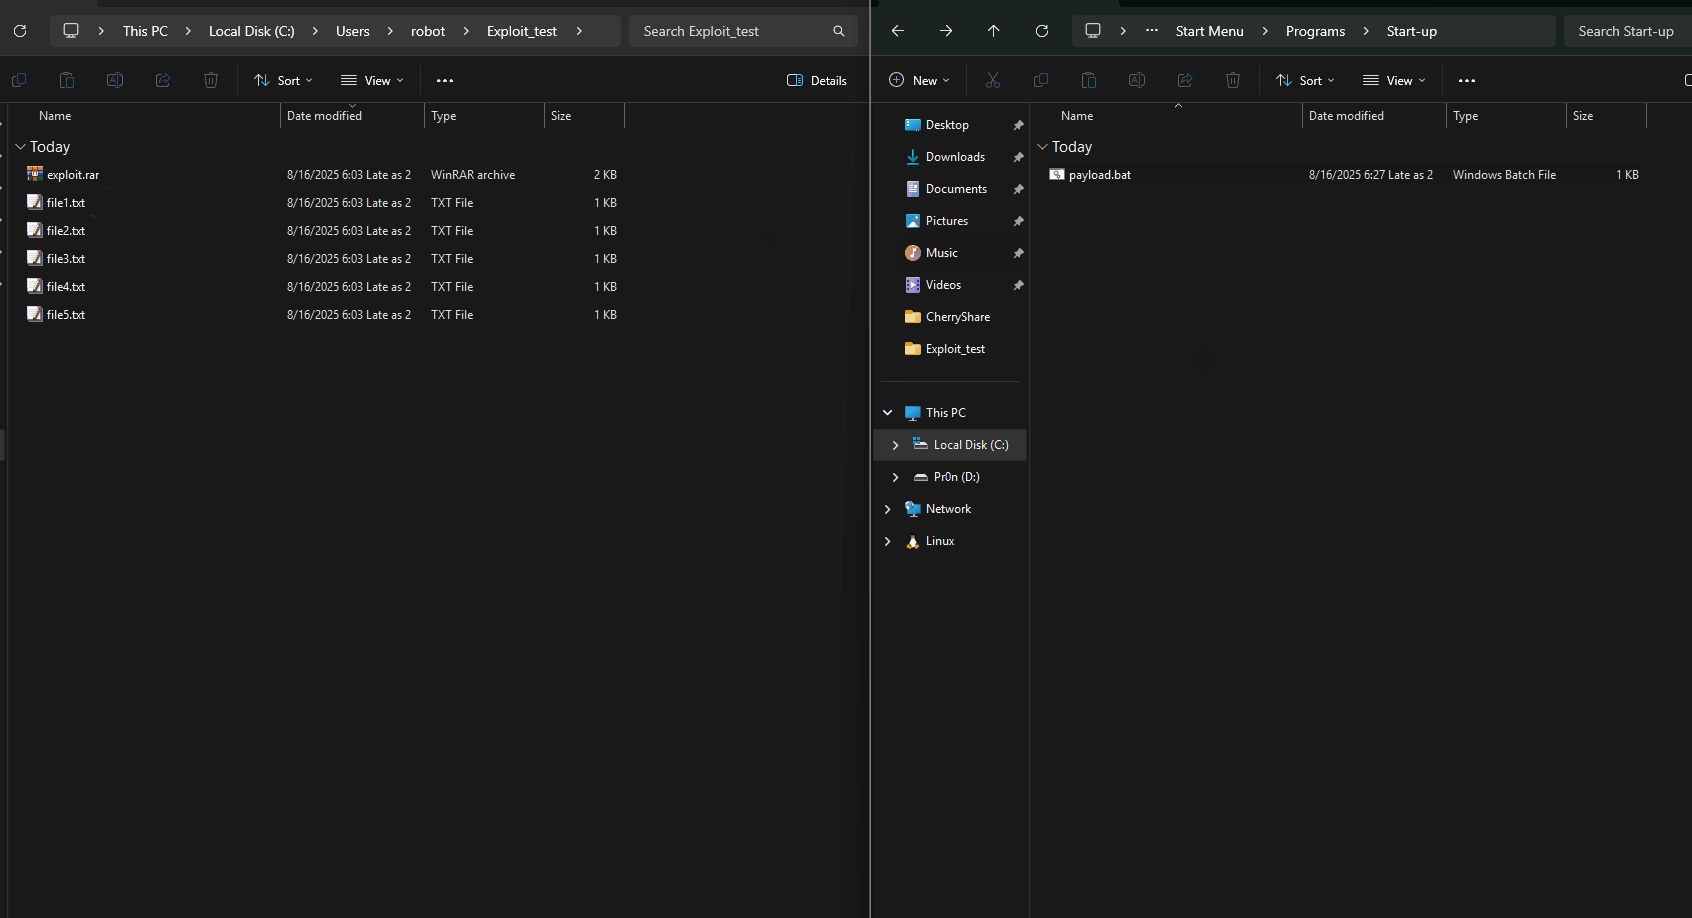 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)
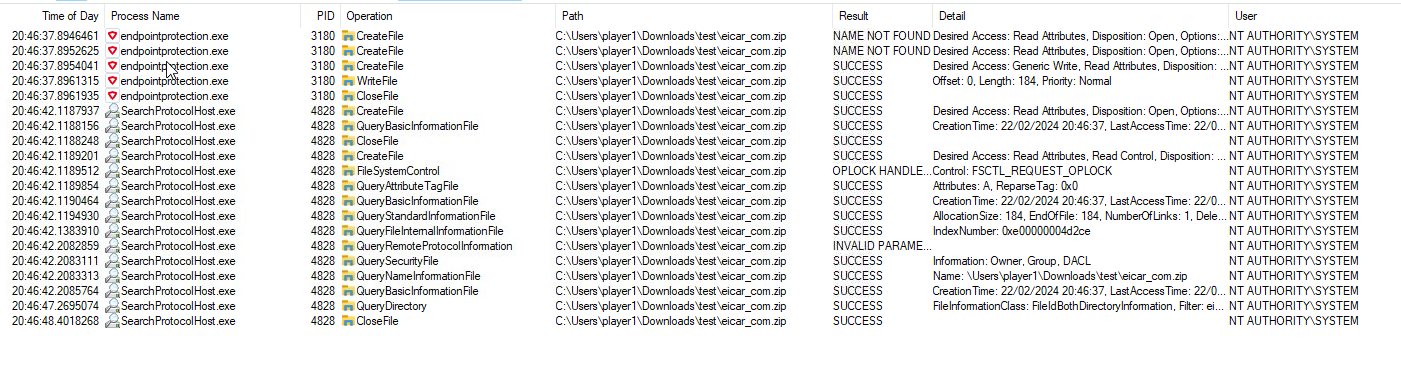 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 pexlexity/winrar-cve-2025-8088-path-traversal-poc
Proof-of-Concept for CVE-2025-8088 vulnerability in WinRAR (path traversal via ADS)