
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
phpsploit preview

phpsploit

GitHubnil0x42/phpsploit

Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor

command-and-controlexploit-frameworkspayload-development+6
2.5k
2 years ago
mimikatz preview

mimikatz

GitHubgentilkiwi/mimikatz

A little tool to play with Windows security

authenticationexploitationexploit-frameworks+10
21.9k5 months ago
wasmforge preview

wasmforge

GitHubpraetorian-inc/wasmforge

WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

binary-analysiscommand-and-controlexploit-frameworks+9
1313 months ago
GodGenesis preview

GodGenesis

GitHubsaumyajeetdas/godgenesis

A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
command-and-controldata-exfiltrationinformation-gathering+5
5322 years ago
thorse preview

thorse

GitHubpushpenderindia/thorse

THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.

anti-botcommand-and-controlexploit-frameworks+6
6133 years ago
wmi-static-spoofer preview

wmi-static-spoofer

GitHubalex3434/wmi-static-spoofer

Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
exploitationhardware-hackinghardware-iot-security+4
5167 years ago
RATel preview

RATel

GitHubfrenchcisco/ratel

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
2775 years ago
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
command-and-controleducationpayload-generation+4
4881 year ago
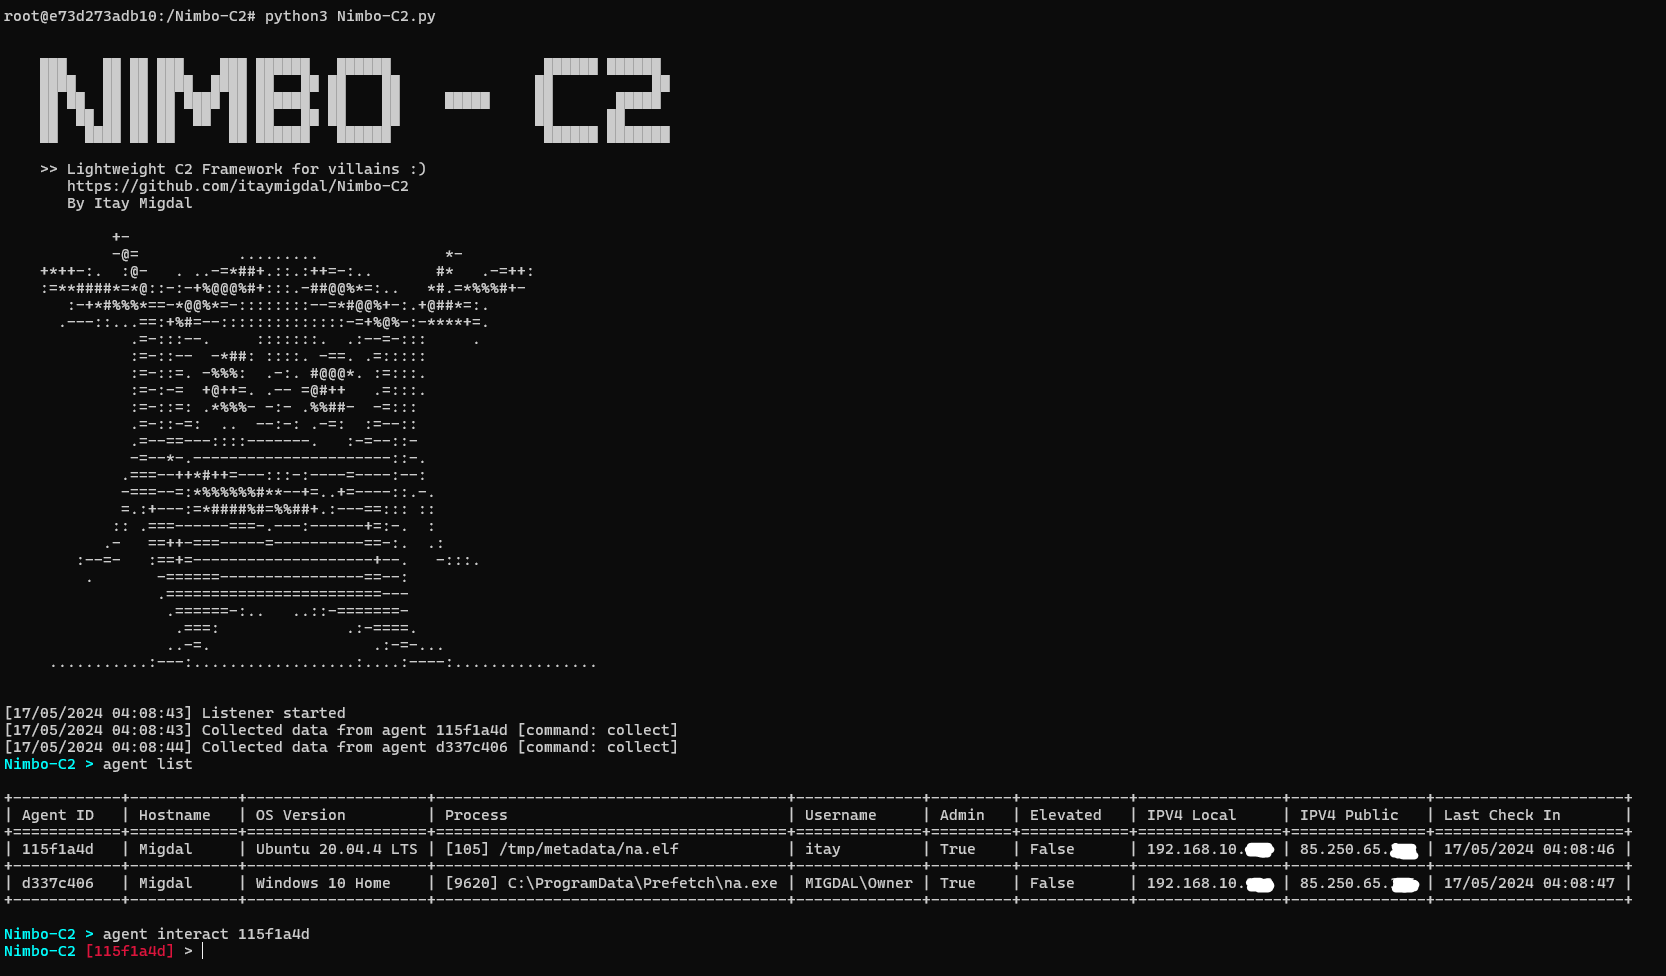
Nimbo-C2 preview

Nimbo-C2

GitHubitaymigdal/nimbo-c2

Nimbo-C2 is yet another (simple and lightweight) C2 framework
command-and-controlexploit-frameworkspayload-generation+5
4477 months ago
NetExec preview

NetExec

GitHubpennyw0rth/netexec

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.9k1 day ago
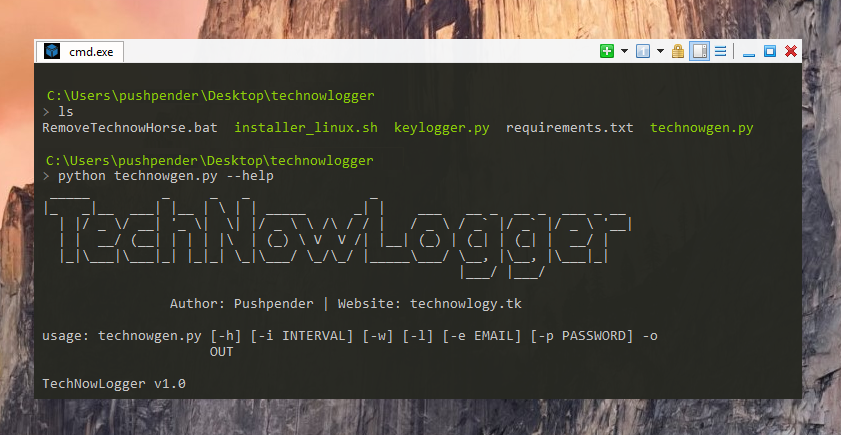
Sinister preview

Sinister

GitHubpushpenderindia/sinister

Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info
data-exfiltrationinformation-gatheringpassword-cracking+5
4662 years ago
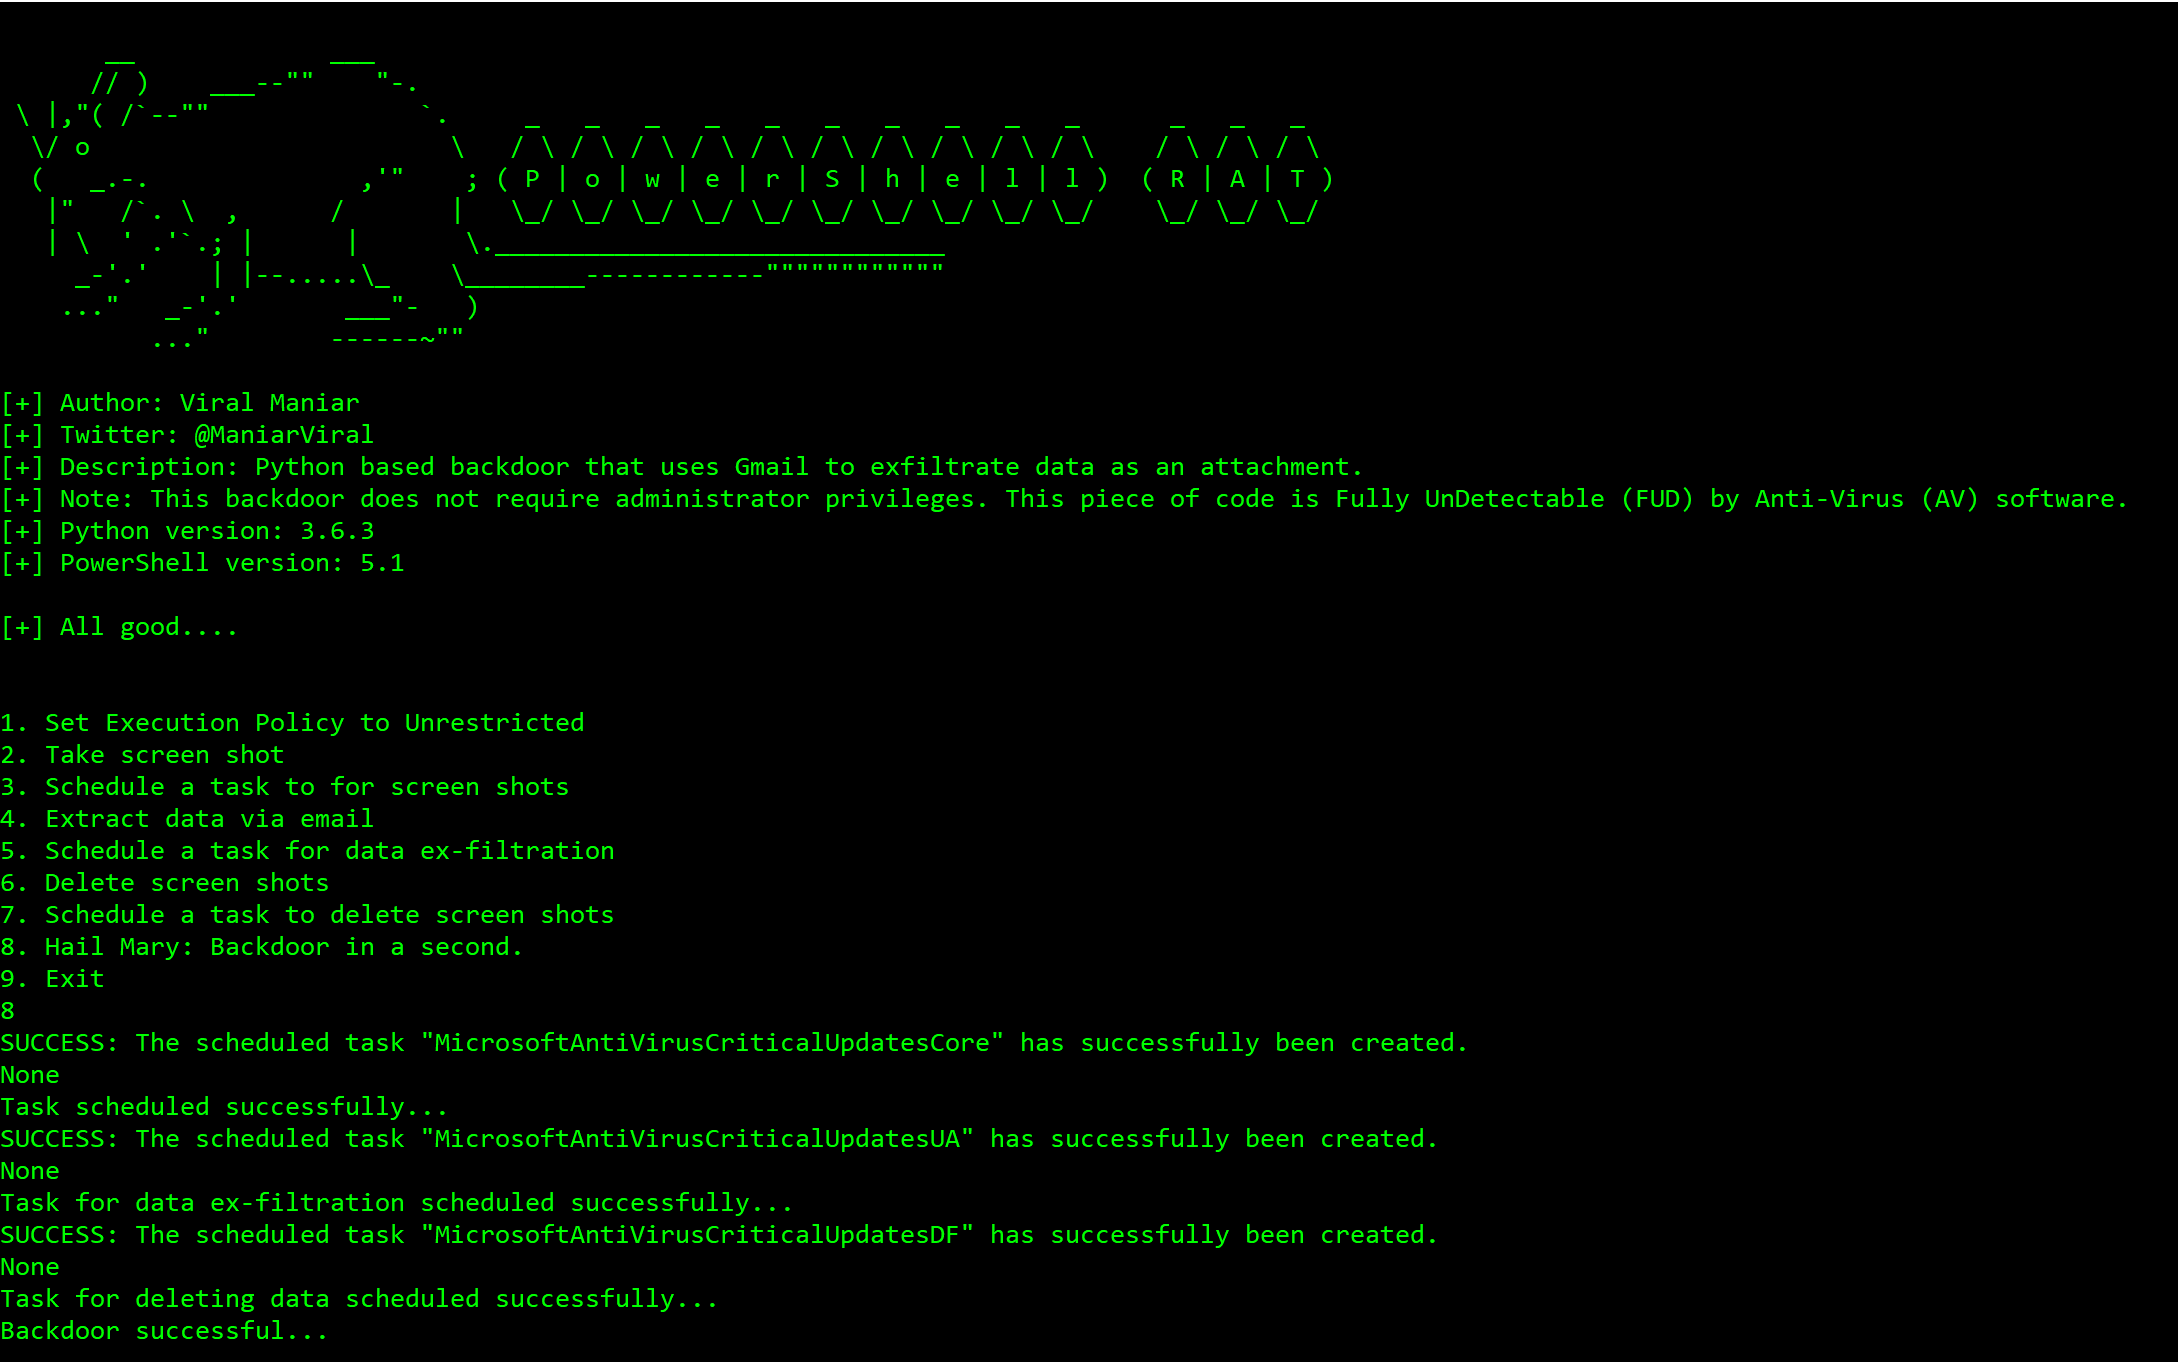
Powershell-RAT preview

Powershell-RAT

GitHubviralmaniar/powershell-rat

Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…

data-exfiltrationeducationpayload-generation+4
1.2k7 years ago
Winpayloads preview

Winpayloads

GitHubnccgroup/winpayloads

Undetectable Windows Payload Generation
command-and-controlexploit-frameworkslateral-movement+9
1.6k7 years ago
Dr0p1t-Framework preview
Archived

Dr0p1t-Framework

GitHubd4vinci/dr0p1t-framework

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
anti-botcommand-and-controlexploitation+9
1.5k7 years ago
ghost preview

ghost

GitHubahxr/ghost

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k8 years ago
paradoxiaRAT preview

paradoxiaRAT

GitHubquantumcore/paradoxiarat

ParadoxiaRat : Native Windows Remote access Tool.
command-and-controlpassword-crackingpenetration-testing+4
8303 years ago
taowu-cobalt_strike preview

taowu-cobalt_strike

GitHubpandasec888/taowu-cobalt_strike

Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
command-and-controlexploit-frameworkslateral-movement+7
1.8k10 months ago
sAINT preview
Archived

sAINT

GitHubtiagorlampert/saint

👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]

data-exfiltrationpayload-generationpersistence-mechanisms+1
7556 years ago
Previous12Next