

T3MP3ST
 elder-plinius/t3mp3st
autonomous red teaming platform; multi-agent offensive-security meta-harness
ai-securitybinary-analysiscloud-security+9
6.2k
elder-plinius/t3mp3stautonomous red teaming platform; multi-agent offensive-security meta-harness
 shellphish/ictf-framework
Open-source framework for hosting Attack/Defense CTF competitions with automated gamebot, script execution, VPN routing, and cloud-based…

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 purpleteam-labs/purpleteam-orchestrator
Orchestration component of purpleteam
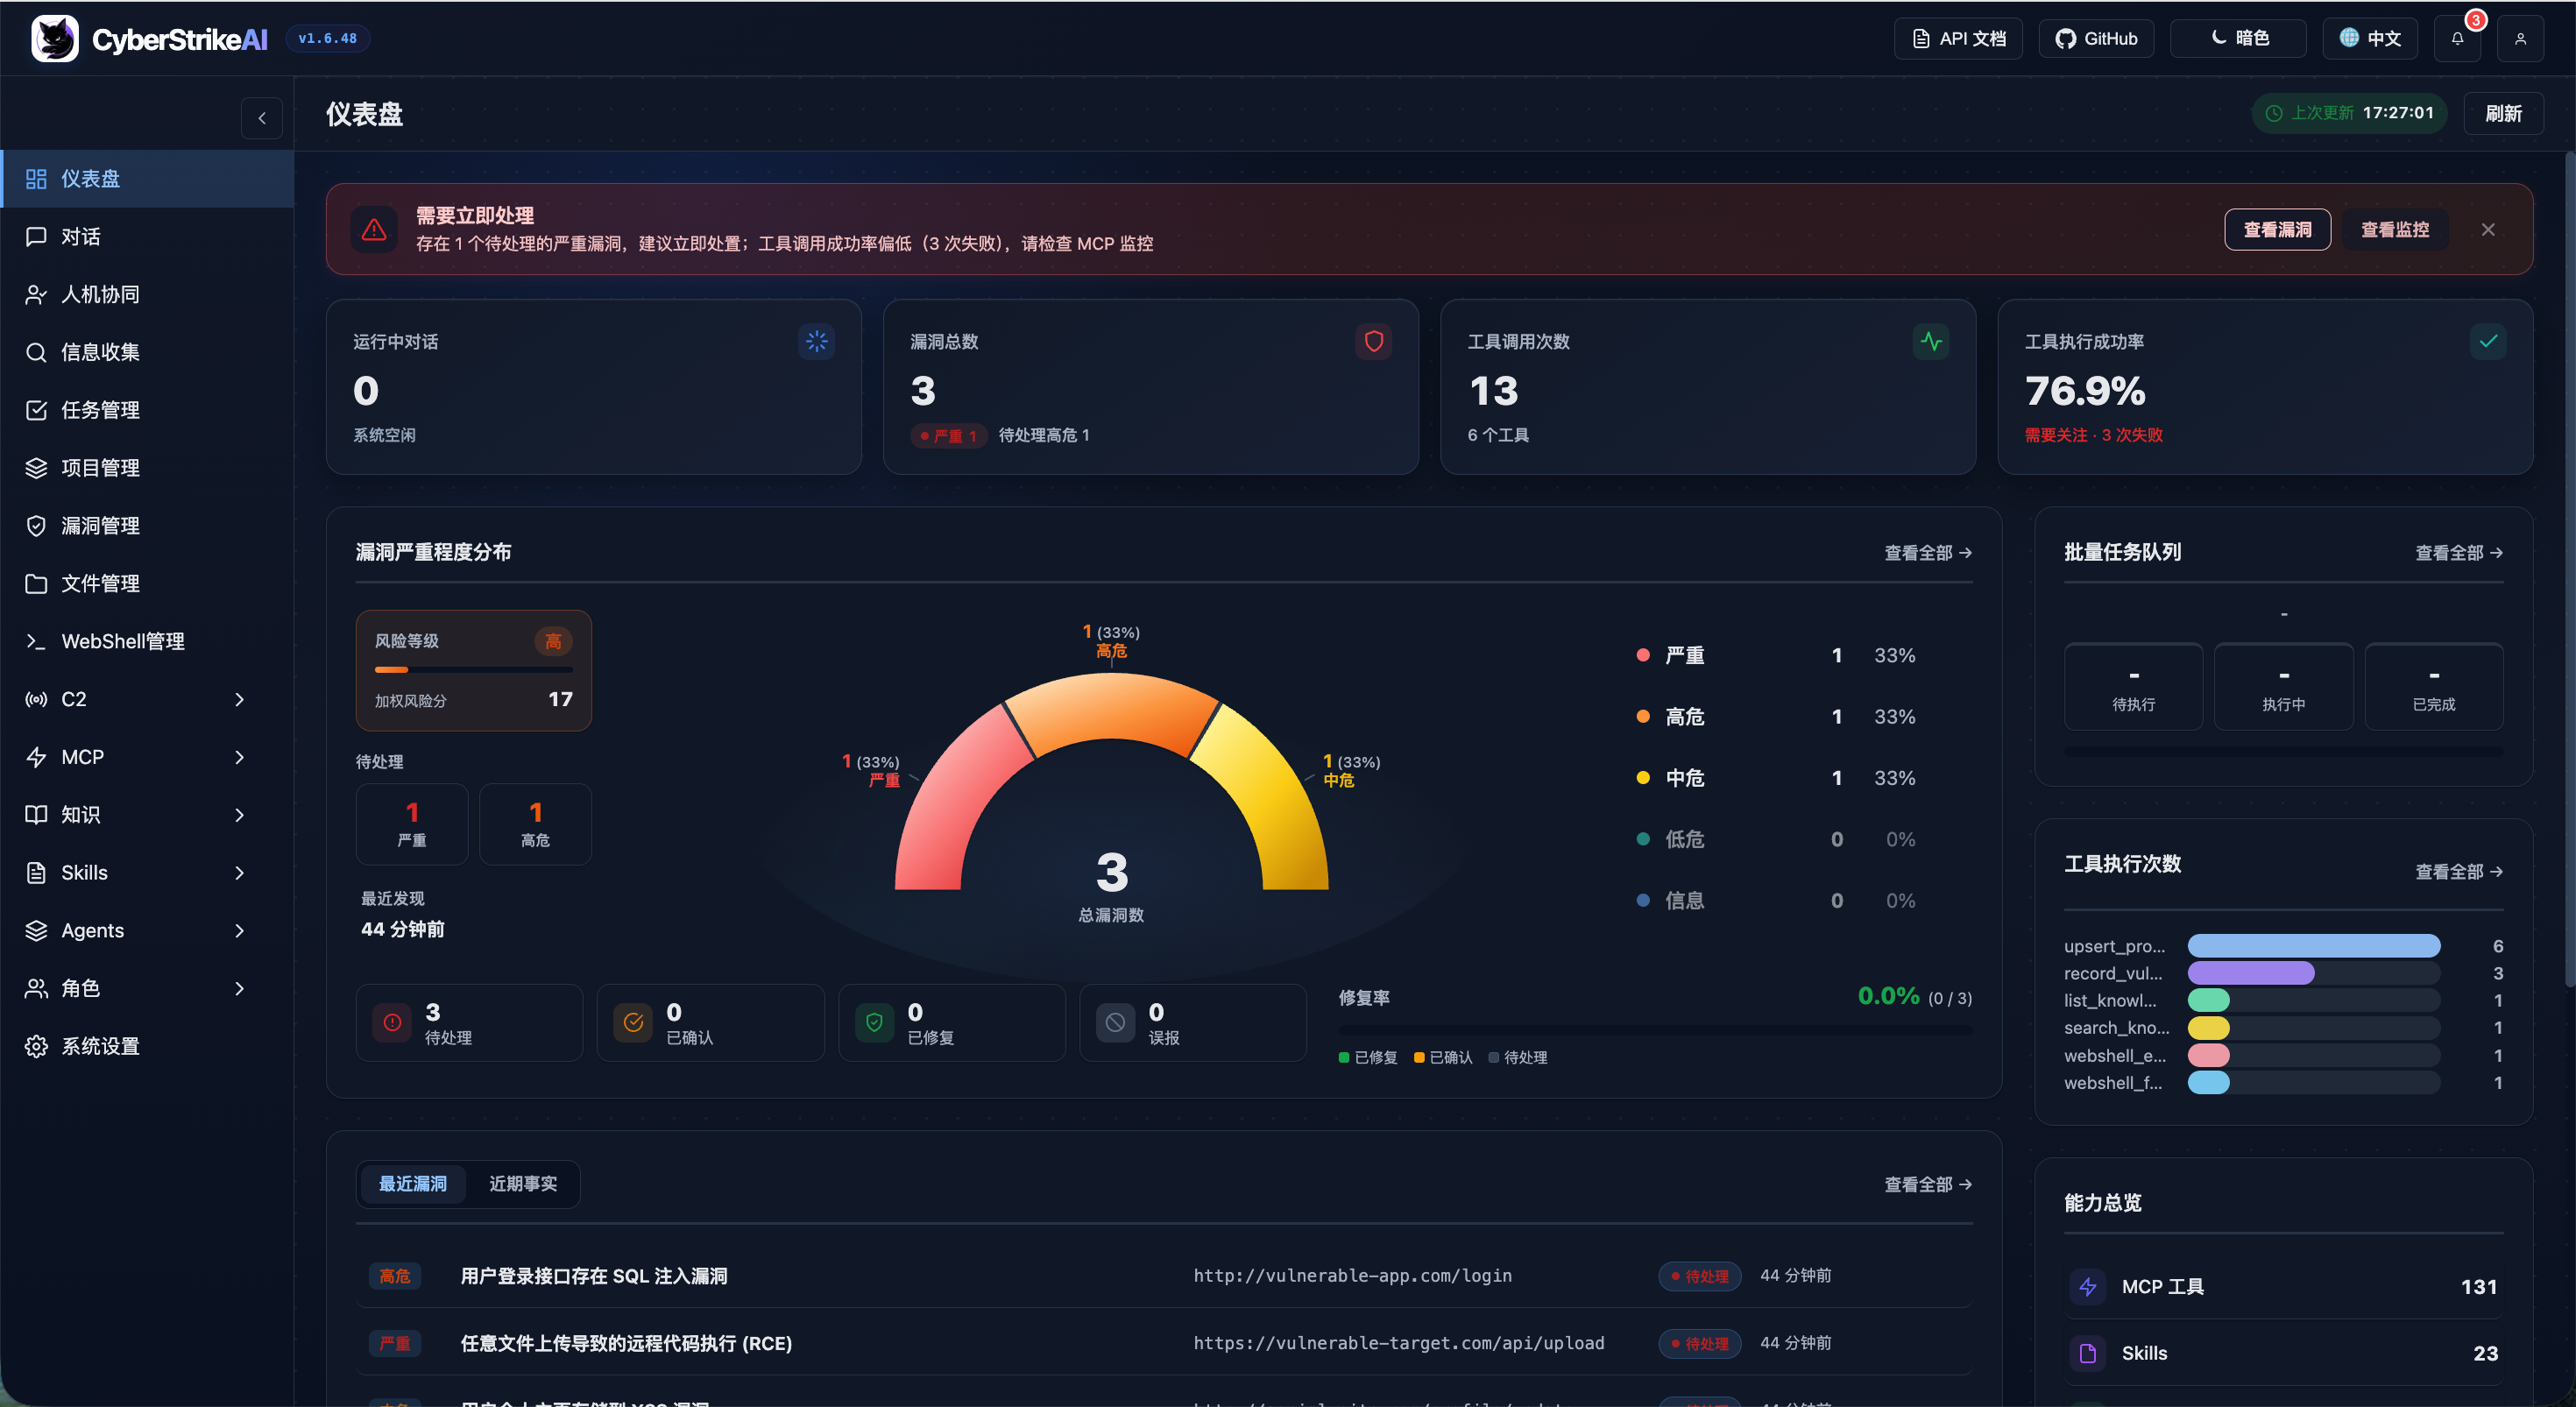 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 zakirkun/guardian-cli
Guardian is a production-ready AI-powered penetration testing automation CLI tool that leverages Google Gemini and LangChain to orchestrate…
 owasp/apts
OWASP Autonomous Penetration Testing Standard
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 luemmelsec/apex
Azure Post Exploitation Framework
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…