
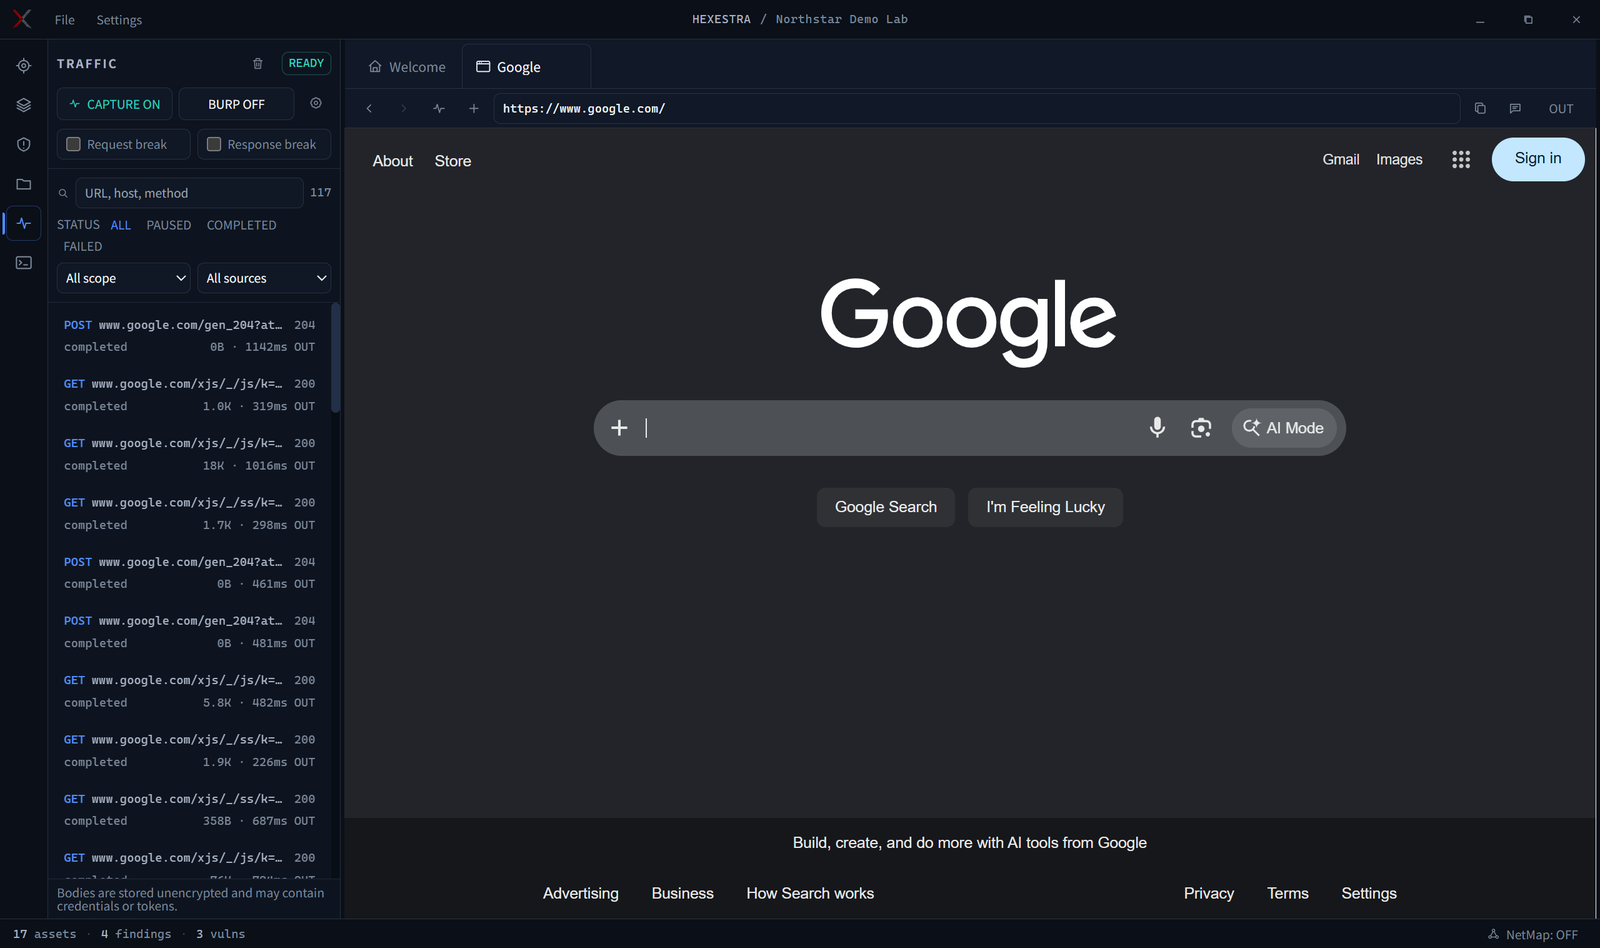
Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 cisc0-gif/kitt
Python-Based Pentesting Framework
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 beefproject/beef
The Browser Exploitation Framework Project
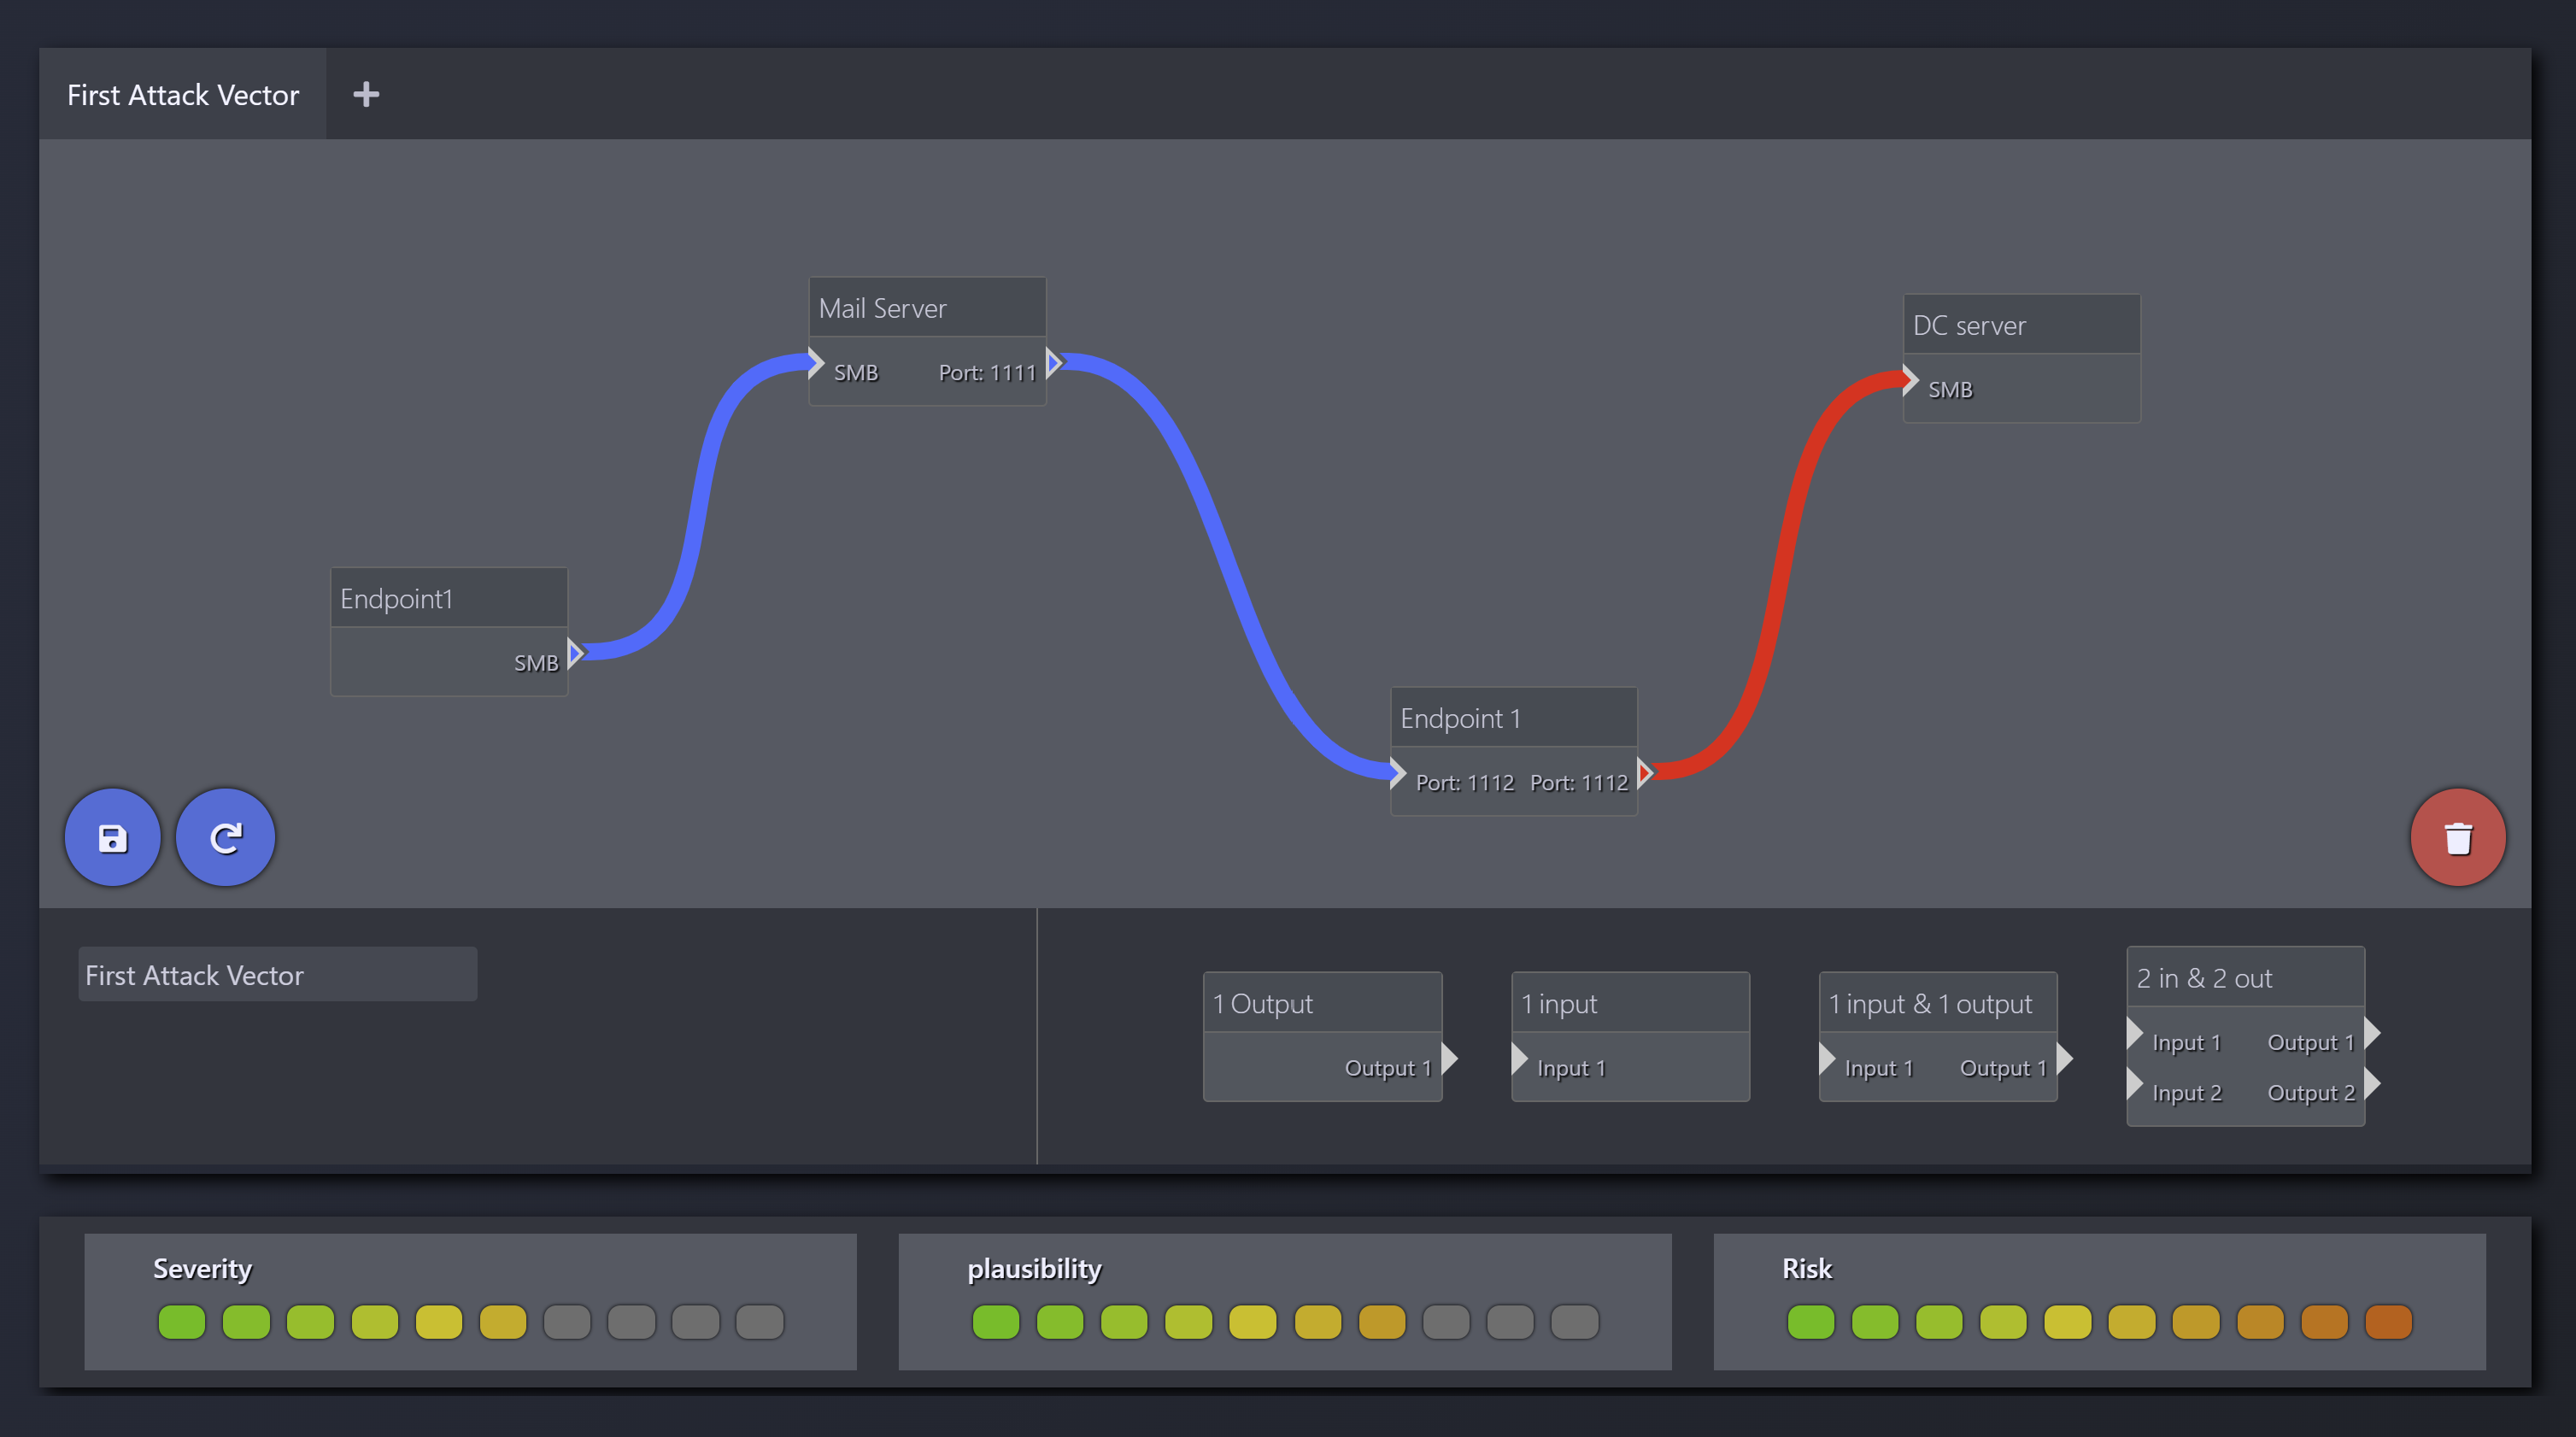 redeye-framework/redeye
Collaborative pentest data management platform for organizing servers, users, vulnerabilities, attack vectors, and files with API access and graph…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 archstrike/archstrike
An Arch Linux repository for security professionals and enthusiasts. Done the Arch Way and optimized for i686, x86_64, ARMv6, ARMv7 and ARMv8.
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 ascr0b/pcwt
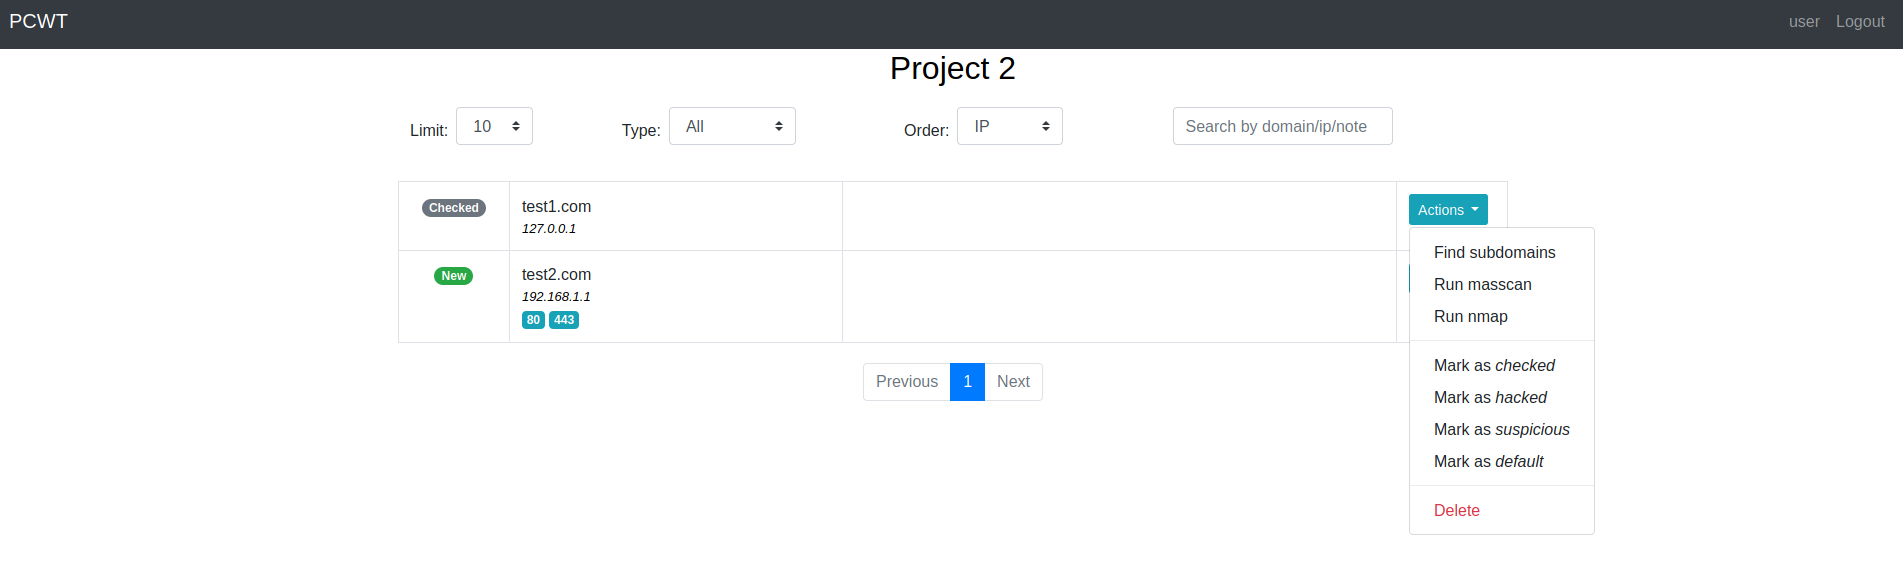
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 ascotbe/medusa
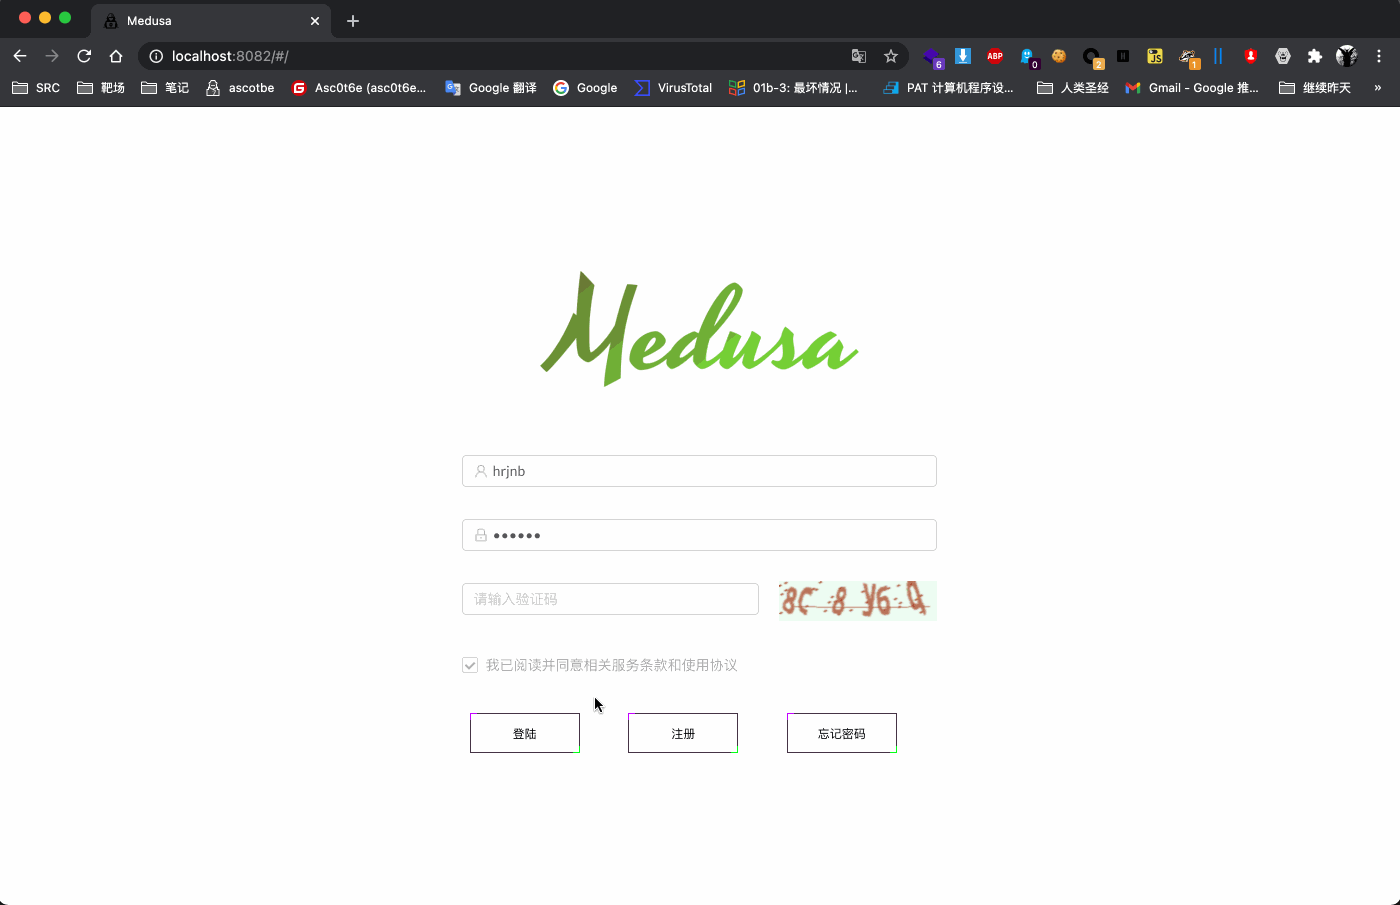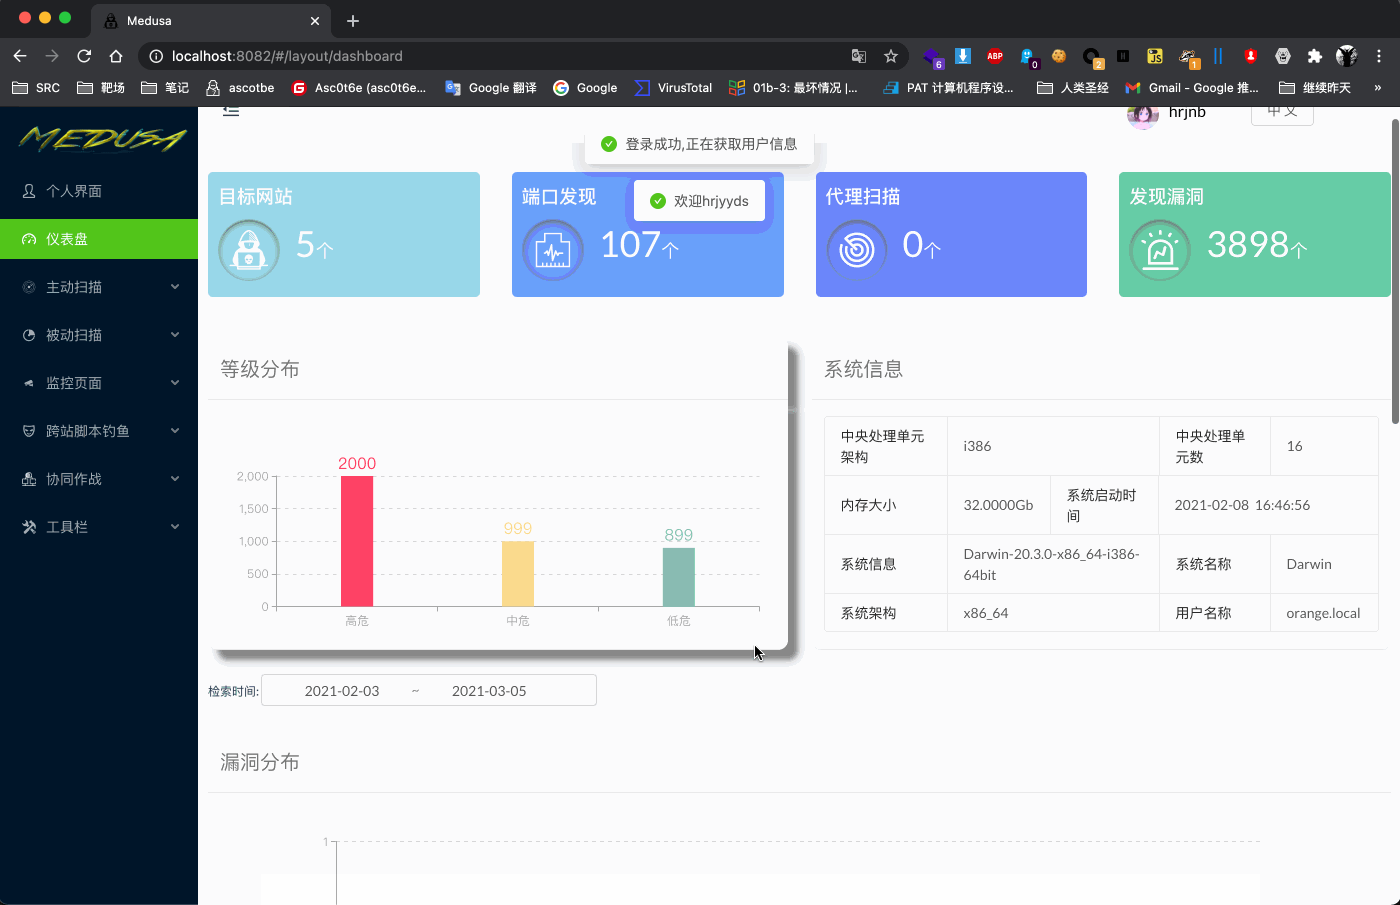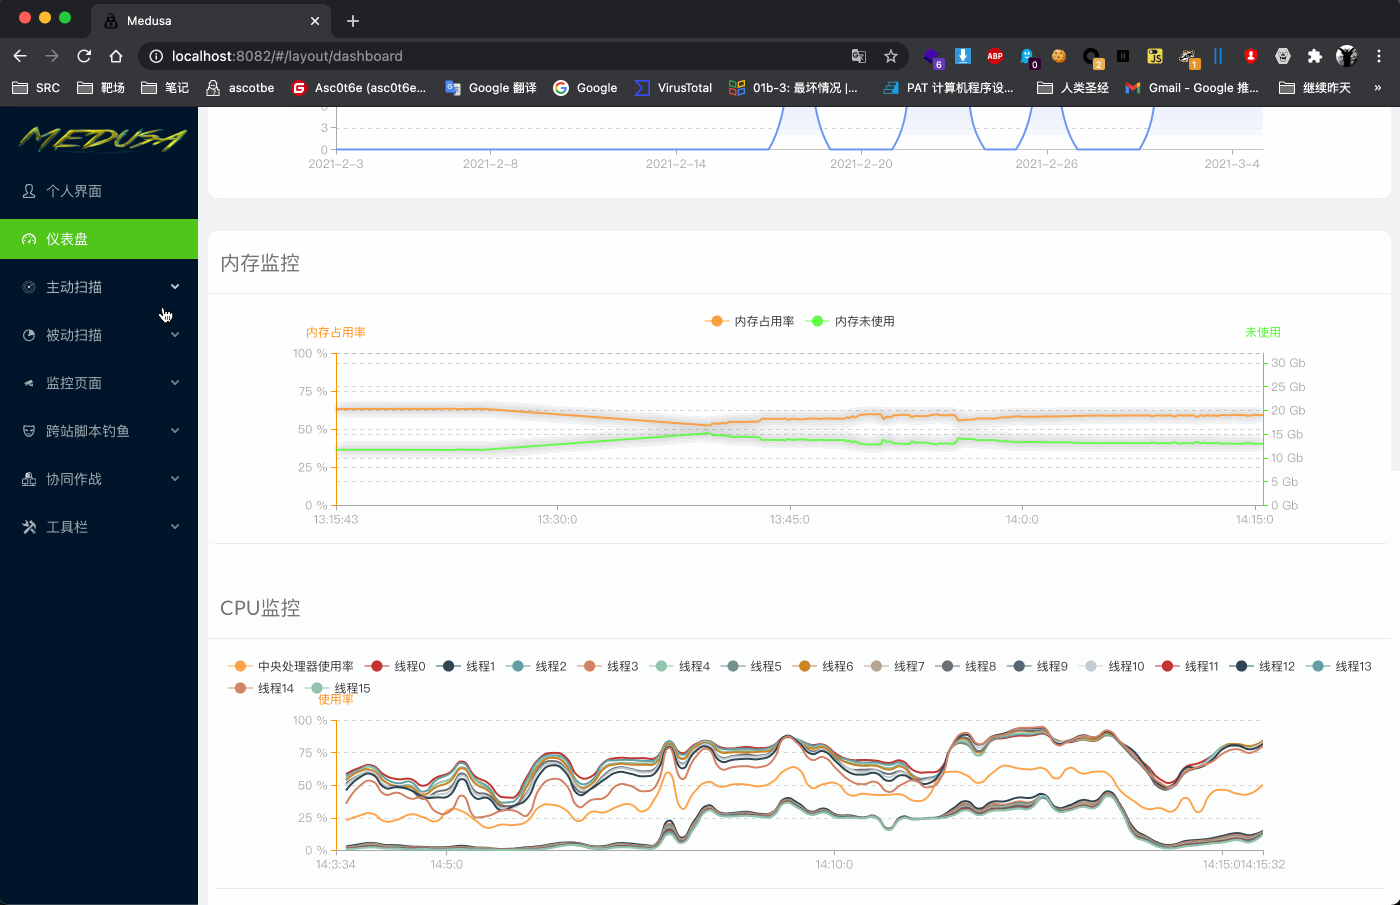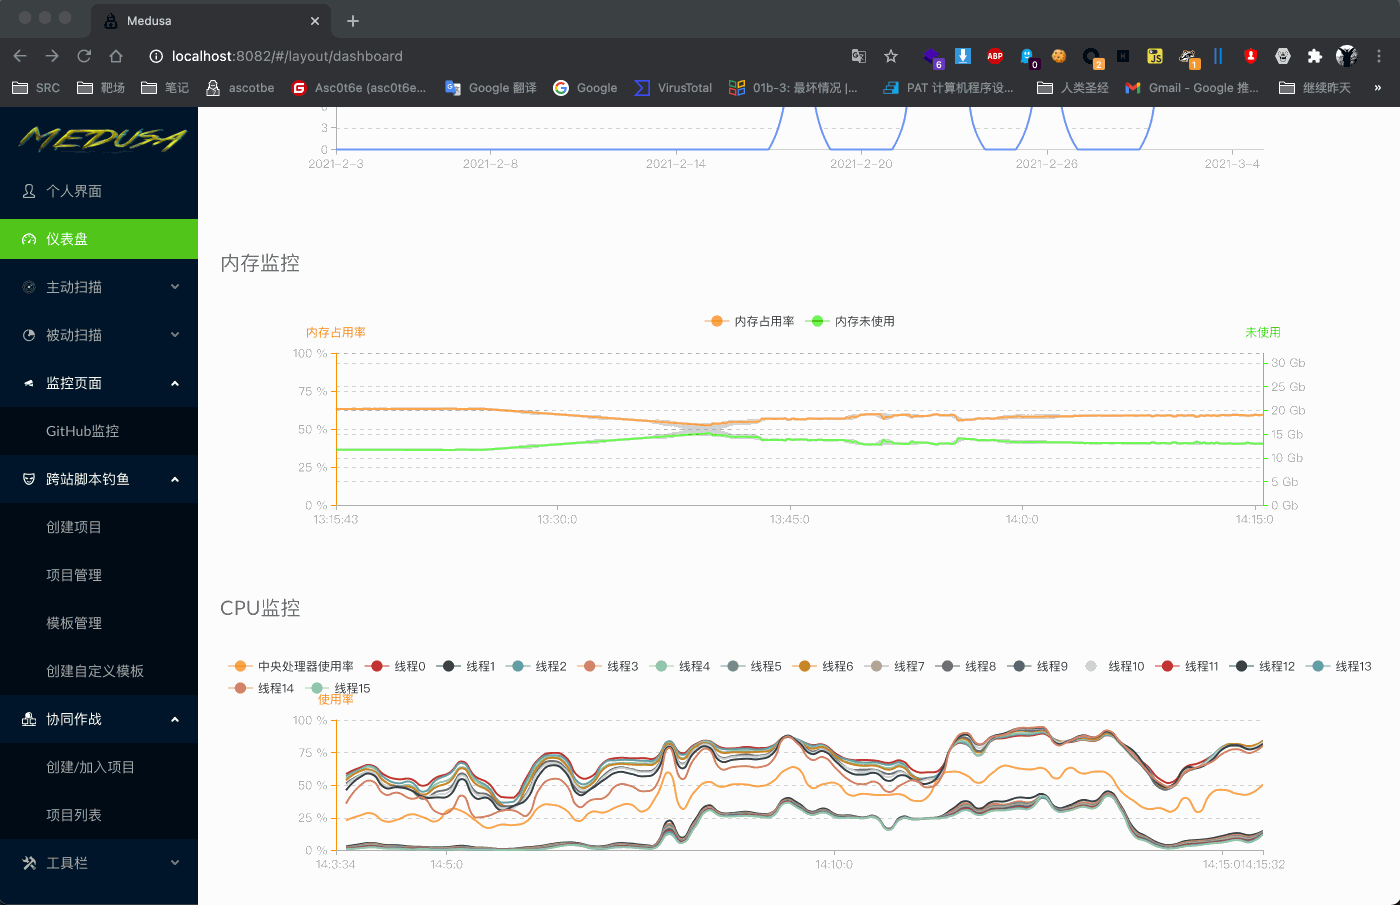
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 mazen160/shennina
Automating Host Exploitation with AI
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
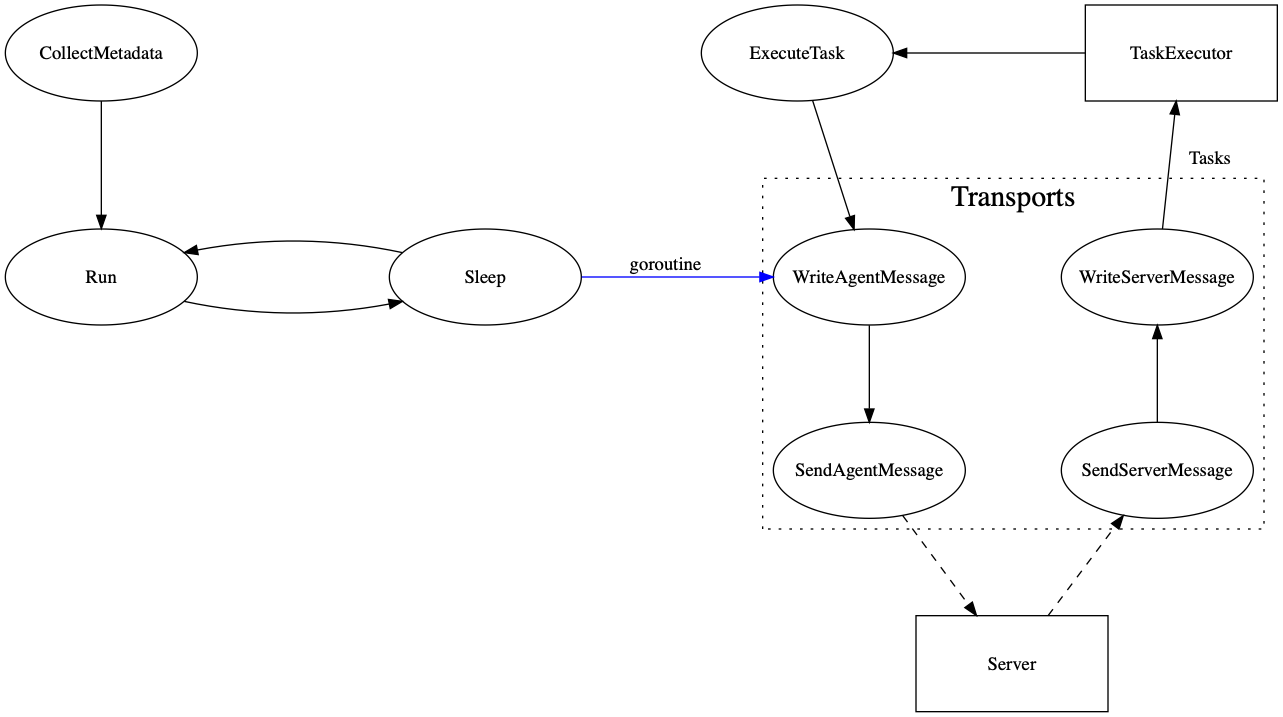 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
