

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PCWT — Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain enumeration via Amass and Findomain. | Kitploit
Tools/GitHubGitHub/ascr0b/pcwt
Penetration Testing FrameworksReconnaissanceVulnerability ScannersPort ScanningInformation GatheringWeb SecurityPenetration TestingSubdomain Enumeration
GitHubascr0b/pcwt

PCWT

Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain enumeration via Amass and Findomain.

4615666 years agoReviewed by Kitploit
View Repository
Share

PCWT

A web application that makes it easy to run your pentest and bug bounty projects.

Description

The app provides a convenient web interface for working with various types of files that are used during the pentest, automate port scan and subdomain search.
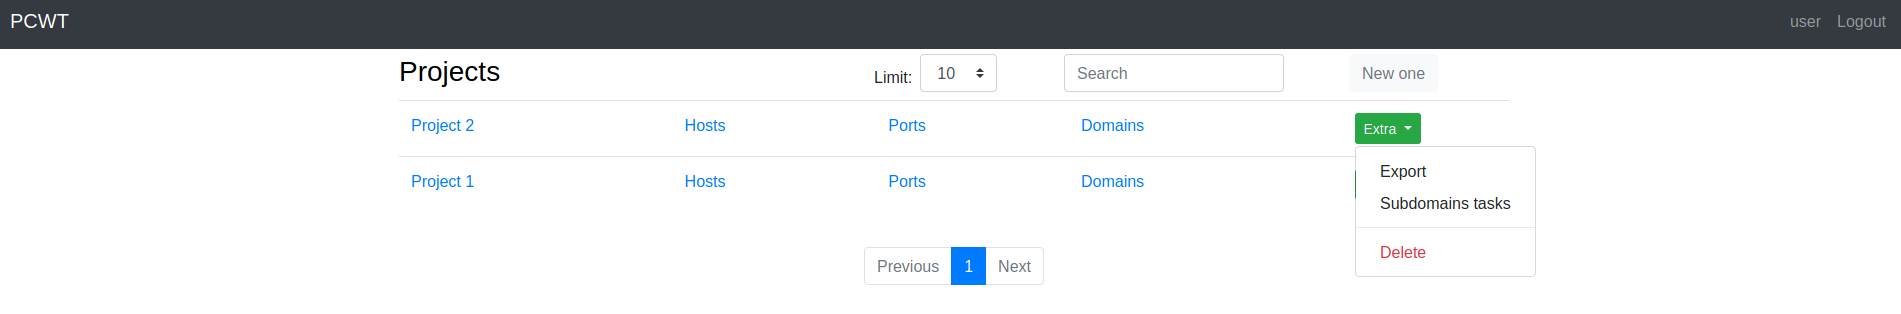
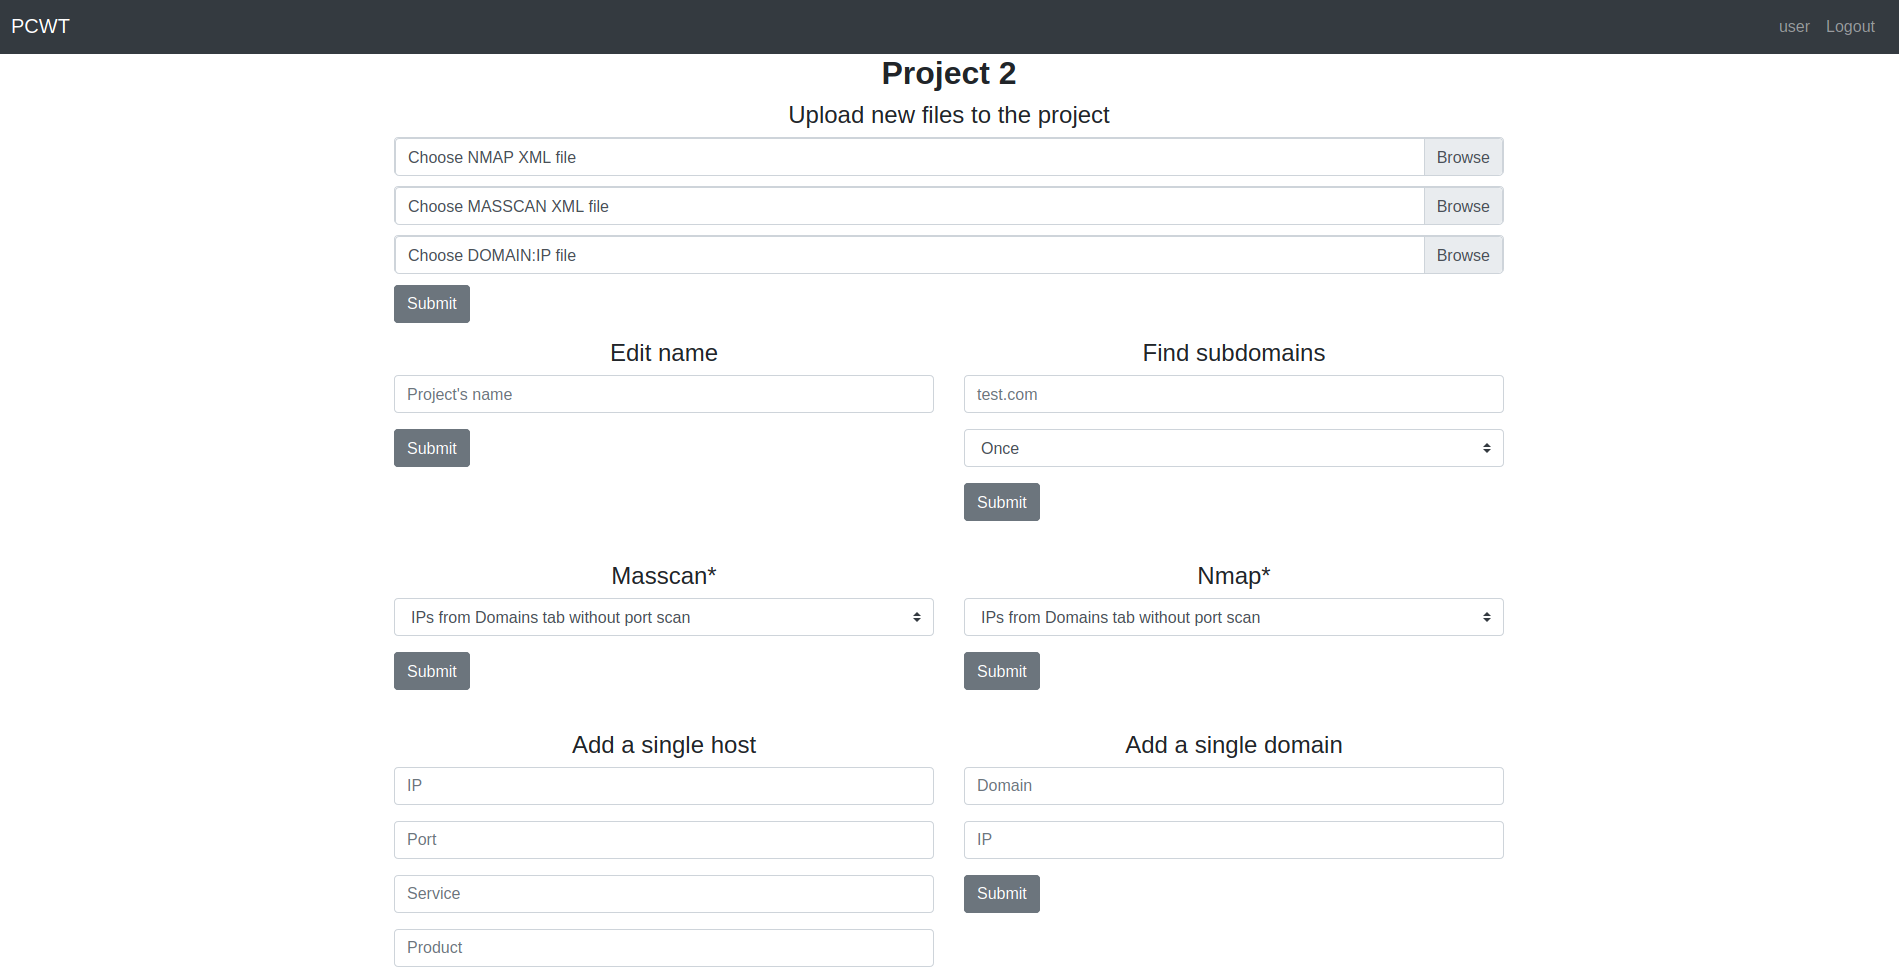
Main page

Main page

Project settings

Settings

Domains dashboard

Domains

Port scan

You can scan ports using nmap or masscan. The nmap is started with the following arguments:

nmap --top-ports 10000 -sV -Pn --min-rate 300 --max-retries 2 [ip]

The masscan is started with the following arguments:

masscan -p 1-65535 --rate 2000

Subdomain search

Amass and findomain are used to find subdomains.

Features

  • Leave notes to host, port or domain.
  • Mark host or domain with tags.
  • Search by any field related with host, port or domain (tags and notes are included). Regexp is available.
  • Different types of sorting ara available on almost all dashboards.
  • Run port scan for all hosts, hosts without port scan or custom list.
  • Create tasks for subdomains search (every 2 hours, every 5 hours, every day or every week). You can also disable and enable them on demand using Subdomain tasks dashboard.
  • Different types of export are available.
  • Notifications about the start and end of the scan, as well as about new found domains can be sent to Telegram. Update the config.py with your chat id and token.

Install from sources

NOTE 1: Change the paths for amass, findomain, nmap and masscan in config.py before running commands. NOTE 2: The app must be started as root if you want masscan to work.

apt install python3 python-venv python3-pip
git clone https://github.com/ascr0b/PCWT
cd PCWT

python3 -m venv env
source env/bin/activate
pip3 install -r requirements.txt

flask init-db
flask crontab add

export FLASK_APP=app
flask run

The app is available at http://127.0.0.1:5000

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →





